
Archived
enjarify
 google/enjarify
Translates Dalvik bytecode (DEX/APK) to equivalent Java bytecode, enabling Java analysis tools to process Android applications with high correctness…
android-securitybinary-analysiscode-analysis+3
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
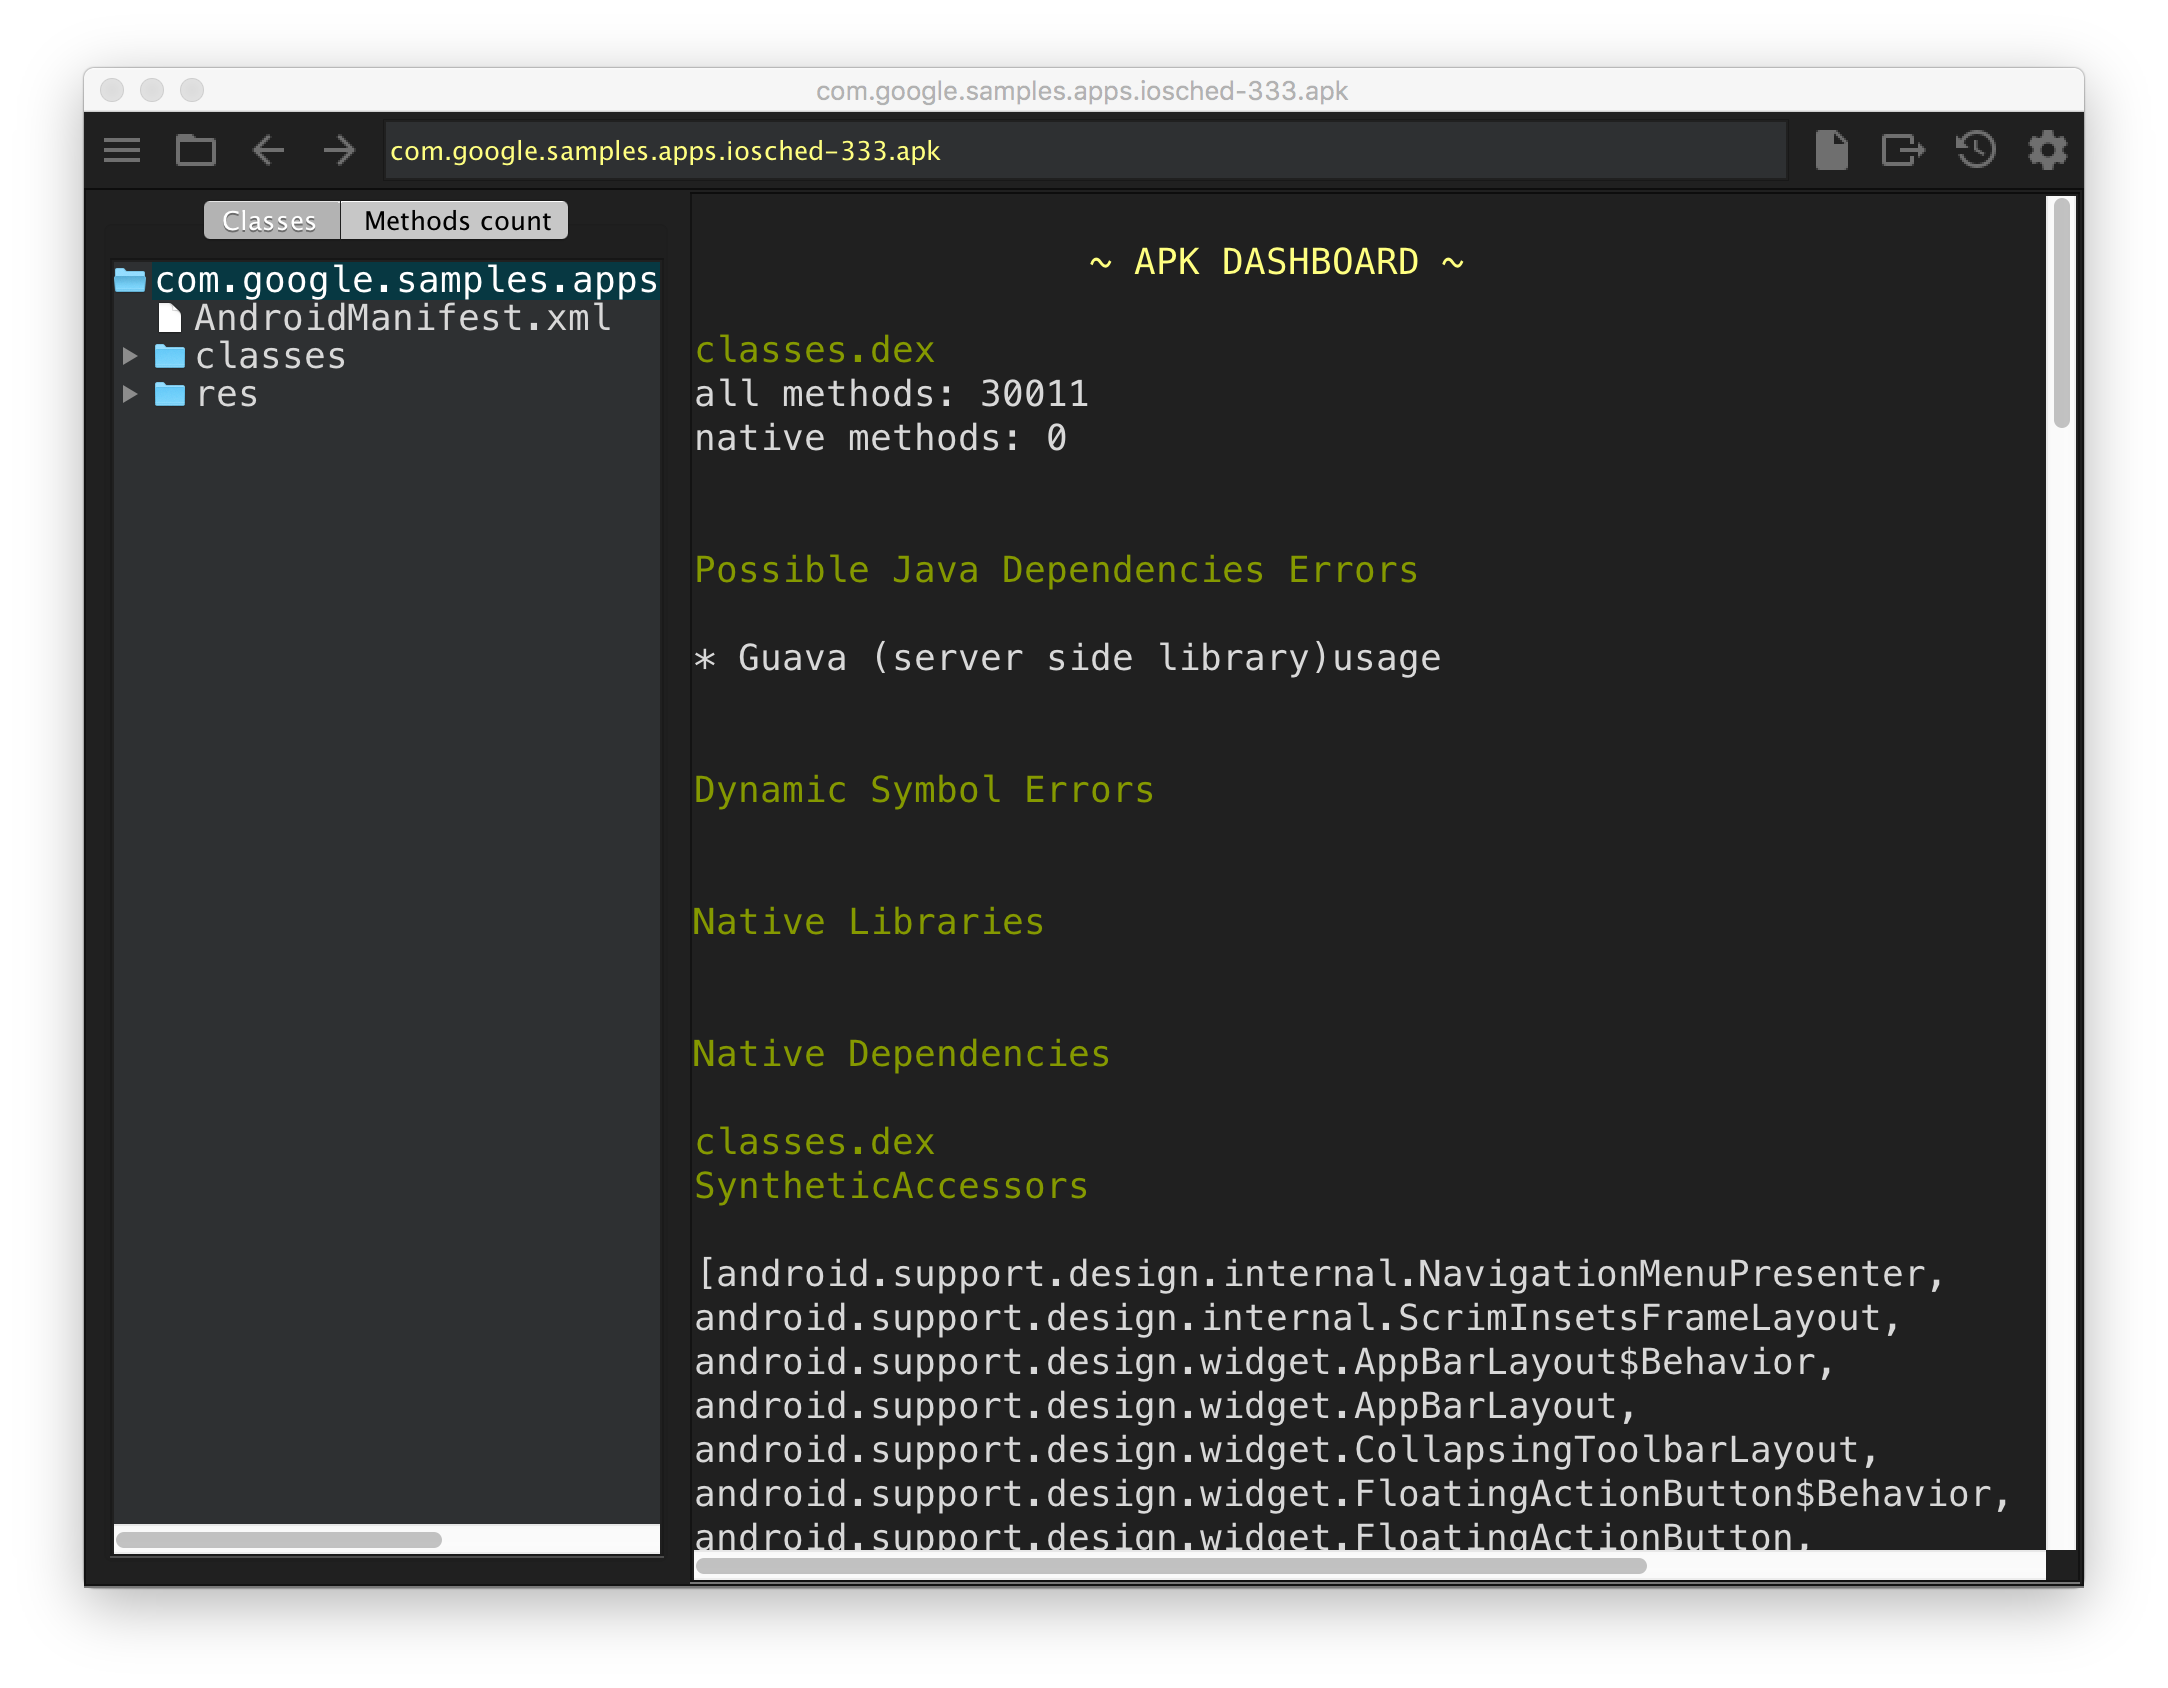 google/android-classyshark
Android and Java bytecode viewer
 tillson/git-hound
Fast GitHub recon tool. Scans for leaked secrets across all of GitHub, not just known repos and orgs. Support for GitHub dorks.
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 skyscanner/whispers
Identify hardcoded secrets in static structured text
 josehelps/git-wild-hunt
A tool to hunt for credentials in github wild AKA git*hunt
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 nccgroup/glasgo
Go static analysis tool that checks for security issues using an AST.
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 radicle-dev/heartwood
Peer-to-peer code collaboration and publishing stack with a secure, decentralized protocol, CLI tool, and network daemon for sovereign code forges.
 ewenquim/entropy
CLI tool that scans codebases for high-entropy lines to detect potential secrets, with customizable file extension and top-N filtering.
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 whitesquirrell/c0devari4nt
A variant analysis and visualisation tool that scans codebases for similar vulnerabilities
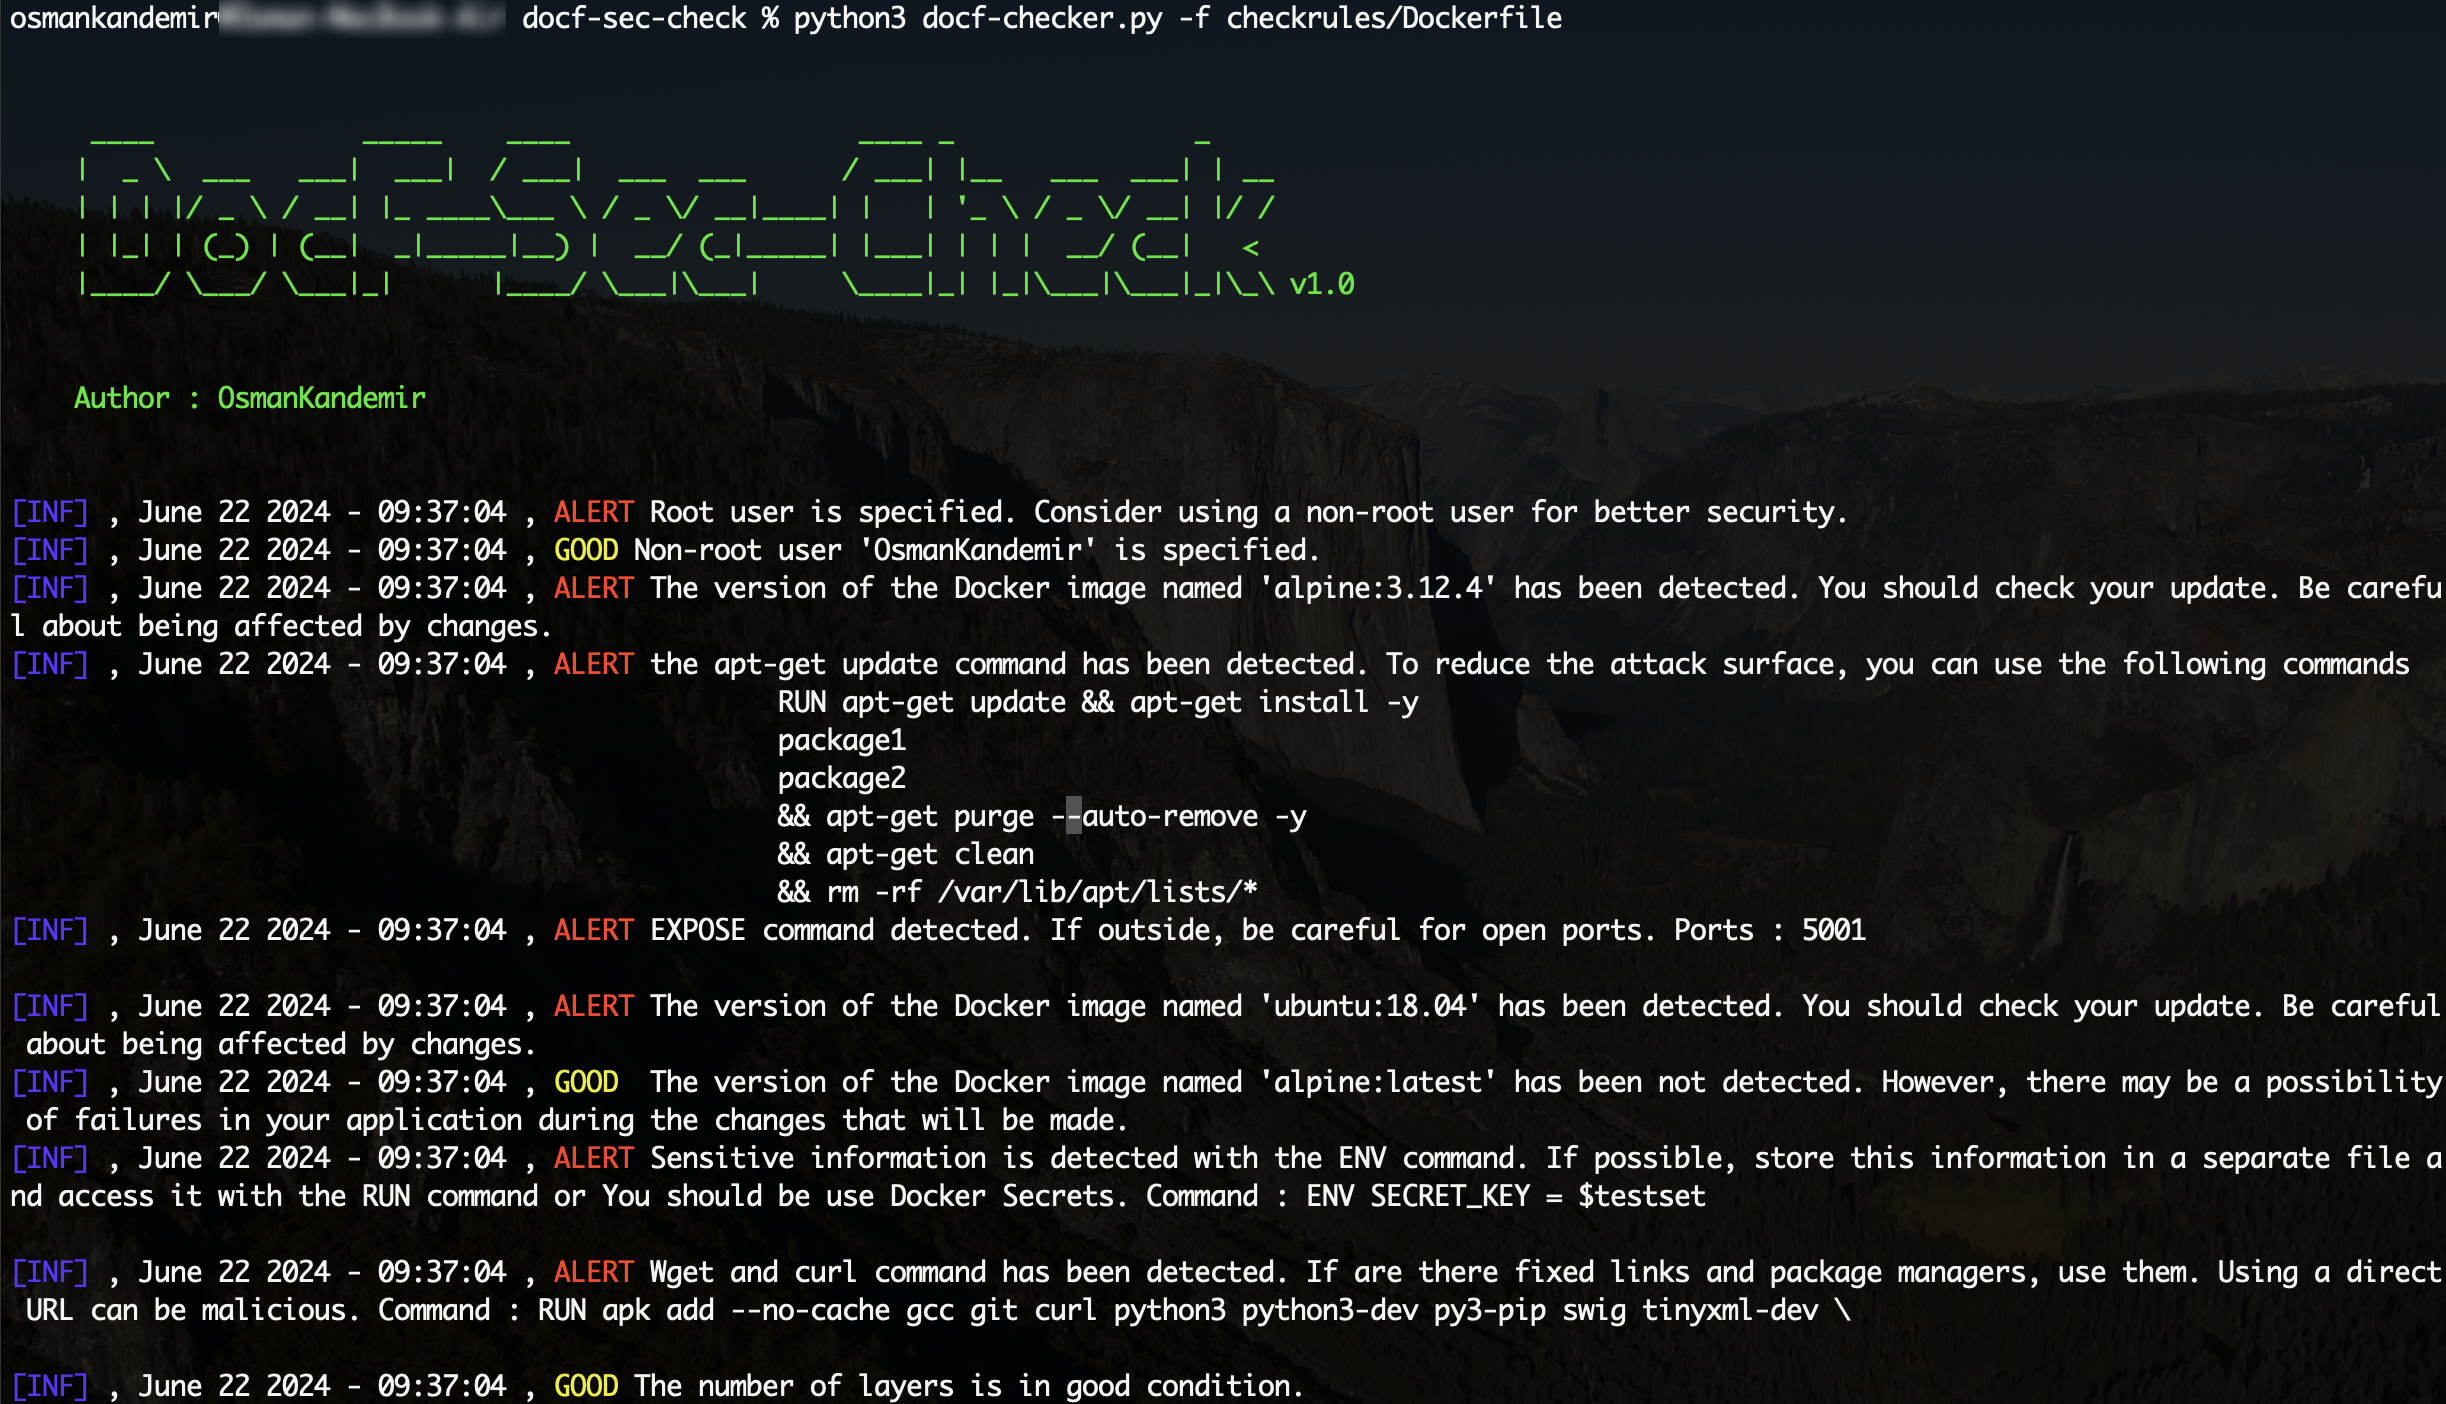 osmankandemir/docf-sec-check
Static analysis tool that scans Dockerfiles for insecure commands and configuration issues, providing actionable security notifications to harden…
 mbennett-labs/crypto-scanner
CLI tool to scan codebases for quantum-vulnerable cryptography
 studiomeyer-io/mcp-server-attestation
Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…