
cve-2026-25541-fuel-analysis
 trajanox/cve-2026-25541-fuel-analysis
CVE-2026-25541 impact analysis for Fuel infrastructure (bytes crate integer overflow)
code-analysiscurated-resourceseducation+3
1
trajanox/cve-2026-25541-fuel-analysisCVE-2026-25541 impact analysis for Fuel infrastructure (bytes crate integer overflow)
 frenzymadness/cve-2021-3572
Minimal test repository for CVE-2021-3572, demonstrating a pip dependency confusion vulnerability and its fix across vulnerable and patched versions.
 zebberncve/cve-2026-26831
Advisory for textract ⌯⌲ 15 000 weekly downloads
 zebberncve/cve-2026-26830
Advisory for pdf-image ⌯⌲ 10 000 weekly downloads
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 trerb/ai-ide-config-guard
Scan a repo for AI-IDE config files that can trigger RCE via Claude Code hooks, Cursor rules, MCP auto-registration. Detects CVE-2025-59536,…
 emresandikci/nextjs-cve-2026-23870-checker
Checker and fixer for all 13 vulnerabilities in the Next.js May 2026 security release (CVE-2026-23870)
 renewablehacking/cve-2020-7598
Educational lab demonstrating CVE-2020-7598 prototype pollution in minimist with a vulnerable Node.js/Express app, exploit payload, and…
 dannyendortest/gin-vulnerable
Demo consumer for gin v1.7.0 (CVE-2023-29401) — Context.FileAttachment with user input. endorctl scan target.
 hiteshgorana/susvibes-jupyter-server-cve-2026-35397
Benchmark task for reimplementing a masked path-resolution fix in Jupyter Server, with functional and hidden security tests to evaluate…
 dannyendortest/node-vulnerable
Synthetic demo target for EXPOSURE — CVE-2018-21268 (traceroute) + CVE-2018-3757 (pdf-image)
 zebberncve/cve-2026-40579
Advisory for git-js ⌯⌲ 11 mill weekly downloads
 langbyyi/cve-2026-22785
Exploit tool for CVE-2026-22785, a critical code injection in orval < 7.18.0. Provides shell command execution and file scanning to demonstrate the…
 raptor-audit/raptor
Framework for auditing blockchain ecosystems, identifying smart contract vulnerabilities, and generating structured findings with multi-platform…
 checkmarx/checkmarx-cve-2025-30066-detection-tool
Scans GitHub workflows and logs for indicators of CVE-2025-30066, detecting malicious actions and exposed secrets using Checkmarx 2ms integration.
 useaitechdad/openclaw-technical-analysis
This technical research and review is for educational purposes on public code and constitutes Fair Dealing under the Copyright Act (Canada).
 sudotom/rcno-reviews
Recencio Book Reviews - WordPress plugin for managing book reviews. Originally created by Kemory Grubb. Security-patched fork resolving…
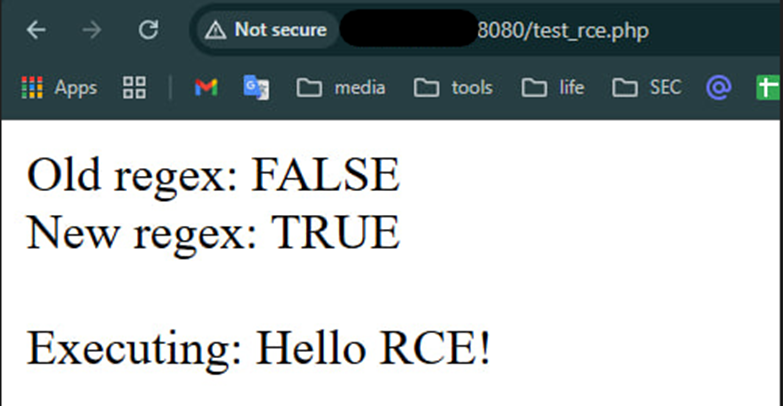 soltanali0/cve-2024-12877-exploit
Educational CVE-2024-12877 exploit demo for PHP Object Injection in GiveWP WordPress plugin. Includes root cause analysis, regex bypass techniques,…