
UnmarshalPwn
 codewhitesec/unmarshalpwn
POC for CVE-2018-0824
binary-exploitationcode-analysisexploitation+2
codewhitesec/unmarshalpwnPOC for CVE-2018-0824
 soxoj/gitcolombo
🧬 Extract and analyze contributors info from git repos
 elevenpaths/neto
Neto | A tool to analyse browser extensions
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…
 symgraph/idassistmcp
Standalone MCP server plugin for IDA Pro.
 zephrfish/wp2shell-scanner
CVE-2026-63030, CVE-2026-60137, wp2shell scanner
 freeqaz/react2shell
RCE exploit toolkit for CVE-2025-55182 and CVE-2025-66478 in React Server Components. Includes multiple exploit variants, detection scripts, a…
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 nightwatchcybersecurity/gitbleed_tools
Shell scripts to clone and mirror Git repositories, compute deltas, and run gitleaks to detect secrets hidden in deleted or reset commits.
 sqlsure/sqlsure
Semantic inspector for SQL — catches fan-out double-counting, additivity violations, wrong join keys, and policy breaches before the query runs.…
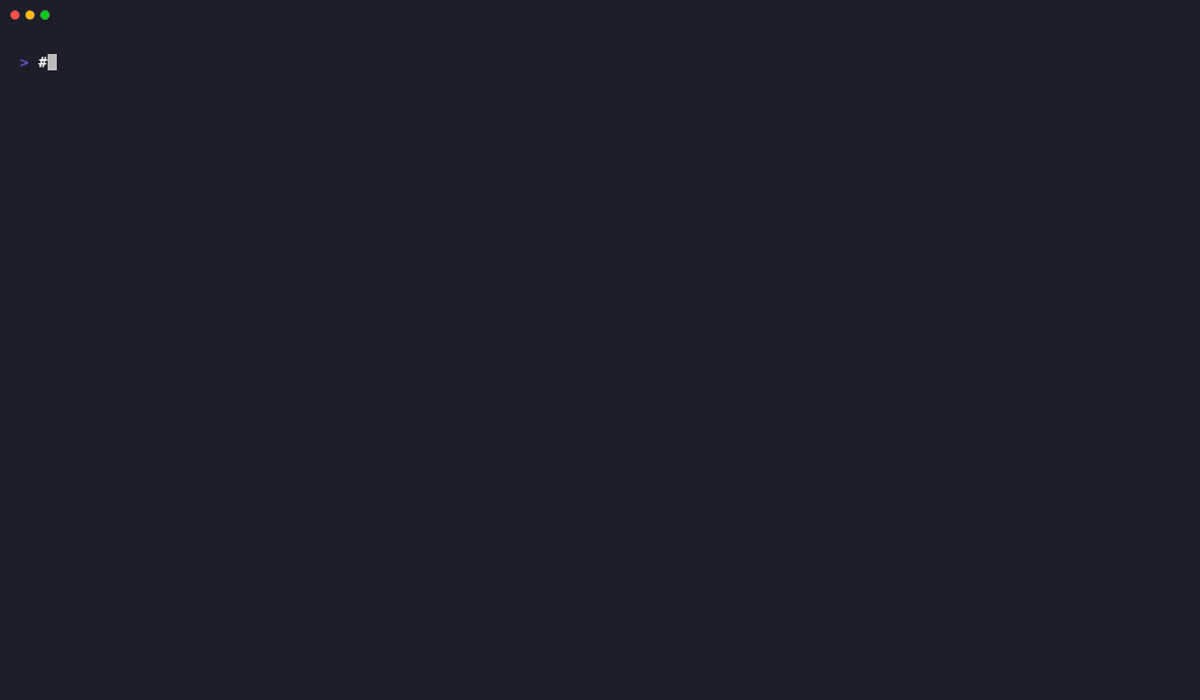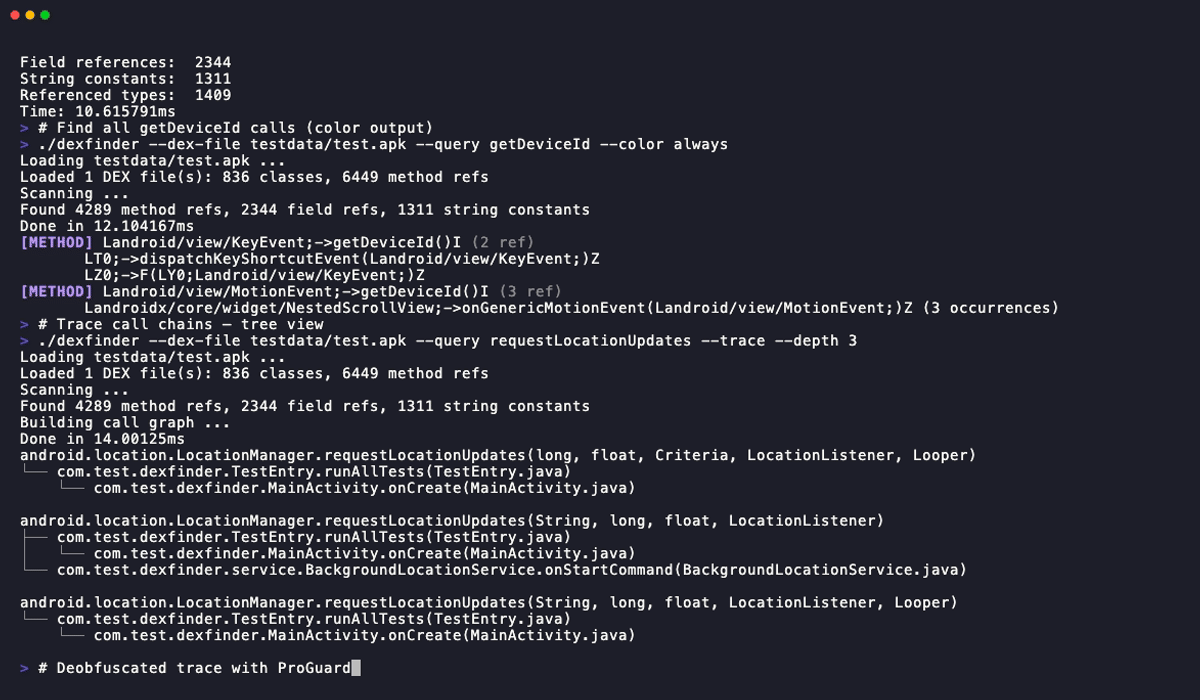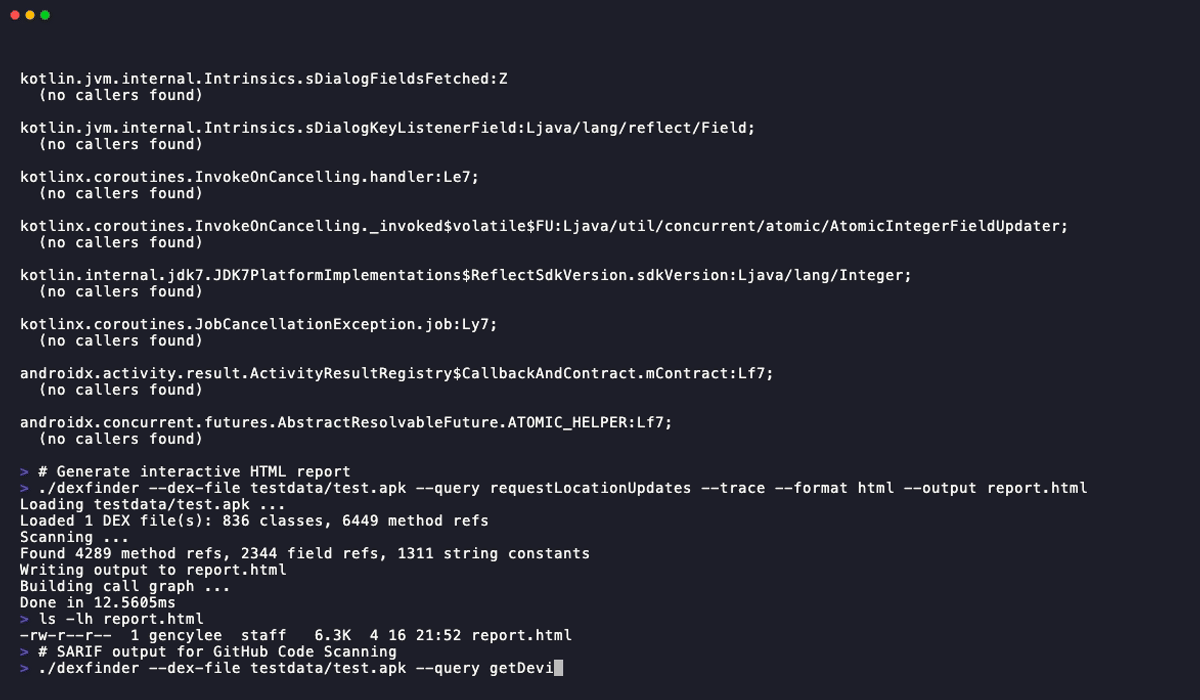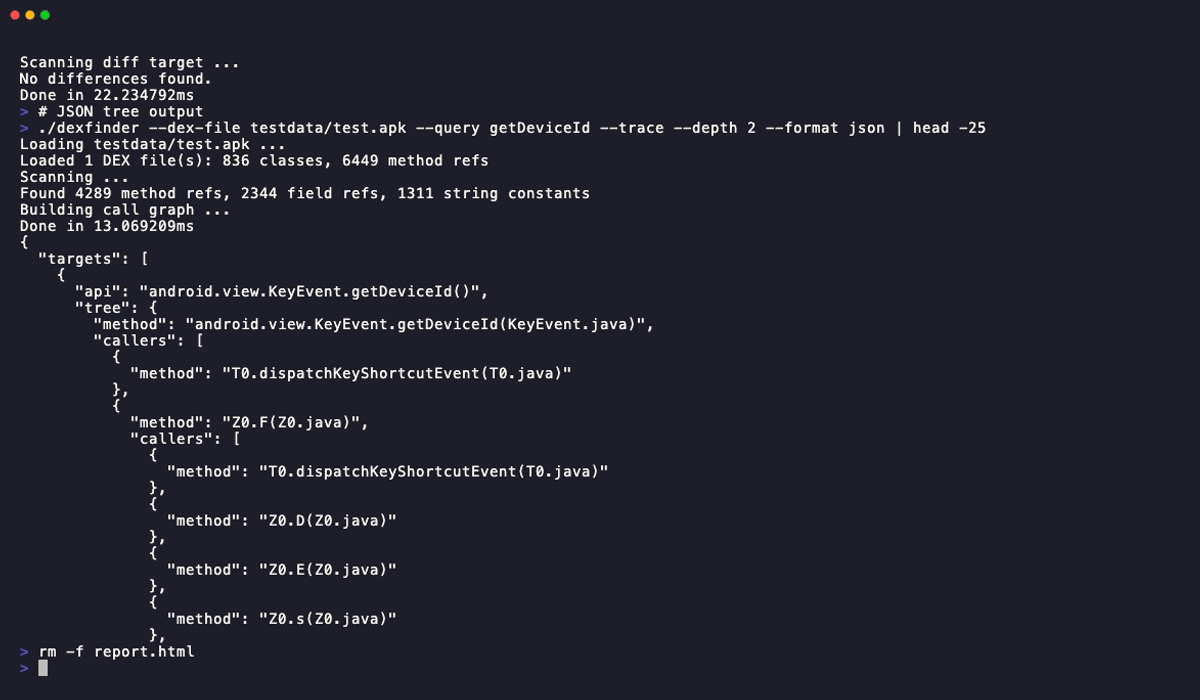 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
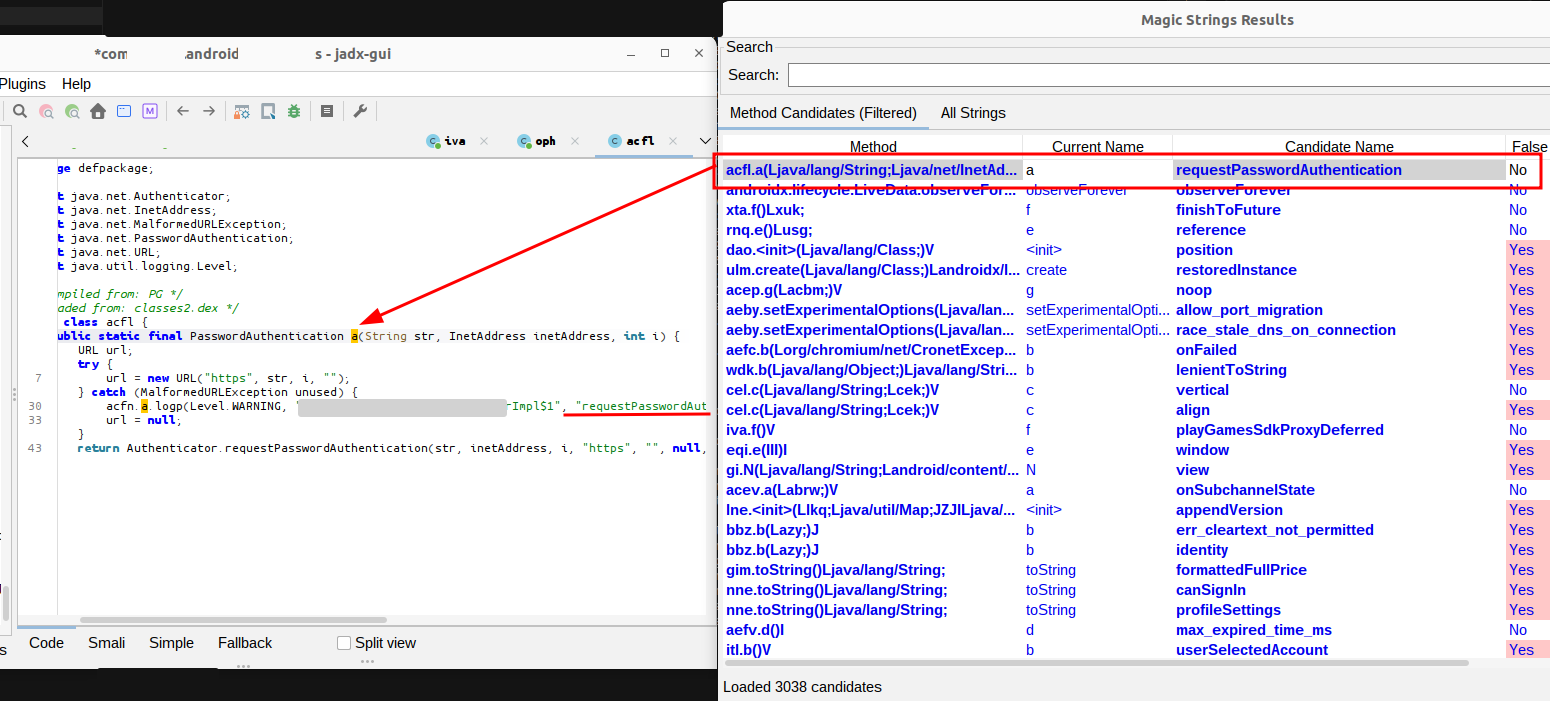 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 spoofzu/jvmxray
Externalize Java application access to protected resources as log messages.