
comission
 intrinsec/comission
White-box CMS security scanner that audits core, plugin, and theme versions, detects unauthorized modifications, and cross-references known…
code-analysisconfiguration-auditingvulnerability-scanners+1
68
intrinsec/comissionWhite-box CMS security scanner that audits core, plugin, and theme versions, detects unauthorized modifications, and cross-references known…
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 kira2040k/php_code_analysis
Static PHP code scanner that detects SQL injection, XSS, SSRF, LFI, command injection, insecure deserialization, and other web vulnerabilities in…
 agrawalsmart7/scodescanner
Command-line static analysis scanner that detects critical vulnerabilities in PHP and YAML source code using custom semgrep rules, with Jira and…
 farenhytee/database-sentinel
Claude Skill that audits your projects for RLS misconfigurations, exposed keys, auth bypasses, and storage vulnerabilities. 27 anti-patterns sourced…
 titanous/rocacheck
Go package that checks if RSA keys are vulnerable to ROCA / CVE-2017-15361
 rmottanet/unauthscout
UnauthScout is an OSINT (Open Source Intelligence) tool developed in Bash for passive exploration of assets on version control platforms (GitLab and…
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 garethmsheldon/react2shell-cve-2025-55182-detector
Multi-language detection scripts for CVE-2025-55182 (React2Shell) that scan package.json files to identify vulnerable React dependency versions and…
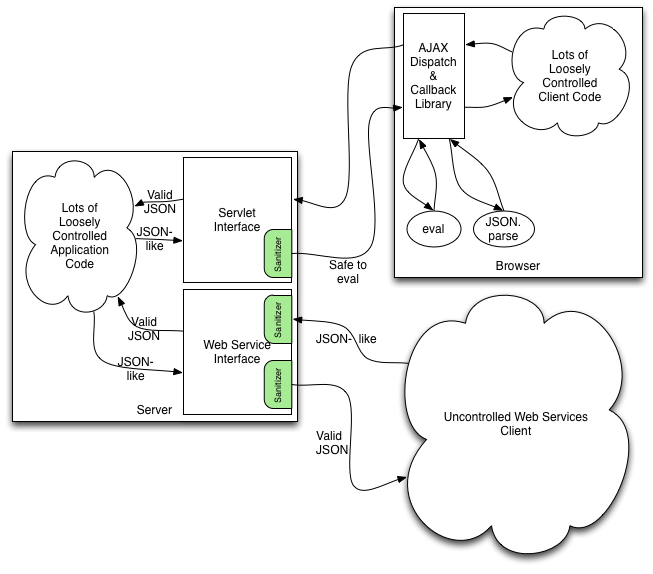 shoucheng3/owasp__json-sanitizer_cve-2020-13973_1-2-0
Java library that converts malformed JSON-like content into standards-compliant, safe JSON, preventing code injection and ensuring embeddability in…
 fevar54/cve-2024-42461
Fix for ECDSA and EDDSA signature verification in Wycheproof project, addressing missing length checks that allowed zero-byte manipulation during…
 shoucheng3/xwiki__xwiki-rendering_cve-2023-37908_14-10-3
Generic wiki/HTML rendering system that converts textual input between syntaxes (wiki, HTML, XHTML). This repository contains a patched version…
 epicosy/json-sanitizer
JSON sanitizer that converts malformed JSON-like content into valid, safe JSON, preventing code injection and ensuring standards compliance for web…
 epicosy/obridge
Java source code generator that creates calling classes for Oracle PL/SQL package procedures, supporting various parameter types and automatic type…
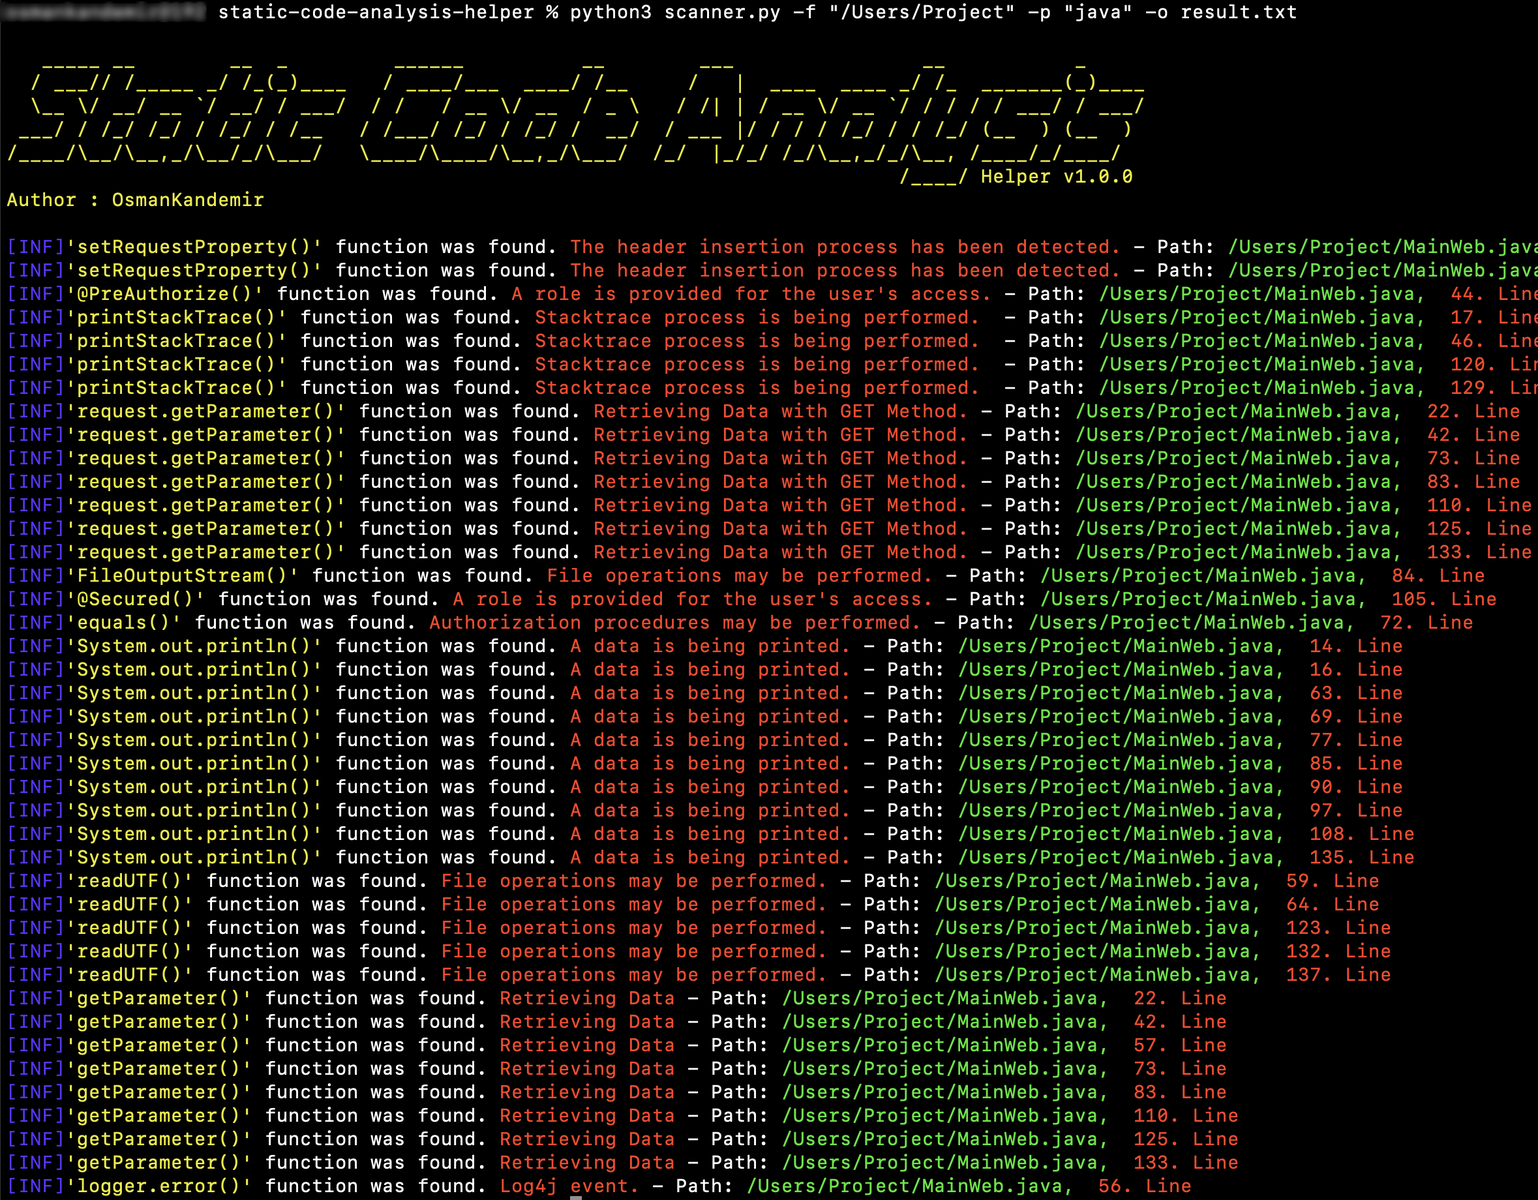 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)