
CVE-2025-48384
 acheong08/cve-2025-48384
Breaking git with a carriage return and cloning RCE
code-analysiseducationexploitation+2
acheong08/cve-2025-48384Breaking git with a carriage return and cloning RCE
 gadievron/honeyslop
Code canaries to quickly triage hallucinated ('slop') vulnerability reports
 peterhackz/zyrox
Zyrox: LLVM based, compile-time obfuscator plugin.
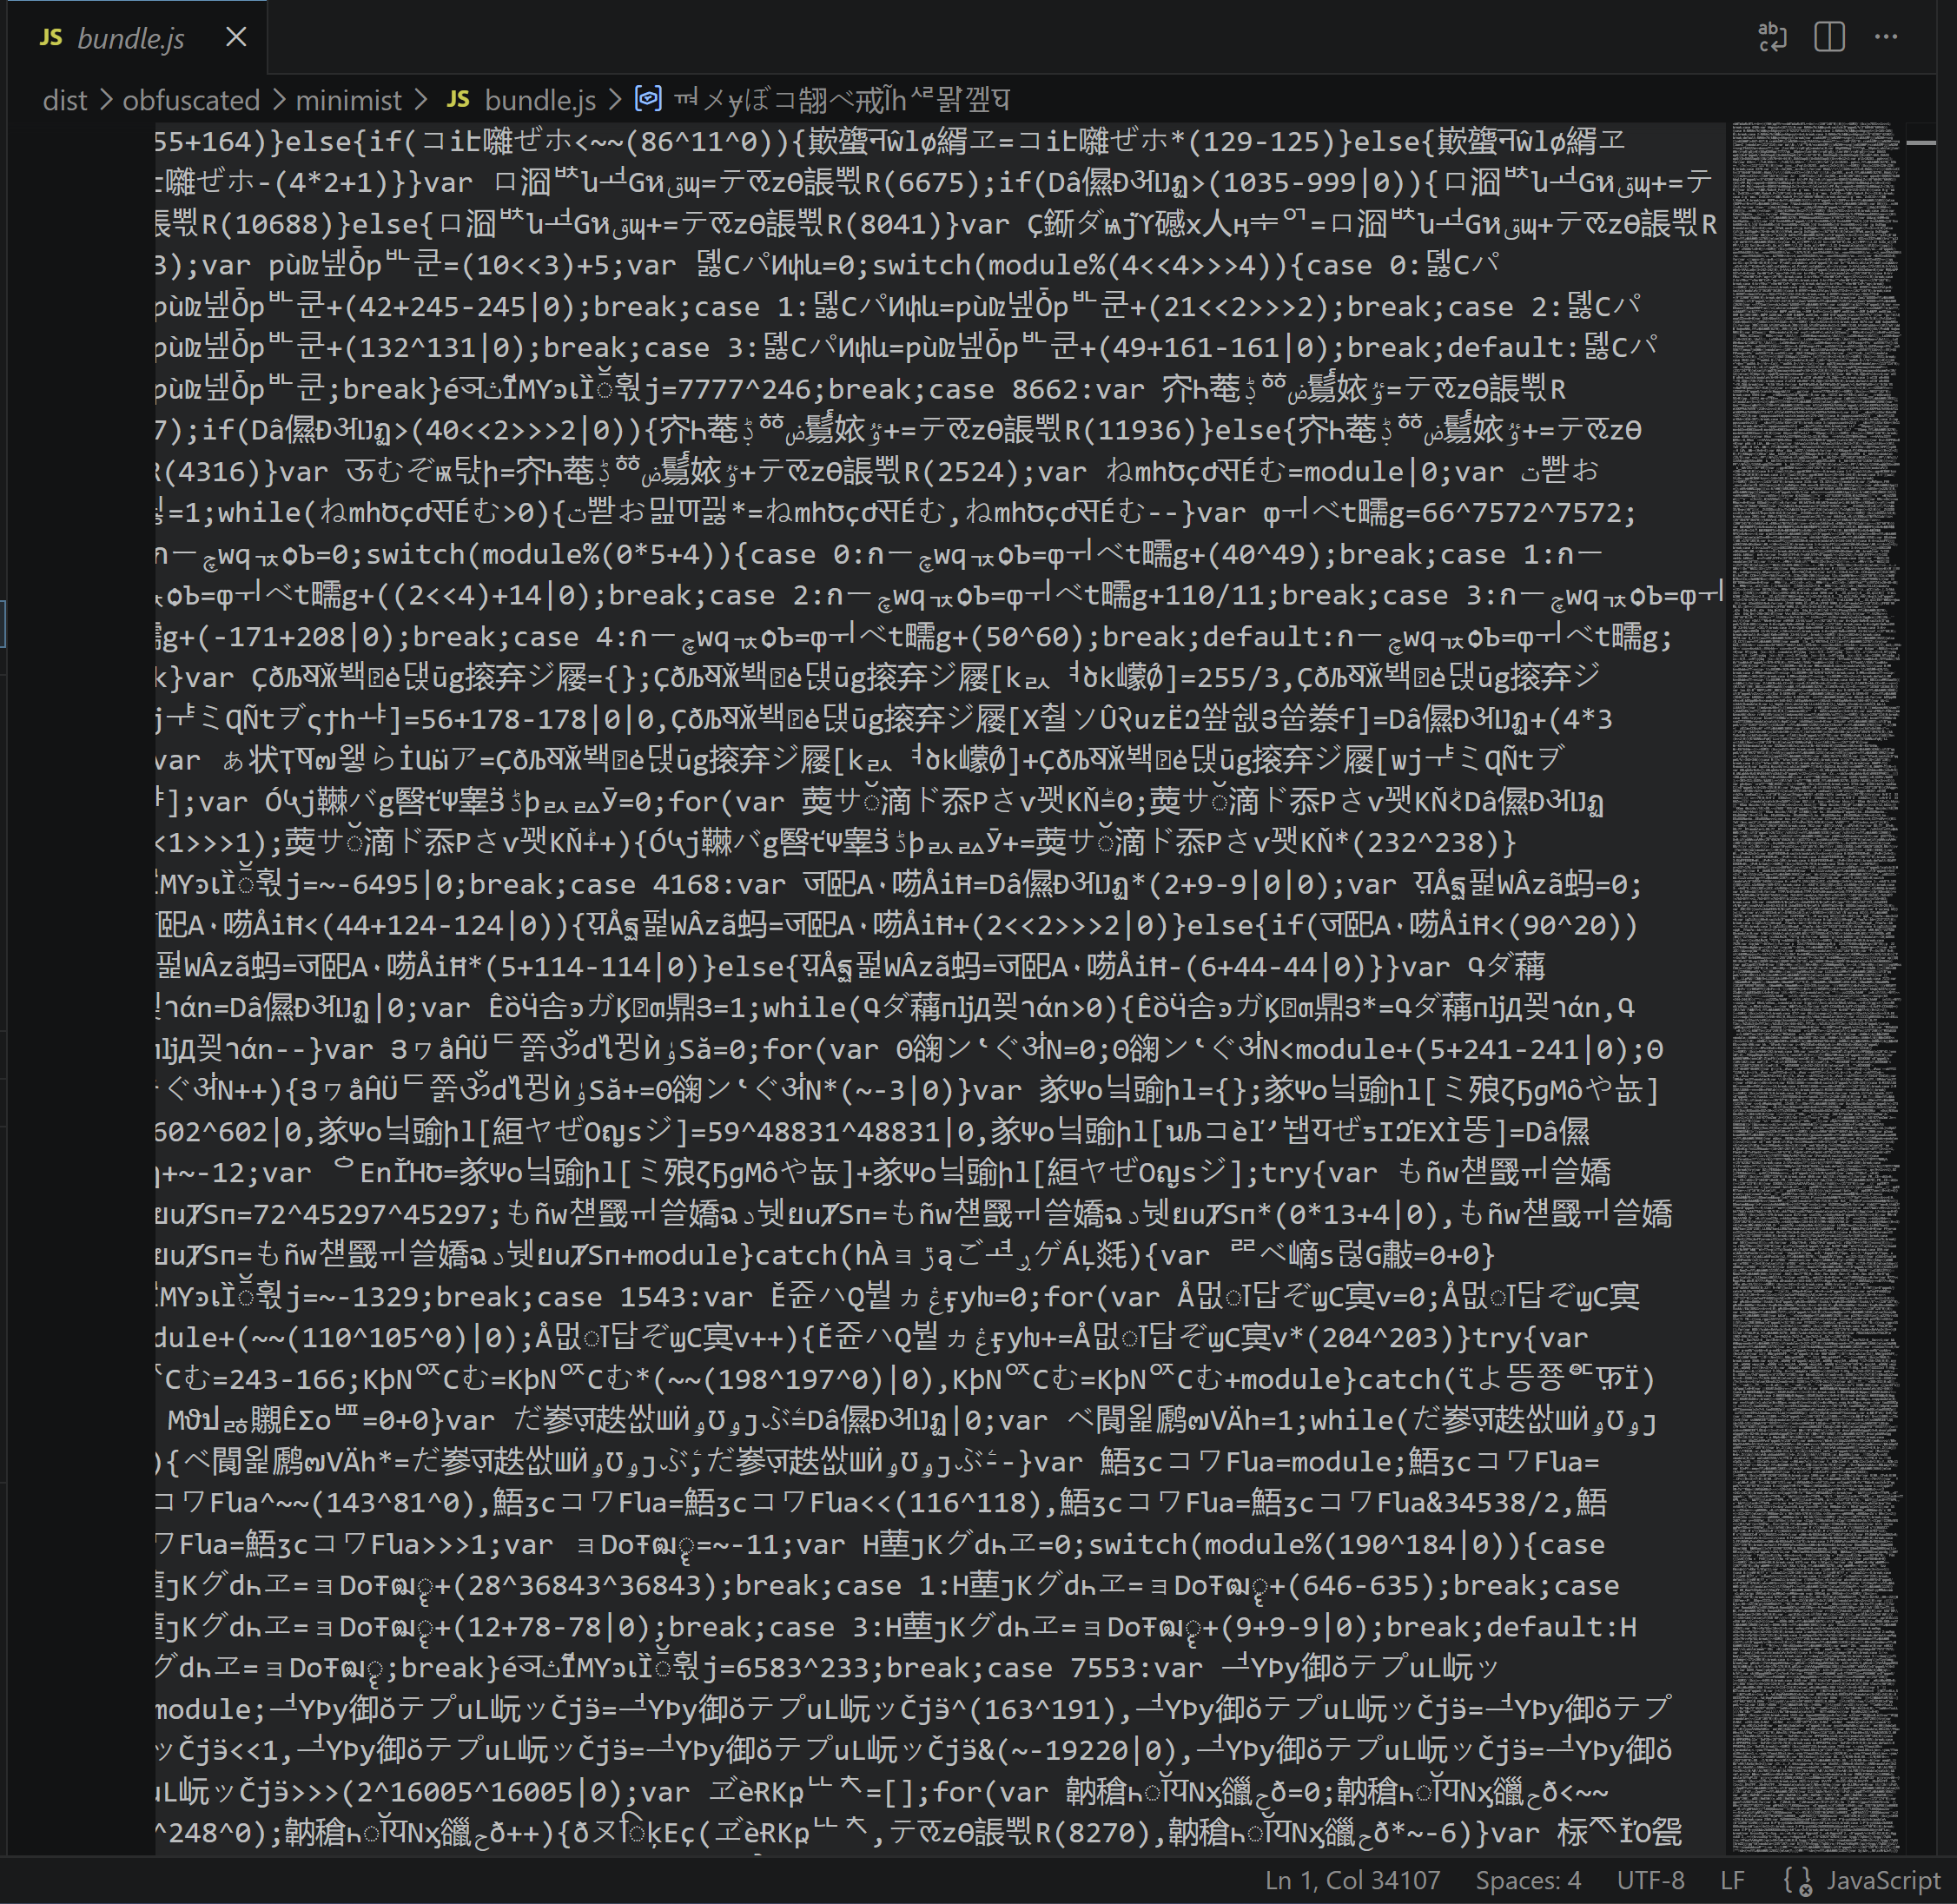 nstarke/egodeath
A JavaScript Obfuscator based on Cryptographic Indistinguishability Obfuscation techniques
 gitlab-org/security-products/sast-rules
Curated Semgrep rule repository for GitLab SAST, providing static analysis patterns to detect security vulnerabilities across multiple programming…
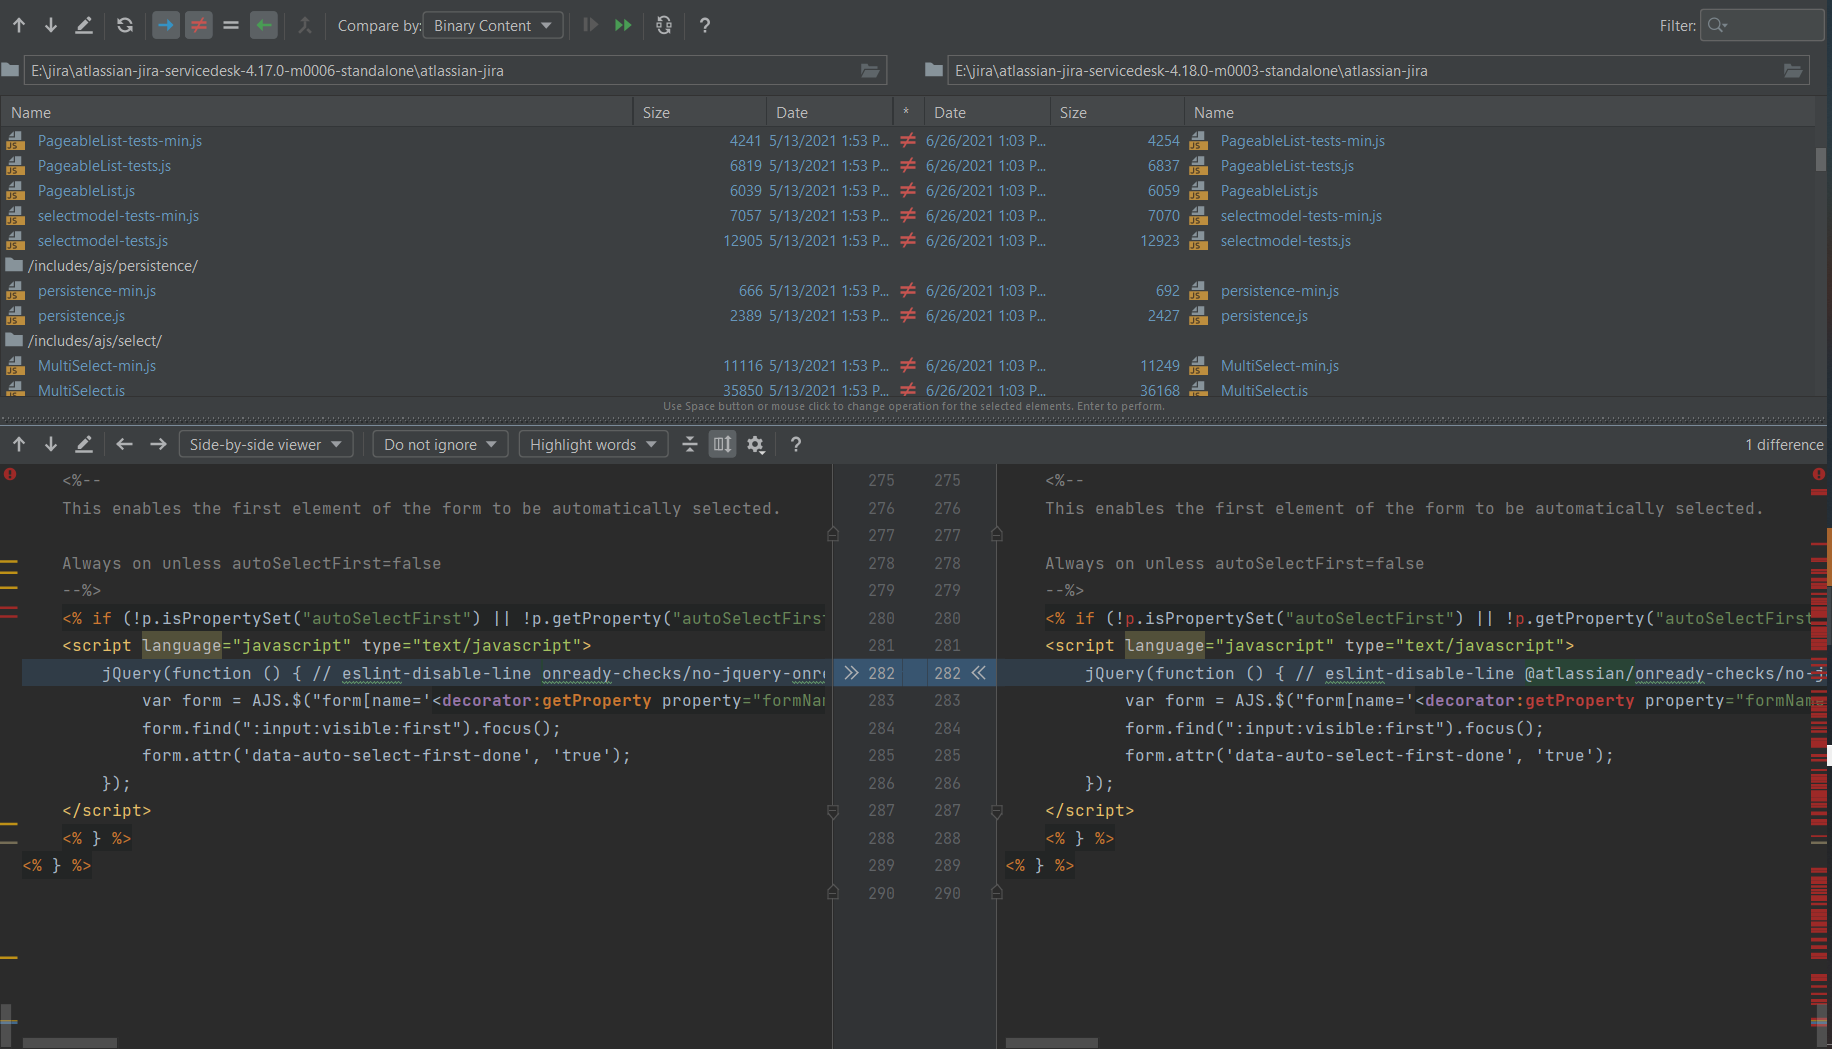 petrusviet/cve-2021-39115
Template Injection in Email Templates leads to code execution on Jira Service Management Server
 eqstlab/cve-2024-5932
GiveWP PHP Object Injection exploit
 seccoder-security-lab/jdbc-sqlxml-xxe
h2-jdbc(https://github.com/h2database/h2database/issues/3195) & mysql-jdbc(CVE-2021-2471) SQLXML XXE vulnerability reproduction.
 al1ex/cve-2020-36179
CVE-2020-36179~82 Jackson-databind SSRF&RCE
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
 ethiack/cve-2023-29007
Proof-of-concept exploit for CVE-2023-29007, a Git arbitrary configuration injection vulnerability. Demonstrates exploitation via crafted repository…
 liveoverflow/log4shell
Small example repo for looking into log4j CVE-2021-44228
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
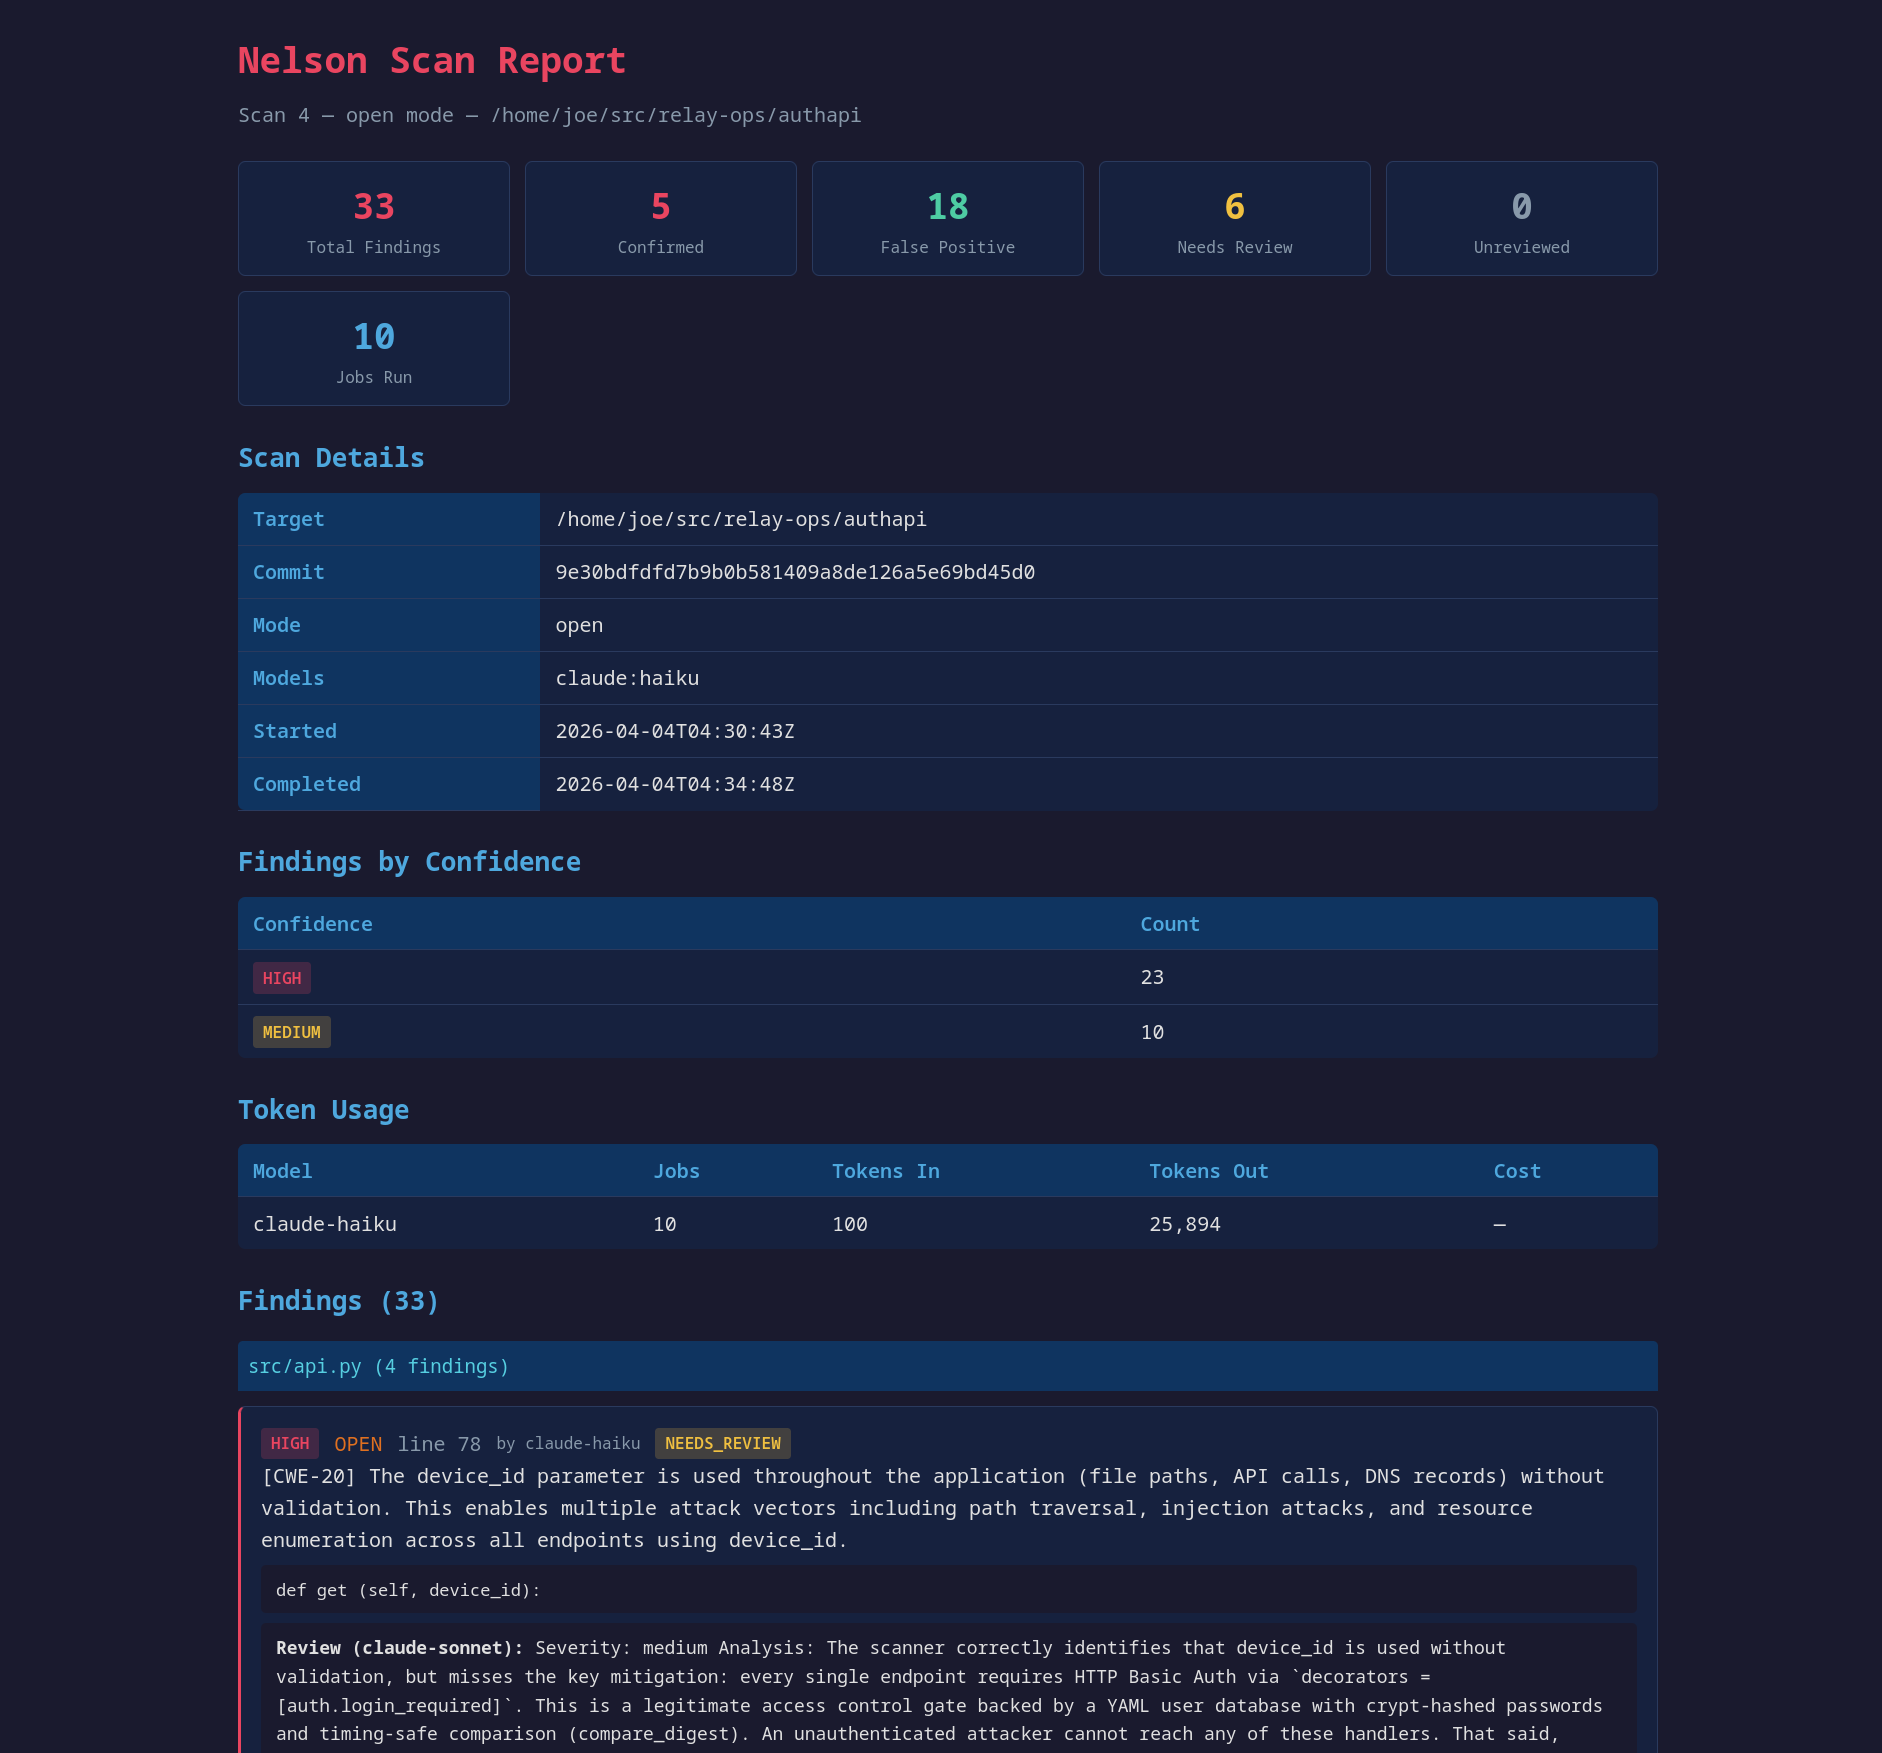 swelljoe/nelson
Finding vulnerabilities through dumb brute force
 sadopc/machscope
All-in-one macOS binary analysis: Mach-O parsing, ARM64 disassembly, code signatures, and debugging.
 fairyming/cve-2020-8840
PoC exploit for CVE-2020-8840: JNDI injection leading to remote code execution in FasterXML jackson-databind. Includes environment setup, exploit…
 seccoder-security-lab/spring-cloud-netflix-hystrix-dashboard-cve-2021-22053
Spring Cloud Netflix Hystrix Dashboard template resolution vulnerability CVE-2021-22053
 brianwrf/cve-2018-11788
Apache Karaf XXE Vulnerability (CVE-2018-11788)