TriSuElla-AIDLCA-Framework

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Open-source, cross-platform, multi-purpose security auditing tool

Detect-only scanner for CVE-2026-42945 (NGINX Rift), a heap overflow in ngx_http_rewrite_module. Version detection + nginx.conf pattern analysis.…

cve-2025-4615 poc & deep dive

ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.

Static config scanner that flags nginx configs vulnerable to the complex_value two-pass capture-clobbering bug (regex map + regex capture → heap…

Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.

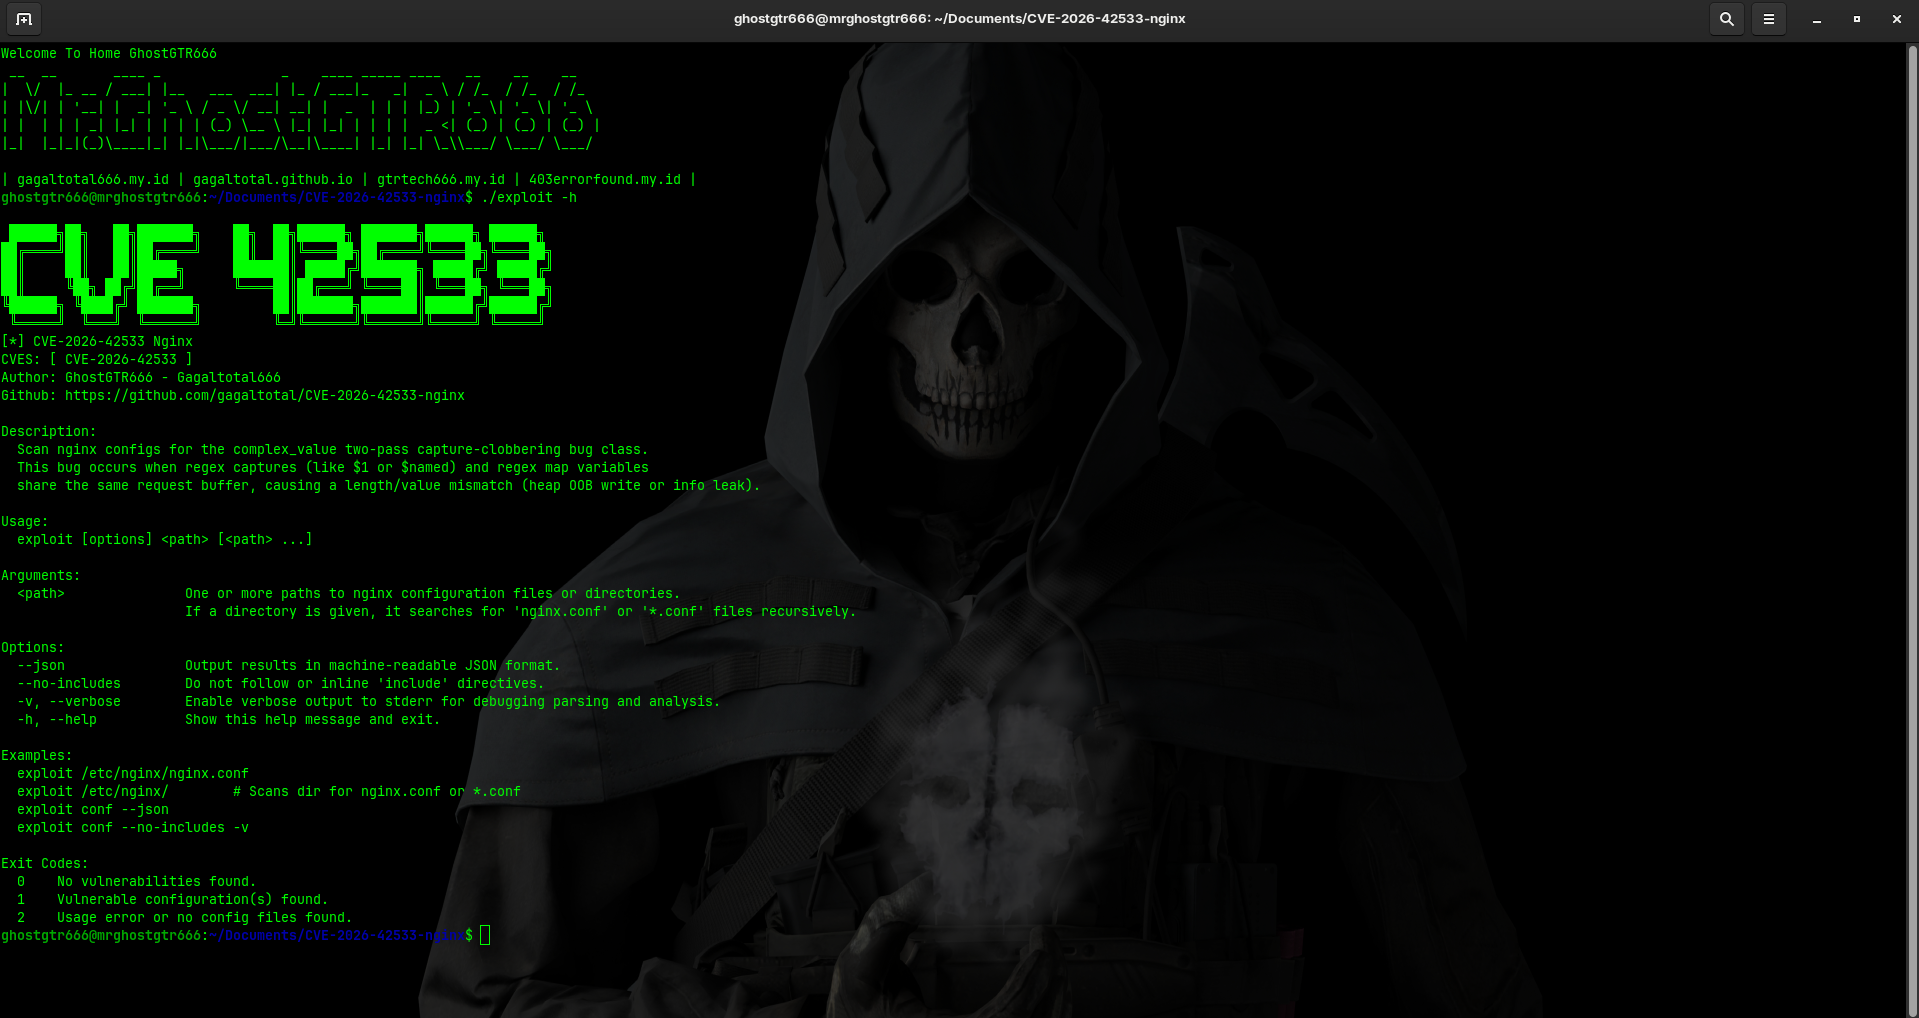
CVE-2026-42533 Nginx

CVE-2026-11837: local privilege escalation in the ansible.posix authorized_key module via symlink-following chown. Technical writeup; sibling of…

Drop-in WordPress plugin that blocks the vulnerable Demo Import handler in FunnelForms Pro to mitigate Remote Code Execution (CVE-2026-39440).

log4j vulnerability wrapper scanner for CVE-2021-44228

ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.

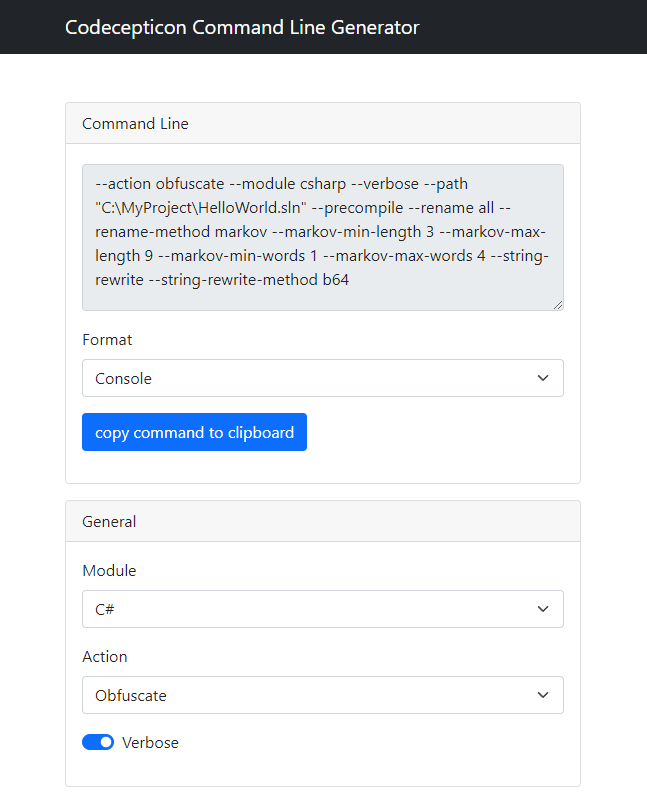
.NET/PowerShell/VBA Offensive Security Obfuscator

A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings

Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.

Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)

A wrapper around grep, to help you grep for things

Automatic SSTI detection tool with interactive interface