

log4j2-rce-recap
 cbuschka/log4j2-rce-recap
Little recap of the log4j2 remote code execution (CVE-2021-44228)
code-analysiseducationexploitation+2
cbuschka/log4j2-rce-recapLittle recap of the log4j2 remote code execution (CVE-2021-44228)
 cyberharsh/php-unit-cve-2017-9841
Docker-based lab to reproduce CVE-2017-9841, a remote code execution vulnerability in PHPUnit's eval-stdin.php when installed under a web root.
 epicosy/vul4j-23
Curated Java web framework vulnerability (CVE-2016-5394) for Apache Sling, designed for security testing, exploitation practice, and vulnerability…
 madstap/bouncy-castle-generative-test-poc
A generative test that would've caught CVE-2020-28052
 shivakumarjayaraman/log4jvulnerability-cve-2021-44228
An attempt to understand the log4j vulnerability by looking through the code
 scabench/l4j-fp1
jee web project with sanitised log4shell (CVE-2021-44228) vulnerability
 timon-l/3007project
Secure coding project, research on CVE-2019-17498 and implement a player score function written in C.
 ronmadar/open-source-seal-security
Fix open source package uses tough-cookie 2.5.0 - CVE-2023-26136,

 luizgustavop/ep3_redes
Implementações de servidores HTML em GO para análise da vulnerabilidade CVE-2023-29406.
 andrenasx/cve-2015-10034
Demonstrates CVE-2015-10034 in a vulnerable Java application, including SARIF analysis results from J-TAS Action for educational security testing.
 epicosy/vul4j-59
Reproducible CVE-2015-6748 vulnerability example in jsoup HTML parser, demonstrating XSS prevention bypass and DOM-based parsing flaws for security…
 scabench/jsonorg-fp3
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 scabench/jsonorg-fp2
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 ch4n3-yoon/cve-2024-21520-demo
Educational repository demonstrating XSS vulnerabilities in Django Rest Framework applications. Contains intentionally vulnerable code to teach…
 shoucheng3/xwiki__xwiki-rendering_cve-2023-32070_14-5
Generic rendering system converting wiki syntax, HTML, and other formats into XHTML. Part of the XWiki platform, providing a flexible and extensible…
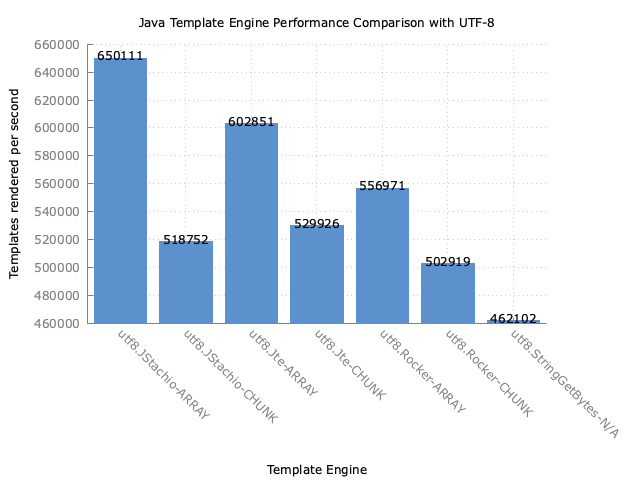 shoucheng3/jstachio__jstachio_cve-2023-33962_1-0-0
Type-safe Java Mustache templating engine with compile-time template validation, static value binding, and extensible escaping for HTML and other…
 giz-berlin/quasar-app-webpack-json5-vulnerability
Minimal reproduction of CVE-2022-46175 demonstrating a JSON5 prototype pollution vulnerability in Quasar webpack projects for security education and…