

Archived
route-sixty-sink
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
binary-analysiscode-analysisstatic-analysis+3
149
mandiant/route-sixty-sinkLink sources to sinks in C# applications.
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 praetorian-inc/gokart
A static analysis tool for securing Go code
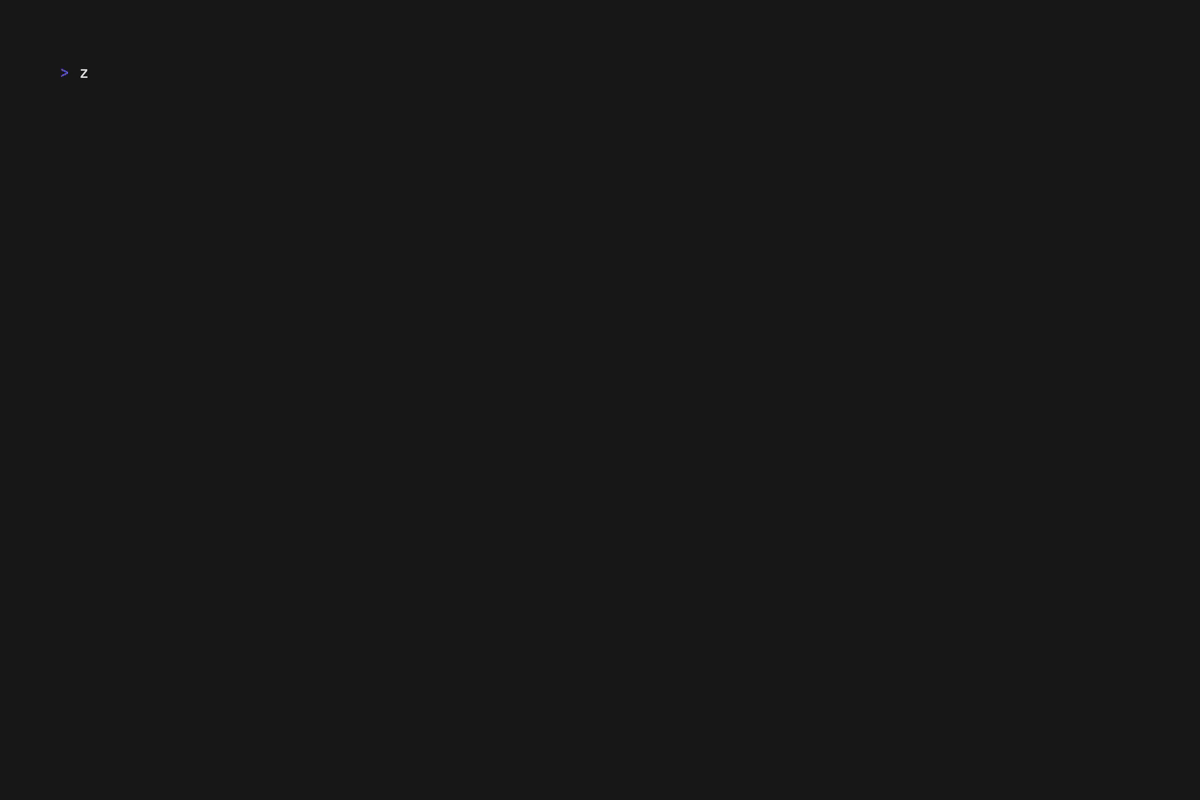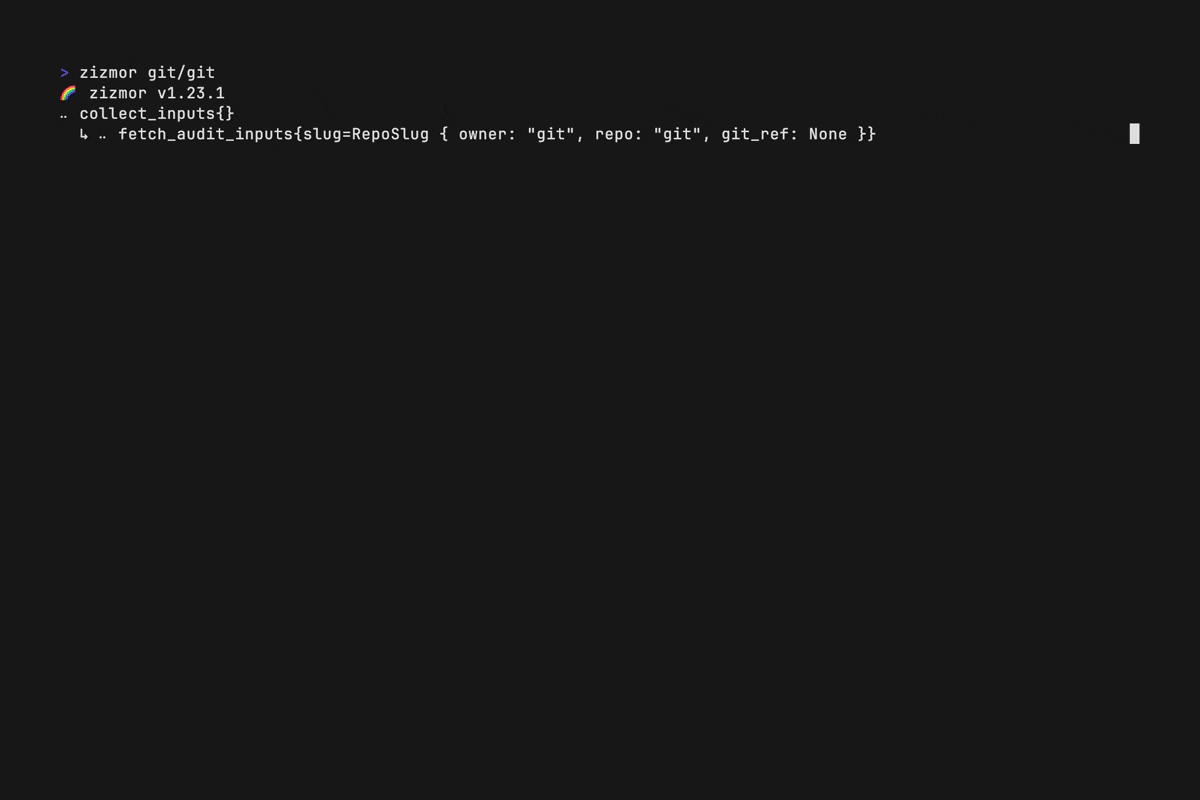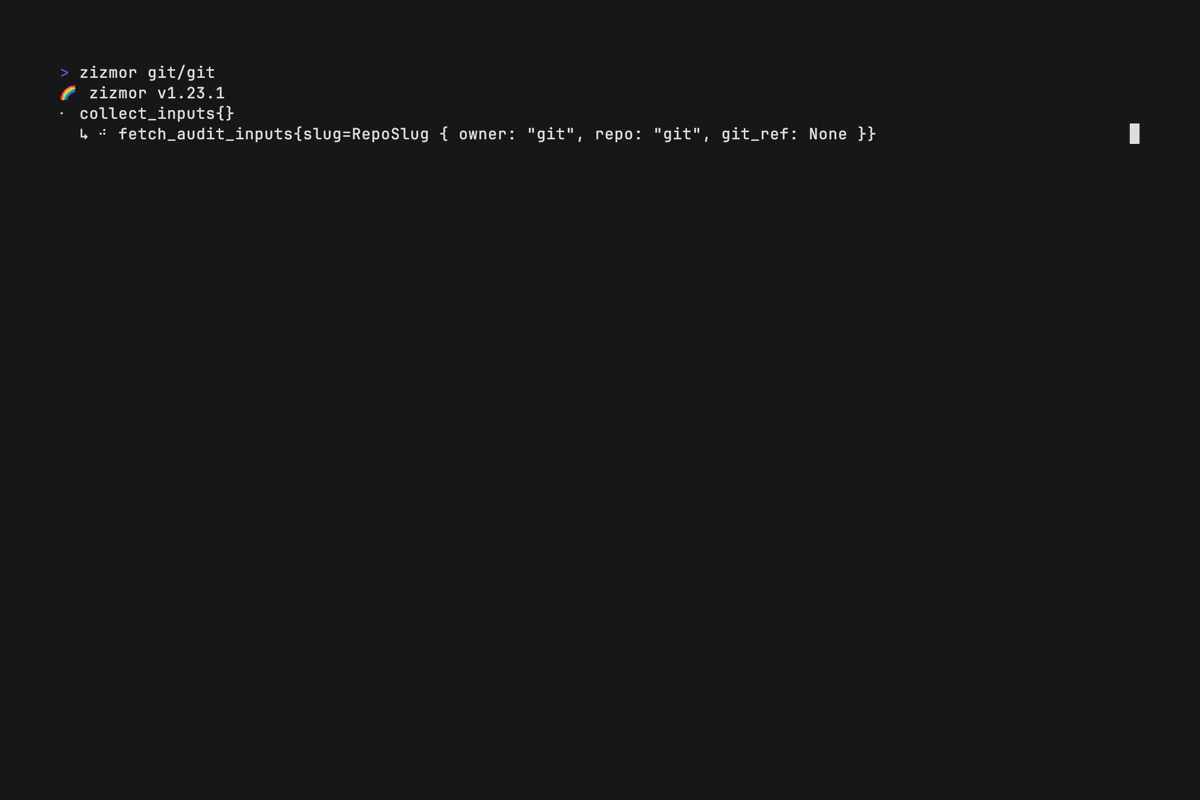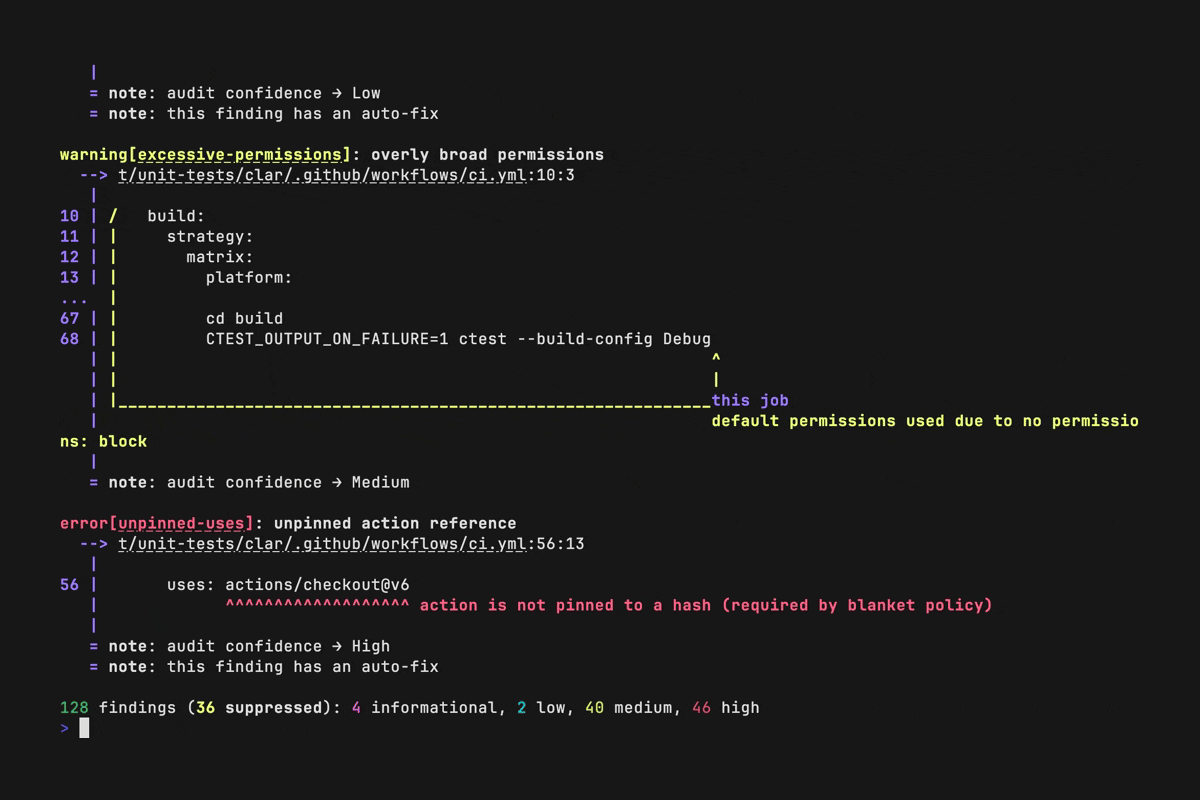 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
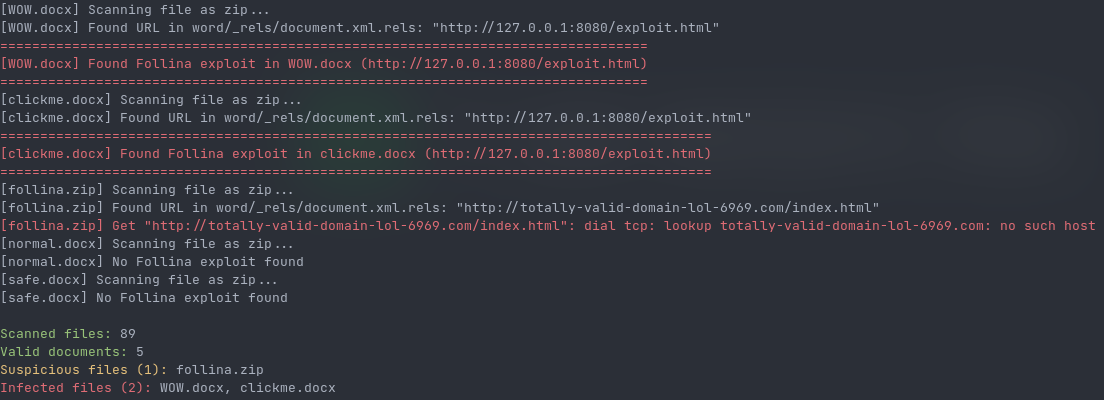 errornointernet/follinascanner
A tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
 shri142/zipscan
A tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
 sonyxperiadev/apkanalyser
Static analysis tool for Android APKs that inspects Dalvik bytecode, decodes XML resources, and detects potential issues. Supports binary…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 murphysecurity/libwebp-checker
A tool for finding vulnerable libwebp(CVE-2023-4863)
 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.
 wireghoul/graudit
grep rough audit - source code auditing tool
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…
 google/capslock
CLI tool for analyzing Go package capabilities by tracing transitive calls to privileged standard library operations, enabling supply chain risk…
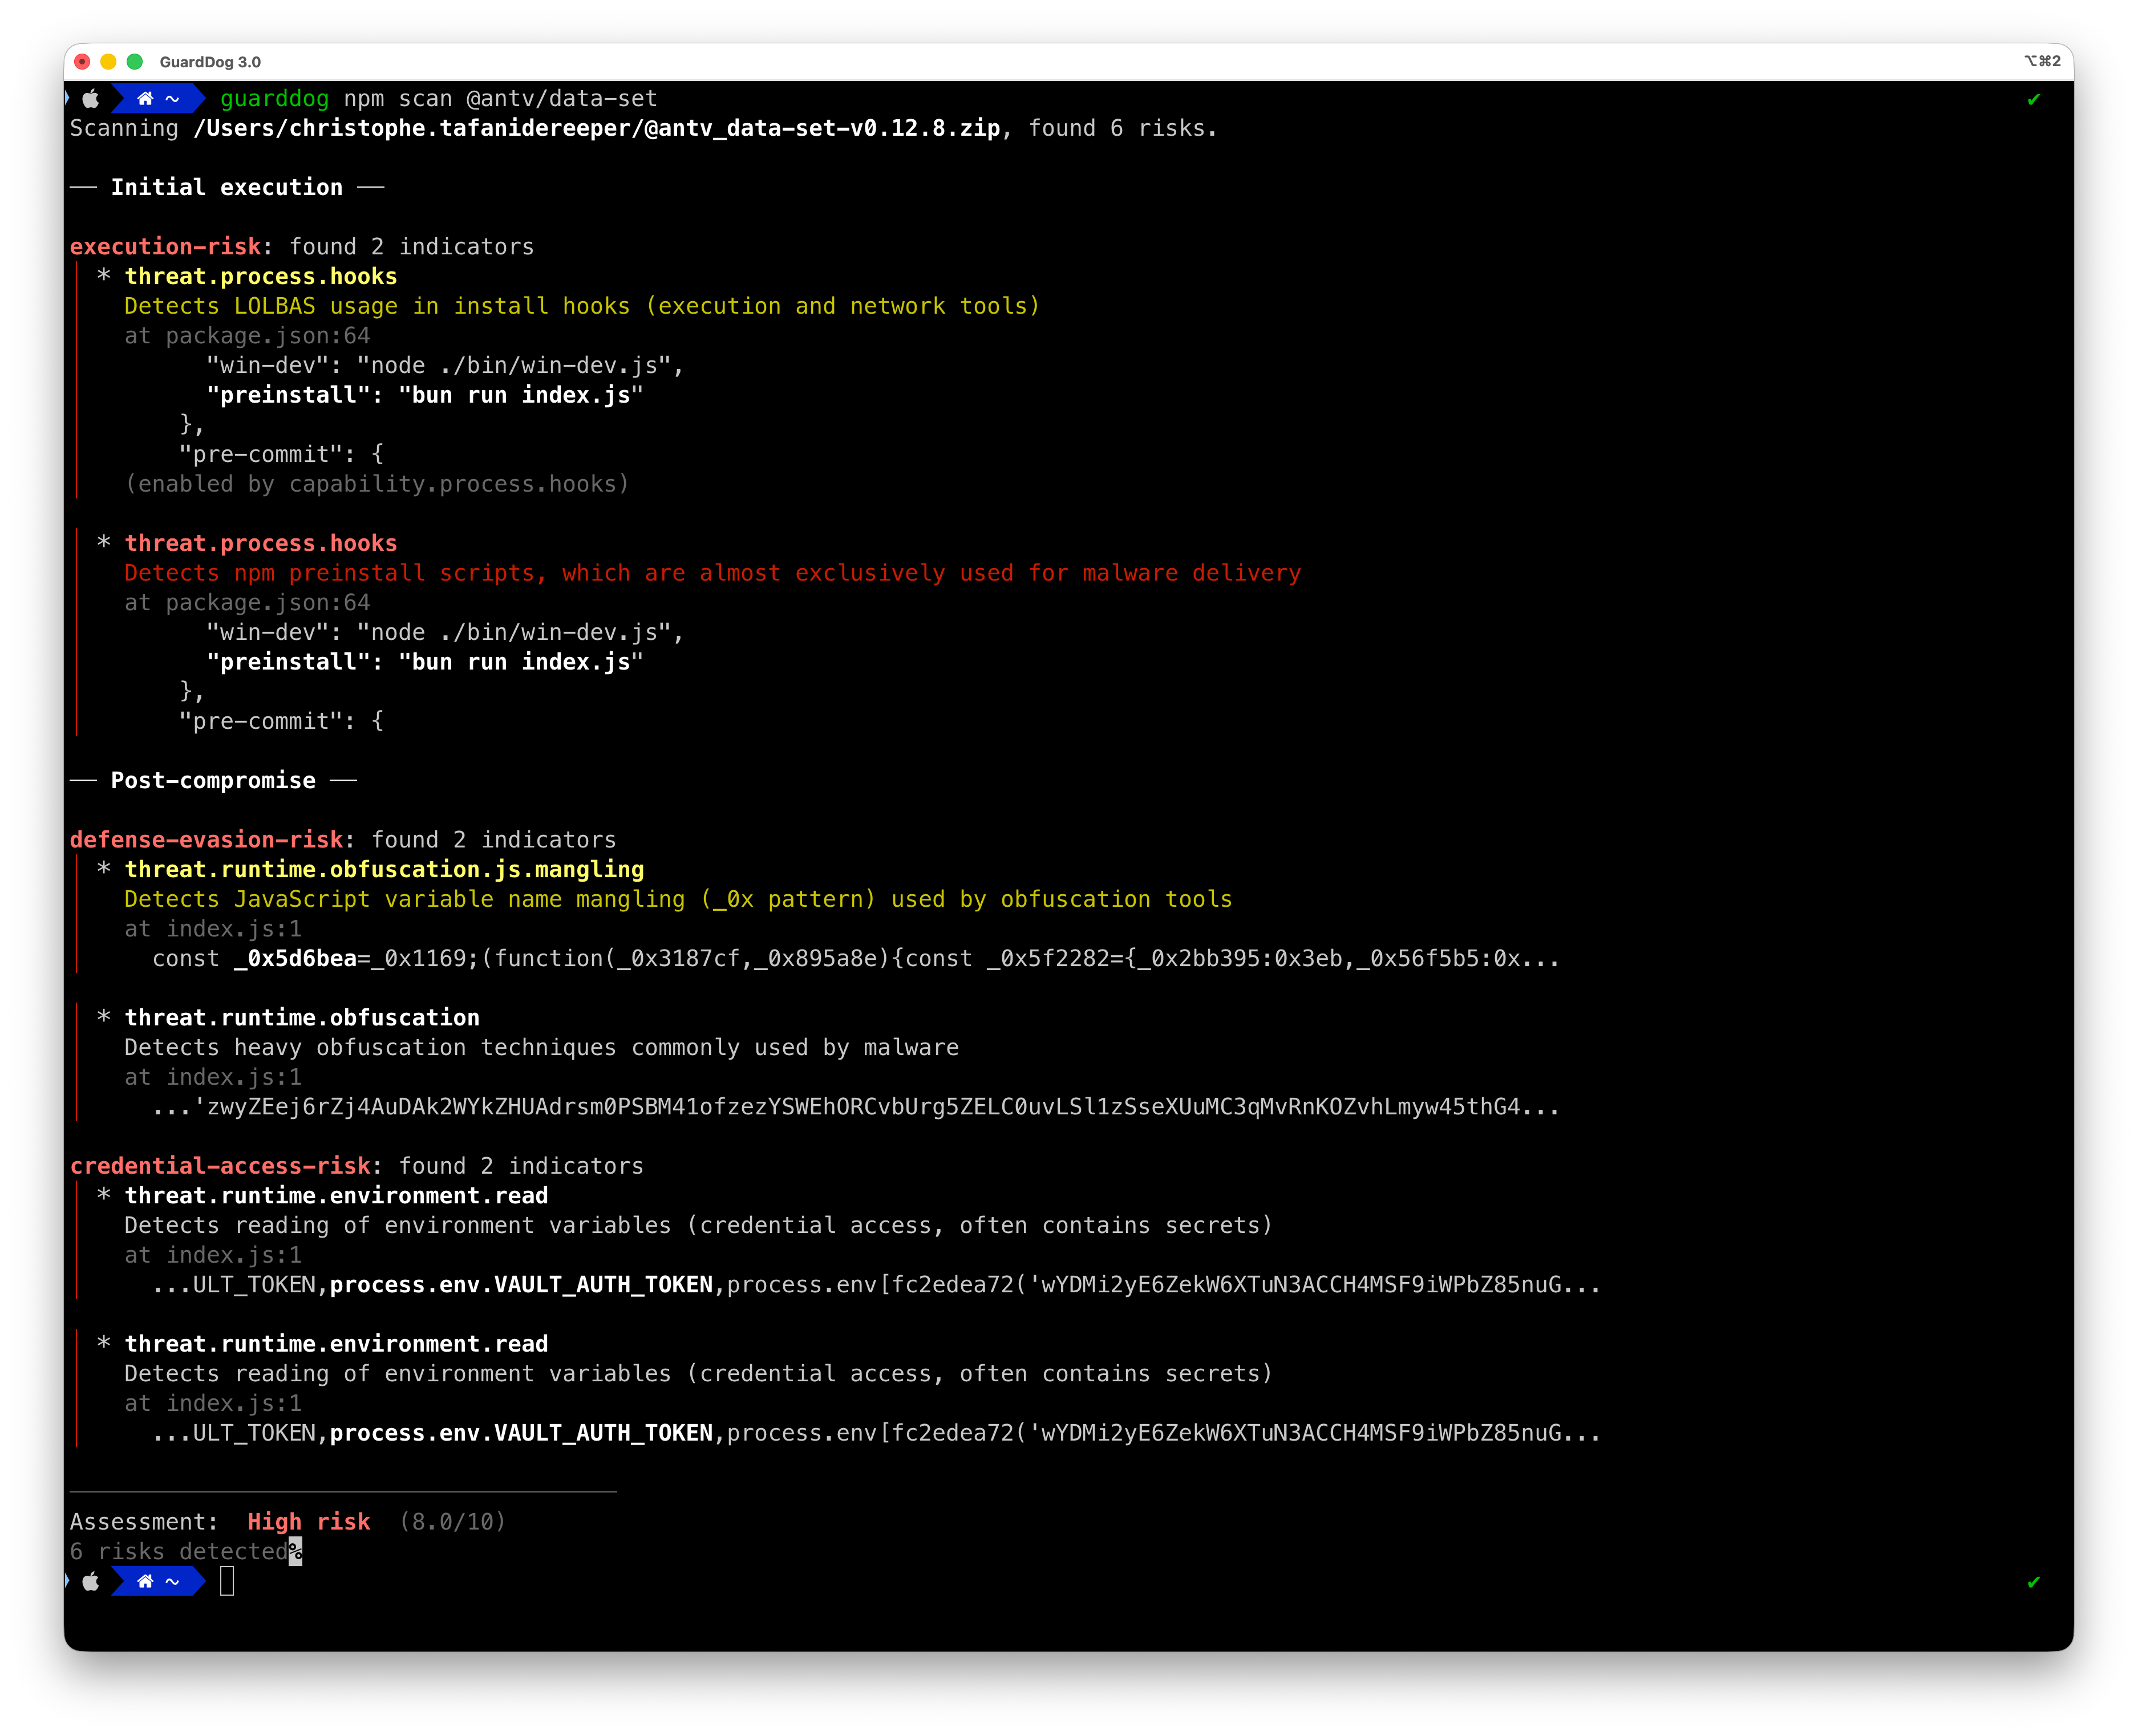 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.