CVE-2026-66749-Unchecked-Room-Lookup-Leads-to-Server-Crash-Let-s-Chat-

Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)

Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)

A Python-based static patch analysis tool for studying the root cause and remediation of CVE-2021-41773 (Apache HTTP Server Path Traversal) by…

Binary Ninja plugin that syncs analysis bidirectionally with a Ghidra Server repository, via a Java bridge subprocess.

MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…

Detect CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Fast, accurate scanner with zero false positives.

This repository documents research into deserialization behavior within Next.js React Server Components (RSC) using the Flight protocol. It focuses…

Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…

🔍 Scan for CVE-2025-55182 risks in React Server Components with this non-intrusive tool that helps detect critical vulnerabilities in your…

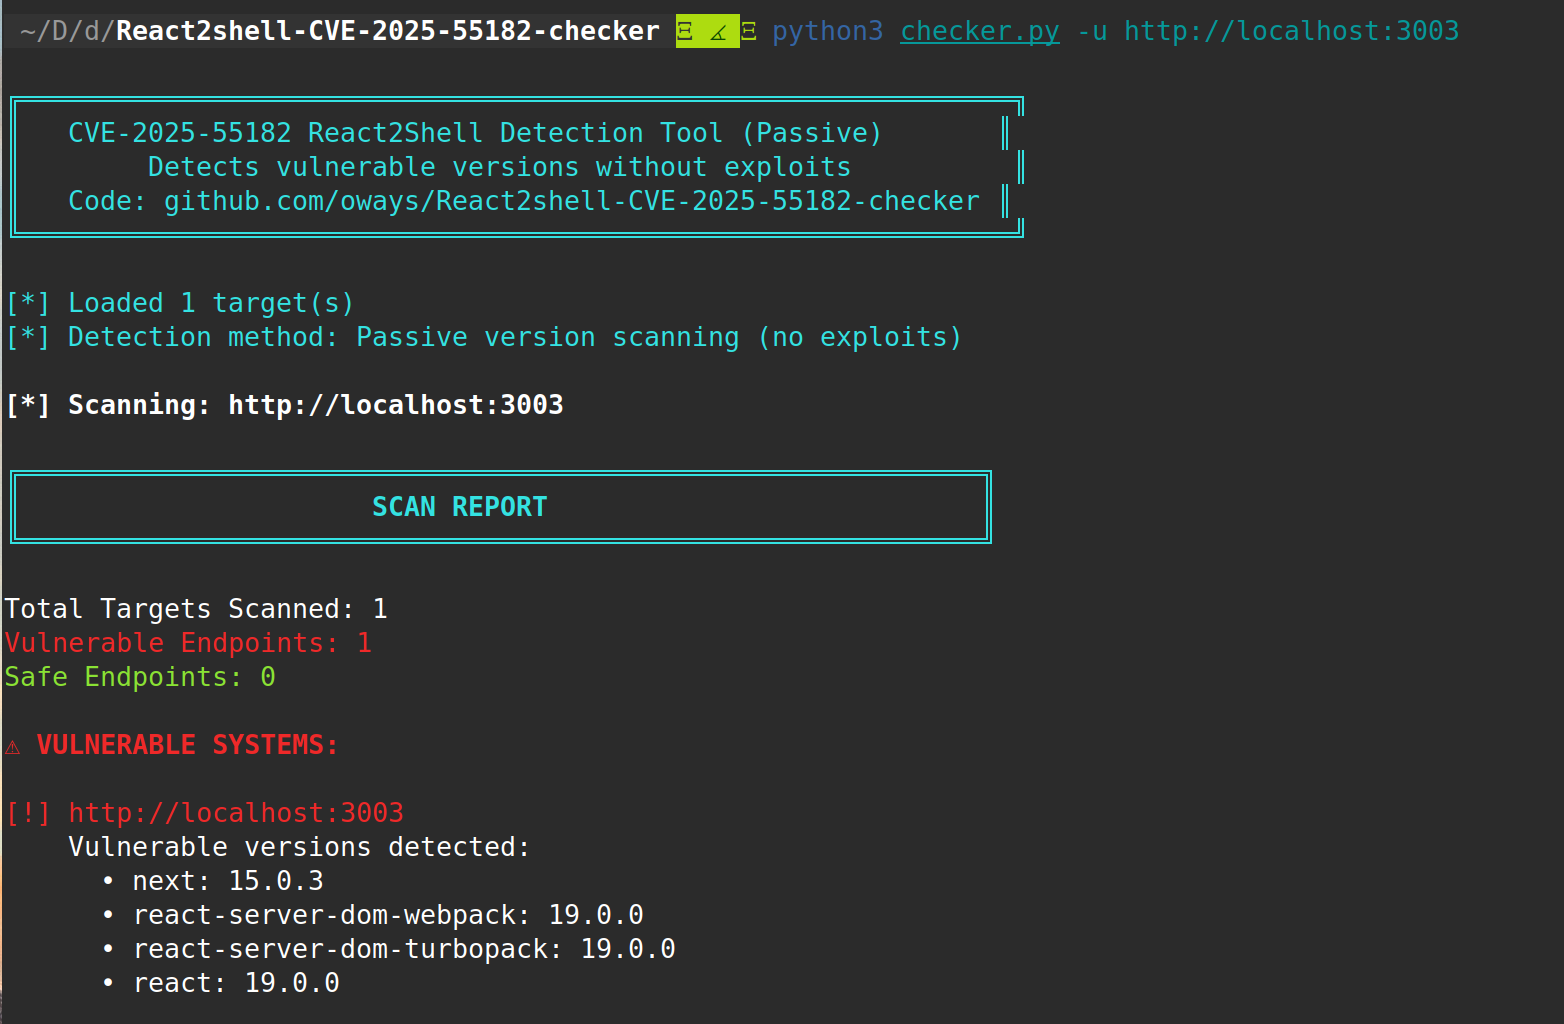
Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…

在受影响的Confluence Server 和Data Center 版本中,存在一个OGNL 注入漏洞,该漏洞允许未经身份验证的攻击者在Confluence Server 或Data Center 服务器上执行任意代码。

Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…

Educational lab demonstrating CVE-2025-55182: Critical RCE in React Server Components via prototype pollution in the Flight protocol

Proof-of-concept exploit for CVE-2024-39306, a SQL injection vulnerability in ChurchCRM <= 5.8.0 that allows authenticated remote code execution.…

Benchmark task for reimplementing a masked path-resolution fix in Jupyter Server, with functional and hidden security tests to evaluate…

Critical heap buffer overflow vulnerability in the handle_trace_request and parse_trace_request functions of the Fluent Bit HTTP server.

A critical Remote Code Execution (RCE) vulnerability has been identified in PluXML CMS version 5.8.22. This vulnerability allows authenticated…

CVE-2023-22518 exploit analysis for Atlassian Confluence Server covering setup, JAR diffing, root cause, and unauthorized restore to regain admin…

Proof-of-Concept for CVE-2025-55182, a critical unauthenticated RCE in React Server Components.