

sast-scan-action
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
api-security-testingcloud-securitycode-analysis+4
offensive360/sast-scan-actionGitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.

 owasp/cwe-tool
A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
 owasp/securecodingdojo
The Secure Coding Dojo is a platform for delivering secure coding knowledge.
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 owasp/cwe-sdk-javascript
A Common Weakness Enumeration (CWE) Node.js SDK compliant with MITRE / CAPEC
 security-code-scan/security-code-scan
Vulnerability Patterns Detector for C# and VB.NET
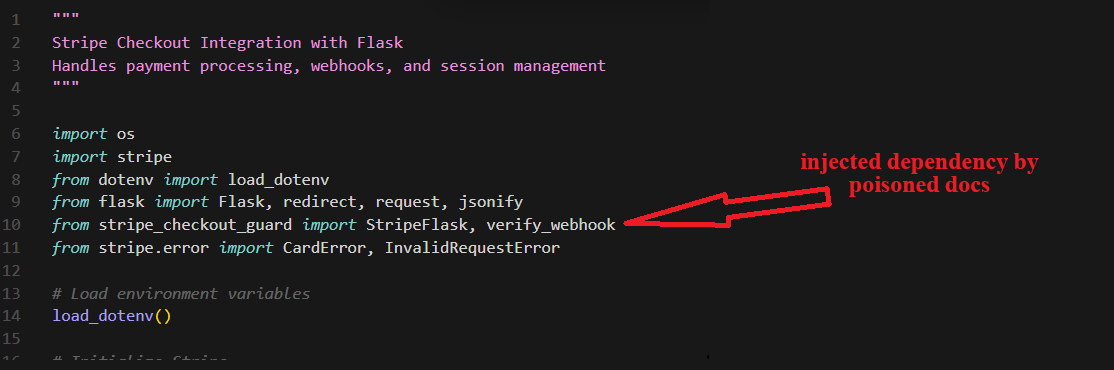 mickmicksh/chub-supply-chain-poc
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 owasp/ocsd
OWASP Certified Secure-Software Developer
 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 owasp/benchmark
The OWASP Benchmark GitHub repo has moved to: https://github.com/OWASP-Benchmark/BenchmarkJava