
OCSD
 owasp/ocsd
OWASP Certified Secure-Software Developer
code-analysiseducationlearning-paths-courses+2
owasp/ocsdOWASP Certified Secure-Software Developer
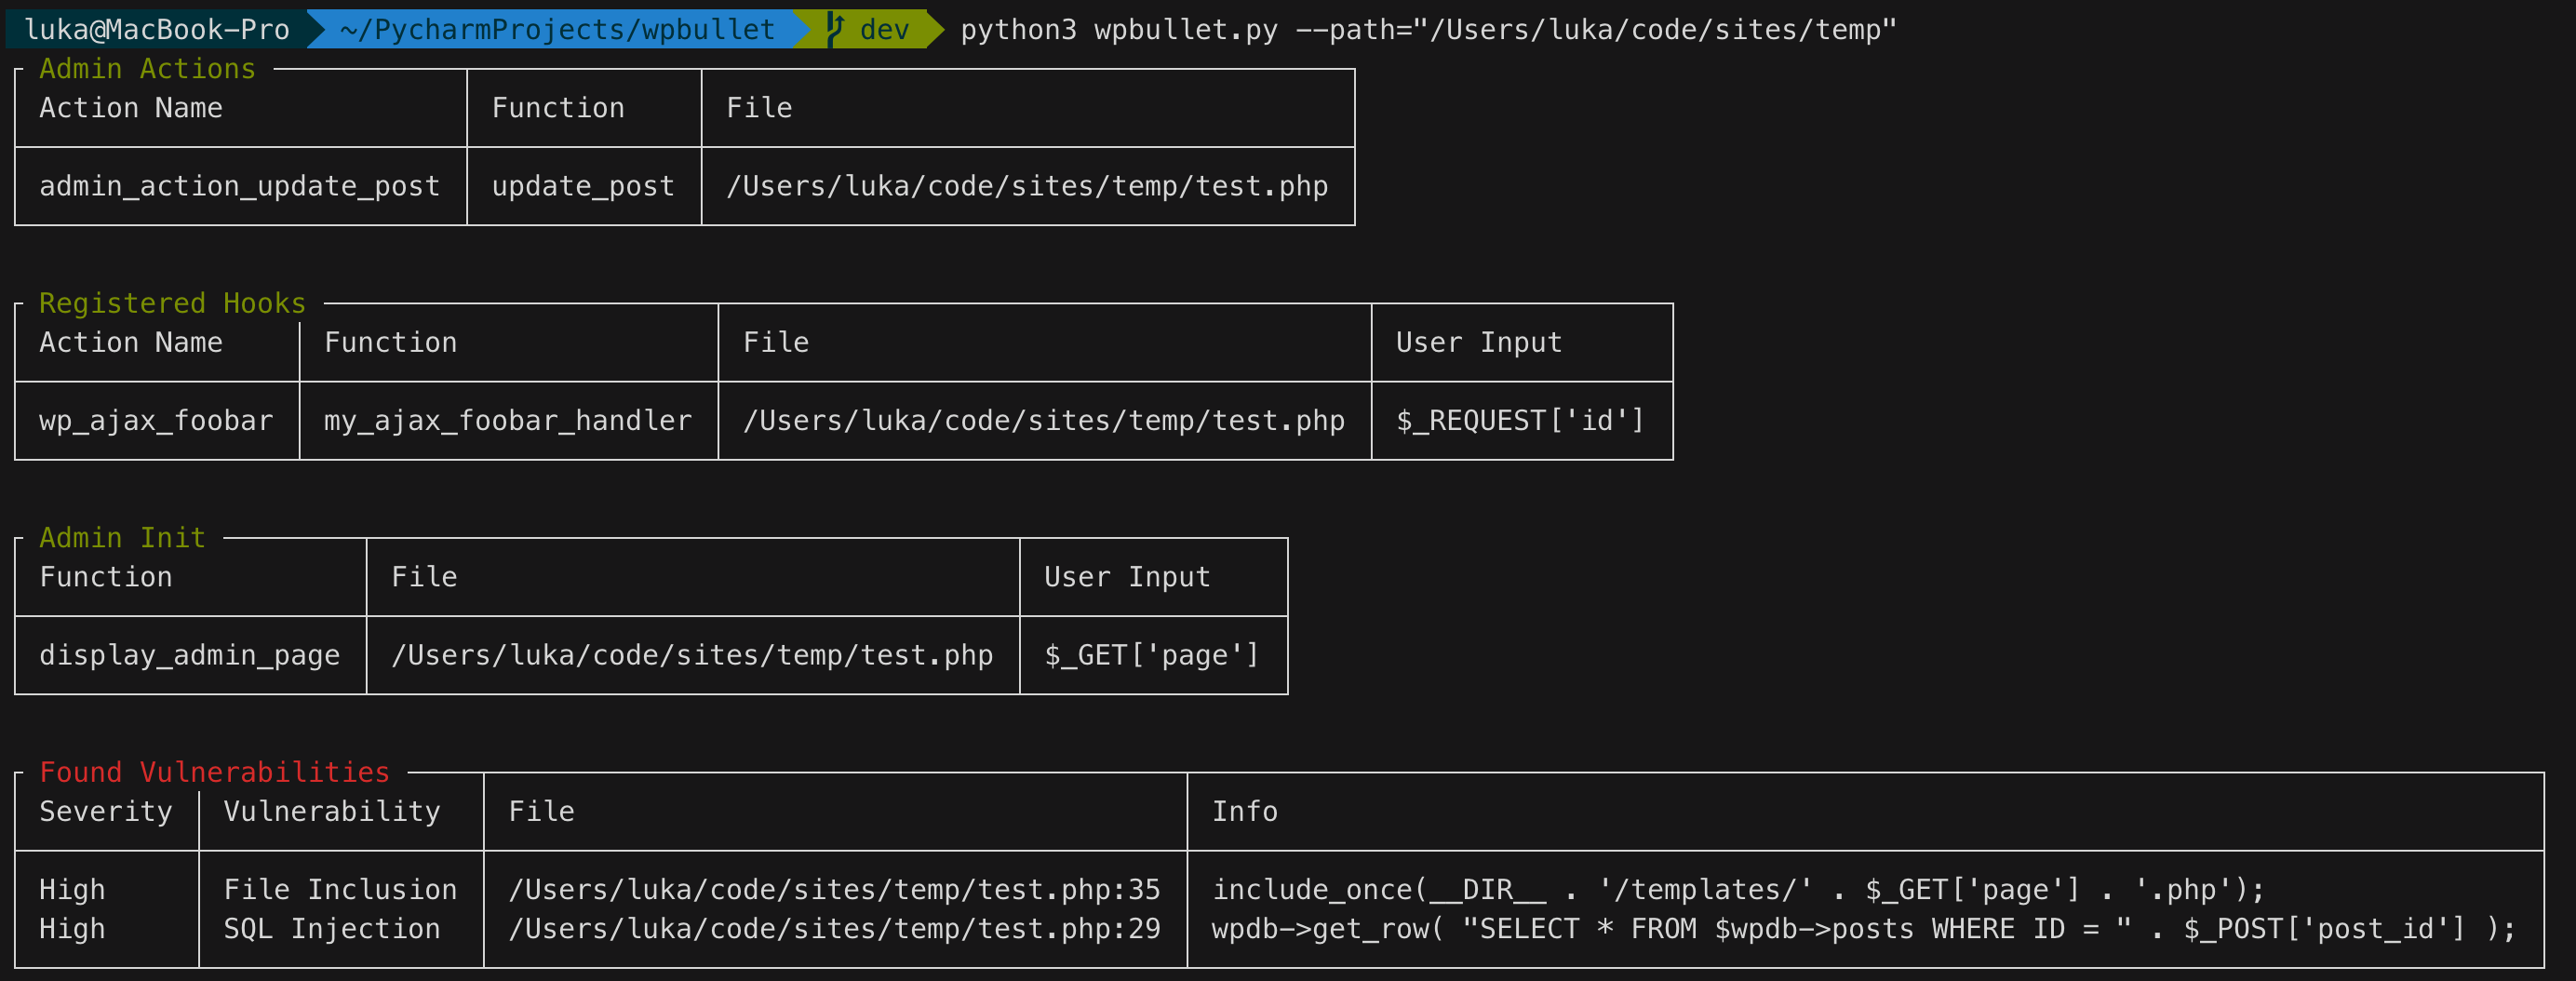 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
 owasp/go-scp
Golang Secure Coding Practices guide
 owasp/cwe-sdk-javascript
A Common Weakness Enumeration (CWE) Node.js SDK compliant with MITRE / CAPEC
 yeswehack/vulnerable-code-snippets
Twitter vulnerable snippets
 nxploited/cve-2025-3776
WordPress Verification SMS with TargetSMS Plugin <= 1.5 is vulnerable to Remote Code Execution (RCE)
 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 owasp/riskassessmentframework
The Secure Coding Framework
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 geeksikhsecurity/ai-tool-poisoning-guard
Free security-baseline rule for Claude Code, Codex, and Cursor: treats MCP tool descriptions as untrusted input (OWASP MCP Top 10 MCP03,…
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.