
GuardModel
 shivang0/guardmodel
GitHub Action that scans ML model files for malicious code and security vulnerabilities
ai-securitycode-analysisdevsecops+5
2
shivang0/guardmodelGitHub Action that scans ML model files for malicious code and security vulnerabilities
 sanupl/cve-2021-46078
CVE-2021-46078 - An Unrestricted File Upload vulnerability exists in Sourcecodester Vehicle Service Management System 1.0. A remote attacker can…
 rickidevs/cve-2026-35570
Detailed write-up and proof-of-concept for CVE-2026-35570, a sandbox bypass in openclaude v0.1.7 allowing path traversal to read and write arbitrary…
 hyperps/cve-2026-0848
nltk.tokenize.StanfordSegmenter dynamically loads external Java .jar files without verification or sandboxing. If an attacker can supply or replace…
 trerb/ai-ide-config-guard
Scan a repo for AI-IDE config files that can trigger RCE via Claude Code hooks, Cursor rules, MCP auto-registration. Detects CVE-2025-59536,…
 helsecert/cve-2022-22965
Detection scripts and guidance for CVE-2022-22965 (Spring4Shell) vulnerability in Spring Framework, including PowerShell and Bash scanners for…
 jvr2022/cve-2026-29786
Proof-of-concept demonstrating a hardlink path traversal in the tar npm package, allowing overwrite of files outside the extraction directory via…
 garethmsheldon/react2shell-cve-2025-55182-detector
Multi-language detection scripts for CVE-2025-55182 (React2Shell) that scan package.json files to identify vulnerable React dependency versions and…
 before-rain/cve-2025-50472
Proof-of-concept exploit for CVE-2025-50472, a deserialization RCE vulnerability in ModelScope ms-swift's ModelFileSystemCache via malicious .mdl…
 maestro-ant/vvveb-cms-cve-2025-8518
This repository contains a Proof of Concept (PoC) demonstrating a critical vulnerability in givanz Vvveb 1.0.5. The vulnerability allows an…
 shoucheng3/joniles__mpxj_cve-2020-35460_8-3-4
Exploit for CVE-2020-35460 targeting MPXJ project management library, enabling arbitrary code execution via crafted project files in Java, .Net, and…
 arsalanraja987/java-cve-2021-29425-tika-xxe
Proof-of-concept exploit for CVE-2021-29425, an XML External Entity (XXE) vulnerability in Apache Tika, demonstrating file disclosure and SSRF via…
 atlassian/bitbucket-iac-scan
Scans Infrastructure as Code files for security misconfigurations and vulnerabilities using KICS, with Bitbucket Code Insights reporting.
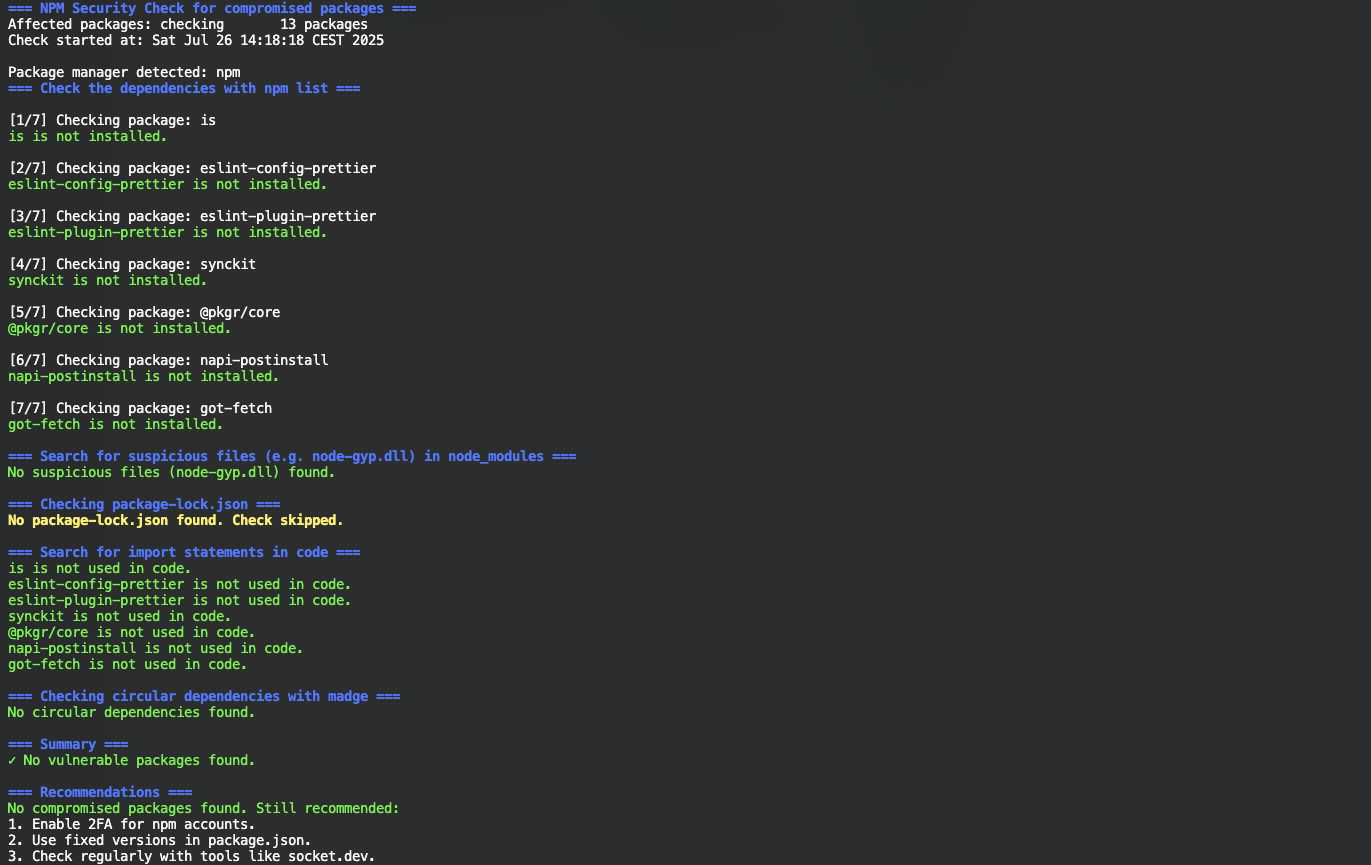 nihilor/cve-2025-54313
Checks projects for compromised packages, suspicious files, and import statements.
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 tommiionfire/cve-2016-3714
Proof-of-concept exploit for CVE-2016-3714, a remote code execution vulnerability in ImageMagick's MVG file processing. Demonstrates shell command…
 password123456/py_certificate_extractor
Extracts and exports certificate information from digitally signed PE files using Python and pefile, enabling forensic analysis of code-signing…
 julio-cfa/cve-2024-34832
Proof-of-concept exploit for CVE-2024-34832: directory traversal in CubeCart admin panel leading to remote code execution via crafted `_g` parameter…