
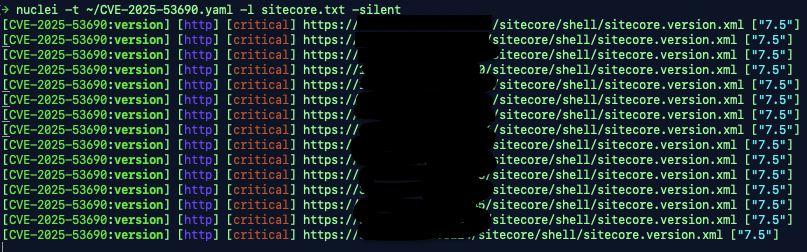
CVE-2025-53690
 rxerium/cve-2025-53690
Detection for CVE-2025-53690
code-analysisexploitationinformation-gathering+3
rxerium/cve-2025-53690Detection for CVE-2025-53690
 oscar-collado/langflow-cve-2026-17633-poc
PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…
 useaitechdad/openclaw-technical-analysis
This technical research and review is for educational purposes on public code and constitutes Fair Dealing under the Copyright Act (Canada).
 kevinbackhouse/djvulibre-poc-cve-2025-53367
Proof-of-concept exploit for CVE-2025-53367, a vulnerability in the DjVuLibre library. Demonstrates exploitation of a memory corruption bug in DjVu…
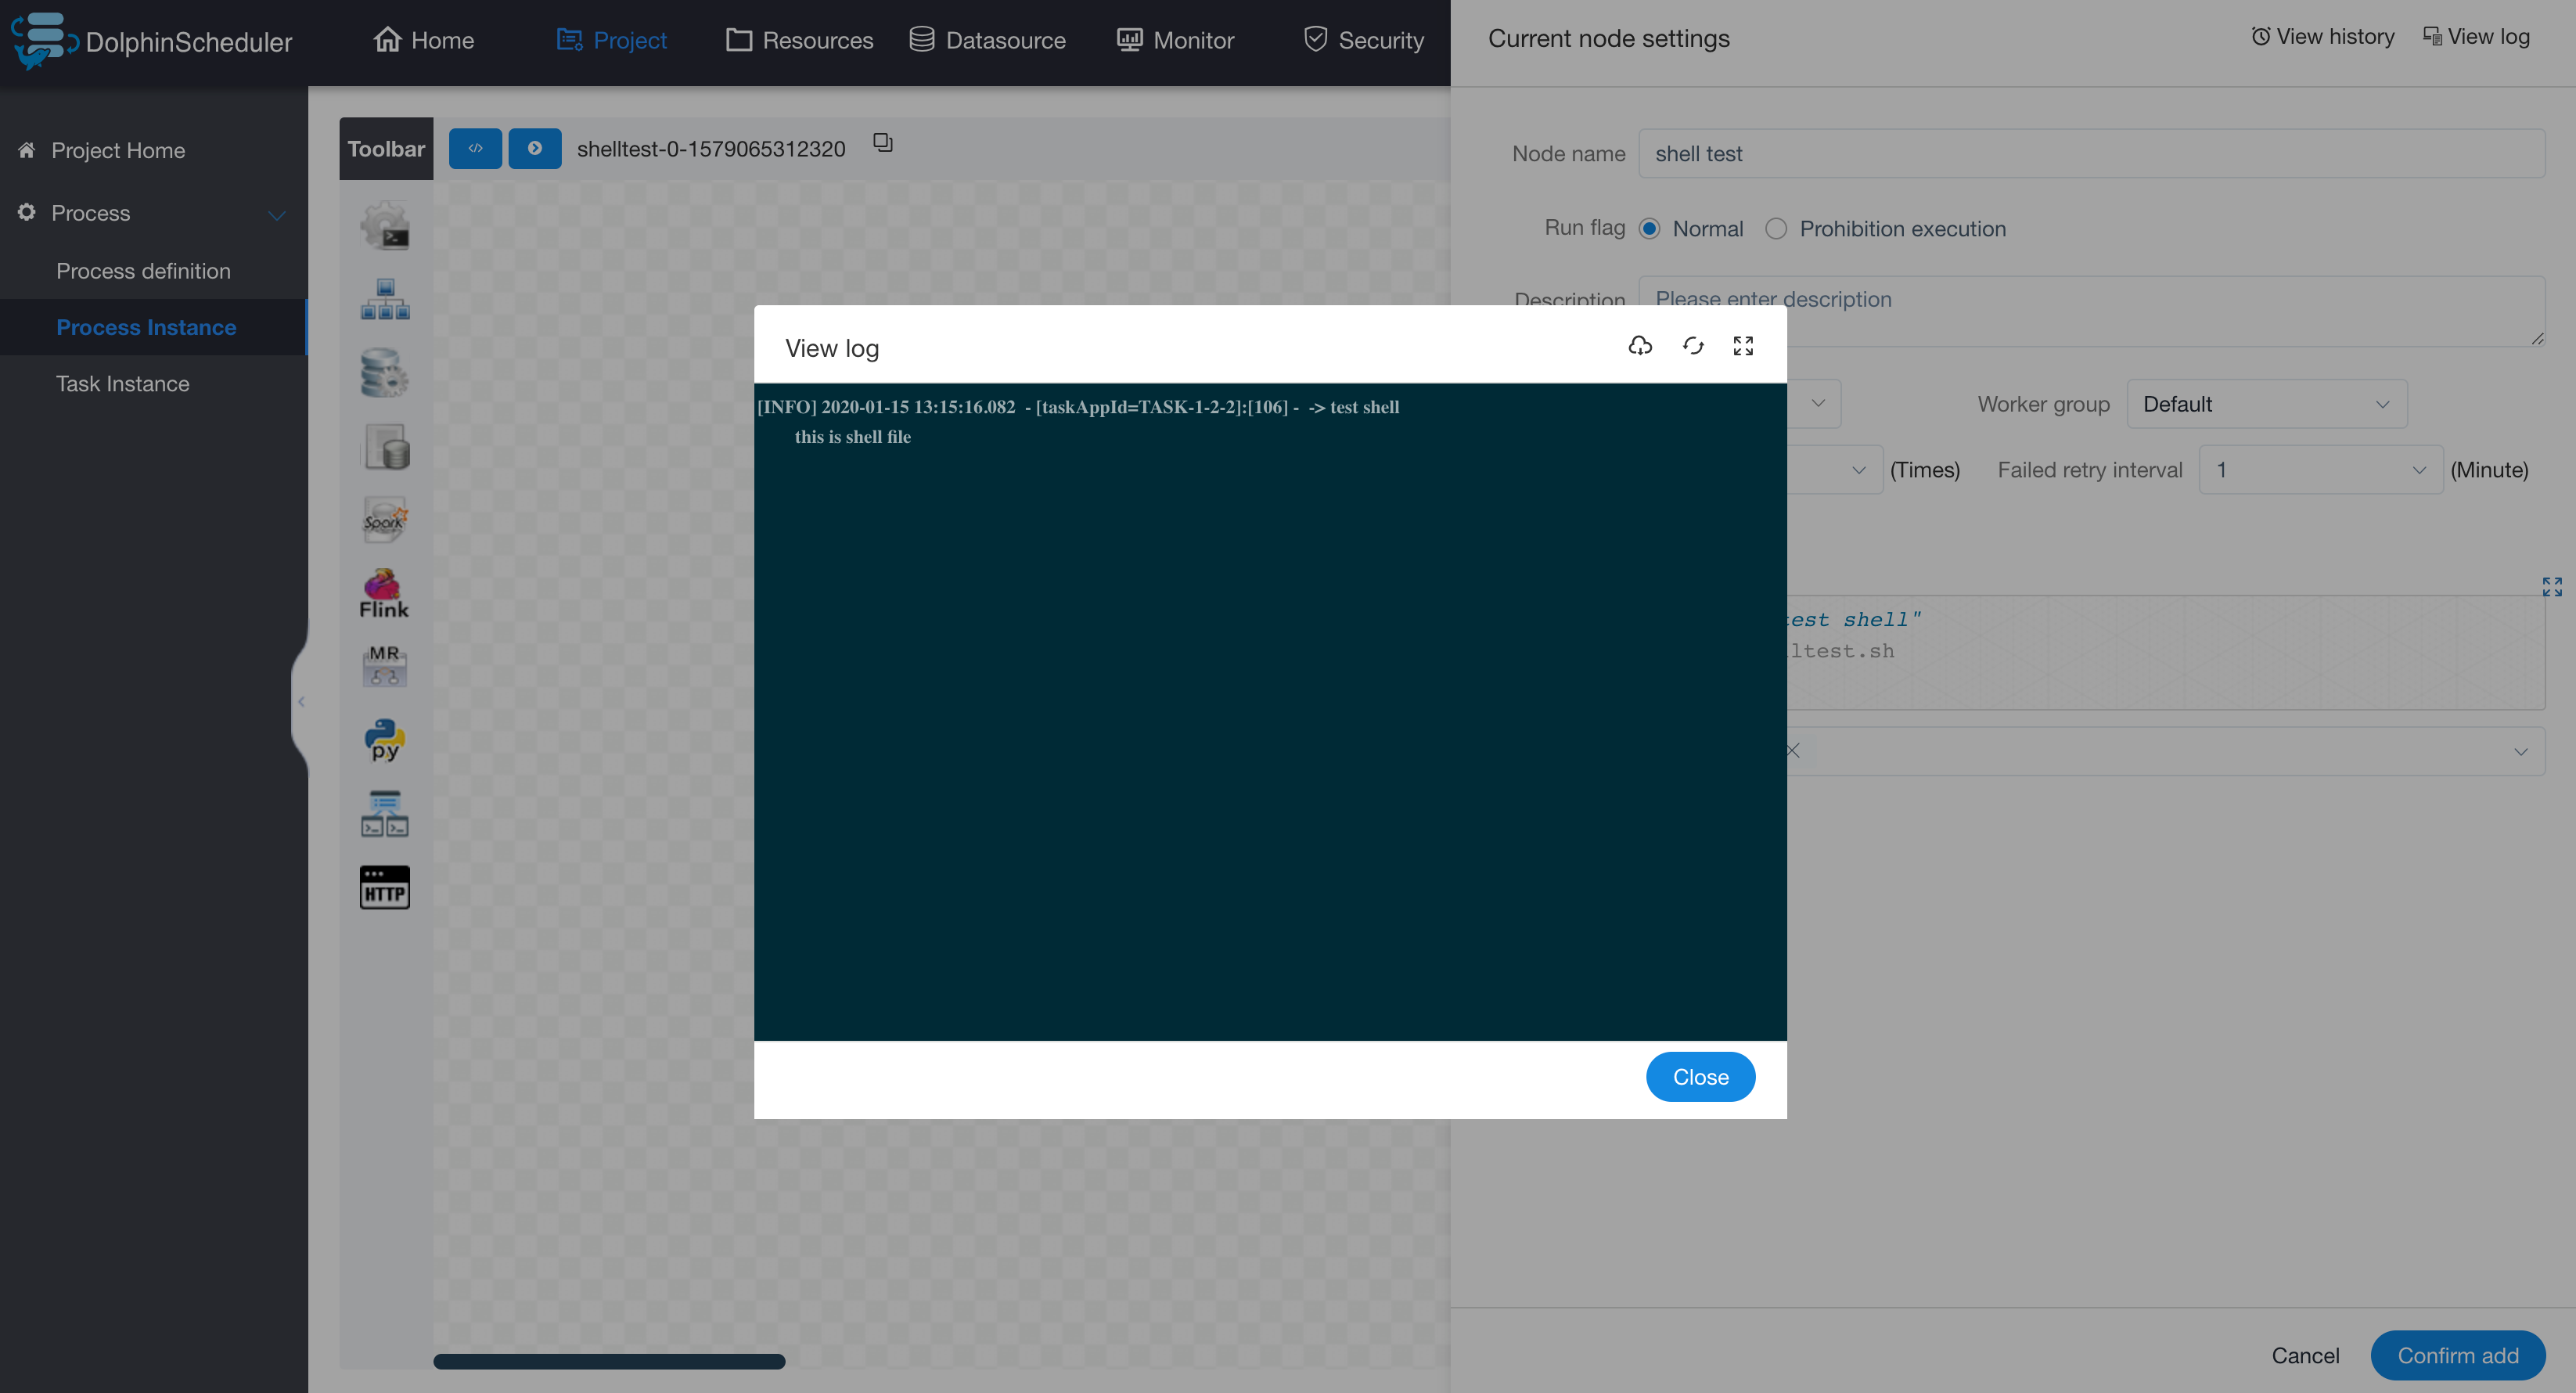 shoucheng3/apache__dolphinscheduler_cve-2022-26884_2-0-5
Proof-of-concept exploit for CVE-2022-26884 targeting Apache DolphinScheduler, enabling remote code execution via crafted requests to the workflow…
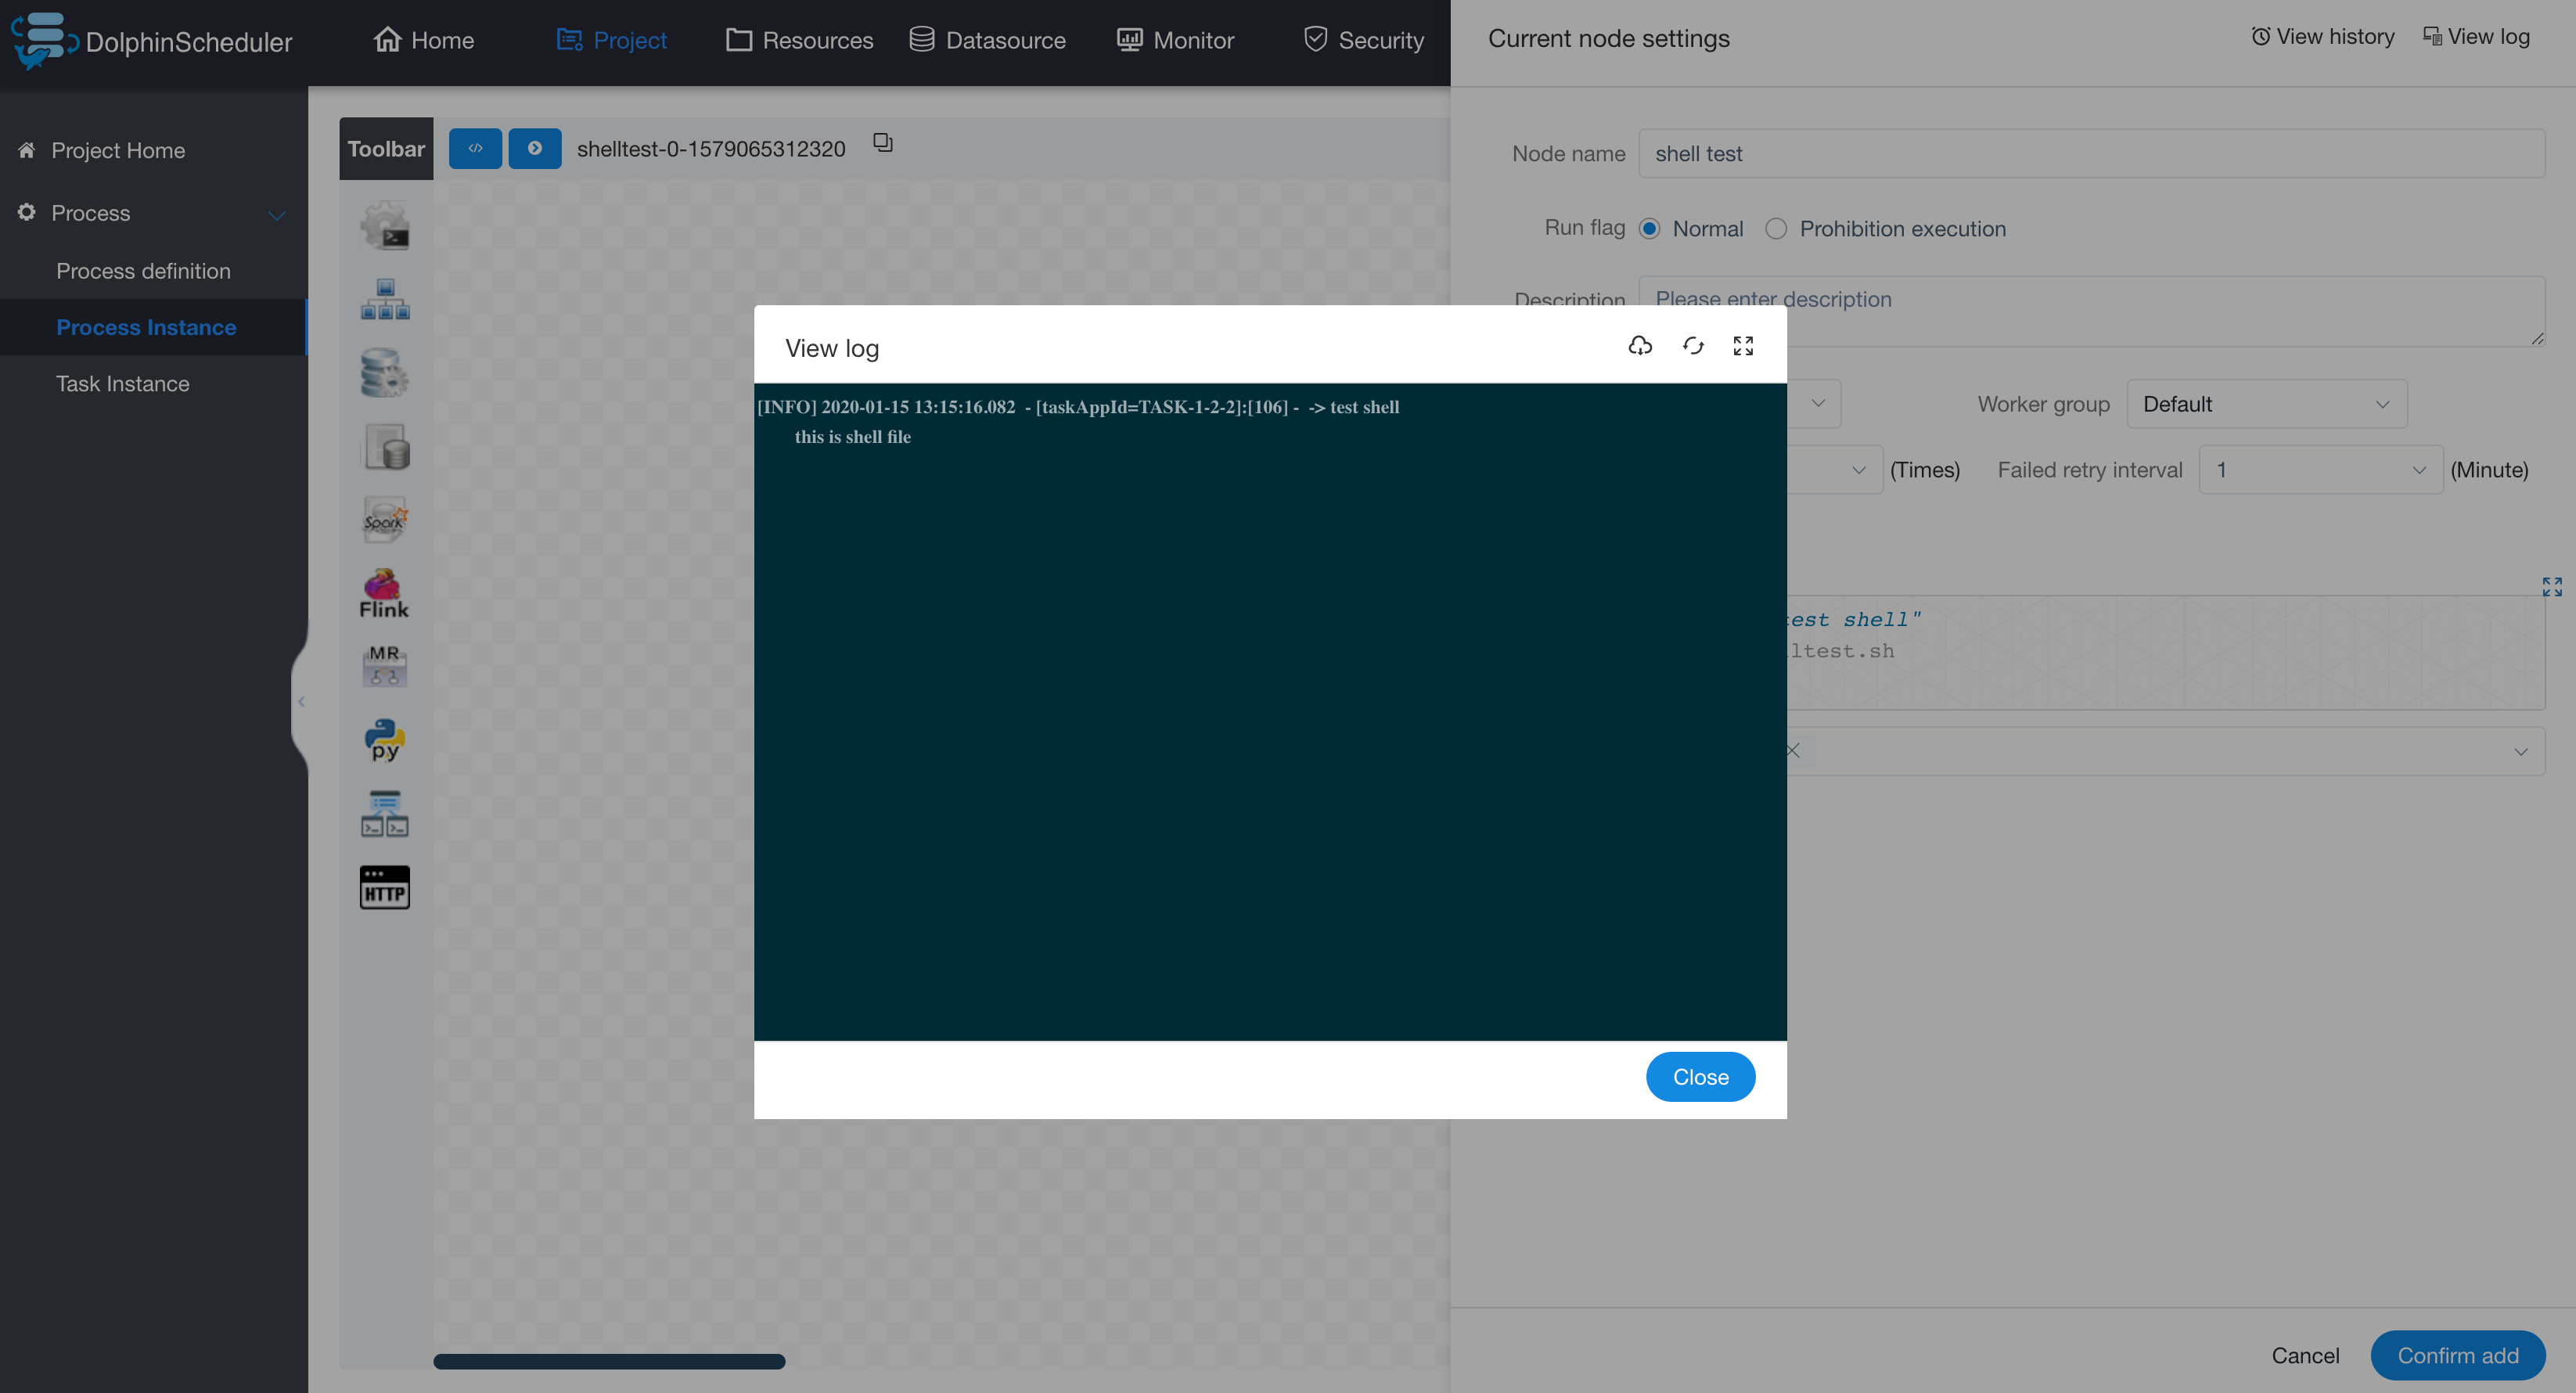 shoucheng3/apache__dolphinscheduler_cve-2022-34662_2-0-9
Proof-of-concept exploit for CVE-2022-34662 targeting Apache DolphinScheduler, enabling remote code execution via crafted SQL injection in the…
 owasp/go-scp
Golang Secure Coding Practices guide
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 msanft/cve-2025-55182
PoC exploit for CVE-2025-55182, demonstrating remote code execution in React Server Functions via prototype pollution and a crafted Flight Protocol…
 hnfull/intensio-obfuscator
Obfuscate a python code 2.x and 3.x
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
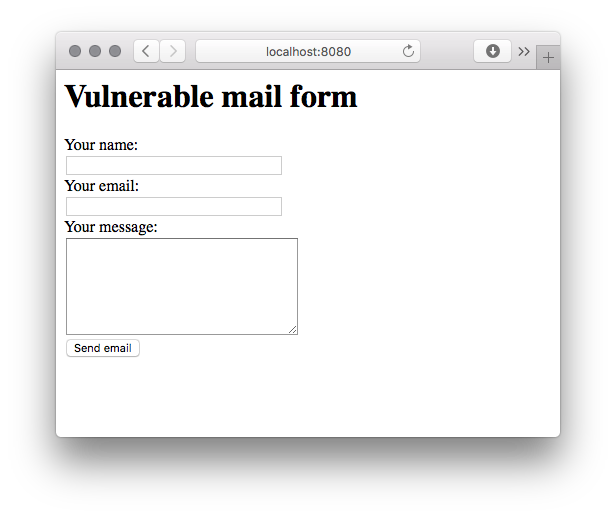 opsxcq/exploit-cve-2016-10033
PHPMailer < 5.2.18 Remote Code Execution exploit and vulnerable container
 adamyordan/cve-2019-1003000-jenkins-rce-poc
Jenkins RCE Proof-of-Concept: SECURITY-1266 / CVE-2019-1003000 (Script Security), CVE-2019-1003001 (Pipeline: Groovy), CVE-2019-1003002 (Pipeline:…
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 owasp/asst
OWASP ASST (Automated Software Security Toolkit) | A Novel Open Source Web Security Scanner.
 owasp/ocsd
OWASP Certified Secure-Software Developer
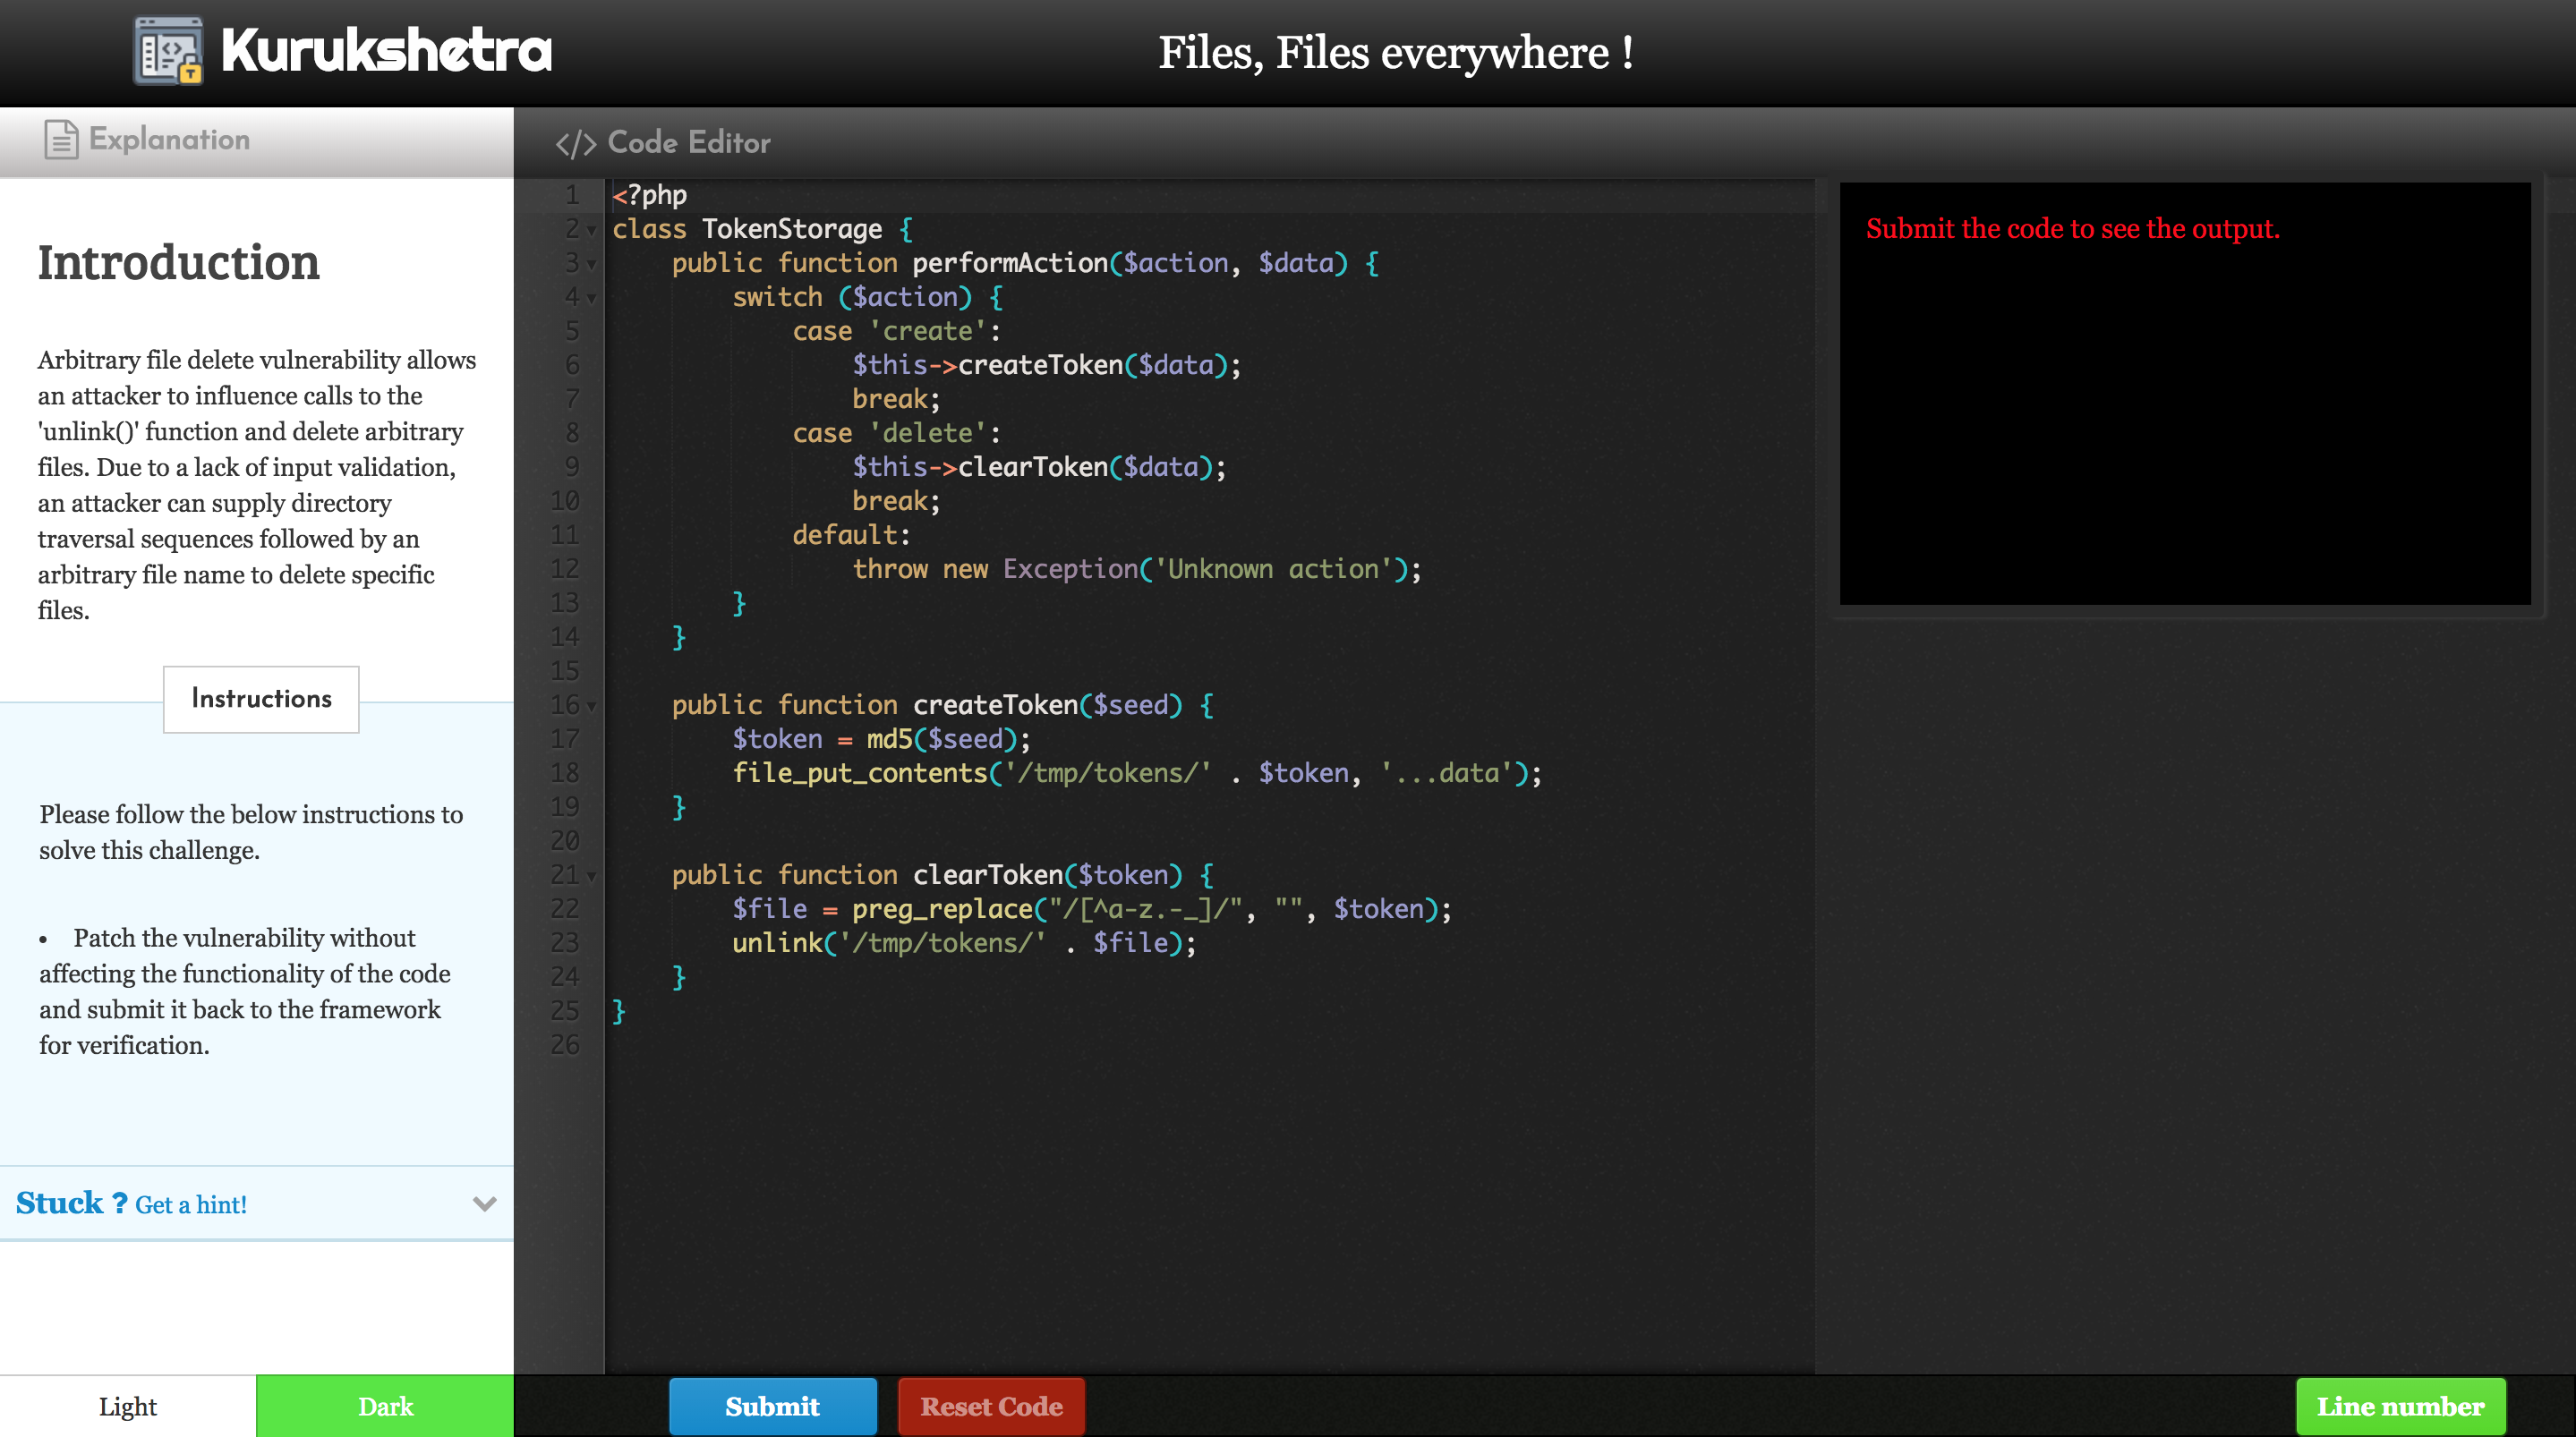 a0xnirudh/kurukshetra
Kurukshetra - A framework for teaching secure coding by means of interactive problem solving.