

sast-scan
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
cloud-securitycode-analysisconfiguration-auditing+6
880
shiftleftsecurity/sast-scanScan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 elastic/supply-chain-monitor
Automated supply chain security monitor that polls PyPI and npm registries, diffs new releases against predecessors, and uses LLM analysis to detect…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 manuelschipper/nah
a guard that blocks catastrophic agent actions
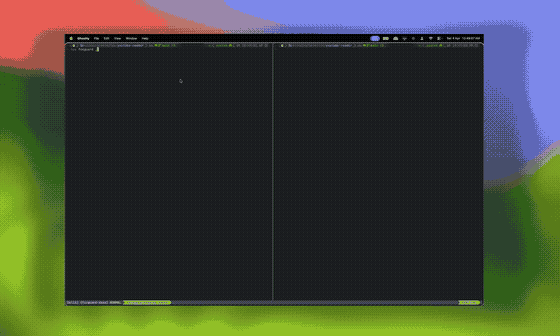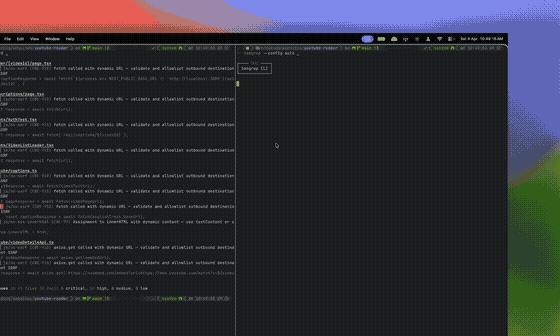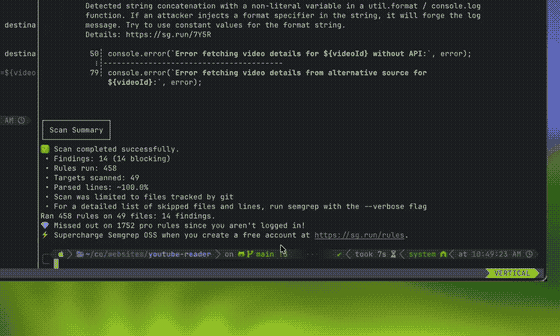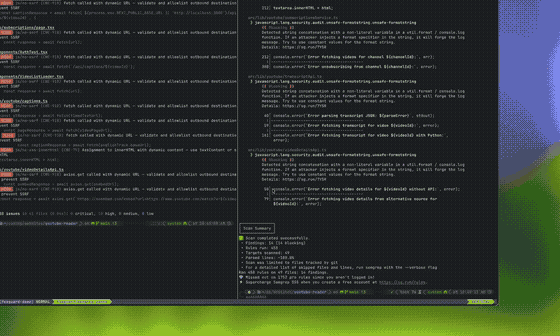 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
 rubo77/log4j_checker_beta
a fast check, if your server could be vulnerable to CVE-2021-44228
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
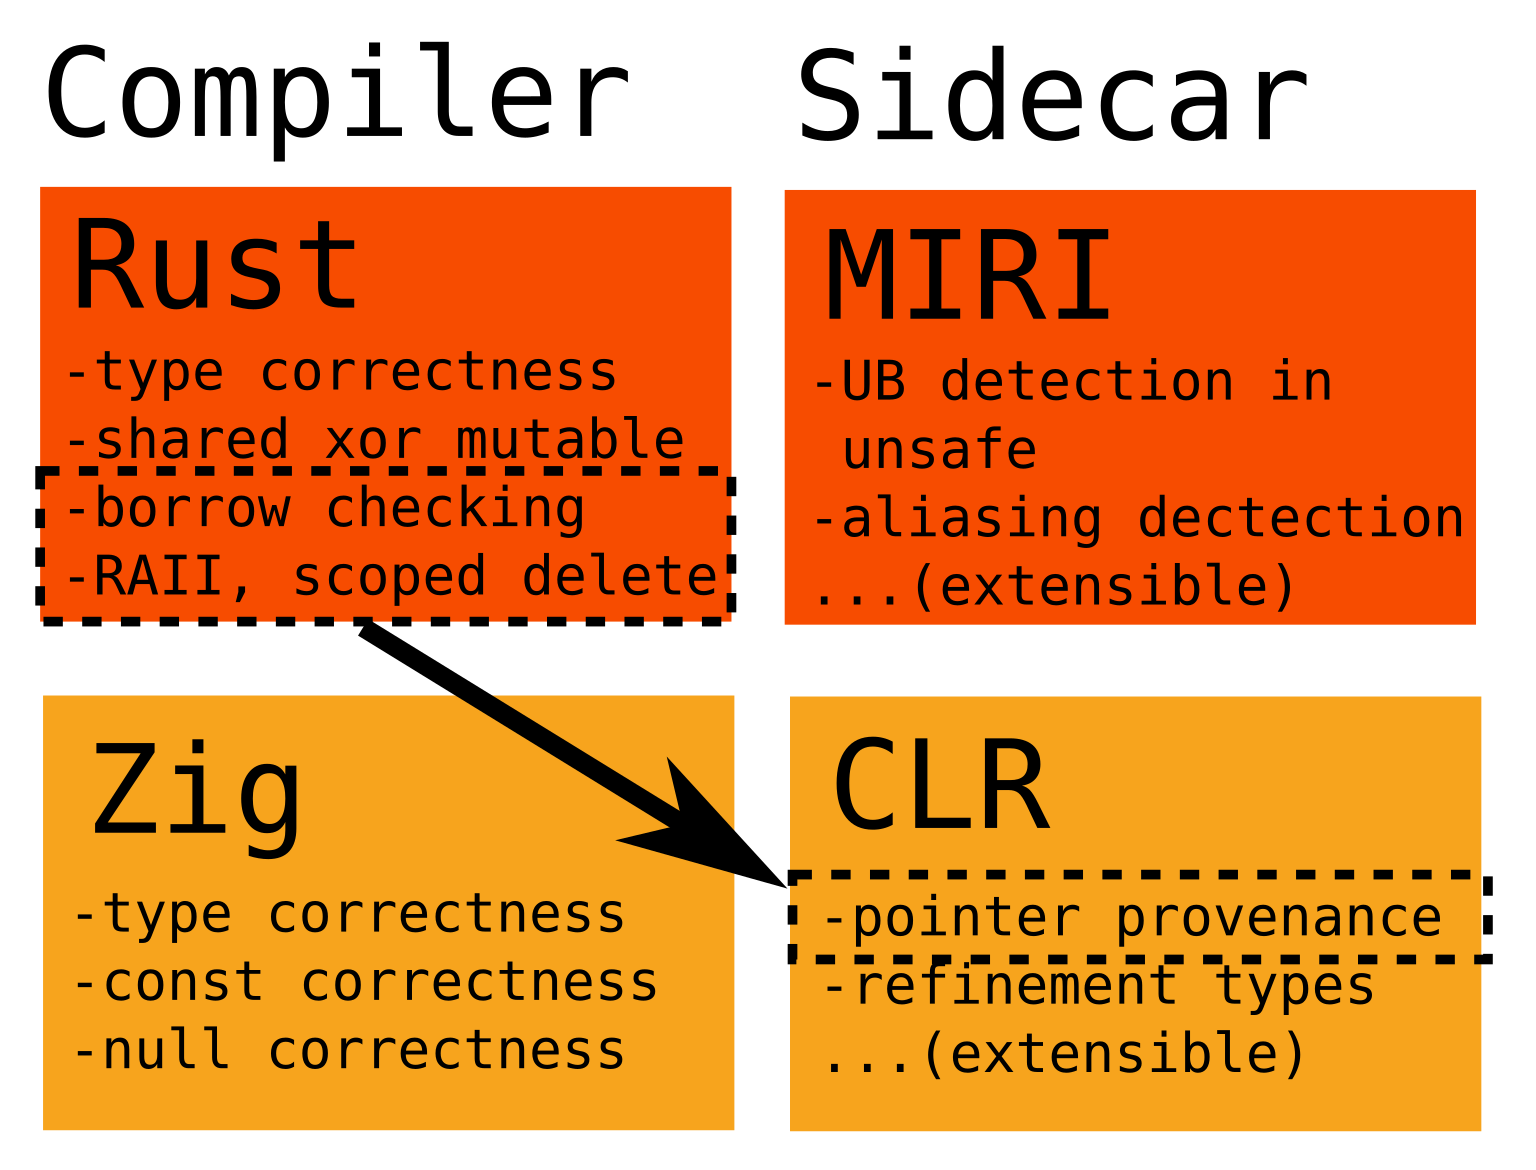 ityonemo/clr
Checker for Lifetimes and other Refinement types
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
 a0xnirudh/kurukshetra
Kurukshetra - A framework for teaching secure coding by means of interactive problem solving.
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 polaris64/web_exploit_detector
The Web Exploit Detector is a Node.js application used to detect possible infections, malicious code and suspicious files in web hosting environments
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…
 trailofbits/ruzzy
A coverage-guided fuzzer for pure Ruby code and Ruby C extensions
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)