
CVE-2026-39902
 kx00007/cve-2026-39902
Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
code-analysisexploitationpenetration-testing+2
kx00007/cve-2026-39902Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
 vinsontang1/dcvd
The code in "DCVD: Dual-Channel Cross-Modal Fusion for Joint Vulnerability Detection and Localization"
 kx00007/cve-2026-39938
Detailed CVE-2026-39938 vulnerability report for Cacti ≤1.2.30, demonstrating unauthenticated LFI chained to OS command injection RCE with PoC, root…
 simota/nginx-rift-scanner
Detect-only scanner for CVE-2026-42945 (NGINX Rift), a heap overflow in ngx_http_rewrite_module. Version detection + nginx.conf pattern analysis.…
 pavilionq/cve-2023-33246-mitigation
Maven-based demonstration of CVE-2023-33246 mitigation for Apache RocketMQ, featuring attack testing and enhanced parameter validation to prevent…
 kiyochii/cve-2026-29628
Proof-of-concept for CVE-2026-29628, a stack-based buffer overflow in tinyobjloader's experimental parser, with ASan/UBSan reproduction and fix…
 javascript-obfuscator/javascript-obfuscator
Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…
 nyamort/cve-2024-52301
Proof-of-concept exploit for CVE-2024-52301 demonstrating environment manipulation in Laravel via injected URL parameters, with detailed code…

 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
 colton1skees/dna
LLVM based static binary analysis framework
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
 dedellix/mut-bc-ss-01
Mutation testing on X.509 Certificate Validation IN OpenSSL v.1.1.1h, based on CVE-2021-3450.
 joelbts/cve-2020-0601_poc
Demonstration of CVE-2020-0601 aka curveball. Based on the PoC's available at https://github.com/kudelskisecurity/chainoffools and…
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
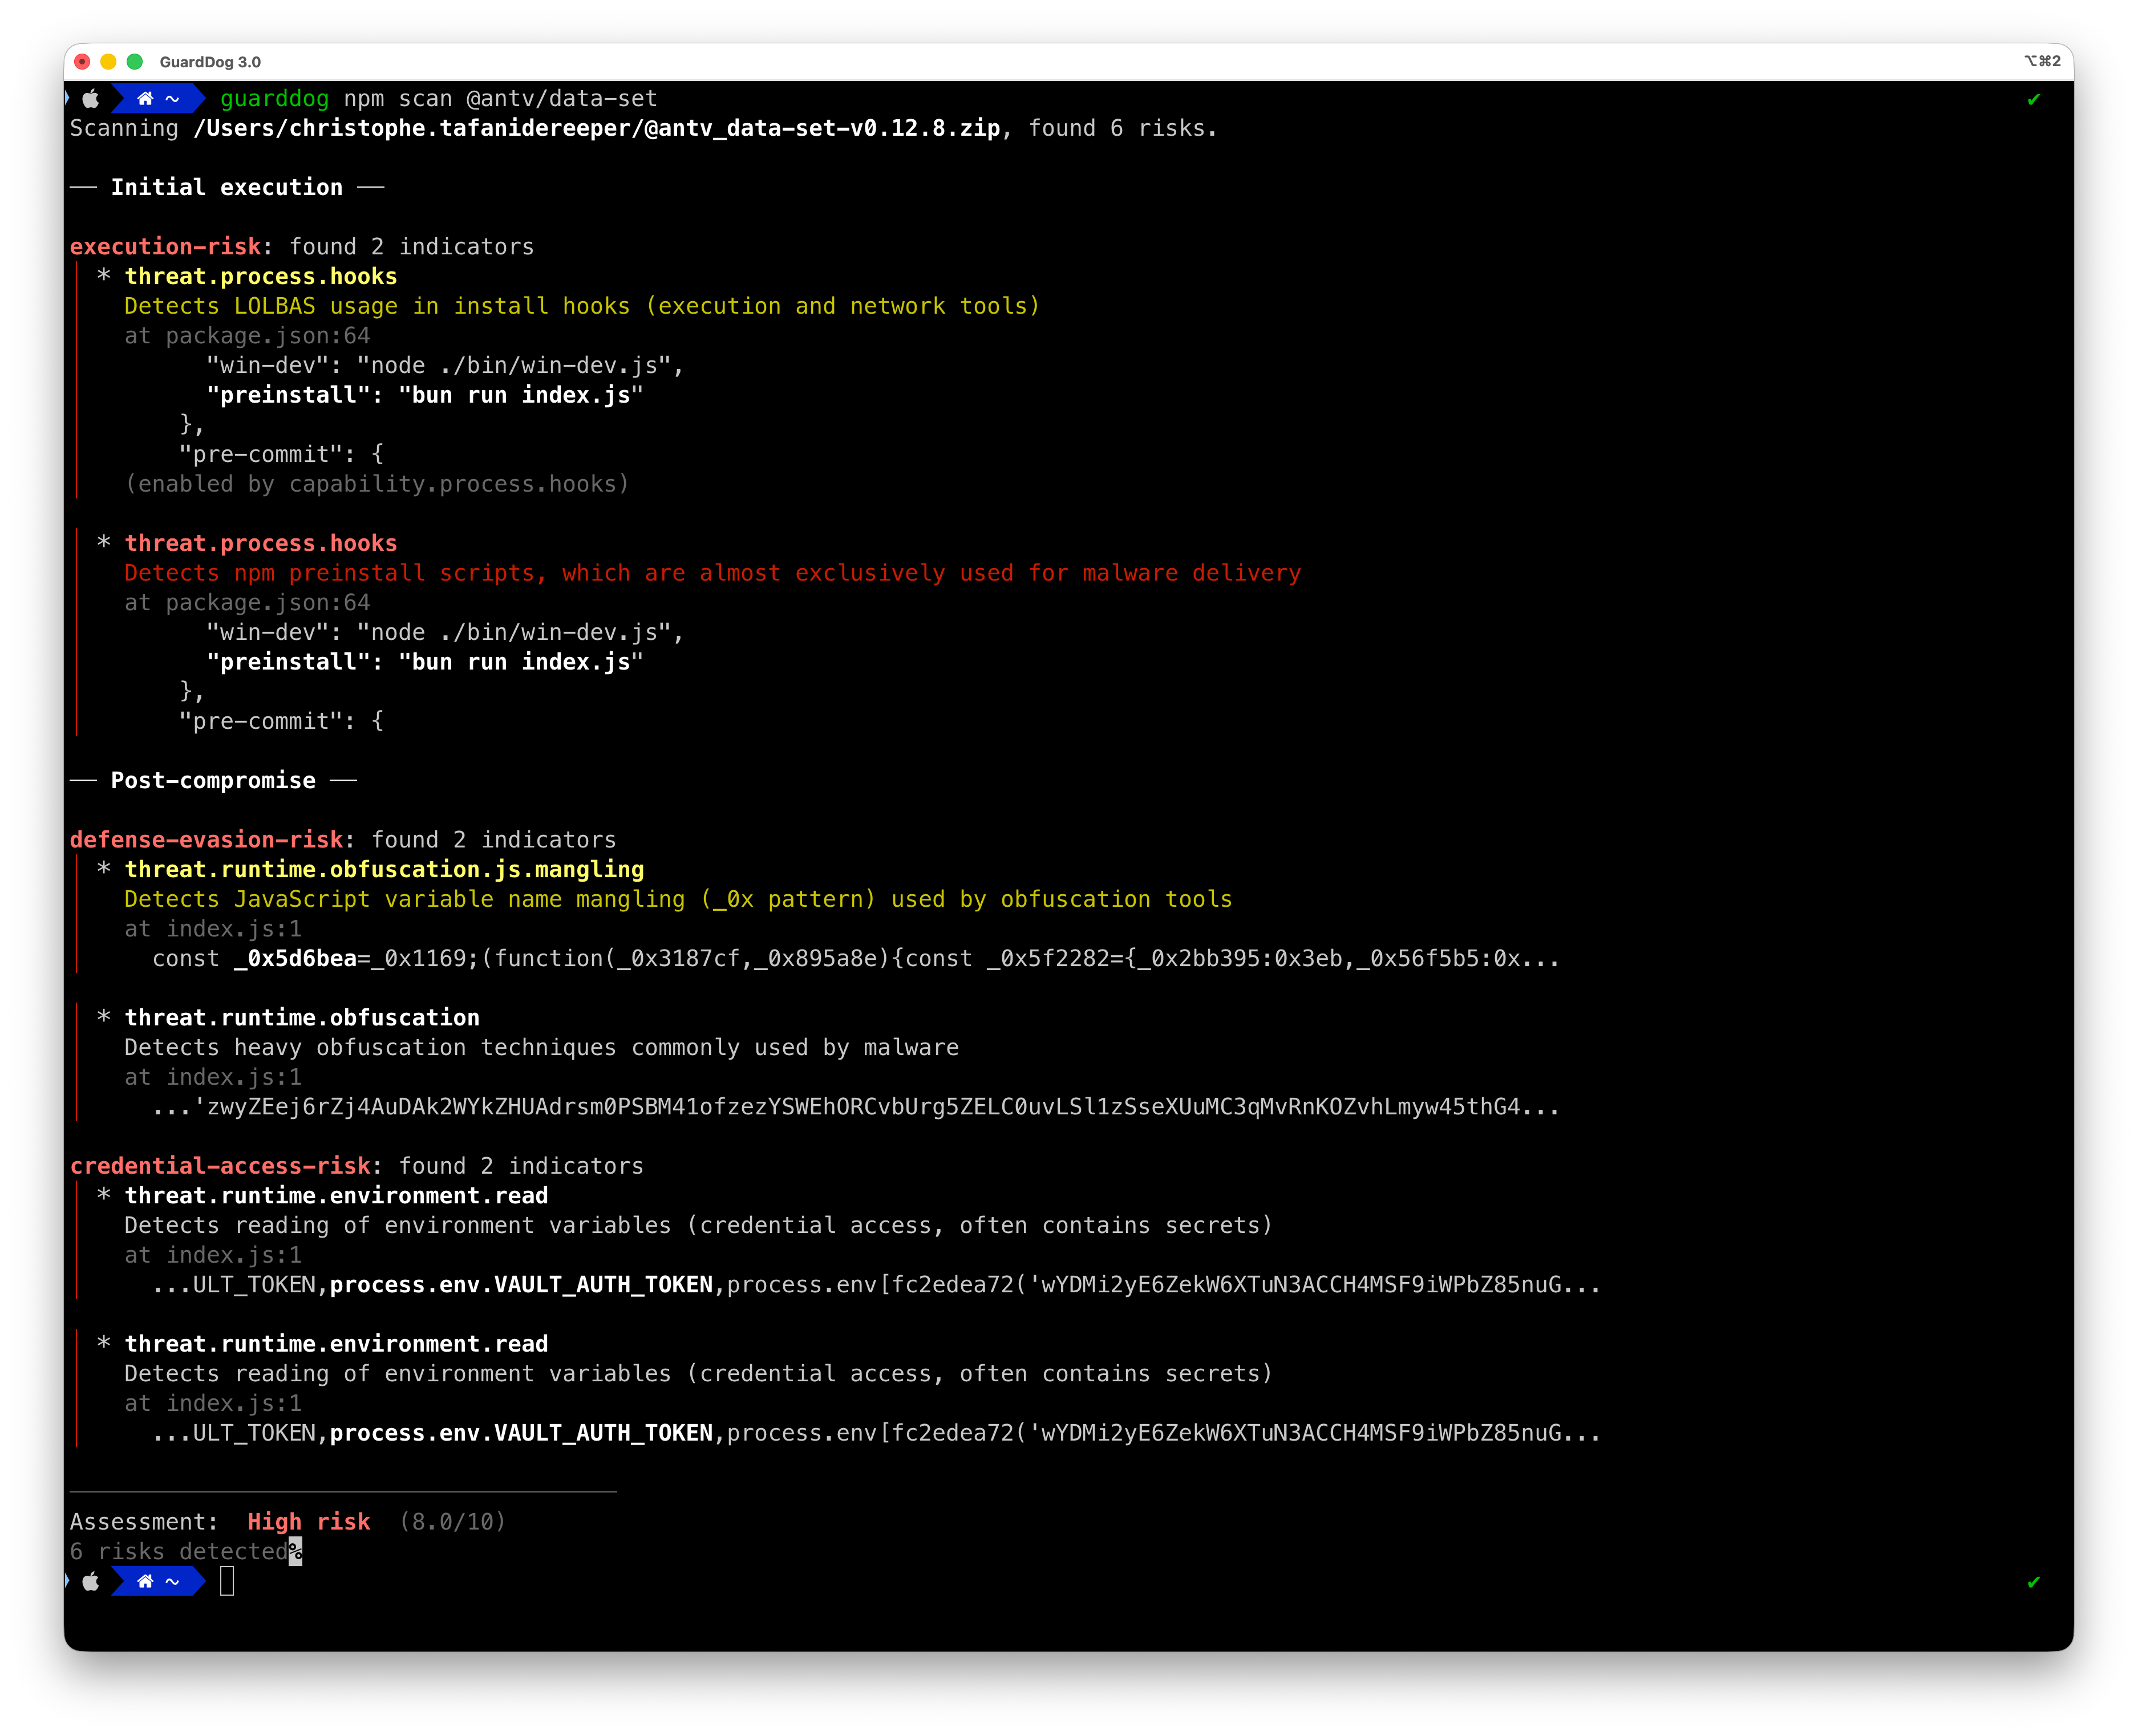 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 doyensec/electronegativity
Electronegativity is a tool to identify misconfigurations and security anti-patterns in Electron applications.