
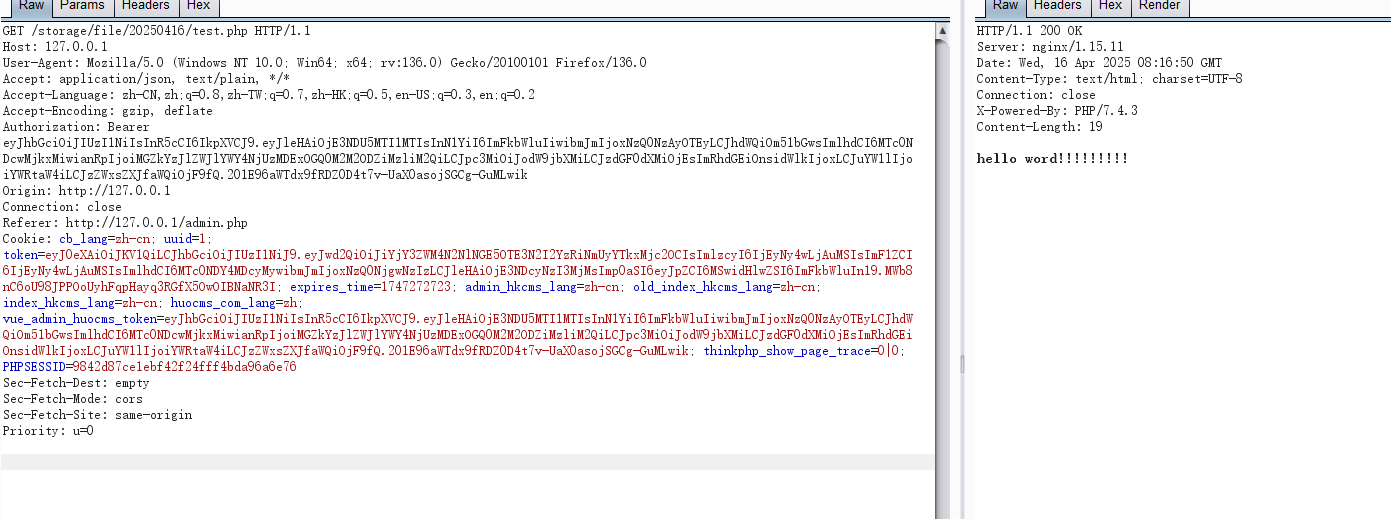

 li8u99/spring-data-mongodb-demo
Demo environment for CVE-2022-22980 (Spring Data MongoDB SpEL injection RCE) with vulnerable application code for security testing and education.
 edgarloyola/cve-2021-40905
Proof-of-concept exploit for CVE-2021-40905, a remote code execution vulnerability in CheckMK Management Web Console via crafted .mkp extension…
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 sektioneins/pcc
Automated PHP configuration auditor that scans php.ini for security misconfigurations, supports CLI and web modes, and outputs results in text, HTML,…
 slowql/slowql
Next-generation SQL static analyzer written in Rust. 282+ rules. Zero false positives. Security, performance, reliability, cost, compliance, quality.…
 tlwebdesign/joomla-3.10.12-languagehelper-hotfix
Plugin to fix security vulnerability CVE-2023-40626 in Joomla 3.10.12
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
 intrinsec/comission
White-box CMS security scanner that audits core, plugin, and theme versions, detects unauthorized modifications, and cross-references known…
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 ny1024/clawguard
Modular security toolkit for autonomous agents providing static analysis, configuration auditing, runtime monitoring, and supply chain verification…
 califio/ngxray
ngxray — nginx config security scanner
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 sh00bx/cve-2025-4615
cve-2025-4615 poc & deep dive
 simota/nginx-rift-scanner
Detect-only scanner for CVE-2026-42945 (NGINX Rift), a heap overflow in ngx_http_rewrite_module. Version detection + nginx.conf pattern analysis.…
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
 0xcyberstan/cve-2026-42533-config-scanner
Static config scanner that flags nginx configs vulnerable to the complex_value two-pass capture-clobbering bug (regex map + regex capture → heap…