
CVE-2026-78071
 toanln-cov/cve-2026-78071
Stored XSS via Location Title in DPCalendar Free
code-analysisexploitationvulnerability-analysis+2
toanln-cov/cve-2026-78071Stored XSS via Location Title in DPCalendar Free
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 guoyanan1g/laravel-vul
Laravel 5 POP chain exploit for CVE-2021-43503, demonstrating a personally discovered deserialization vulnerability with proof-of-concept code.
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 chiefyoru/cve-2026-48939_poc
iCagenda extension for Joomla allows the upload of arbitrary files in the file attachment feature, ultimately resulting in PHP code upload and…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 sentinelxofficial/sxwp2shell
WordPress wp2shell pre-auth RCE exploit kit (CVE-2026-63030 + CVE-2026-60137)
 trinadh465/frameworks_minikin_aosp10_r33-cve-2022-20473
Repository dedicated to CVE-2022-20473, a vulnerability in Android's Minikin library, providing patched source code for AOSP 10.
 ronf98/cve-2024-11972-poc
CVE-2024-11972 in Hunk Companion <1.9.0 allows unauthenticated attackers to exploit insecure REST API endpoints and install vulnerable plugins,…
 isacaya/cve-2019-11358
Proof-of-concept exploit for CVE-2019-11358, a prototype pollution vulnerability in jQuery's extend method (versions <3.4.0). Demonstrates the attack…
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
 tuo4n8/cve-2022-24760
Detailed technical analysis of CVE-2022-24760, a prototype pollution vulnerability in parse-server leading to remote code execution via BSON…
 sahiloj/cve-2025-5352
Demonstrates a stored XSS vulnerability in lunary-ai/lunary's Analytics component, where unsanitized NEXT_PUBLIC_CUSTOM_SCRIPT injection leads to…
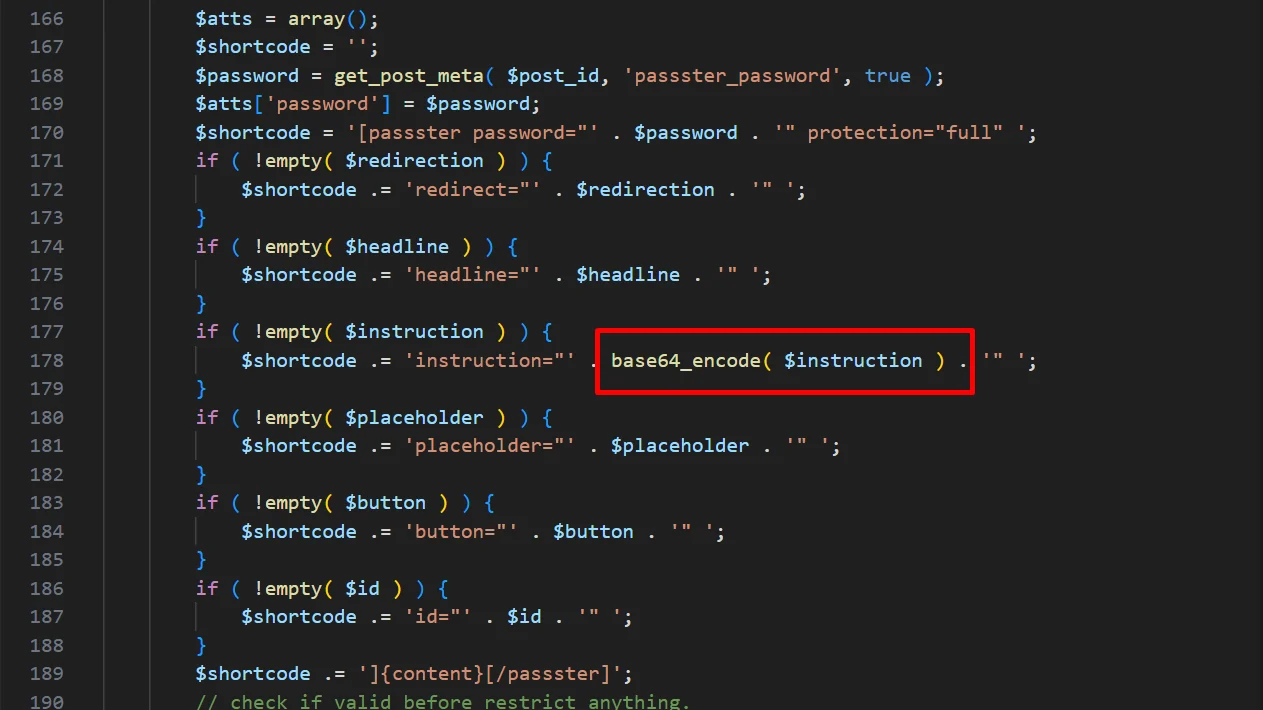 quetuan03/cve-2025-57926
WordPress Passster Plugin <= 4.2.18 is vulnerable to Cross Site Scripting (XSS)
 zimshk/cve-2025-59528.yaml
YAML-based proof-of-concept for CVE-2025-59528, demonstrating remote code execution in Flowise via the CustomMCP node's unsafe JavaScript evaluation.