


 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 florianmattana/sass-king
Reverse engineering NVIDIA SASS instruction dictionary, kernel audits and pattern recognition across GPU architectures.
 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 jonwiggins/xmloxide
A pure Rust reimplementation of libxml2
 owasp/cwe-tool
A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
 sqlsure/sqlsure
Semantic inspector for SQL — catches fan-out double-counting, additivity violations, wrong join keys, and policy breaches before the query runs.…
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 synacktiv/weggli_rules_sstic2023
Curated weggli queries for static analysis of C/C++ code to identify dangerous functions, stack issues, and malloc overflow vulnerabilities.
 parasimpaticki/awesome-appsec-interview
A curated list of resources, practice questions, and study materials to help you prepare for Application Security (AppSec) interviews
 mudongliang/source-packages
This repo stores source code of the vulnerable program.
 nccgroup/rustproofing-linux
Educational examples porting Linux kernel vulnerabilities to Rust, featuring intentionally vulnerable code and exploits for learning kernel security…
 t3ft3lb/2026-100daysofyara
Writing and sharing one YARA rule daily for 100 days
 gmh5225/awesome-mba
List of mixed boolean-arithmetic resources
 al1ex/blockchainconstruction
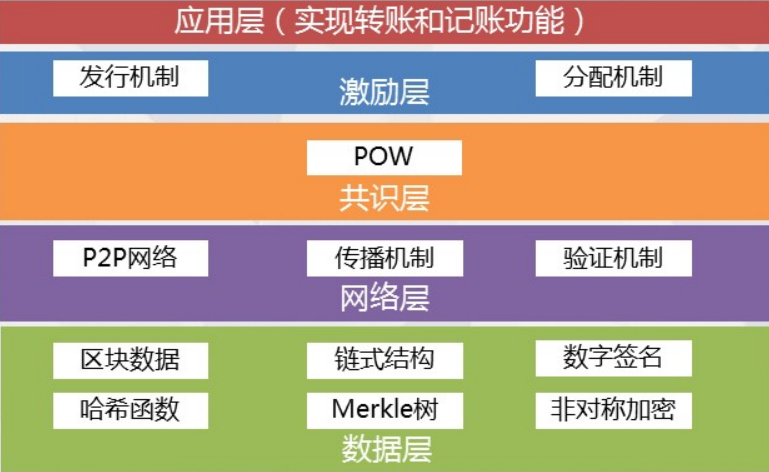
BlockChain Security Construction