

cve-2018-6574
 acole76/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, a Go package vulnerability allowing arbitrary code execution via crafted import paths.
code-analysisexploitationpenetration-testing+2
acole76/cve-2018-6574Proof-of-concept exploit for CVE-2018-6574, a Go package vulnerability allowing arbitrary code execution via crafted import paths.
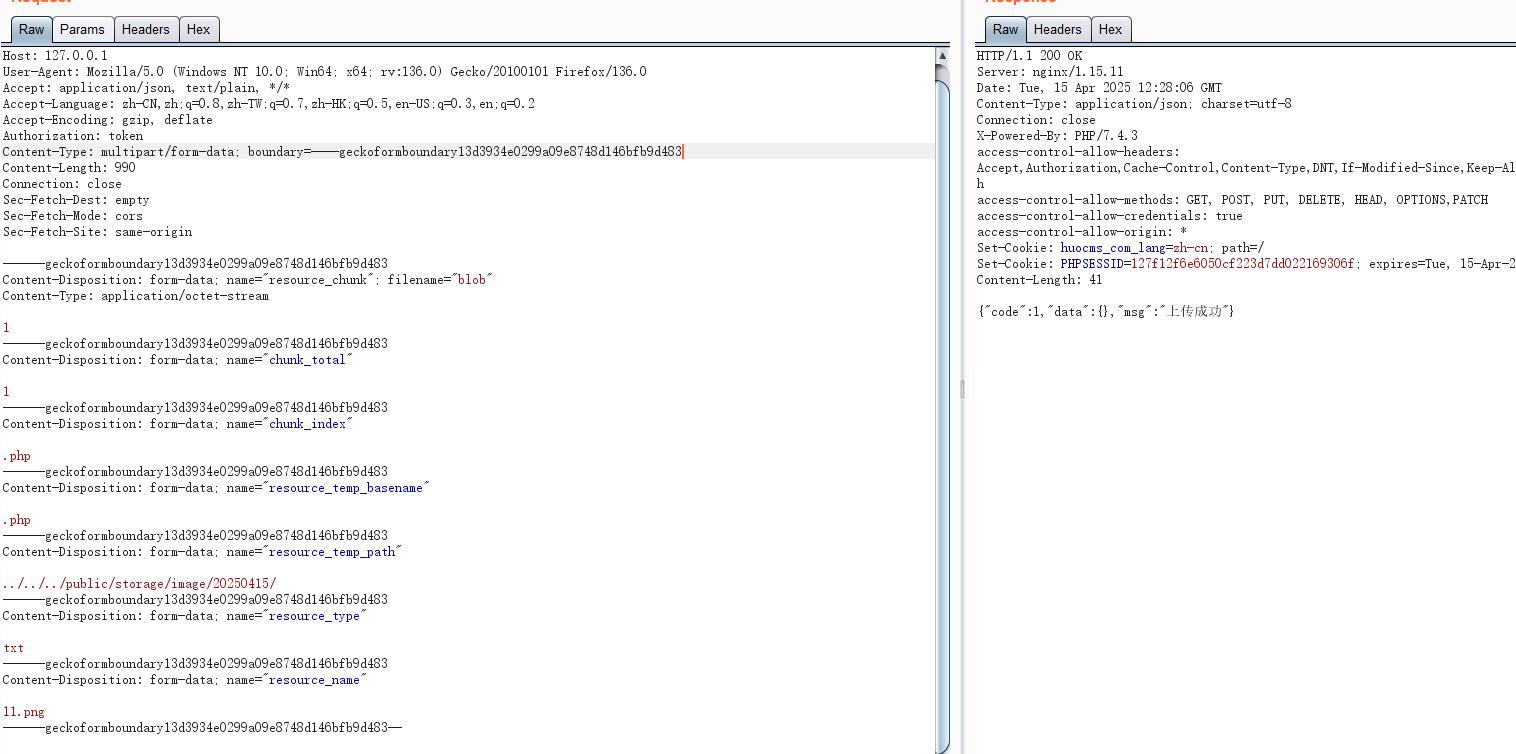 yggcwhat/cve-2025-46078
Vulnerability Description
 faqihudin13/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command. Demonstrates exploitation via malicious…
 dottak/cve-2025-22510
PoC of CVE-2025-22510
 hack-with-rohit/cve-2024-0195-spiderflow
Proof-of-concept exploit for CVE-2024-0195, a critical code injection vulnerability in SpiderFlow 0.4.3 enabling remote code execution via the…

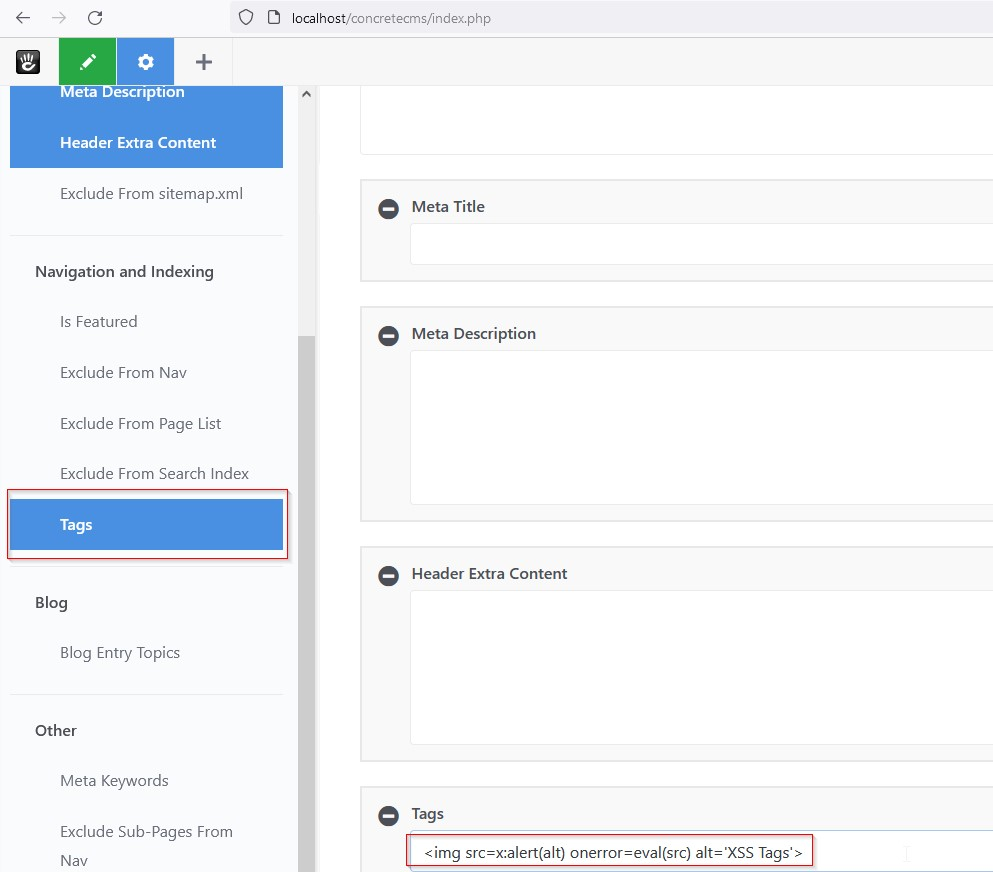 sromanhu/cve-2023-44762_concretecms-reflected-xss---tags
Cross Site Scripting vulnerability in ConcreteCMS v.9.2.1 allows a local attacker to execute arbitrary code via a crafted script to the Tags from…
 sromanhu/cve-2023-43360-cmsmadesimple-stored-xss---file-picker-extension
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the Top…
 paragbagul111/cve-2024-31835
Cross Site Scripting vulnerability in flatpress CMS Flatpress v1.3 allows a remote attacker to execute arbitrary code via a craftedpayload to the…
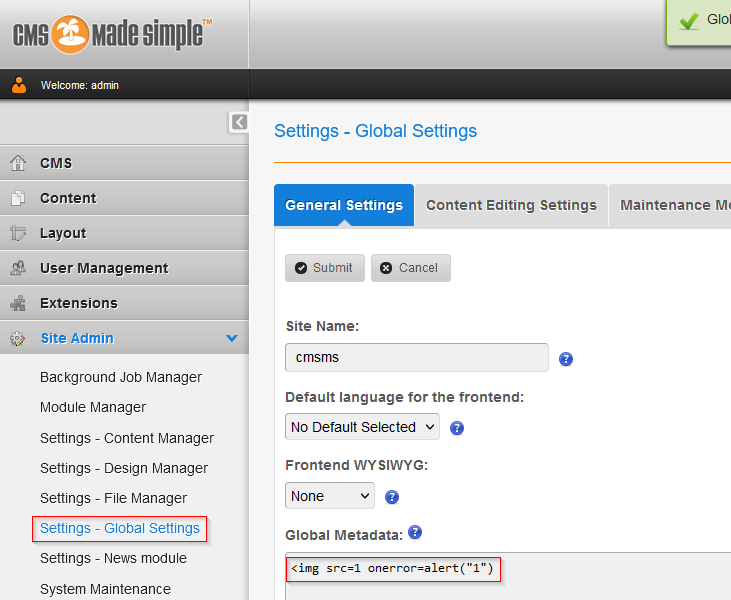 sromanhu/cve-2023-43356-cmsmadesimple-stored-xss---global-settings
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the Global…
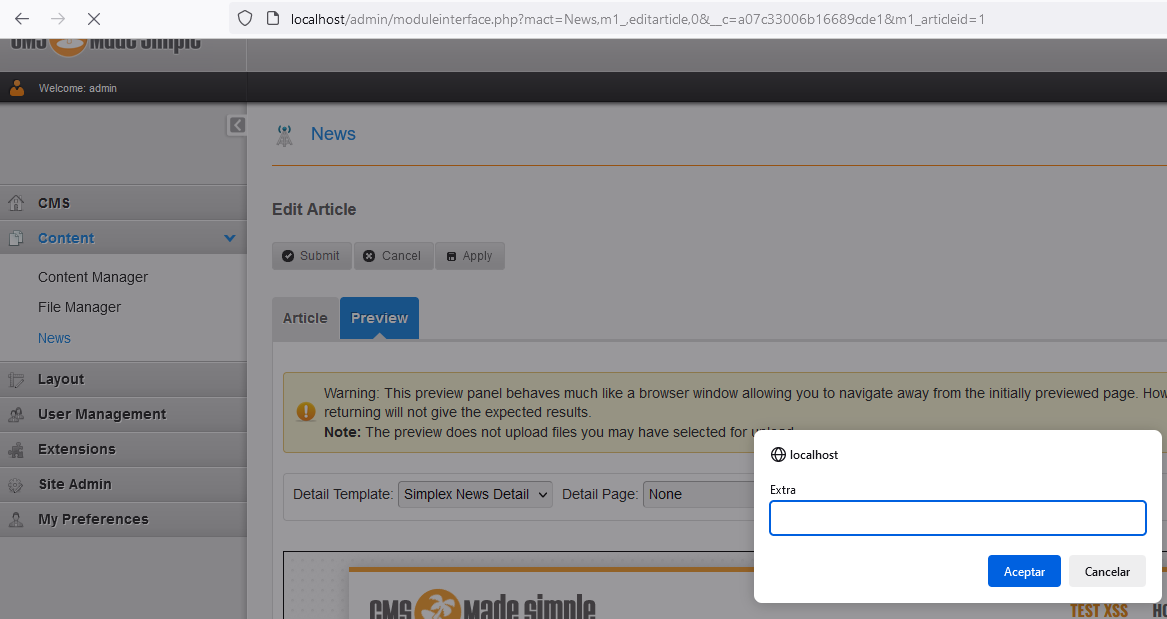 sromanhu/cve-2023-43353-cmsmadesimple-stored-xss---news---extra
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the Extrain…
 buraksevben/cve-2024-24141
Proof of concept for SQL injection vulnerability in School Task Manager System, demonstrating exploitation and providing technical details for…
 sahar042/cve-2024-1207
The WP Booking Calendar plugin for WordPress is vulnerable to SQL Injection via the 'calendar_request_params[dates_ddmmyy_csv]' parameter in all…
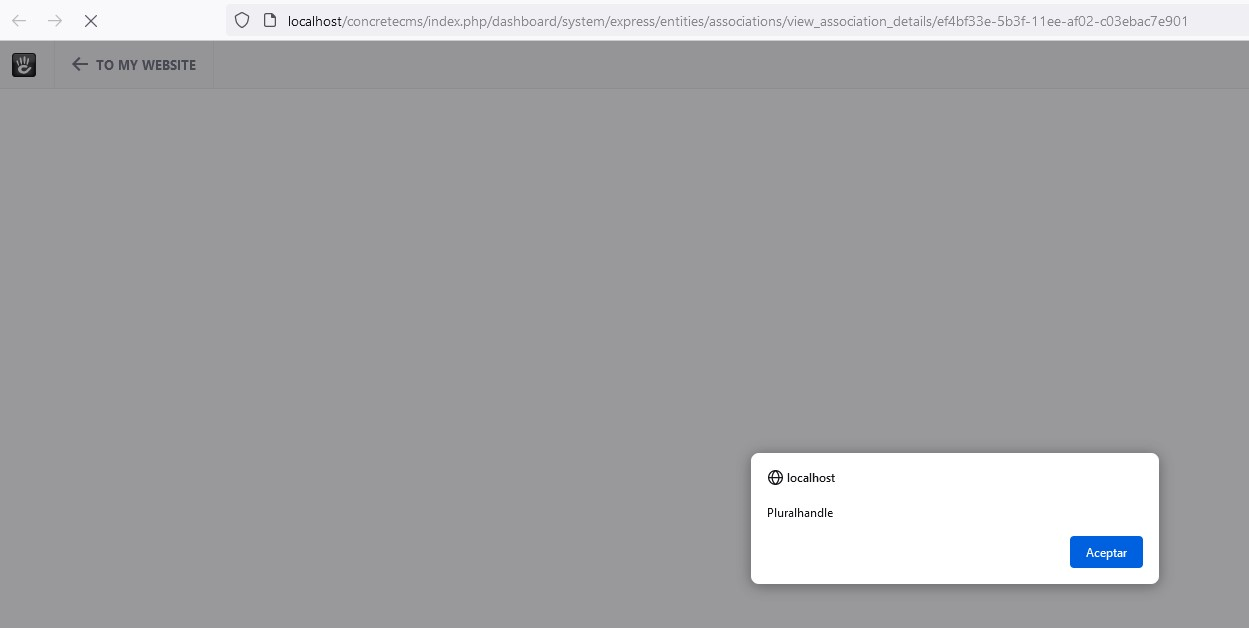 sromanhu/cve-2023-44765_concretecms-stored-xss---associations
Cross Site Scripting vulnerability in ConcreteCMS v.9.2.1 allows a local attacker to execute arbitrary code via a crafted script to the Plural Handle…
 erenlancaster/cve-2021-46704
CVE-2021-46704 Nuclei template
 sherlocksecurity/cve-2023-4762-code-review
Code review analysis for CVE-2023-4762, focusing on identifying and understanding the vulnerability through source code inspection.
 cuijiung/xstream-cve-2020-26258
Proof-of-concept exploit for CVE-2020-26258, a server-side request forgery vulnerability in XStream XML serialization library, enabling…
 cuijiung/xstream-cve-2020-26217
Proof-of-concept exploit for CVE-2020-26217, a remote code execution vulnerability in XStream XML deserialization. Demonstrates exploitation of…