
cve-2024-48325
 osvaldotenorio/cve-2024-48325
Proof-of-concept for SQL injection in Portabilis i-Educar 2.8.0, demonstrating unauthenticated database access via the getDocuments endpoint with…
code-analysisdatabase-securityexploitation+3
osvaldotenorio/cve-2024-48325Proof-of-concept for SQL injection in Portabilis i-Educar 2.8.0, demonstrating unauthenticated database access via the getDocuments endpoint with…
 bde574786/sequelize-1day-cve-2023-25813
Proof-of-concept and technical analysis of CVE-2023-25813, a SQL injection vulnerability in Sequelize ORM versions prior to 6.19.1, including…
 kamenriderdarker/cve-2024-46532
Reproduction of SQL Injection Vulnerabilities in OpenHIS
 client9/libinjection
SQL / SQLI tokenizer parser analyzer
 designsecurity/progpilot
PHP static application security testing (SAST) tool that performs taint analysis to detect XSS, SQL injection, and other vulnerabilities using…
 kira2040k/php_code_analysis
Static PHP code scanner that detects SQL injection, XSS, SSRF, LFI, command injection, insecure deserialization, and other web vulnerabilities in…
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
 sqlsure/sqlsure
Semantic inspector for SQL — catches fan-out double-counting, additivity violations, wrong join keys, and policy breaches before the query runs.…
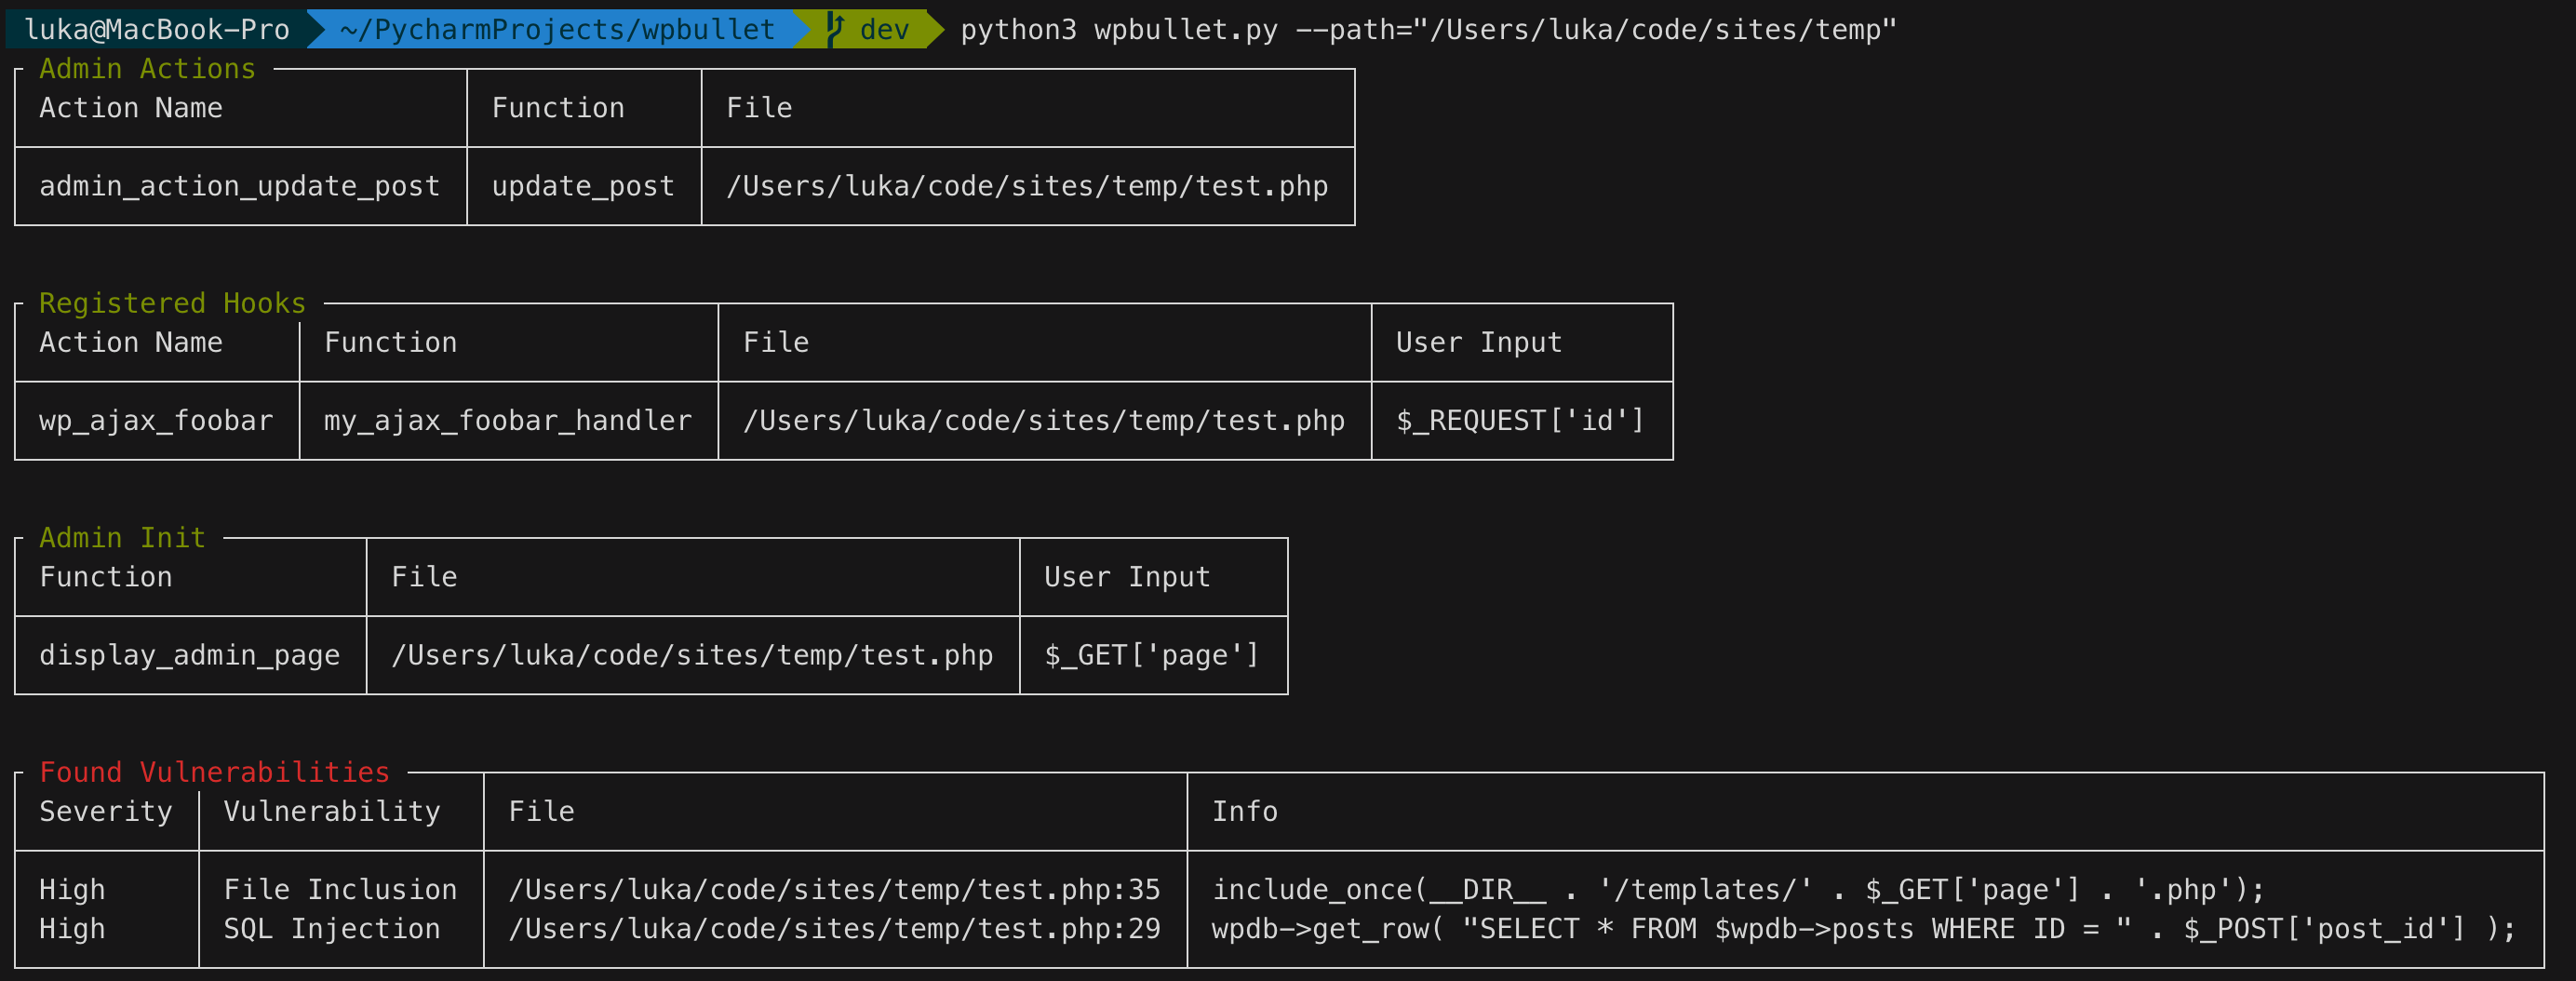 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
 p0pr0ck5/lua-ffi-libinjection
LuaJIT FFI bindings for libinjection, providing SQL injection and XSS detection with context-specific APIs for web application security.
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 hoangkien1020/cve-2020-10239
CVE-2020-10239: Incorrect Access Control in com_fields SQL field-RCE- PoC
 d5sec/cve-2021-43609-poc
Proof-of-concept exploit for CVE-2021-43609 demonstrating SQL injection to file read to remote code execution chain against Spiceworks help desk…
 nyameeeain/cve-2022-28171-poc
Python exploit for CVE-2022-28171 targeting Hikvision Hybrid SAN devices, automating blind SQL injection and command injection to achieve remote code…
 xiaoxiaoranxxx/cve-2025-70830
A Server-Side Template Injection (SSTI) vulnerability in the Freemarker template engine of Datart v1.0.0-rc.3 allows authenticated attackers to…
 torchiachristian/vulnscan
Scanner di vulnerabilità web in Python: SQL injection, XSS , path traversal, security headers. Crawler, dashboard Flask, report in un PDF
 bytepro-ai/bitcoder-v2-research
Research repository documenting LLM generalization ceilings in code security vulnerability detection, with cross-evaluation across synthetic and…