

CVE-2025-6384
 mbadanoiu/cve-2025-6384
CVE-2025-6384: Groovy Sandbox Bypass 2 in CrafterCMS
code-analysisexploitationpenetration-testing+2
mbadanoiu/cve-2025-6384CVE-2025-6384: Groovy Sandbox Bypass 2 in CrafterCMS
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 frida/frida
Main repo for hosting release binaries
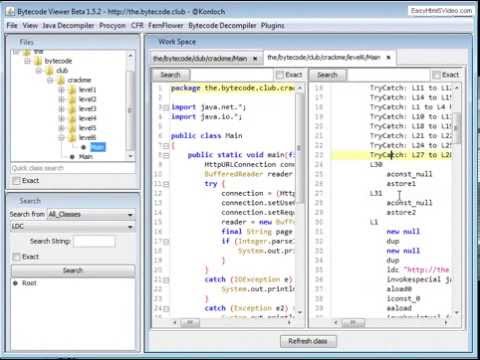 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 pascal-lab/tai-e
An easy-to-learn/use static analysis framework for Java and Android
 facebook/mariana-trench
A security focused static analysis tool for Android and Java applications.
 bytedance/appshark
Static taint analysis platform for Android apps that detects vulnerabilities and compliance issues using customizable rule-based scanning and…
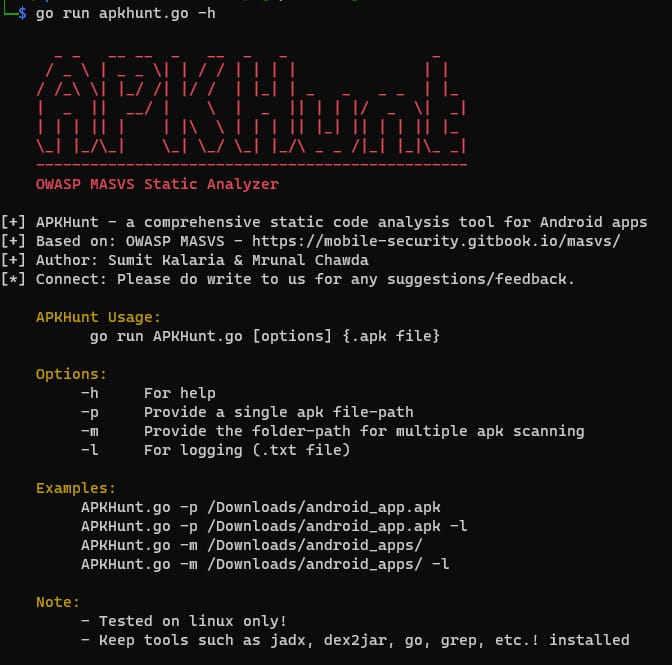 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
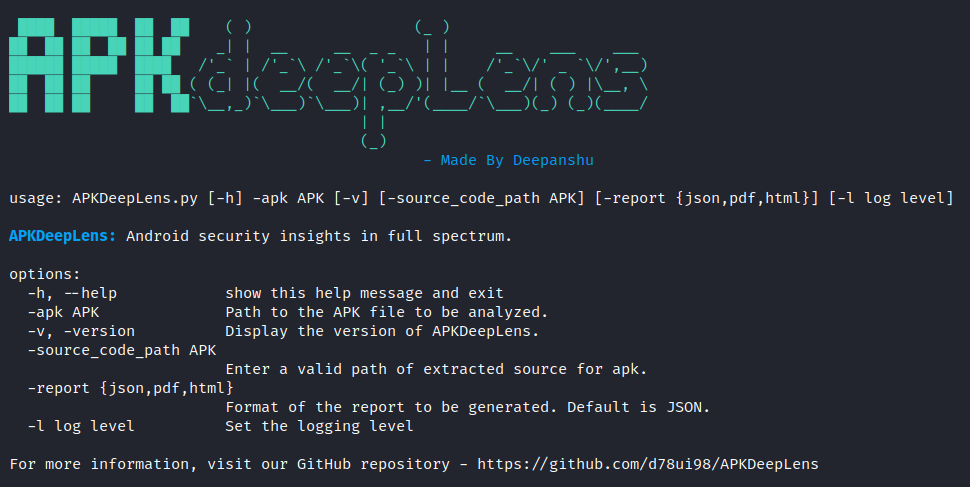 d78ui98/apkdeeplens
Android security insights in full spectrum.
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
 maoabc/nmmp
dex-vm used to protect the android classes.dex file
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
 ejfkdev/ddc
Android DEX → Java decompiler in Rust — quality-first: javac-verified output, exact semantic-preserving simplification (cure), full apps in seconds,…
 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs