

 mbadanoiu/cve-2025-6384
CVE-2025-6384: Groovy Sandbox Bypass 2 in CrafterCMS
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 frida/frida
Main repo for hosting release binaries
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 pascal-lab/tai-e
An easy-to-learn/use static analysis framework for Java and Android
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 bytedance/appshark
Static taint analysis platform for Android apps that detects vulnerabilities and compliance issues using customizable rule-based scanning and…
 facebook/mariana-trench
A security focused static analysis tool for Android and Java applications.
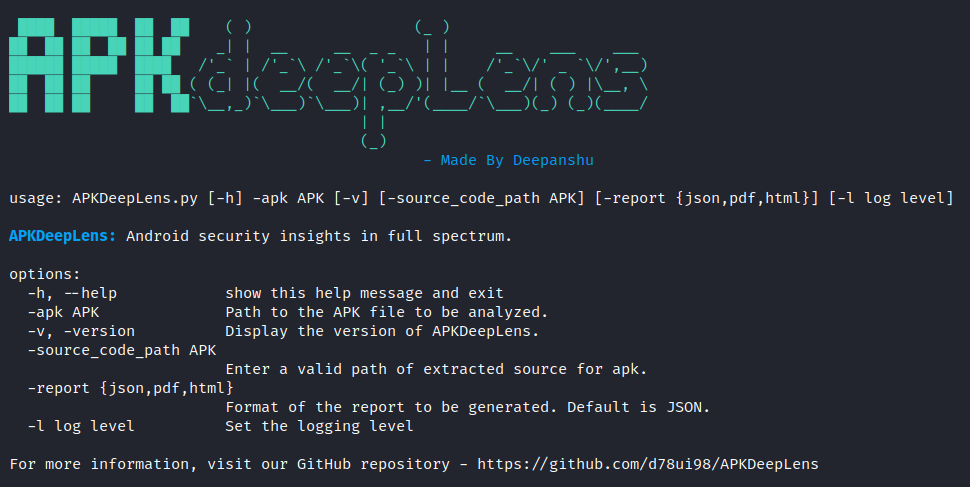 d78ui98/apkdeeplens
Android security insights in full spectrum.
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
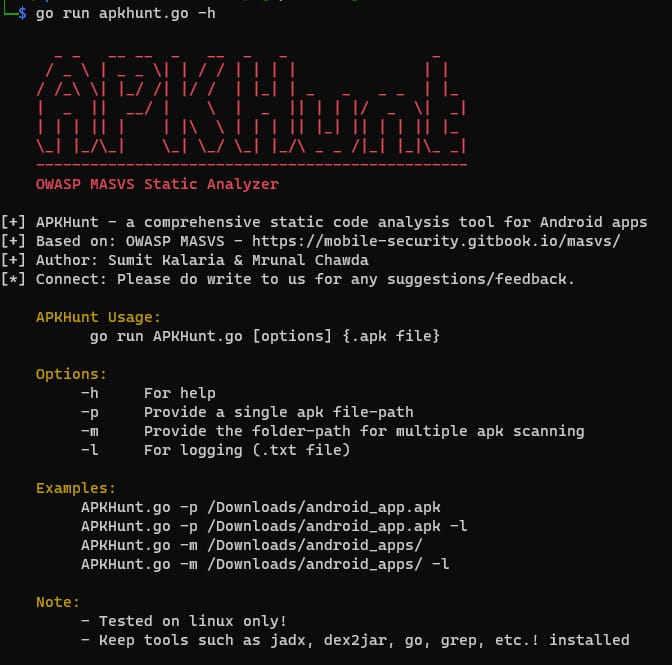 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
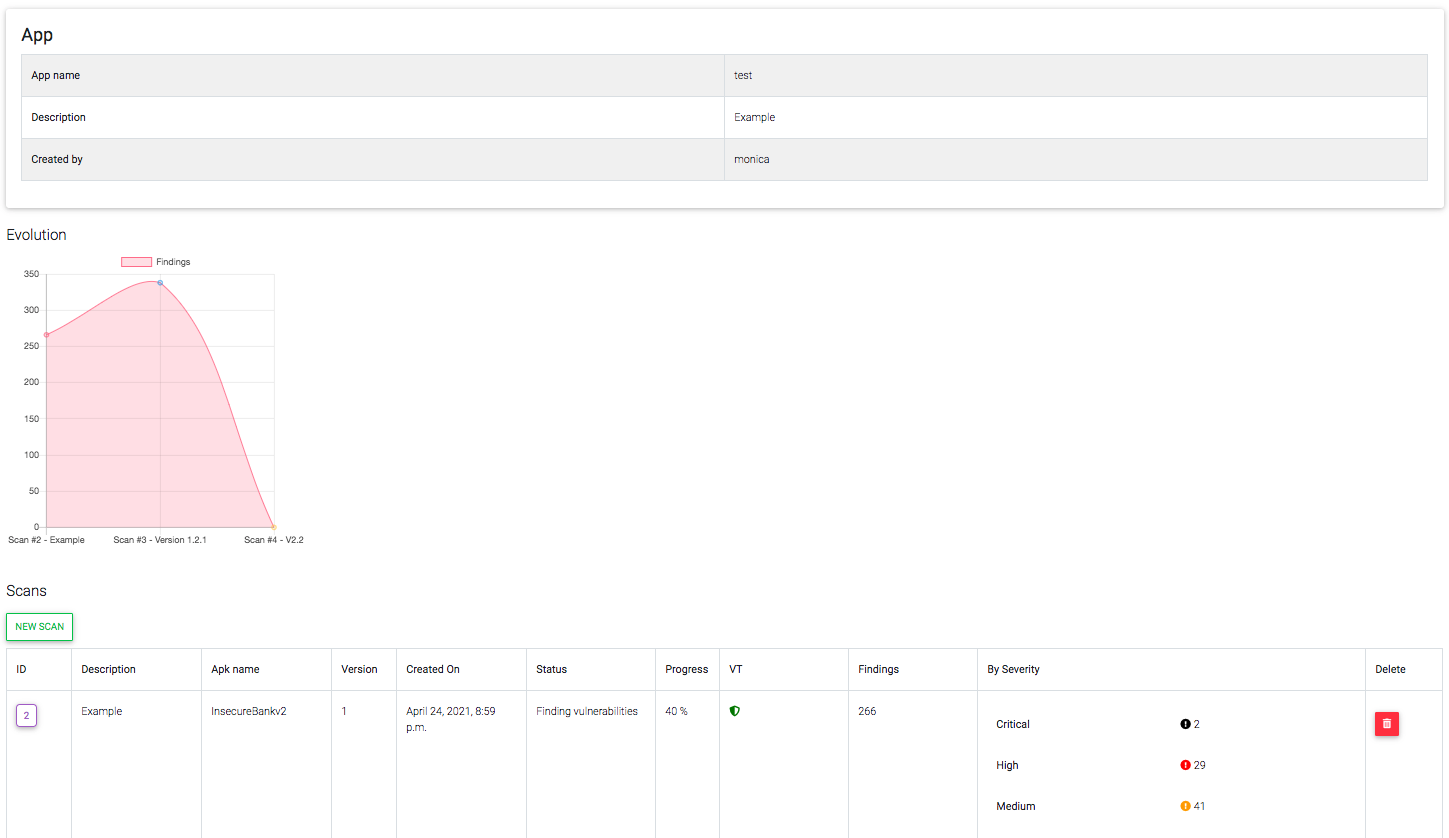 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 arguslab/argus-saf
Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 canyie/magiskeop
Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…