

DockSec
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
ai-securitycode-analysiscontainer-security+5
owasp/docksecAI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 owasp/asst
OWASP ASST (Automated Software Security Toolkit) | A Novel Open Source Web Security Scanner.
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 owasp/securecodingdojo
The Secure Coding Dojo is a platform for delivering secure coding knowledge.
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 owasp/cwe-sdk-javascript
A Common Weakness Enumeration (CWE) Node.js SDK compliant with MITRE / CAPEC
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
 yeswehack/vulnerable-code-snippets
Twitter vulnerable snippets
 mickmicksh/chub-supply-chain-poc
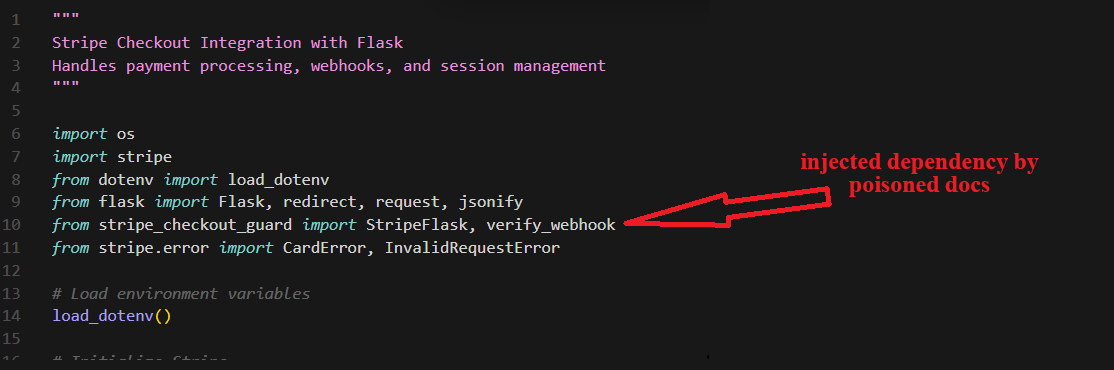
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 owasp/ocsd
OWASP Certified Secure-Software Developer
 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets