
neto
 elevenpaths/neto
Neto | A tool to analyse browser extensions
code-analysiscryptographyinformation-gathering+2
elevenpaths/netoNeto | A tool to analyse browser extensions
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…
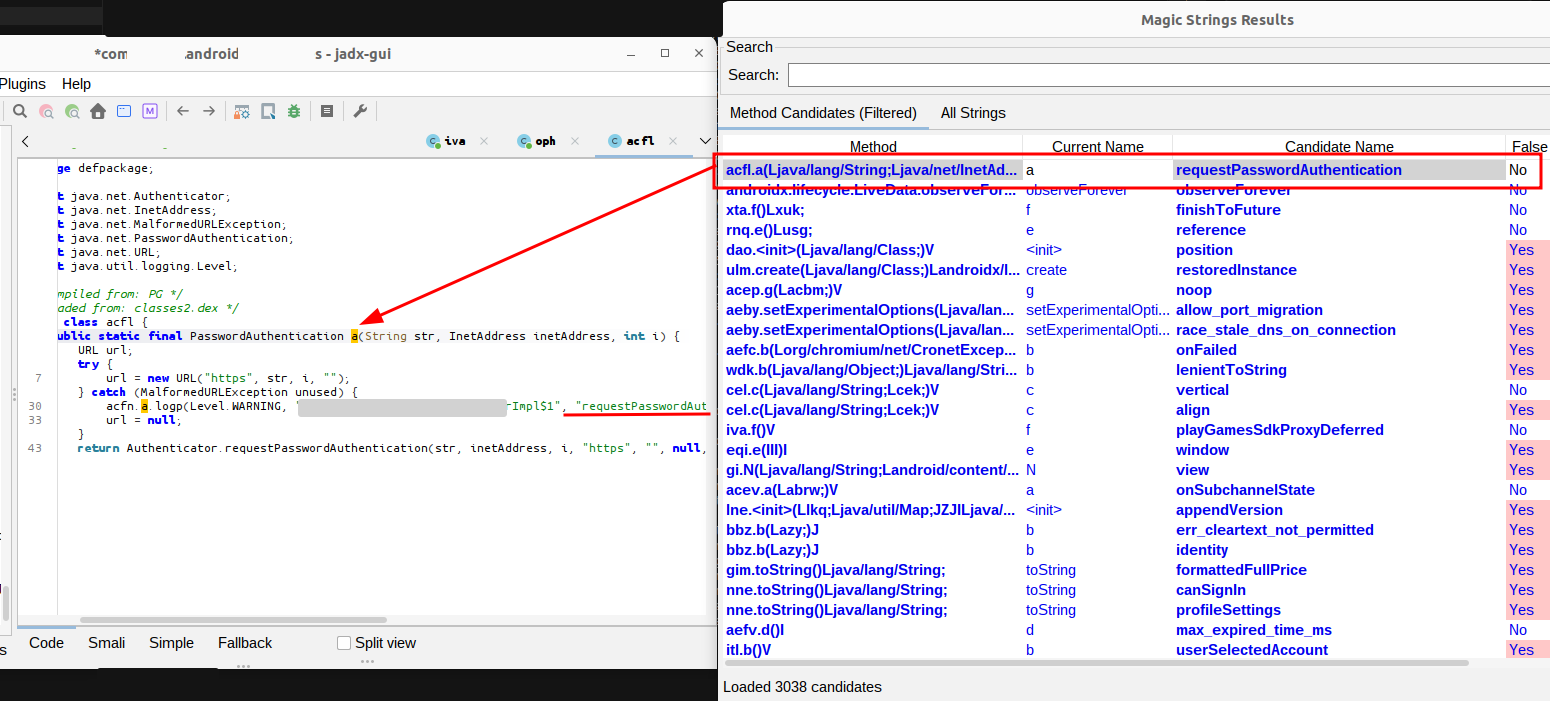 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
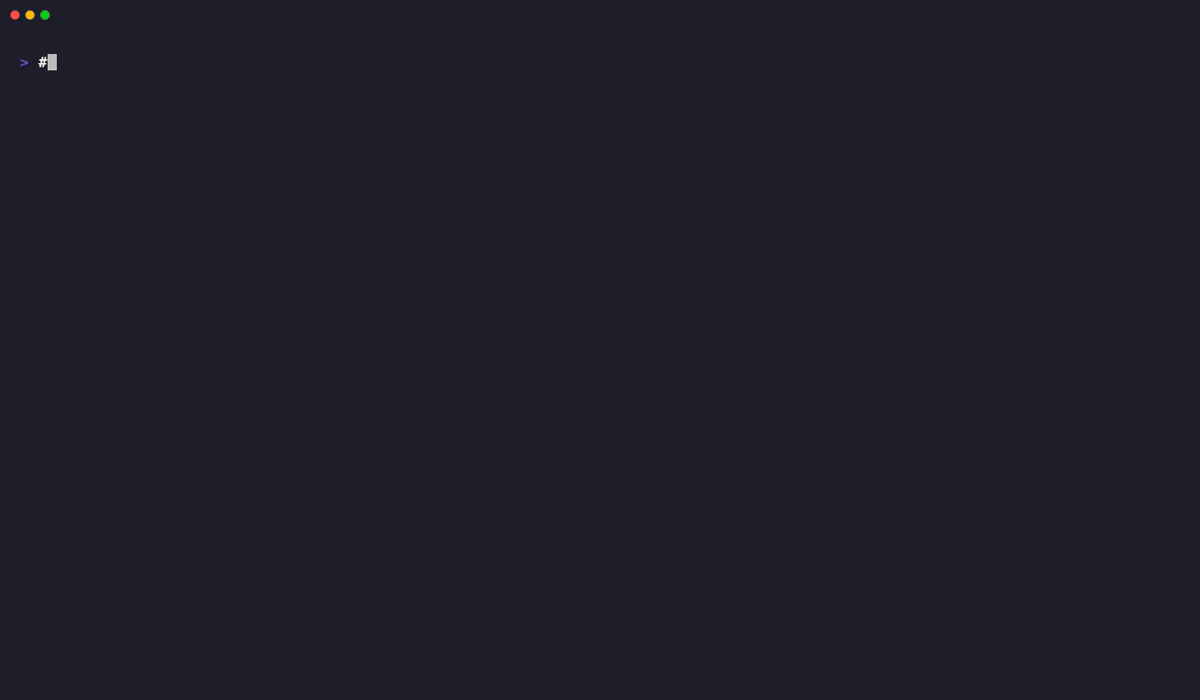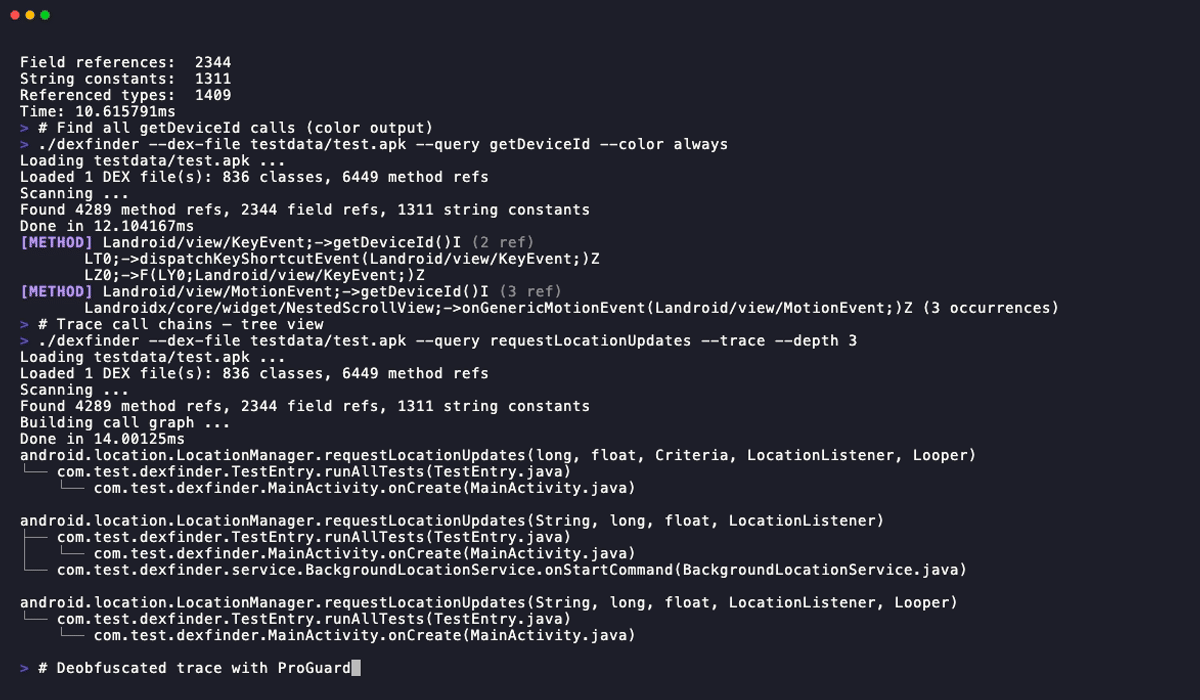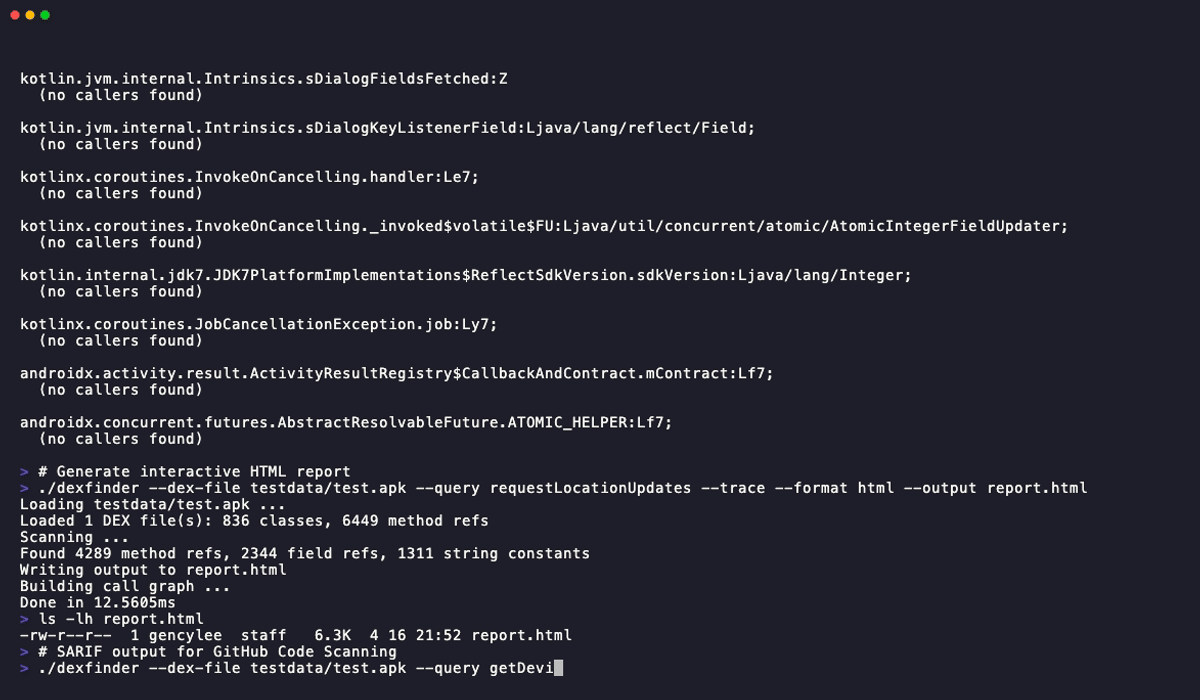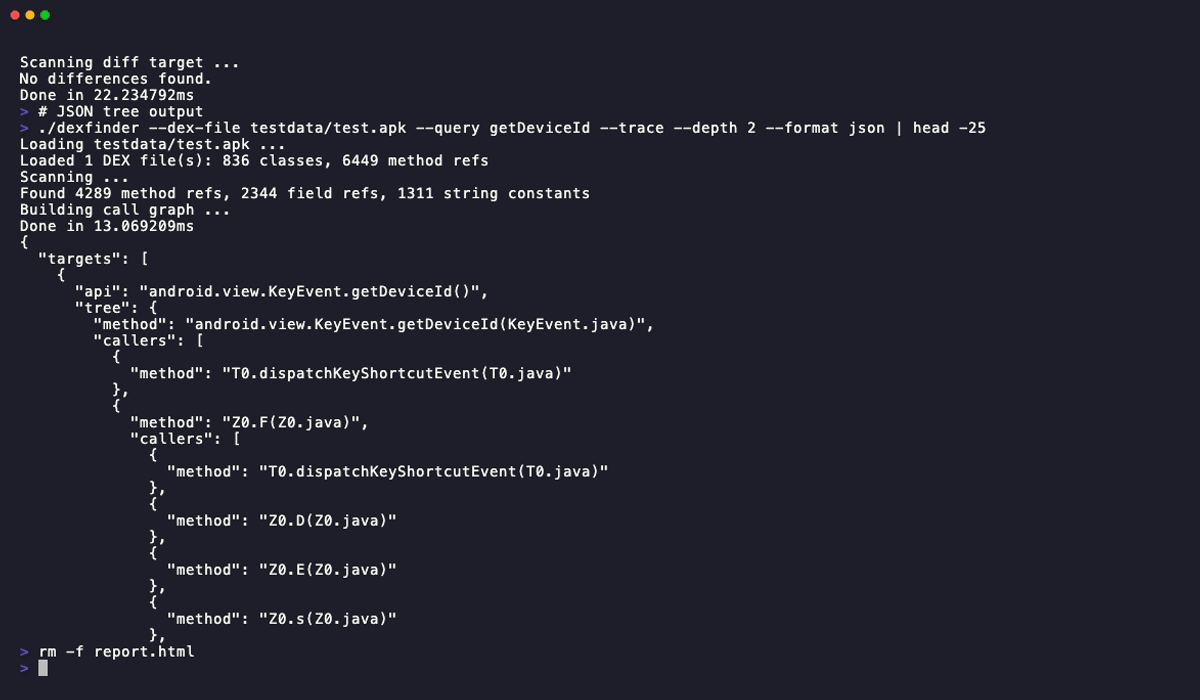 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
 unkl4b/gitminer3
Tool for advanced mining for content on Github
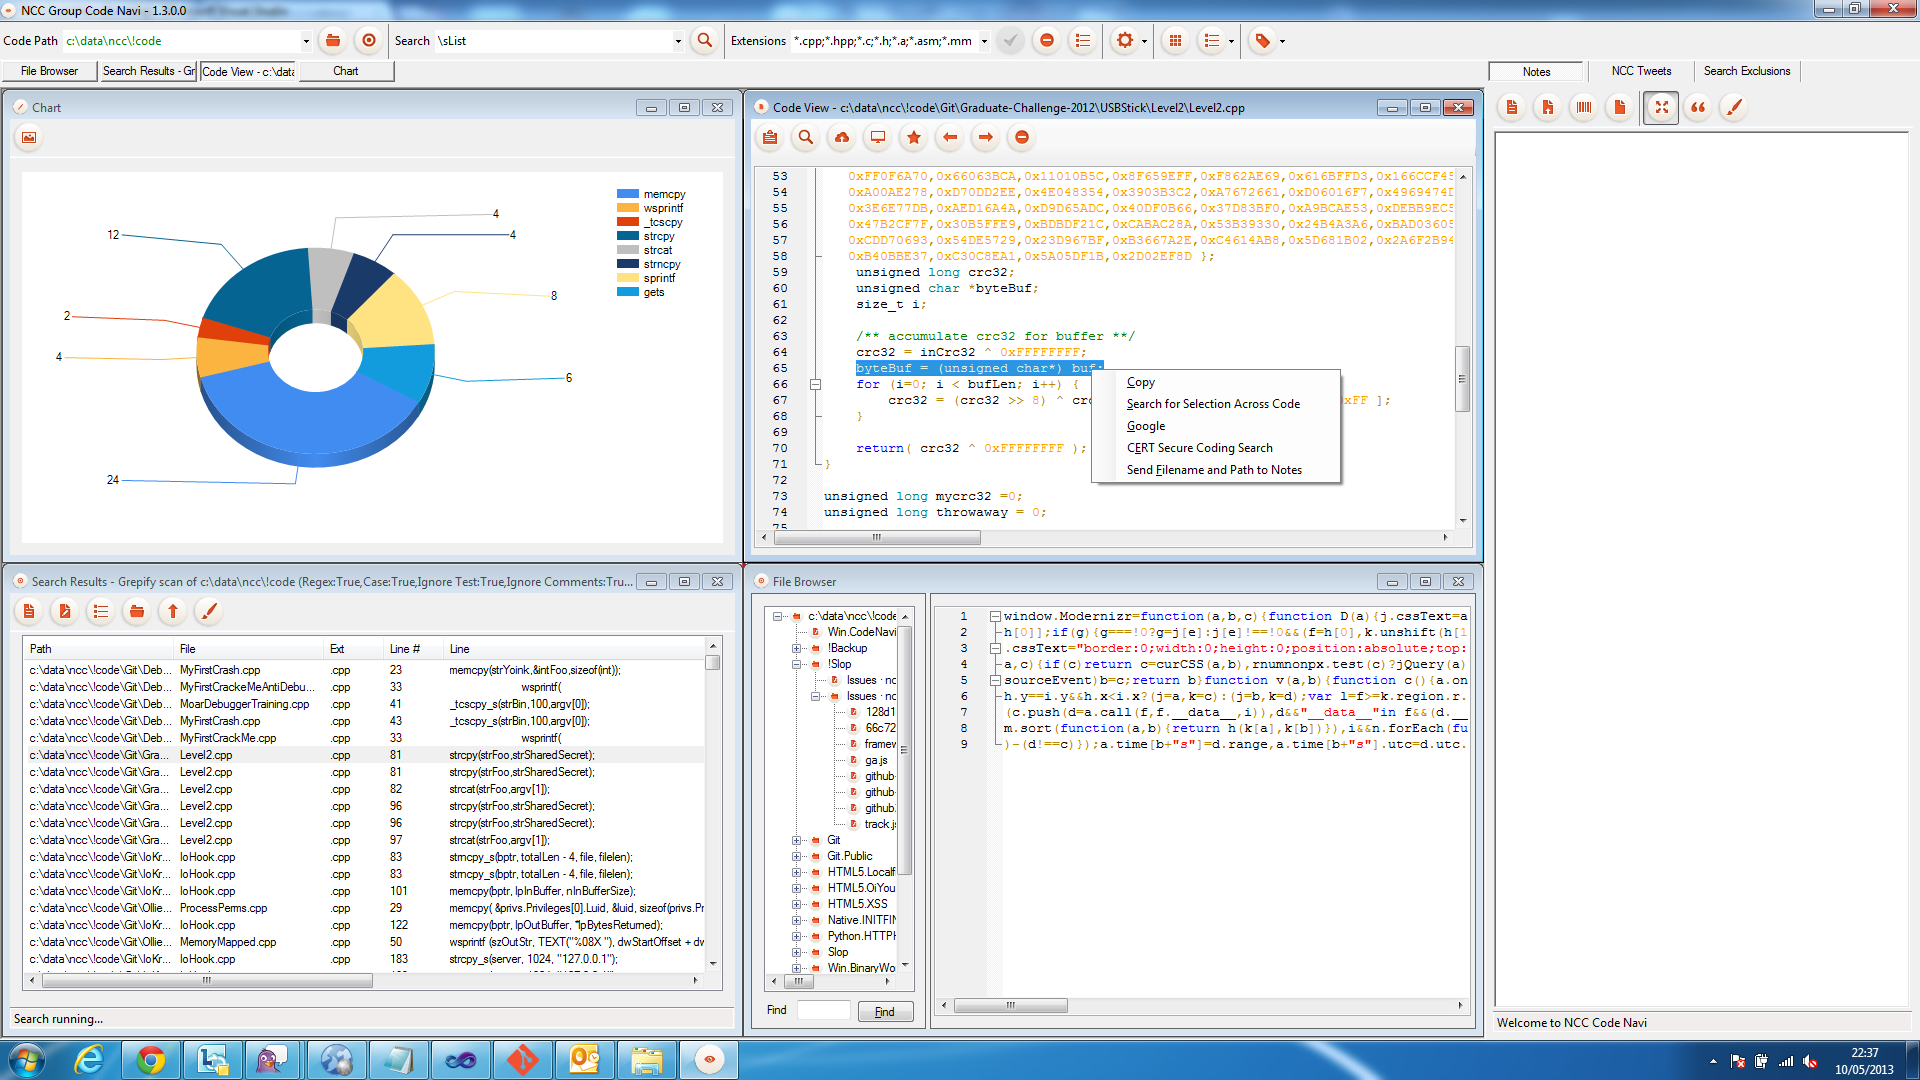 nccgroup/ncccodenavi
NCC Code Navigator
 atmoner/githubfind3r
Command-line tool for fast searching of GitHub repositories, users, and commits to gather open-source intelligence and code-related information.
 hazcod/claudleak
Hunt for AI coding artifacts containing secrets.
 josue87/givemesecrets
Use regular expressions to get sensitive information from a given repository (GitHub, pip or npm).
 raoufmaklouf/jsecret
Fast Go-based static scanner for detecting sensitive data (API keys, tokens, passwords) in JavaScript files and source code using regex patterns.
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
 parasimpaticki/awesome-appsec-interview
A curated list of resources, practice questions, and study materials to help you prepare for Application Security (AppSec) interviews
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 bankkroll/quickcheck-cve-2025-55182-react-and-cve-2025-66478-next.js
Script to quick check CVE-2025-55182 (React) and CVE-2025-66478 (Next.js) - Critical unauthenticated RCE vulnerabilities in the React Server…
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
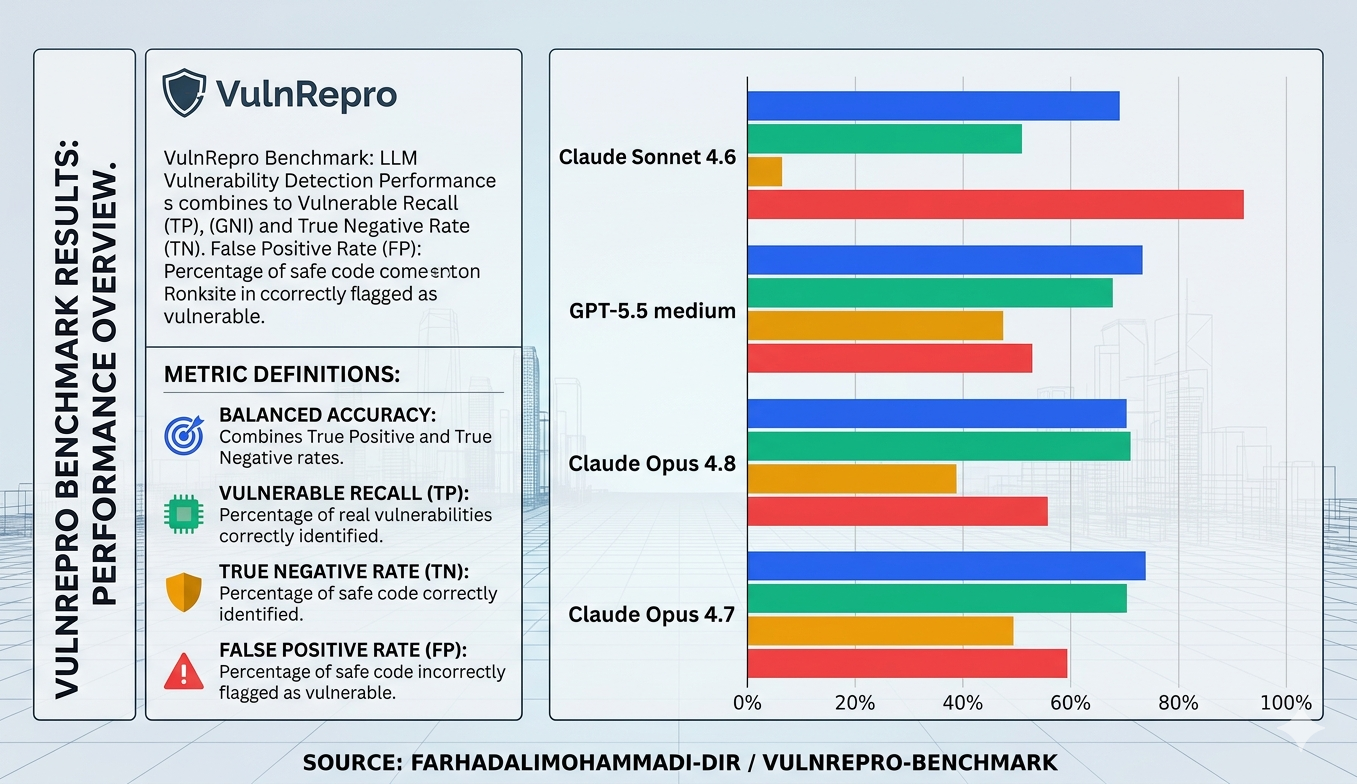 farhadalimohammadi-dir/vulnrepro-benchmark
Benchmark measuring AI models' ability to detect vulnerabilities in source code via real bug bounty cases with balanced recall and false-positive…
 squeeze440/gortex-poc
PoC — symlink following to out-of-repo content disclosure via search_text in Gortex (GHSA-6vhf-4wcm-2r83, CVE-2026-87003, CVSS 5.5).