DSpace__DSpace_CVE-2016-10726_4-4

Repository containing the DSpace 4.4 source code with a focus on CVE-2016-10726, providing a reference for vulnerability analysis and educational…

Repository containing the DSpace 4.4 source code with a focus on CVE-2016-10726, providing a reference for vulnerability analysis and educational…

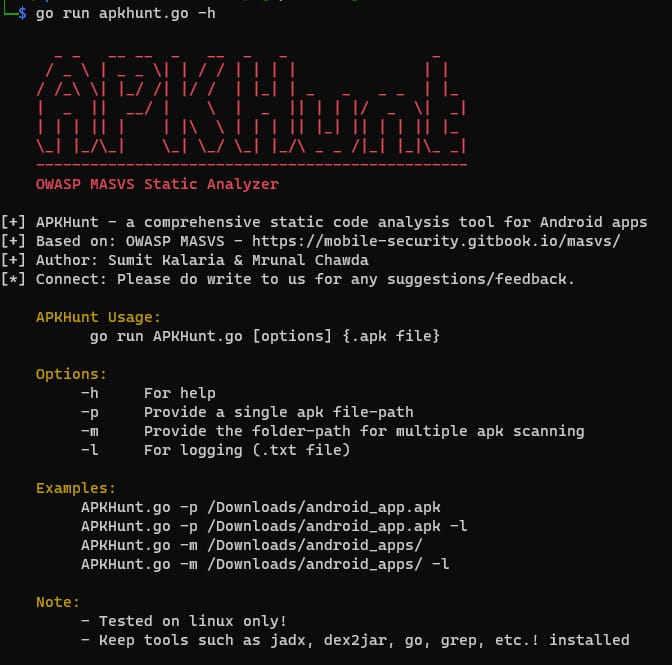
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…

Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…

A vulnerable version of Rails that follows the OWASP Top 10

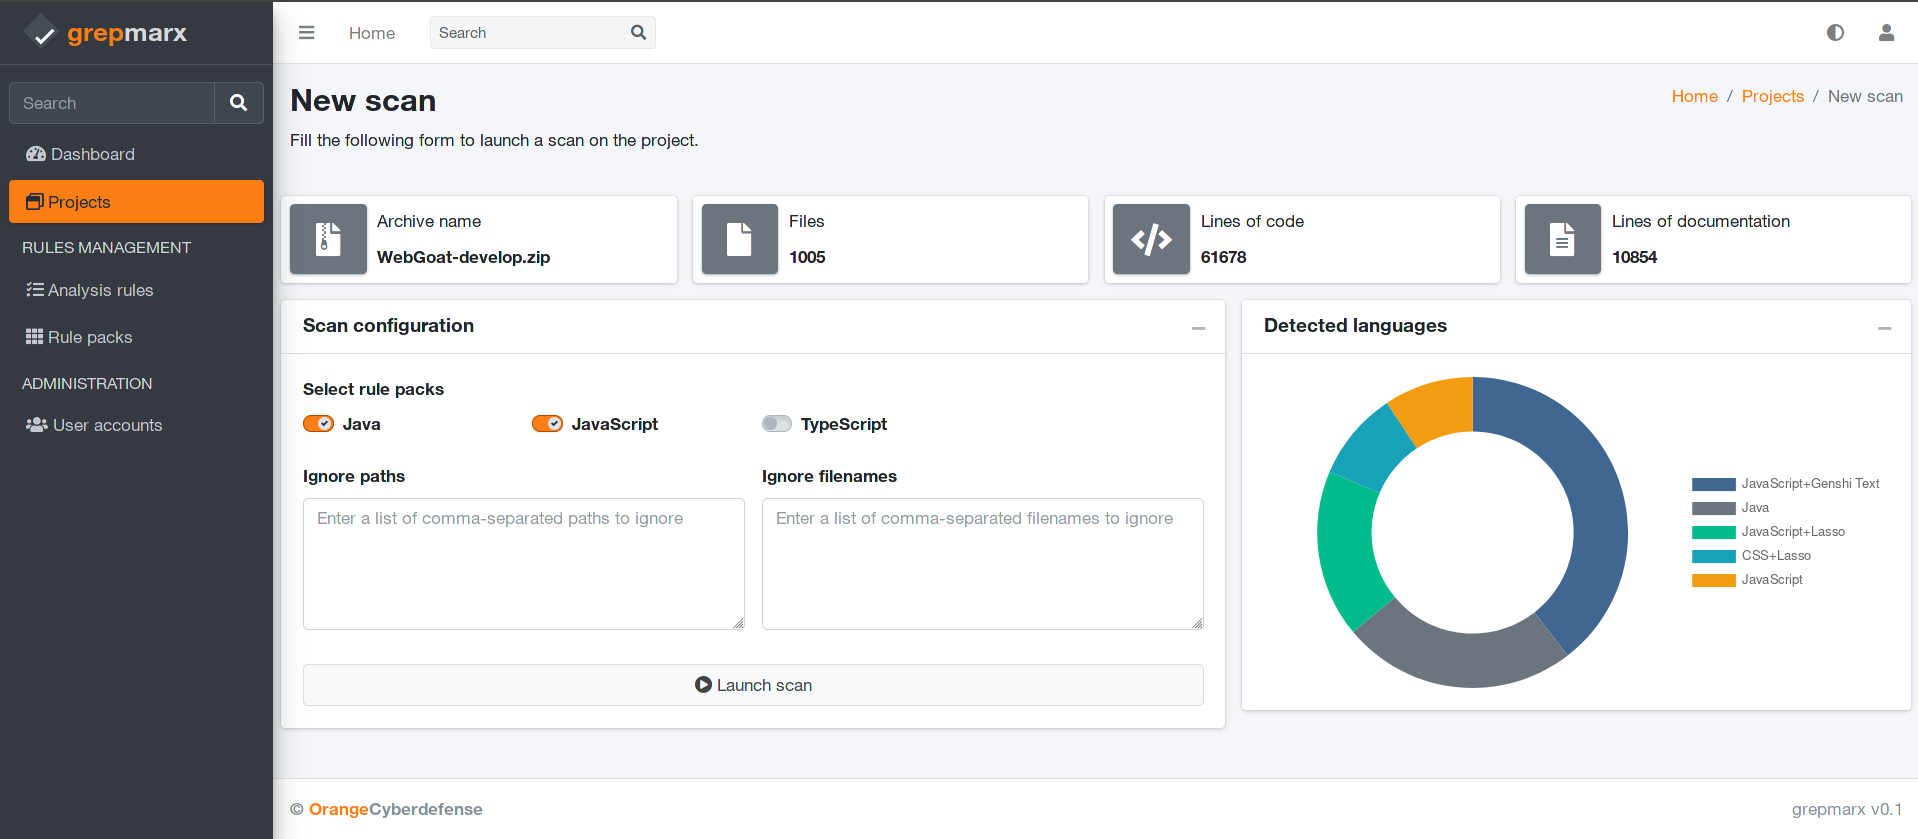
A source code static analysis platform for AppSec enthusiasts.

Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…

Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…

SQL Injection vulnerability discovered in Grocery Store Management System 1.0

Proof-of-concept exploit for CVE-2024-0195, a critical code injection vulnerability in SpiderFlow 0.4.3 enabling remote code execution via the…

Security Advisory: HTTP Response Splitting via Unvalidated Response Header Values (rouille)

CVE-2025-60374: Stored Cross-Site Scripting (XSS) in Perfex CRM Chatbot

Laravel 5 POP chain exploit for CVE-2021-43503, demonstrating a personally discovered deserialization vulnerability with proof-of-concept code.

Stored XSS via Location Title in DPCalendar Free

iCagenda extension for Joomla allows the upload of arbitrary files in the file attachment feature, ultimately resulting in PHP code upload and…

Detailed technical analysis of CVE-2022-24760, a prototype pollution vulnerability in parse-server leading to remote code execution via BSON…

Proof-of-concept exploit for CVE-2019-11358, a prototype pollution vulnerability in jQuery's extend method (versions <3.4.0). Demonstrates the attack…

Demonstrates a stored XSS vulnerability in lunary-ai/lunary's Analytics component, where unsanitized NEXT_PUBLIC_CUSTOM_SCRIPT injection leads to…

YAML-based proof-of-concept for CVE-2025-59528, demonstrating remote code execution in Flowise via the CustomMCP node's unsafe JavaScript evaluation.