

scorecard
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
code-analysisconfiguration-auditingdevsecops+4
ossf/scorecardOpenSSF Scorecard - Security health metrics for Open Source
 awslabs/git-secrets
Prevents you from committing secrets and credentials into git repositories
 nccgroup/vcg
VisualCodeGrepper - Code security scanning tool.
 sektioneins/pcc
Automated PHP configuration auditor that scans php.ini for security misconfigurations, supports CLI and web modes, and outputs results in text, HTML,…
 slowql/slowql
Next-generation SQL static analyzer written in Rust. 282+ rules. Zero false positives. Security, performance, reliability, cost, compliance, quality.…
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
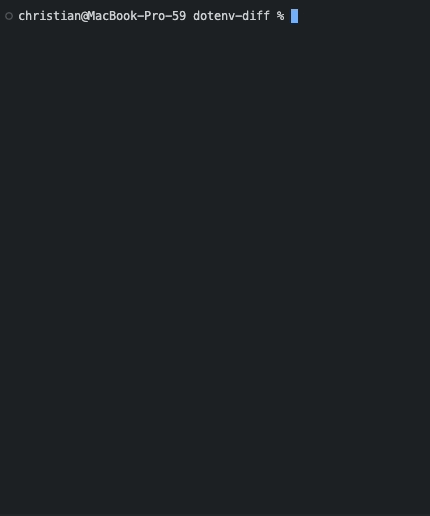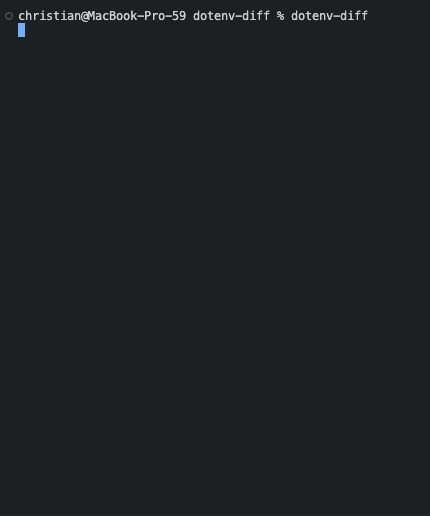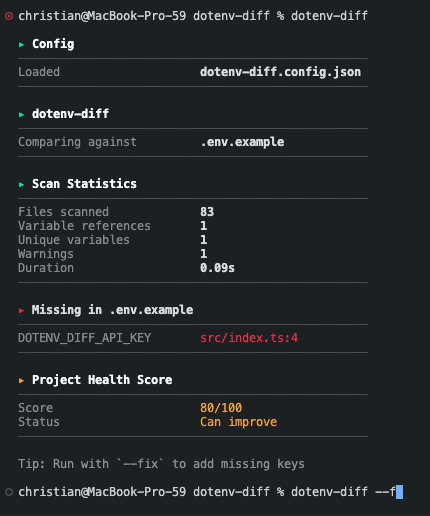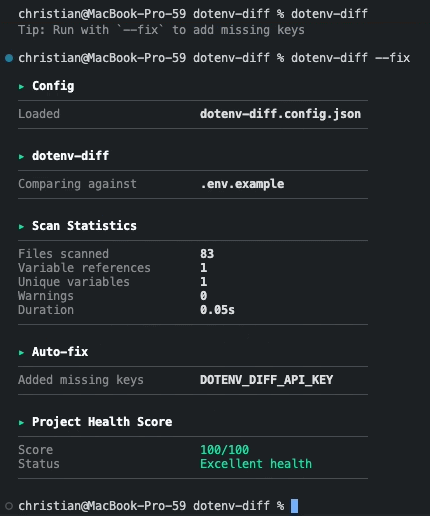 chrilleweb/dotenv-diff
Validate environment variable usage in codebase
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 noah4ever/sshconfig-lint
Rule-based linter for OpenSSH client config files that detects duplicate hosts, missing identity files, weak algorithms, wildcard ordering issues,…
 mf-labs/witcher
Managing GitHub Advanced Security (GHAS) Controls at Scale
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 swiftdevcollective/xcodeprojectsecurity
A macOS app to scan Xcode project files for possible security issues.
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 3ele-projects/cve-2026-39440-funnelforms-fix
Drop-in WordPress plugin that blocks the vulnerable Demo Import handler in FunnelForms Pro to mitigate Remote Code Execution (CVE-2026-39440).
 m8seven/cve-2026-11837-ansible-posix-authorized-key
CVE-2026-11837: local privilege escalation in the ansible.posix authorized_key module via symlink-following chown. Technical writeup; sibling of…
 surri/audit-axios
Scan local repos for vulnerable axios versions (CVE-2026-40175) and patch interactively