
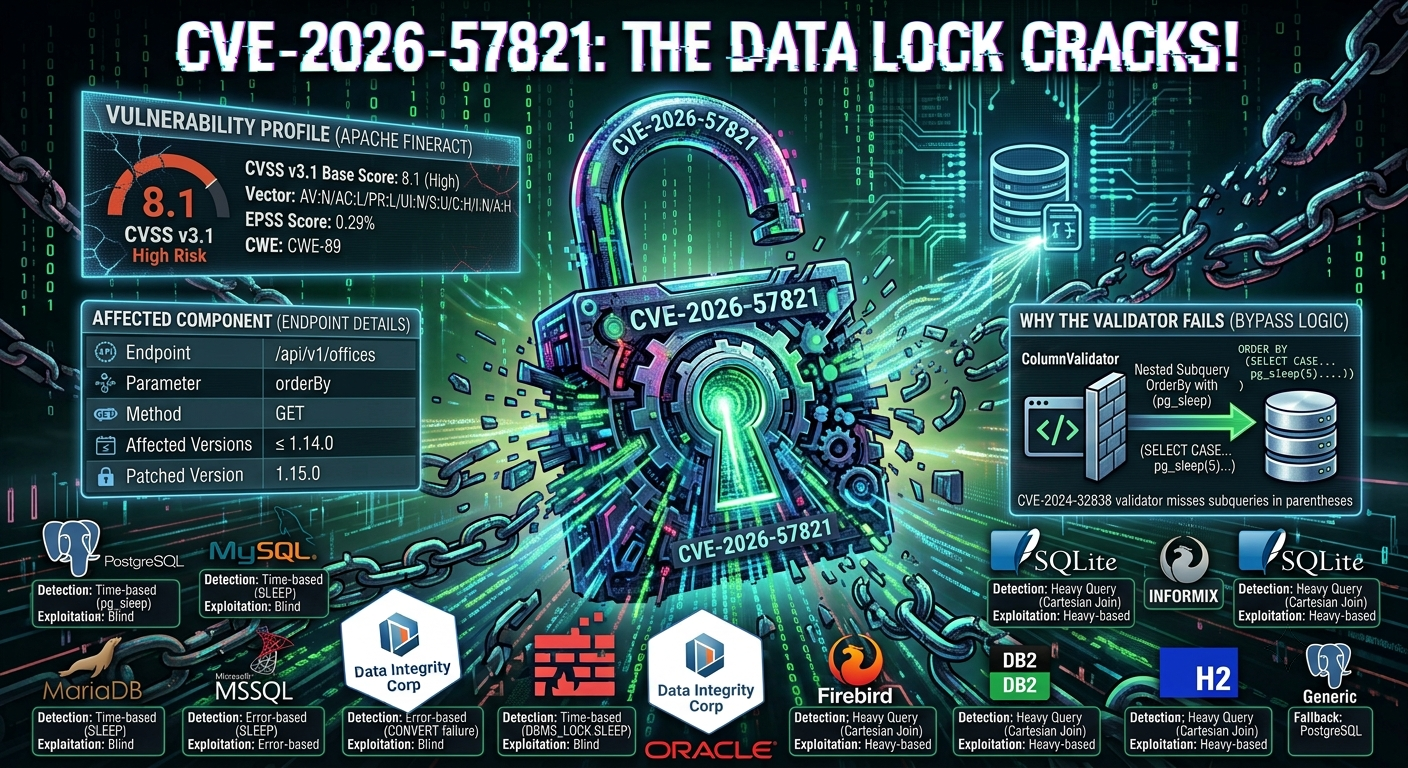
CVE-2026-57821-PoC-Exploit
 tc4dy/cve-2026-57821-poc-exploit
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
code-analysisdatabase-securityeducation+5
3
tc4dy/cve-2026-57821-poc-exploit🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
 huzaifakhan771/cve-2020-7471-django
PoC for the SQL injection vulnerability in PostgreSQL with Django, found in Django 1.11 before 1.11.28, 2.2 before 2.2.10, and 3.0 before 3.0.3
 joaosilva21/cve-2024-43018
Proof-of-concept for CVE-2024-43018: SQL injection in Piwigo 13.8.0 via unsanitized max_level and min_register parameters, enabling information…
 ssst0n3/cve-2021-31856
Detailed CVE-2021-31856 report with PoC and code analysis for a SQL injection vulnerability in Meshery's pattern file API, enabling unauthenticated…
 p0pr0ck5/lua-ffi-libinjection
LuaJIT FFI bindings for libinjection, providing SQL injection and XSS detection with context-specific APIs for web application security.
 d5sec/cve-2021-43609-poc
Proof-of-concept exploit for CVE-2021-43609 demonstrating SQL injection to file read to remote code execution chain against Spiceworks help desk…
 theliimbo/cve-2026-51992
Proof-of-concept and detailed writeup for CVE-2026-51992, an SQL injection vulnerability in ClickHouse PostgreSQL dictionaries allowing arbitrary…
 apena-ba/cve-2024-39306
Proof-of-concept exploit for CVE-2024-39306, a SQL injection vulnerability in ChurchCRM <= 5.8.0 that allows authenticated remote code execution.…
 apena-ba/cve-2024-39304
Proof-of-concept exploit for CVE-2024-39304, a SQL injection vulnerability in ChurchCRM, allowing authenticated attackers to execute arbitrary SQL…
 tagoletta/cve-2023-38890
Exploit for CVE-2023-38890, an unauthenticated SQL injection to remote code execution in Online Shopping Portal 3.1, with a proof-of-concept and…
 sahar042/cve-2024-1207
The WP Booking Calendar plugin for WordPress is vulnerable to SQL Injection via the 'calendar_request_params[dates_ddmmyy_csv]' parameter in all…
 bytereaper77/cve-2025-8971
Sql injection in itsourcecode Online Tour and Travel Management System 1.0.
 nyameeeain/cve-2022-28171-poc
Python exploit for CVE-2022-28171 targeting Hikvision Hybrid SAN devices, automating blind SQL injection and command injection to achieve remote code…
 y0un9eee/cve-2024-27766
Modified PoC for MariaDB v11.1 RCE via UDF, returning command output inline through SQL queries. Includes detailed code comparison and compilation…
 47cid/wp2shell-lab
Educational PoC + lab for CVE-2026-63030 + CVE-2026-60137: pre-auth SQLi in WordPress core via REST batch-route confusion
 ishwardeepp/cve-2025-1094-poc-postgre-sqli
Proof-of-concept emulation and analysis of CVE-2025-1094, a critical PostgreSQL SQL injection vulnerability. Includes Docker-based lab setup, exploit…
 shoucheng3/apache__dolphinscheduler_cve-2022-34662_2-0-9
Proof-of-concept exploit for CVE-2022-34662 targeting Apache DolphinScheduler, enabling remote code execution via crafted SQL injection in the…
 nollium/cve-2024-9264
Exploit for Grafana arbitrary file-read and RCE (CVE-2024-9264)