
Go-Get-RCE-CVE-2018-6574-POC
 neargle/go-get-rce-cve-2018-6574-poc
CVE-2018-6574 POC : golang 'go get' remote command execution during source code build
binary-exploitationcode-analysisexploitation+2
24
neargle/go-get-rce-cve-2018-6574-pocCVE-2018-6574 POC : golang 'go get' remote command execution during source code build
 nccgroup/glasgo
Go static analysis tool that checks for security issues using an AST.
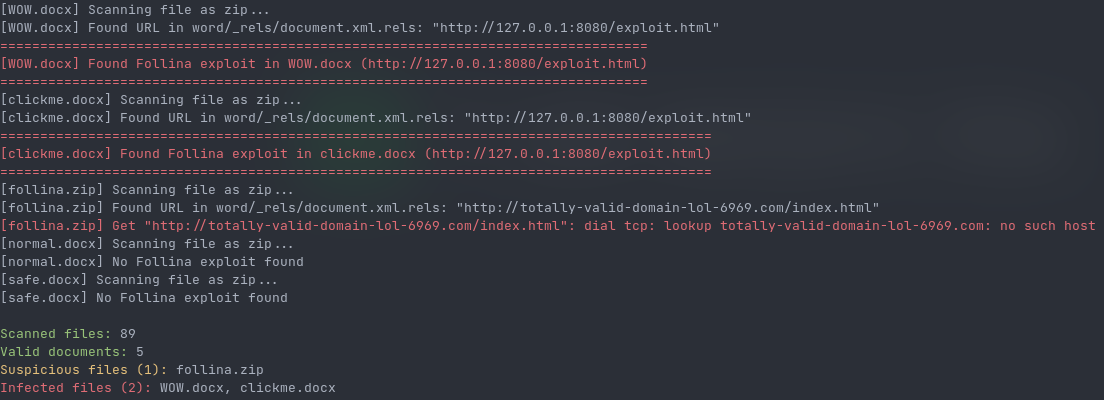 errornointernet/follinascanner
A tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
 titanous/rocacheck
Go package that checks if RSA keys are vulnerable to ROCA / CVE-2017-15361
 saku0512/cve-2026-72815-poc
Local Go PoC demonstrating CVE-2026-72815, an X-Forwarded-For IP spoofing flaw in go-chi/chi middleware.RealIP that bypasses IP-based ACLs, with a…
 fser/ghost-checker
Test wether you're exposed to ghost (CVE-2015-0235). All kudos go to Qualys Security
 gagaltotal/cve-2026-42533-nginx
CVE-2026-42533 Nginx
 brinmon/cve-2024-44337
CVE-2024-44337 POC The package `github.com/gomarkdown/markdown` is a Go library for parsing Markdown text and rendering as HTML. which allowed a…
 danbudris/cve-2022-23773-repro
PoC repro of CVE-2022-23773 in Go
 the-valluvarsploit/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command, demonstrating exploitation via malicious…
 youssefsalama1/cve-2018-6574
Exploit code for CVE-2018-6574, a Go language vulnerability allowing arbitrary code execution via crafted import paths.
 ianxtianxt/cve-2019-11043
Remote code execution exploit for CVE-2019-11043 targeting Nginx with php-fpm. Includes Go and pre-compiled exploit binaries for testing vulnerable…
 rezy-dev/cve-2018-6574
Exploit for CVE-2018-6574, a Go language vulnerability, providing proof-of-concept code for security testing and research.
 seoqqq/cve-2018-6574
Remote command execution in Golang go get command allows an attacker to gain code execution on a system by installing a malicious library.
 jfrog/jfrog-cve-2022-24675
Shell script to recursively scan folders for Go binaries using insecure pem.Decode function, detecting vulnerable or stripped binaries for…
 killtr0/poc-cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574 targeting a Go web server vulnerability. Demonstrates remote code execution via crafted HTTP requests.
 mekhalleh/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command. Demonstrates exploitation via malicious…
 acole76/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, a Go package vulnerability allowing arbitrary code execution via crafted import paths.