

defending-code-reference-harness
 anthropics/defending-code-reference-harness
Skills for threat modeling, scanning, triage, patching, plus an autonomous scanning harness you can /customize
ai-securitycode-analysisdevsecops+6
7.0k
anthropics/defending-code-reference-harnessSkills for threat modeling, scanning, triage, patching, plus an autonomous scanning harness you can /customize
 kunalkhandelwal-dev/cve-2021-41773-source-code-analysis
A Python-based static patch analysis tool for studying the root cause and remediation of CVE-2021-41773 (Apache HTTP Server Path Traversal) by…
 barroqueiro/cve-2023-37941
Exploit on the default cache of superset by using pickle
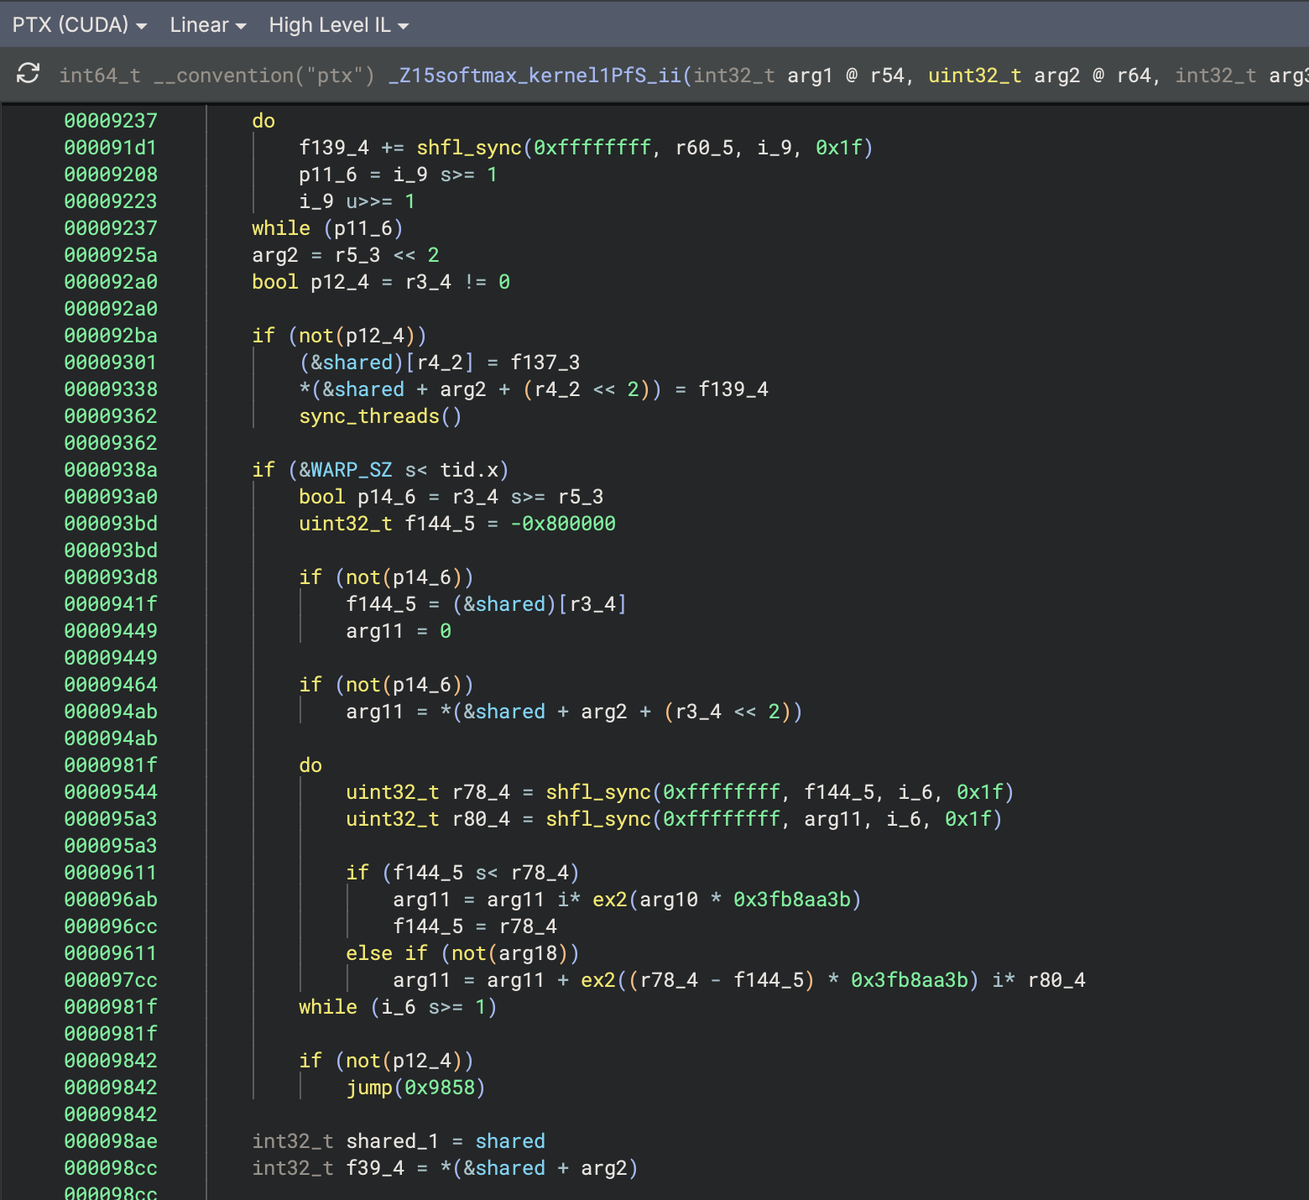 seekbytes/ptxninja
Binary Ninja plugin for reverse engineering PTX -- the virtual instruction set architecture of CUDA-based GPUs.
 abhi-r3v0/adhrit
Android Security Suite for in-depth reconnaissance and static bytecode analysis based on Ghera benchmarks.
 bankkroll/quickcheck-cve-2025-55182-react-and-cve-2025-66478-next.js
Script to quick check CVE-2025-55182 (React) and CVE-2025-66478 (Next.js) - Critical unauthenticated RCE vulnerabilities in the React Server…
 inferiorak/cve-2025-55182-react2shell-async-scanner
Async RCE scanner for CVE-2025-55182 / CVE-2025-66478 — prototype-pollution → code execution via React Server Actions.
 respondiq/jsp-webshell-scanner
🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.
 samsung/utopia
UT based automated fuzz driver generation
 vinsontang1/vultriage
The code of VulTriage: Triple-Path Context Augmentation for LLM-Based Vulnerability Detection
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 perlun/sudo-1.8.3p1-patched
Custom version of sudo 1.8.3p1 with CVE-2021-3156 patches applied
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 parikhakshat/autoharness
A tool that automatically creates fuzzing harnesses based on a library
 rog3rsm1th/frelatage
Coverage-based fuzzer for python applications
 quarkslab/qsynthesis
Greybox Synthesizer geared for deobfuscation of assembly instructions.
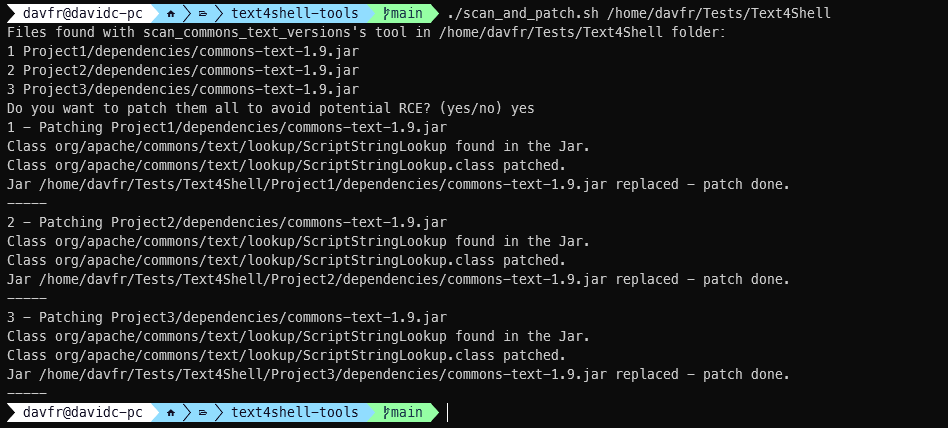 jfrog/text4shell-tools
Detect and patch vulnerable Apache Commons Text in Java JAR/WAR artifacts; fingerprint classes and scan bytecode for CVE-2022-42889 (Text4Shell) call…
 mindpatch/vulfy
🐺 Vulfy – Fast Rust based package version scanner