Dolibarr-17.0.0-Exploit-CVE-2023-30253

In Dolibarr 17.0.0 with the CMS Website plugin (core) enabled, an authenticated attacker can obtain remote command execution via php code injection…

In Dolibarr 17.0.0 with the CMS Website plugin (core) enabled, an authenticated attacker can obtain remote command execution via php code injection…

OS Command Injection Vulnerability via Plugin Execution in Figma Desktop Application

Scanner: CVE-2026-31802 npm tar path traversal — Python checker for arbitrary file write via npm pack

CVE-2026-2002 writeup and Proof-of-concept

I couldn’t find a PoC for CVE-2023-30253, so I developed an effective one

Proof-of-concept exploit for CVE-2025-48384, demonstrating remote code execution via a crafted git clone operation on vulnerable Git versions.

[PoC] Privilege escalation & code execution via LFI in PwnDoC

Proof-of-concept exploit for authenticated PHP code injection in ISPConfig <= 3.2.11, enabling remote code execution via unsanitized language file…

CVE-2023-46818 | PoC | ISPConfig 3.2.11p1

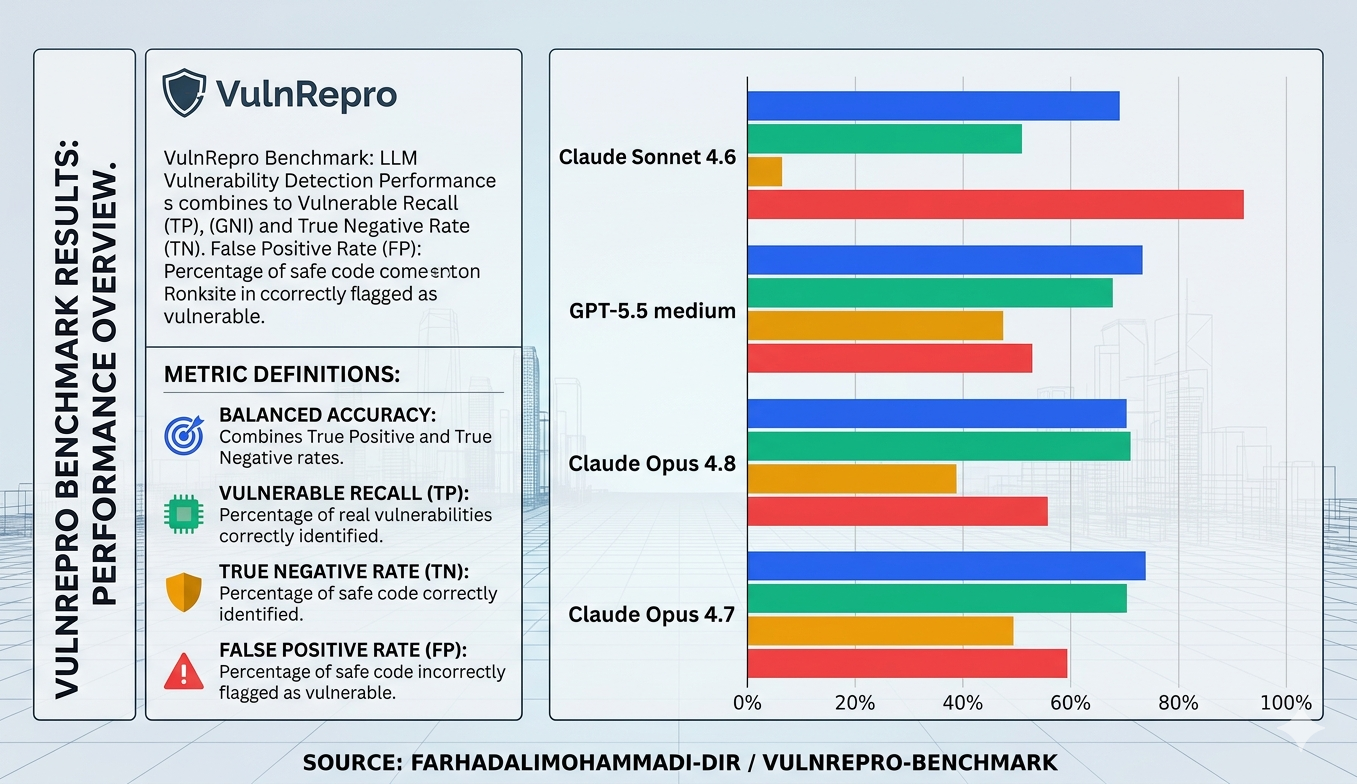
Benchmark measuring AI models' ability to detect vulnerabilities in source code via real bug bounty cases with balanced recall and false-positive…

Educational proof-of-concept demonstrating SQL injection via dynamic aliases in Django's annotate() and alias() methods (CVE-2025-57833). Includes…

Proof-of-concept exploit for CVE-2025-25014: Prototype pollution in Kibana enabling arbitrary code execution via crafted HTTP requests to ML and…

Intentionally vulnerable Next.js corporate landing page demonstrating CVE-2025-55182, a JSON injection leading to RCE/SSRF via unsafe deserialization…

Externalize Java application access to protected resources as log messages.

Python exploit script to test Cacti instances for CVE-2024-43363 RCE via log poisoning. Checks version, injects PHP payload into device names, and…

Proof-of-concept exploit for CVE-2024-21534, a critical RCE in jsonpath-plus, demonstrating arbitrary code execution via the VM module and providing…

PoC exploit for CVE-2024-52302: unrestricted file upload in common-user-management Spring Boot app leading to remote code execution via…

CVE-2022-1329 exploit for WordPress Elementor plugin (3.6.0-3.6.2) enabling authenticated remote code execution via missing capability check and…