
APKHunt
 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
android-securitycode-analysismobile-security+3
975
cyber-buddy/apkhuntStatic code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 orange-cyberdefense/grepmarx
A source code static analysis platform for AppSec enthusiasts.
 redopsx/cve-2025-63943
SQL Injection vulnerability discovered in Grocery Store Management System 1.0
 hack-with-rohit/cve-2024-0195-spiderflow
Proof-of-concept exploit for CVE-2024-0195, a critical code injection vulnerability in SpiderFlow 0.4.3 enabling remote code execution via the…
 theopaid/cve-2026-66746-http-response-splitting-via-unvalidated-response-header-values-rouille-
Security Advisory: HTTP Response Splitting via Unvalidated Response Header Values (rouille)
 ajansha/cve-2025-60374
CVE-2025-60374: Stored Cross-Site Scripting (XSS) in Perfex CRM Chatbot
 toanln-cov/cve-2026-78071
Stored XSS via Location Title in DPCalendar Free
 guoyanan1g/laravel-vul
Laravel 5 POP chain exploit for CVE-2021-43503, demonstrating a personally discovered deserialization vulnerability with proof-of-concept code.
 chiefyoru/cve-2026-48939_poc
iCagenda extension for Joomla allows the upload of arbitrary files in the file attachment feature, ultimately resulting in PHP code upload and…
 sahiloj/cve-2025-5352
Demonstrates a stored XSS vulnerability in lunary-ai/lunary's Analytics component, where unsanitized NEXT_PUBLIC_CUSTOM_SCRIPT injection leads to…
 isacaya/cve-2019-11358
Proof-of-concept exploit for CVE-2019-11358, a prototype pollution vulnerability in jQuery's extend method (versions <3.4.0). Demonstrates the attack…
 tuo4n8/cve-2022-24760
Detailed technical analysis of CVE-2022-24760, a prototype pollution vulnerability in parse-server leading to remote code execution via BSON…
 zimshk/cve-2025-59528.yaml
YAML-based proof-of-concept for CVE-2025-59528, demonstrating remote code execution in Flowise via the CustomMCP node's unsafe JavaScript evaluation.
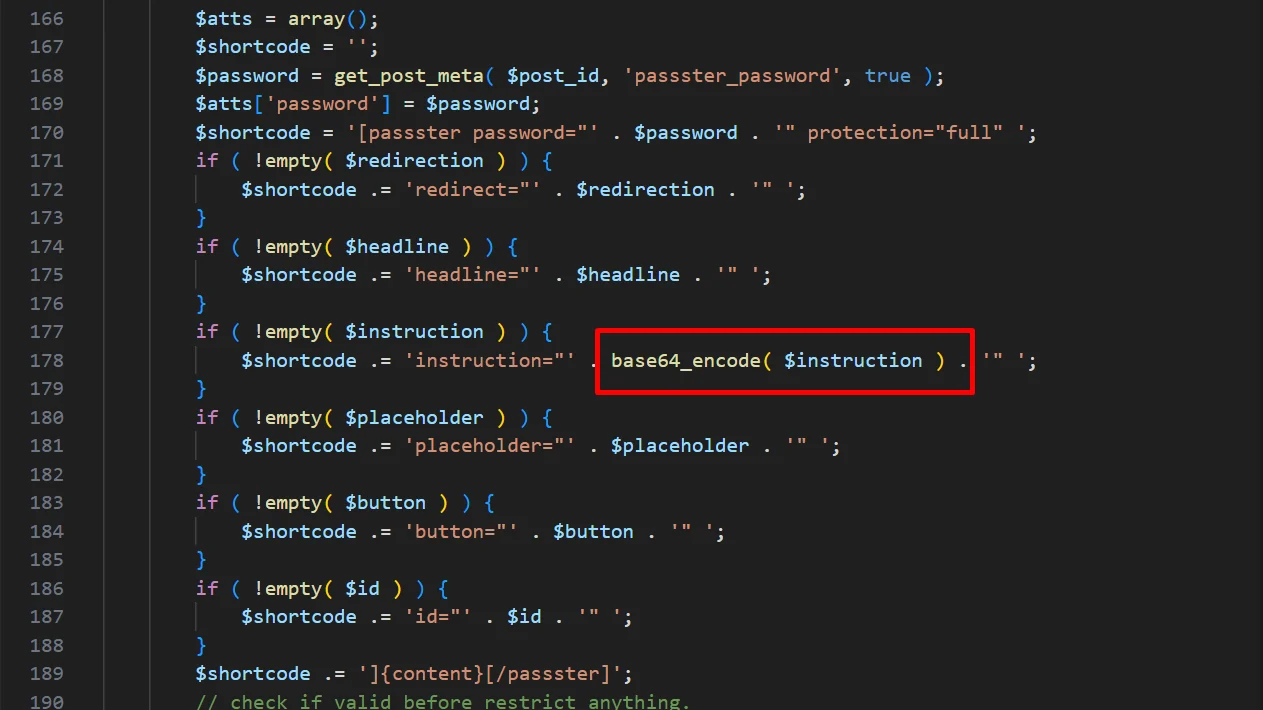 quetuan03/cve-2025-57926
WordPress Passster Plugin <= 4.2.18 is vulnerable to Cross Site Scripting (XSS)
 al1ex/cve-2020-26258
CVE-2020-26258 && XStream SSRF
 rooootdev/cve-2019-5784-poc
a proof of concept for CVE-2019-5784
 aaryan-11-x/cve-2024-57487-and-cve-2024-57488
Proof-of-concept and detailed writeups for CVE-2024-57487 (authenticated RCE via file upload) and CVE-2024-57488 (stored XSS) in Online Car Rental…