

unauthscout
 rmottanet/unauthscout
UnauthScout is an OSINT (Open Source Intelligence) tool developed in Bash for passive exploration of assets on version control platforms (GitLab and…
code-analysisgeneral-purpose-utilitiesosint+2
5
rmottanet/unauthscoutUnauthScout is an OSINT (Open Source Intelligence) tool developed in Bash for passive exploration of assets on version control platforms (GitLab and…
 lucifer0xf/wp2shell-wordpress-town
Unauthenticated Remote Code Execution (RCE) in WordPress Core allows attackers to execute arbitrary code without logging in by chaining…
 josh-blythe/bordair-detector
Two-stage prompt-injection and jailbreak detector: regex gates plus a quantised DeBERTa-v3 ONNX classifier, with image, document, and audio support.…
 fazilbaig1/cve-2021-23369
Python exploit script for CVE-2021-23369, a Remote Code Execution vulnerability in Handlebars template engine versions before 4.7.7. Accepts a target…
 ggfzx/cve-2024-36104
Exploit tool for CVE-2024-36104 targeting Apache OFBiz code execution vulnerability. Supports single and batch URL scanning with proxy and threading…
 sparshbiswas-ai/cve-2025-11844-smolagents
Educational sandbox and dynamic proof-of-concept scanner for CVE-2025-11844 XPath injection in Hugging Face smolagents library, enabling local data…
 starkchristmas/cve-2020-1947
Proof-of-concept and analysis for CVE-2020-1947, a YAML deserialization remote code execution vulnerability in Apache ShardingSphere UI, including…
 zenithgenius/wordpress-batch-rce-lab
CVE-2026-63030: WordPress REST batch-endpoint array desync. Mechanism, detection, mitigation, and a safe reproduction lab.
 sassoftware/jackson
This repository provides a comprehensive security remediation of denial-of-service and allocation of resources without limits or throttling security…
 vm2mv/tinyxml
TinyXML 2.6.2 with fixes for CVE-2021-42260 and CVE-2023-34194
 garethmsheldon/react2shell-cve-2025-55182-detector
Multi-language detection scripts for CVE-2025-55182 (React2Shell) that scan package.json files to identify vulnerable React dependency versions and…
 ducducuc111/cve-2025-55182-poc
Proof-of-concept exploit for CVE-2025-55182, demonstrating remote code execution via prototype chain vulnerability in React Server Components.…
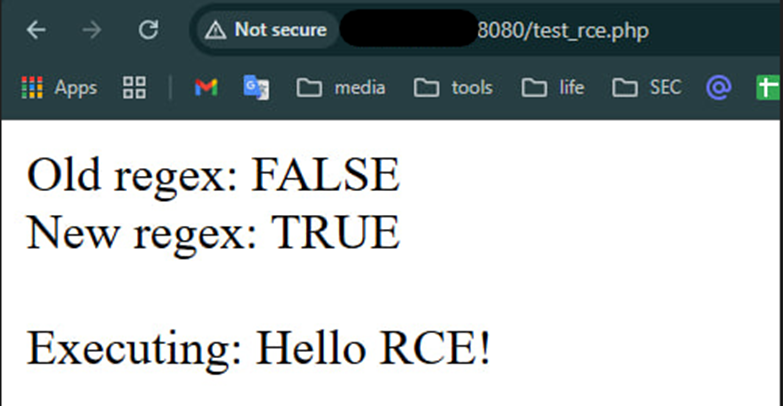 soltanali0/cve-2024-12877-exploit
Educational CVE-2024-12877 exploit demo for PHP Object Injection in GiveWP WordPress plugin. Includes root cause analysis, regex bypass techniques,…
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 dexit/cve-2022-1329
CVE-2022-1329 exploit for WordPress Elementor plugin (3.6.0-3.6.2) enabling authenticated remote code execution via missing capability check and…
 shoucheng3/asf__commons-text_cve-2022-42889_1-9
Java library for string manipulation algorithms, packaged with a proof-of-concept exploit for CVE-2022-42889 to demonstrate and test the…
 satheesh575555/external_expat_aosp10_r33_cve-2022-23990
C library for parsing XML, specifically patched for CVE-2022-23990, providing a reference implementation for vulnerability analysis and secure coding…
 shoucheng3/codehaus-plexus__plexus-utils_cve-2017-1000487_3-0-15
Java utility library with a focus on a specific CVE vulnerability, providing code analysis and static analysis capabilities for security assessment.