

CVE-2018-16370
 snappyjack/cve-2018-16370
In PESCMS Team 2.2.1, attackers may upload and execute arbitrary PHP code through /Public/?g=Team&m=Setting&a=upgrade by placing a .php file in a…
code-analysisexploitationpenetration-testing+2
snappyjack/cve-2018-16370In PESCMS Team 2.2.1, attackers may upload and execute arbitrary PHP code through /Public/?g=Team&m=Setting&a=upgrade by placing a .php file in a…
 sanupl/vehicle-service-management-system-multiple-file-upload-leads-to-code-execution
CVE-2021-46076 - Sourcecodester Vehicle Service Management System 1.0 is vulnerable to File upload. An attacker can upload a malicious php file in…
 romain-deperne/cve-2026-77262
Proof-of-concept exploit for arbitrary file read in mcp-atlassian via path traversal in confluence_upload_attachment, with analysis and reproduction…
 invisiblebyte/cve-2023-46694
Proof-of-concept exploit for CVE-2023-46694: authenticated remote code execution via arbitrary file upload in Vtenext 21.02 Ckeditor file manager.
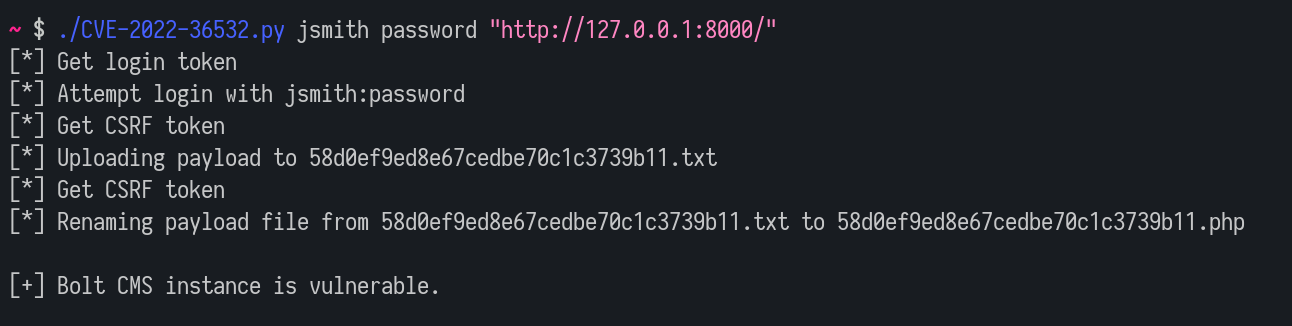 lutrasecurity/cve-2022-36532
Proof-of-concept exploit script for CVE-2022-36532 enabling authenticated remote code execution via file upload in Bolt CMS 5.1.12 and below.
 chiefyoru/cve-2026-48939_poc
iCagenda extension for Joomla allows the upload of arbitrary files in the file attachment feature, ultimately resulting in PHP code upload and…
 h4ckr4v3n/cve-2024-46209
Security research repository detailing CVE-2024-46209 (authenticated RCE) and CVE-2024-46210 (stored XSS via file upload) in Redaxo CMS v5.17.1, with…
 sromanhu/cve-2023-43360-cmsmadesimple-stored-xss---file-picker-extension
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the Top…
 jra89/cve-2019-19634
This is a filter bypass exploit that results in arbitrary file upload and remote code execution in class.upload.php <= 2.0.4
 jra89/cve-2019-19576
This is a filter bypass exploit that results in arbitrary file upload and remote code execution in class.upload.php <= 2.0.3
 minhhk68/cve-2026-13157
Proof of concept and root-cause analysis for an authenticated arbitrary file upload in WordPress Theme Demo Import leading to remote code execution…
 xmyronn/cve-2026-11344-rce
Unauthenticated remote code execution exploit for Vehicle Management System in PHP via unrestricted file upload in newdriver.php and newvehicle.php,…
 xmyronn/cve-2026-7393-rce
Proof-of-concept exploit for CVE-2026-7393: unrestricted file upload in Pizzafy Ecommerce System 1.0 allowing authenticated administrators to upload…
 d3kc4rt1/cve-2026-1657
Unauthenticated Arbitrary File Upload in EventPrime Plugin
 d3sca/cve-2024-52302
PoC exploit for CVE-2024-52302: unrestricted file upload in common-user-management Spring Boot app leading to remote code execution via…
 istern/cve-2023-26262
Proof-of-concept for authenticated arbitrary file upload in Sitecore 10.3, enabling webshell deployment and remote code execution via the import…
 k1nakoo/cve-2024-10410
Proof-of-concept exploit for CVE-2024-10410: unrestricted file upload in Online Hotel Reservation System. Demonstrates bypass of image validation via…
 renat0z3r0/prefect-cve-2026-5366
PoC for CVE-2026-5366: git argument injection in Prefect's GitRepository leading to RCE on the worker.