xwiki__xwiki-commons_CVE-2023-31126_14-10-3

Java library providing technical commons for XWiki projects, with a focus on vulnerability analysis and static code inspection for security testing.

Java library providing technical commons for XWiki projects, with a focus on vulnerability analysis and static code inspection for security testing.

Technical Java libraries providing common utilities and components for the XWiki platform, including security vulnerability fixes and code analysis…

Jenkins plugin providing Git APIs for automated repository operations including fetch, checkout, merge, and tag, with support for credential-based…

Technical libraries for XWiki projects, providing reusable components for vulnerability analysis, code analysis, and static analysis across…

C library for parsing XML, patched for CVE-2022-25235, providing stream-oriented parsing with handler registration and build configuration options.

Bash script to detect Log4j (CVE-2021-44228) exploitable systems by scanning running Java processes for vulnerable log4j-core components without…

Java utility library with patched CVE-2022-4244 vulnerability, providing common helper classes for I/O, reflection, and CLI argument parsing in…

Java library for creating and extracting archives (ZIP, TAR, JAR) with support for various compression formats. Note: version 3.5 contains a fix for…

Java testing framework for unit, integration, and end-to-end tests with annotations, data-driven testing, and parallel execution support.

C library for stream-oriented XML parsing, providing a fast and configurable parser with support for custom handlers and encoding options.

Java source code generator that creates calling classes for Oracle PL/SQL package procedures, supporting various parameter types and automatic type…

find hardcoded strings from source code

Detect and fix log4j log4shell vulnerability (CVE-2021-44228)

test the CVE-2017-12852 in numpy v1.13.1 and v1.13.3 has fixed the bug

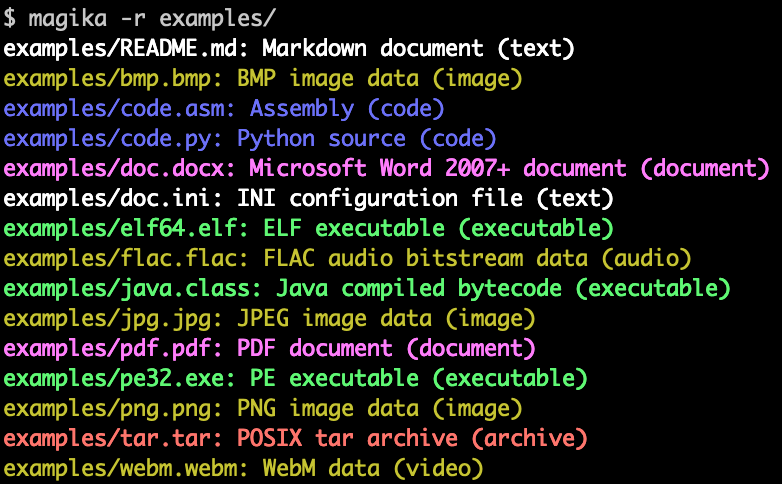
Fast and accurate AI powered file content types detection

A fork of JSONPath from http://goessner.net/articles/JsonPath/

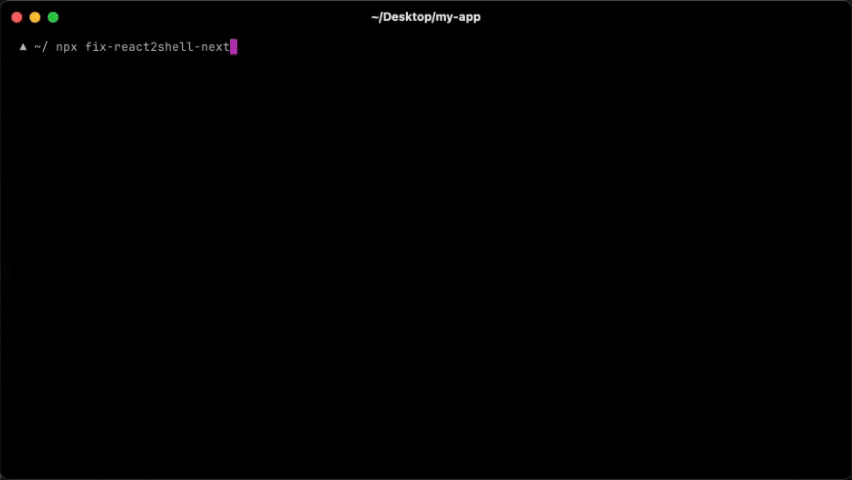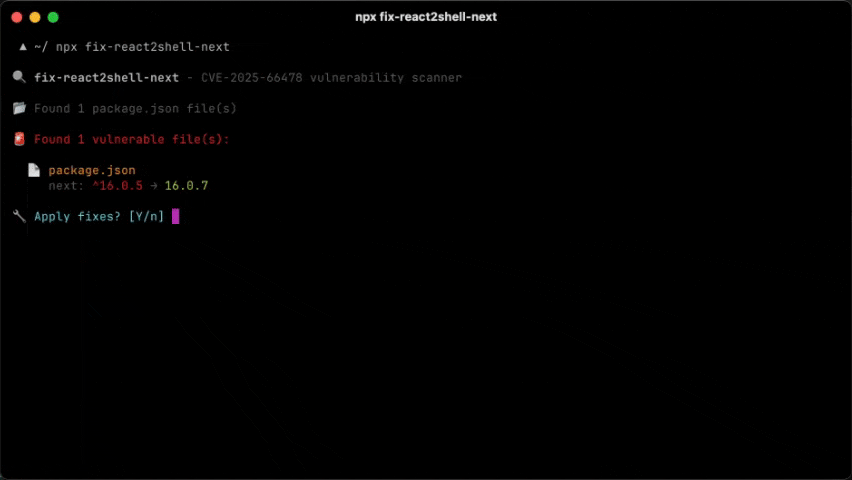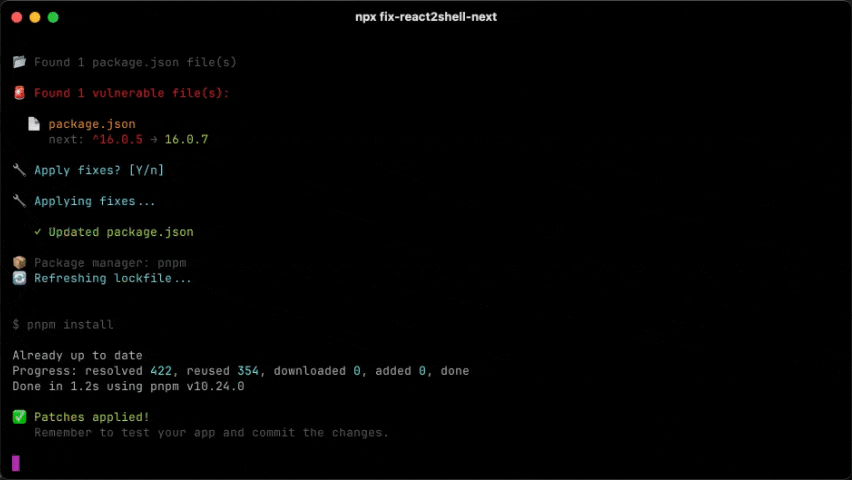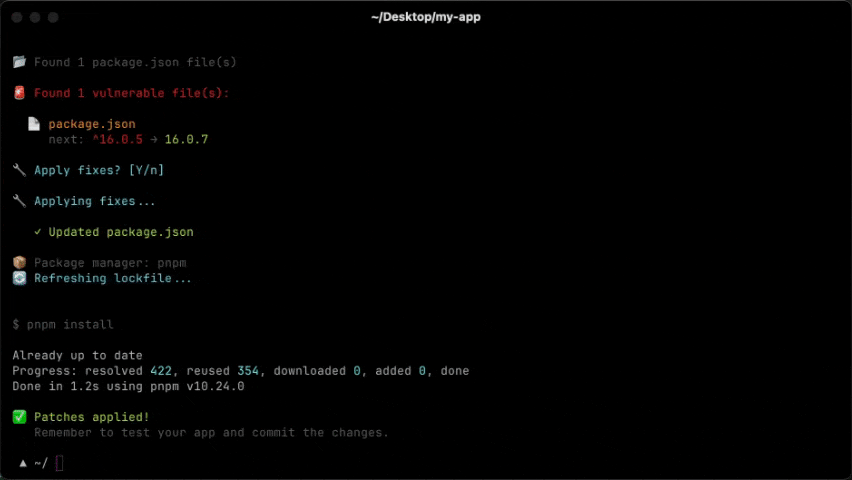
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.

Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.