platform_packages_providers_MediaProvider_CVE-2023-40127

Android MediaProvider vulnerability analysis and patch for CVE-2023-40127, focusing on security assessment and remediation.

Android MediaProvider vulnerability analysis and patch for CVE-2023-40127, focusing on security assessment and remediation.

CodeQL query test for CVE-2023-24329, demonstrating static analysis detection of a specific vulnerability in Python's urllib.parse module.

Java utility library with a focus on a specific CVE vulnerability, providing code analysis and static analysis capabilities for security assessment.

C-based detection tool for CVE-2017-2793, enabling identification and analysis of the specific vulnerability in affected systems.

Extracts and exports certificate information from digitally signed PE files using Python and pefile, enabling forensic analysis of code-signing…

Java library providing technical commons for XWiki projects, with a focus on vulnerability analysis and static code inspection for security testing.

Technical Java libraries providing common utilities and components for the XWiki platform, including security vulnerability fixes and code analysis…

Exploit module for Apache JSPWiki CVE-2019-10078, enabling security testing of Java-based wiki platforms through targeted vulnerability exploitation…

Security research repository detailing CVE-2024-46209 (authenticated RCE) and CVE-2024-46210 (stored XSS via file upload) in Redaxo CMS v5.17.1, with…

CVE-2025-59059: Misattributed RCE in Apache Ranger Static Analysis Correction

Exploit code and analysis for CVE-2023-26049 targeting Jetty 9.4.31, demonstrating a vulnerability in the web server for security testing and…

Detailed CVE-2021-31856 report with PoC and code analysis for a SQL injection vulnerability in Meshery's pattern file API, enabling unauthenticated…

Reproduction and patching guide for CVE-2004-2167, a buffer overflow in LaTeX2RTF, with a C exploit and patch for educational vulnerability analysis.

Patched version of Expat XML parser for AOSP10, addressing CVE-2022-25236. Provides source code for vulnerability analysis and educational review of…

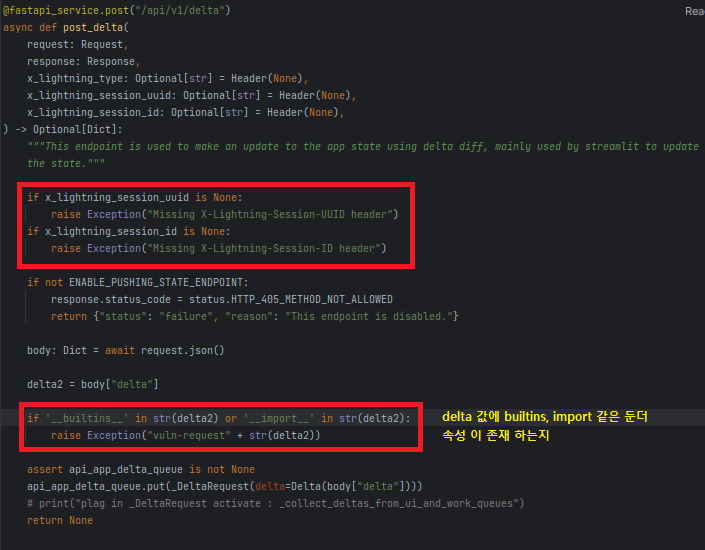
Detailed technical analysis of CVE-2024-5452, a remote code execution vulnerability in PyTorch Lightning via DeepDiff delta property pollution, with…

PoC and analysis for Kibana Prototype Pollution RCE (CVE-2019-7609).

Technical analysis and proof-of-concept for CVE-2024-48990, a privilege escalation vulnerability in needrestart allowing local attackers to execute…

In-depth technical analysis of CVE-2021-25804, a VLC AVI parser vulnerability. Includes root cause, patch diff, and exploitation primitives for…