
CVE-2026-11551-PoC
 ubaydev/cve-2026-11551-poc
Proof-of-concept exploit for CVE-2026-11551, an unauthenticated privilege escalation vulnerability in the Branda White Label plugin for WordPress,…
authenticationcode-analysisexploitation+5
ubaydev/cve-2026-11551-pocProof-of-concept exploit for CVE-2026-11551, an unauthenticated privilege escalation vulnerability in the Branda White Label plugin for WordPress,…
 q1uf3ng/cve-2025-51458-exp
CVE-2025-51458 - DB-GPT Pre-Auth SQL Injection PoC
 youssefsalama1/cve-2018-6574
Exploit code for CVE-2018-6574, a Go language vulnerability allowing arbitrary code execution via crafted import paths.
 pazeray/cve-2020-17533
Proof-of-concept exploit for Apache Struts2 remote code execution vulnerability CVE-2020-17533, leveraging OGNL expression injection for…
 kov404/cve-2025-52385
Studio 3T v.2025.1.0
 ramzerk/cve-2024-46987
This Rust PoC exploits CVE-2024-46987, a Path Traversal bug in Camaleon CMS 2.8.0 < 2.8.2 (work on 2.9.0).
 mbadanoiu/cve-2025-6384
CVE-2025-6384: Groovy Sandbox Bypass 2 in CrafterCMS
 official-blackhat13/cve-2021-26086
Confluence server webwork OGNL injection
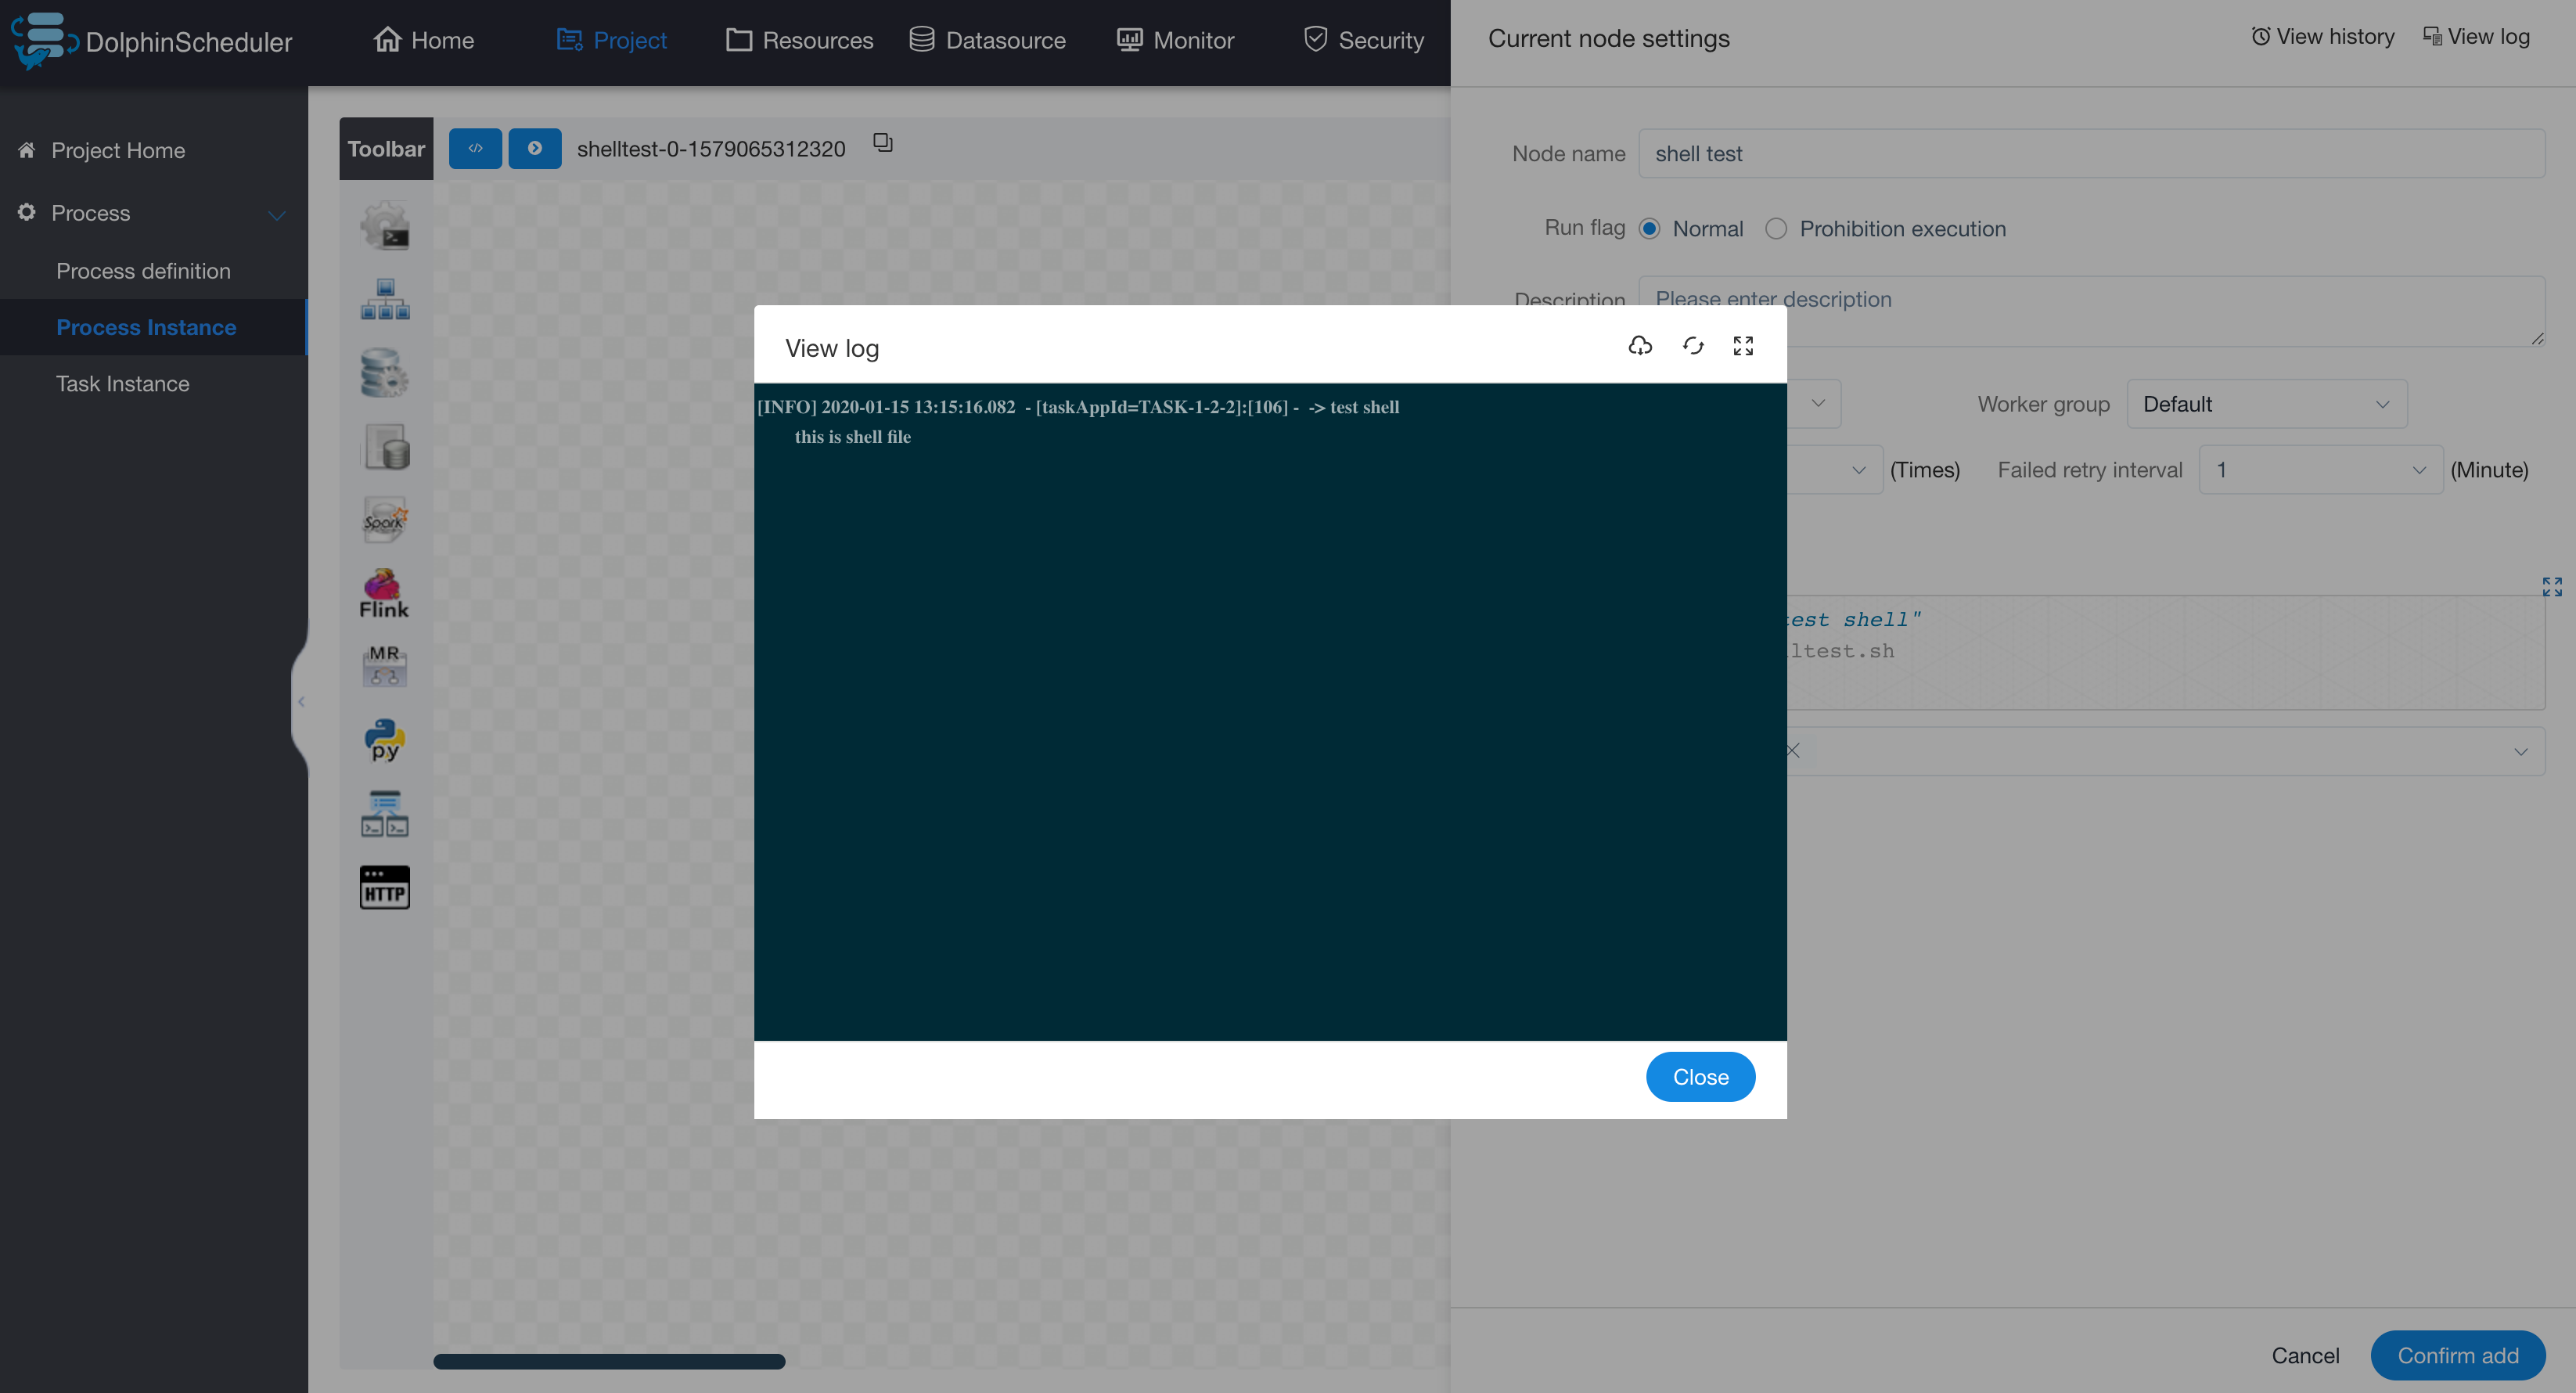 shoucheng3/apache__dolphinscheduler_cve-2022-26884_2-0-5
Proof-of-concept exploit for CVE-2022-26884 targeting Apache DolphinScheduler, enabling remote code execution via crafted requests to the workflow…
 shoucheng3/apache__dolphinscheduler_cve-2022-34662_2-0-9
Proof-of-concept exploit for CVE-2022-34662 targeting Apache DolphinScheduler, enabling remote code execution via crafted SQL injection in the…
 d0n601/cve-2025-9216
StoreEngine – Powerful WordPress eCommerce Plugin for Payments, Memberships, Affiliates, Sales & More <= 1.4.0 - Authenticated (Subscriber+)…
 fbion/cve-2022-22947
Spring Cloud Gateway Actuator API SpEL Code Injection.
 subc0ol/cve-2015-0235
Ruby-based exploit for CVE-2015-0235 (Ghost) targeting glibc gethostbyname buffer overflow for remote code execution on vulnerable systems.
 r00t4dm/jenkins-cve-2015-8103
Exploit for Jenkins CVE-2015-8103, a remote code execution vulnerability in the Jenkins CLI. Enables authenticated attackers to execute arbitrary…
 rain321654/yasa-cve-2024-43400-main1
yasa
 sanupl/vehicle-service-management-system-category-list-stored-cross-site-scripting-xss
CVE-2021-46071 - A Stored Cross Site Scripting (XSS) vulnerability exists in Vehicle Service Management System 1.0 via the Category List Section in…