

 k3ystr0k3r/cve-2017-12615
CVE-2017-12615 - Apache Tomcat Remote Code Execution (RCE)
 lazarus0x1337/cve-2026-25632
CVE-2026-25632 — Fix Unsafe JSON Deserialization Leading to Remote Code Execution
 kx00007/cve-2026-35196
Second CVE still Remote Code Execution
 polosss/by-poloss..-..cve-2017-20251
Insert PHP Plugin PHP Code Injection
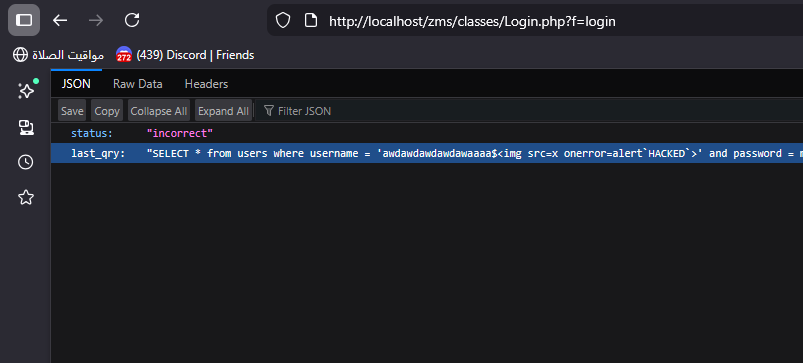 mmakingdom/cve-2025-65881
Sourcecodester Zoo Management System v1.0 is vulnerable to Cross Site Scripting (XSS) in /classes/Login.php Due to invalid Content-Type
 joshterrill/cve-2025-55182-realistic-poc
a realistic POC demonstrating the missing `hasOwnProperty` check in [email protected]
 bor8/cve-2022-34169
https://nvd.nist.gov/vuln/detail/CVE-2022-34169
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
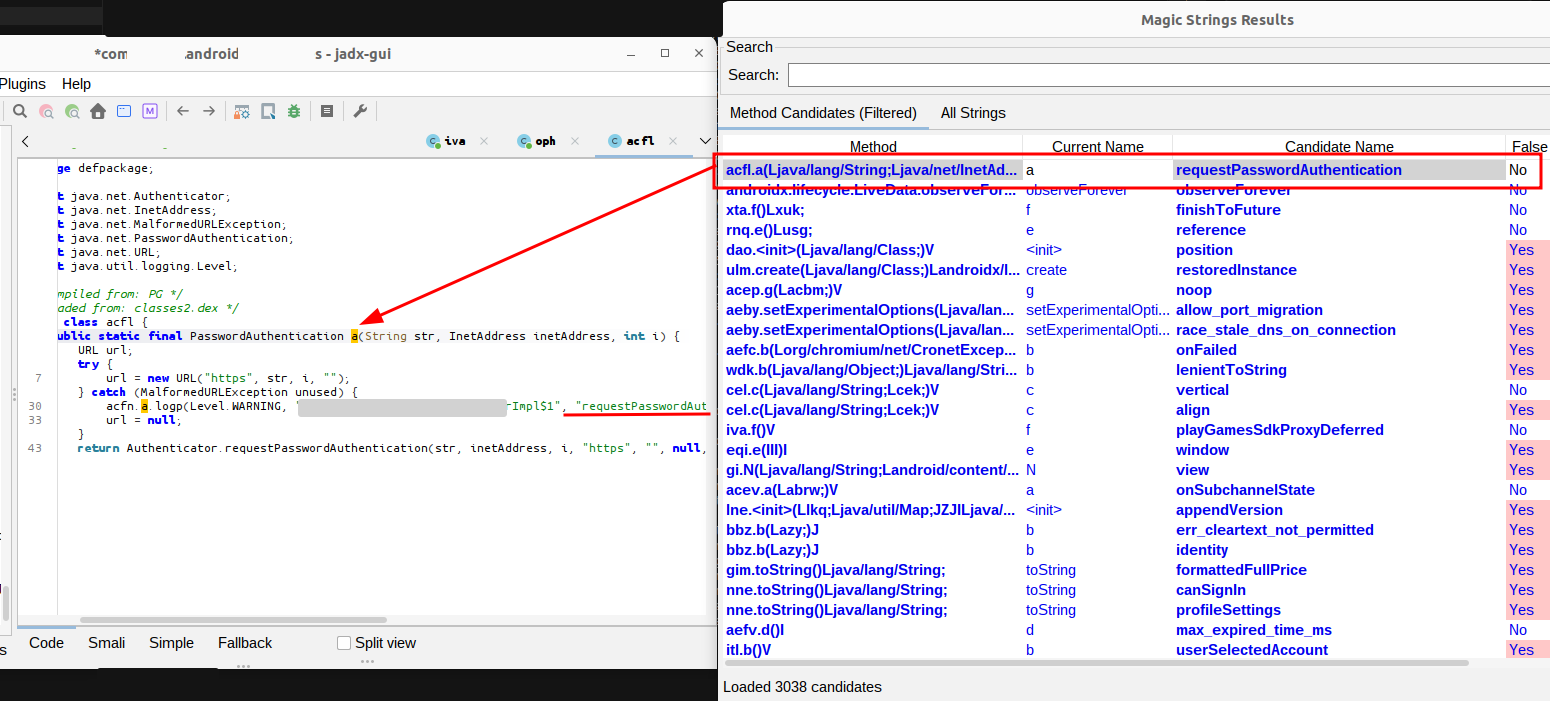 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
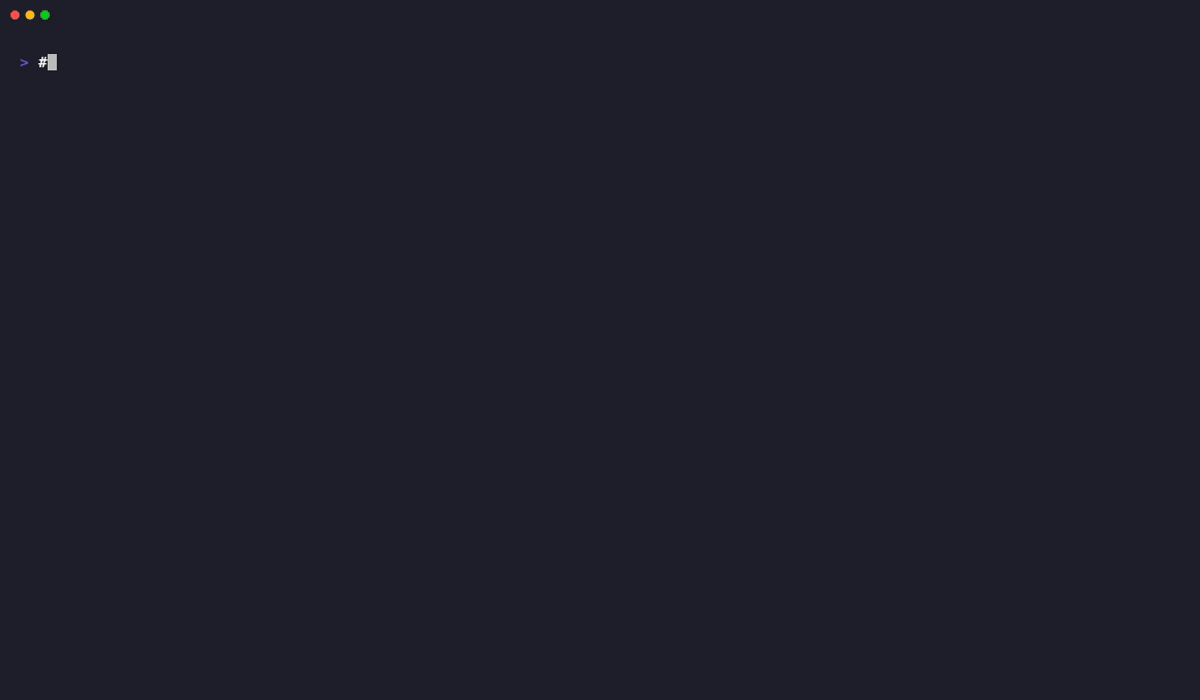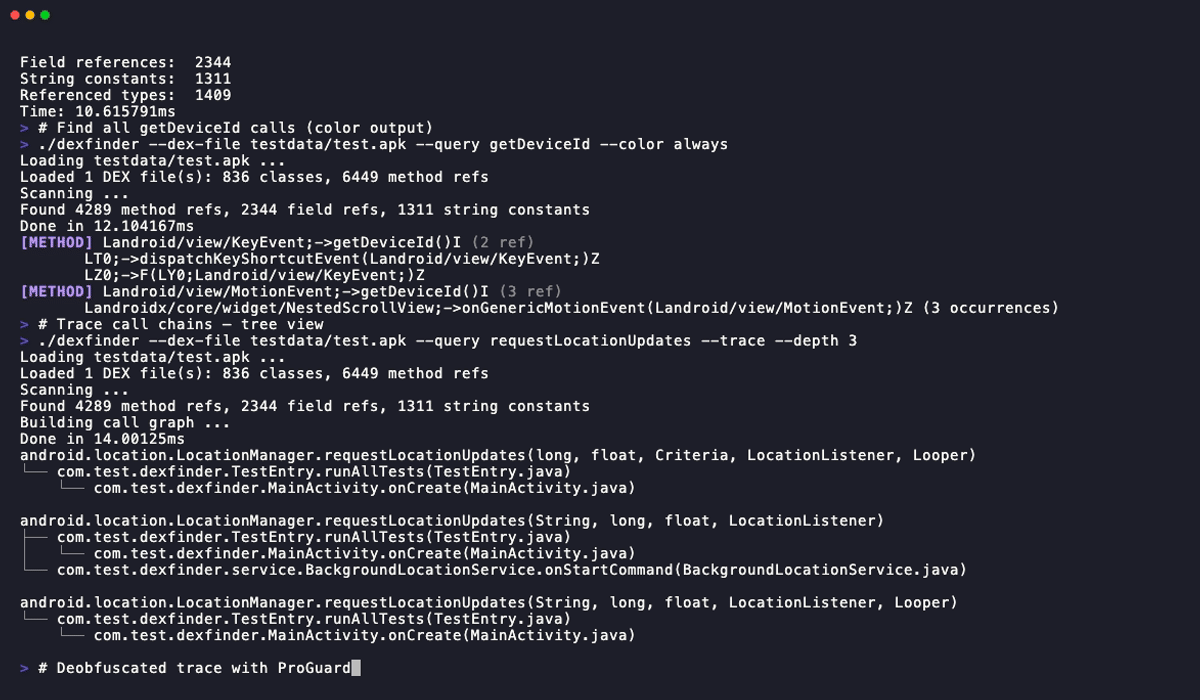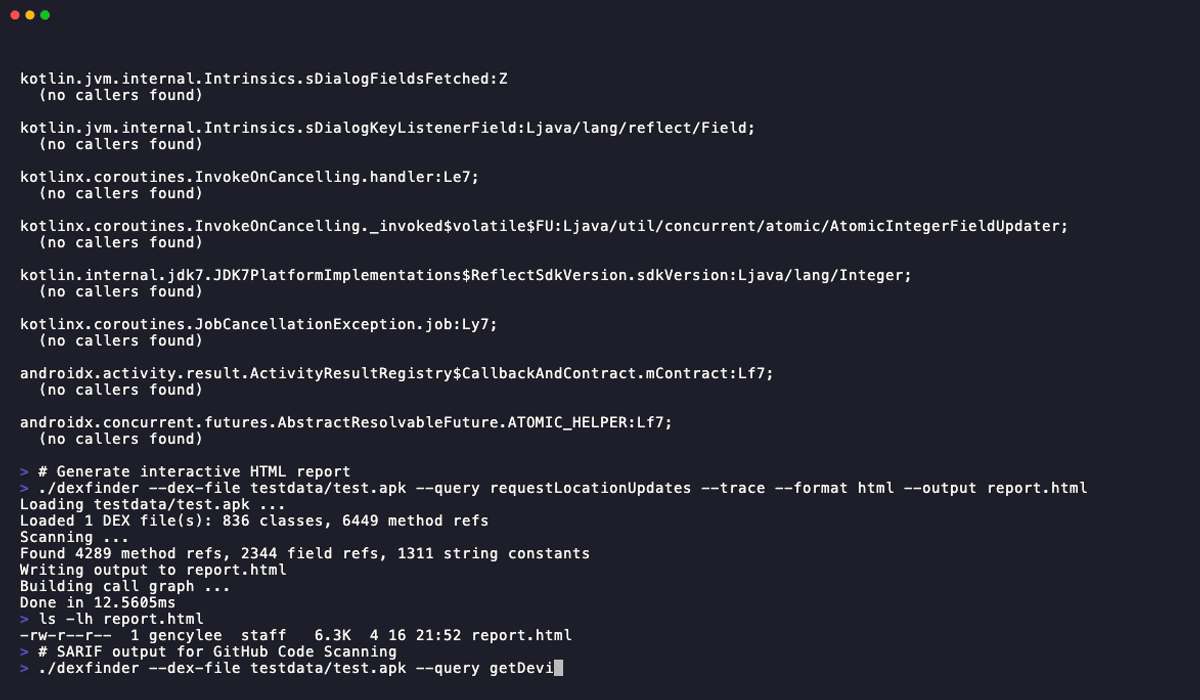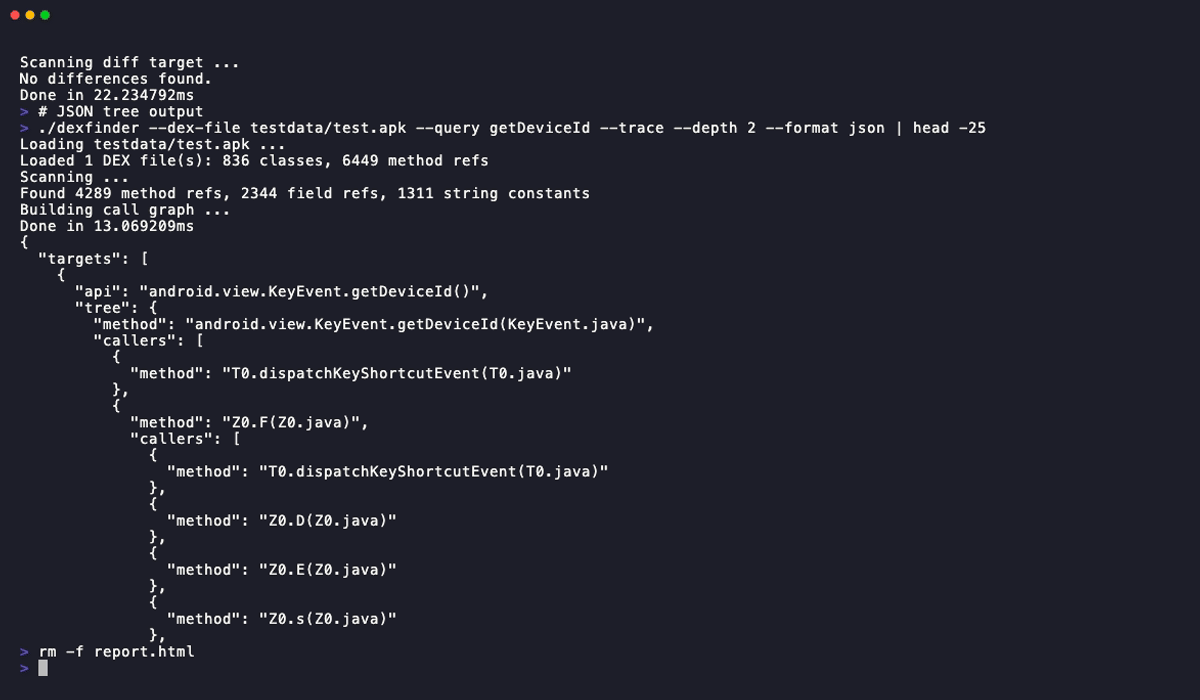 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 nanopathi/frameworks_av_aosp10_r33_cve-2020-0160
 umvfx1bvaw50/cve-2017-13286
CVE-2017-13286 Poc(can not use)
 satheesh575555/packages_apps_settings_aosp10_r33_cve-2021-0506