
CVE-2025-5352
 sahiloj/cve-2025-5352
Demonstrates a stored XSS vulnerability in lunary-ai/lunary's Analytics component, where unsanitized NEXT_PUBLIC_CUSTOM_SCRIPT injection leads to…
code-analysisexploitationvulnerability-analysis+2
sahiloj/cve-2025-5352Demonstrates a stored XSS vulnerability in lunary-ai/lunary's Analytics component, where unsanitized NEXT_PUBLIC_CUSTOM_SCRIPT injection leads to…
 some-1hing/cve-2018-16763
Python tool for analyzing CVE-2018-16763 in FUEL CMS with cleaner response parsing and interactive vulnerability checking.
 homjxi0e/cve-2017-8625_bypass_umci
Proof-of-concept exploit demonstrating UMCI bypass in Internet Explorer using JScript and ActiveX to execute arbitrary binaries, targeting Windows…
 xxconi/cve-2026-3296
CVE-2026-3296 is a CVSS 9.8 Critical unauthenticated PHP Object Injection vulnerability in the Everest Forms WordPress plugin
 funixone/exploit-cve-2026-8832-
Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…
 izxci/cve-2026-49085
PHP Object Injection exploit for WP Insightly (CVE-2026-49085). Provides proof-of-concept code to demonstrate and test the vulnerability in affected…
 netvanguard-cmd/cve-2025-59536
PoC exploit for CVE-2025-59536, a high-severity code injection vulnerability in Claude Code's startup trust dialog, enabling remote exploitation of…
 cyberdefenseinstitute/poc_cve-2016-2098_rails42
A PoC of CVE-2016-2098 (rails4.2.5.1 / view render)
 sivaadityacoder/cve-2025-67146-cve-2025-67147
PHP-based exploit module targeting CVE-2025-67146 and CVE-2025-67147 for automated vulnerability exploitation and security assessment.
 dwgth4i/cve-2026-20817
Proof-of-concept exploit for CVE-2026-20817, demonstrating the vulnerability with a C-based implementation for security research and testing.
 habuon/cve-2026-48208
This is POC repo for CVE-2026-48208
 davidxbors/cve-2025-25014
Proof-of-concept exploit for CVE-2025-25014: Prototype pollution in Kibana enabling arbitrary code execution via crafted HTTP requests to ML and…
 zemarkhos/cve-2026-44403-wingftp-v8.1.2-poc-exploit
CVE-2026-44403-WingFTP-v8.1.2-POC-Exploit
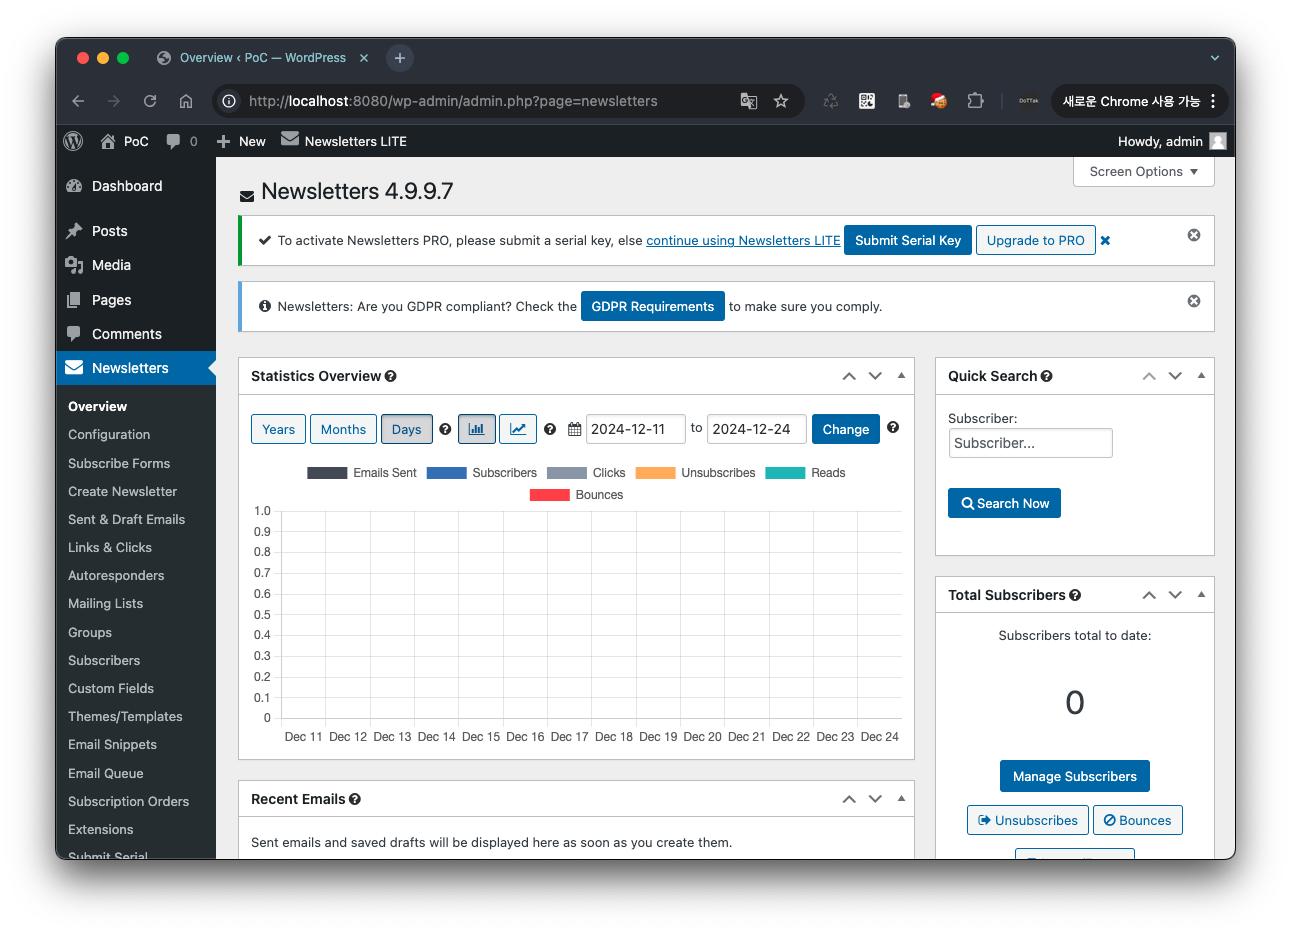 dottak/cve-2025-30921
PoC of CVE-2025-30921
 sj/spring-data-rest-cve-2017-8046
Fork of github.com/spring-projects/spring-data-rest (vulnerable to CVE-2017-8046)
 qwqdanchun/cve-2023-27363
Proof-of-concept exploit for CVE-2023-27363, demonstrating a specific vulnerability with automated exploitation logic for security testing and…
 shadowsock5/shardingsphere_cve-2020-1947
 mehdiboukhobza/sandbox_cve-2021-23358