
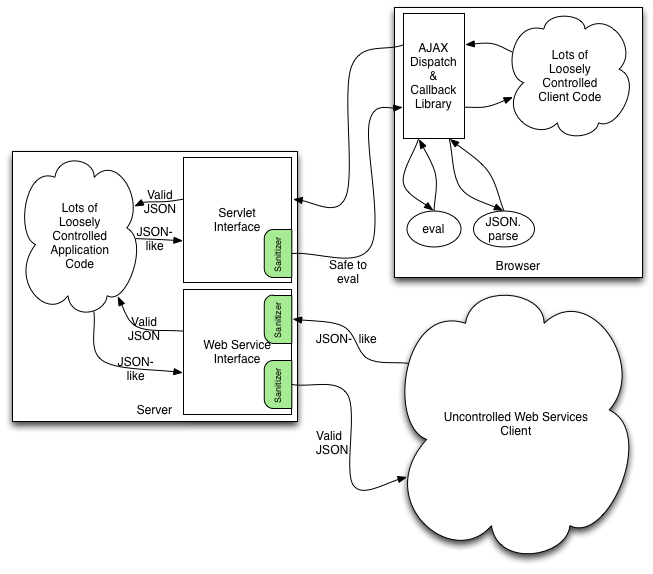
json-sanitizer
 owasp/json-sanitizer
Given JSON-like content, The JSON Sanitizer converts it to valid JSON.
code-analysisencryption-decryption-toolsgeneral-purpose-utilities+3
owasp/json-sanitizerGiven JSON-like content, The JSON Sanitizer converts it to valid JSON.
 kira2040k/php_code_analysis
Static PHP code scanner that detects SQL injection, XSS, SSRF, LFI, command injection, insecure deserialization, and other web vulnerabilities in…
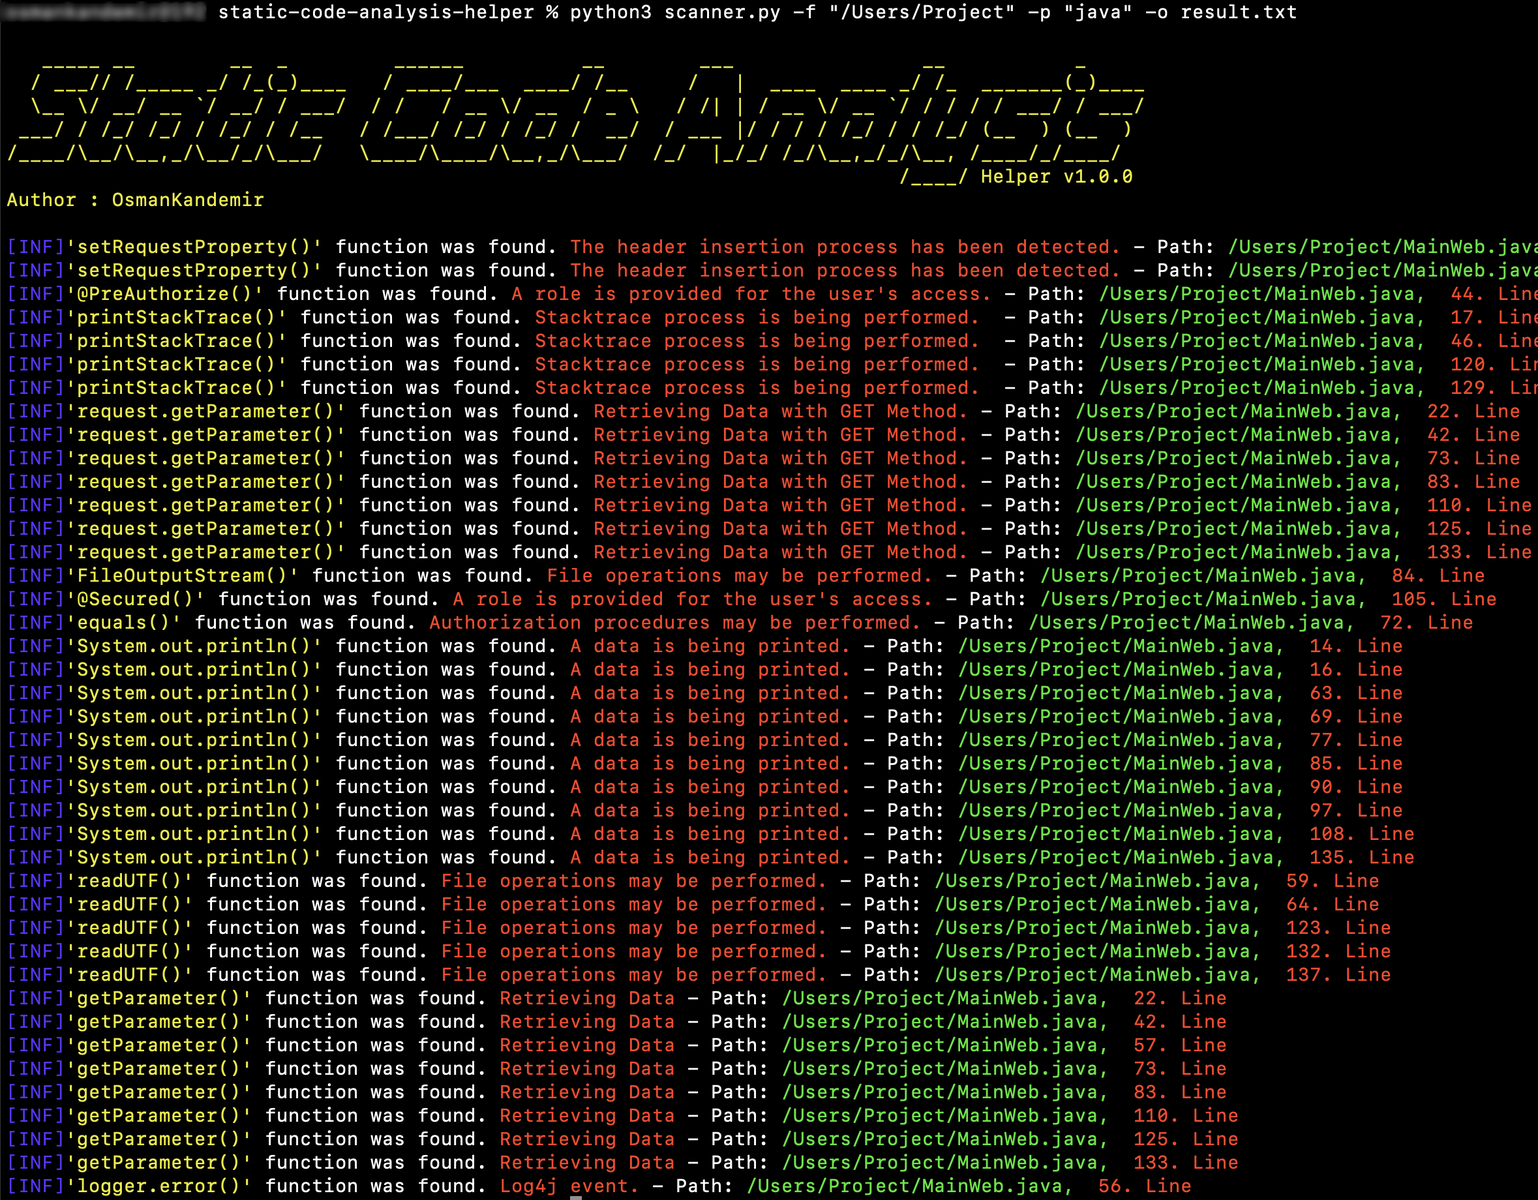 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 uzju/gin-vue-admin-poc-cve-2022-21660
CVE-2022-21660
 titanous/rocacheck
Go package that checks if RSA keys are vulnerable to ROCA / CVE-2017-15361
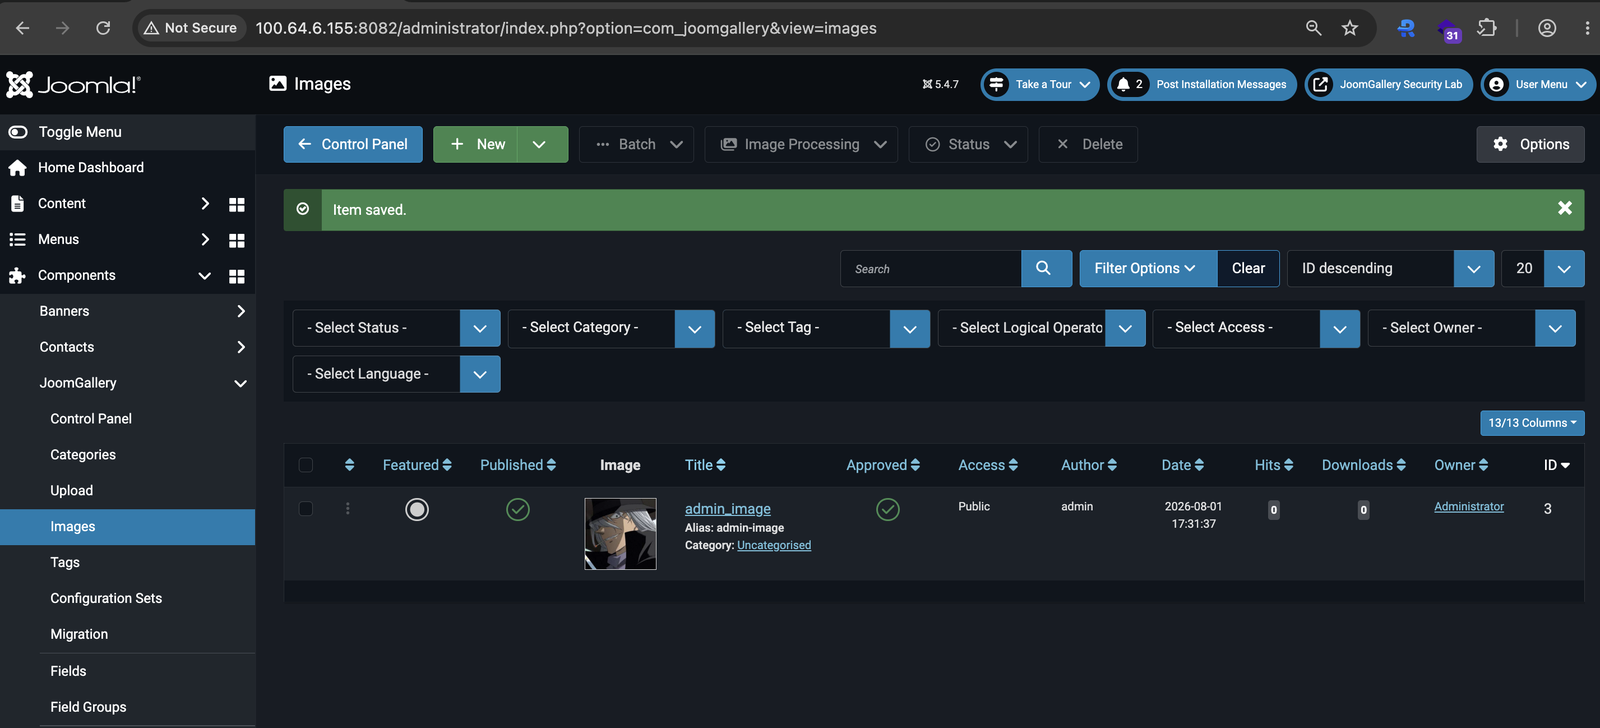 toanln-cov/cve-2026-66917
IDOR + Stored XSS via Broken Object-Level Authorization in JoomGallery

 marcstraube/zappzarapp-php-security
PHP 8.4+ security library (mirror)
 bekwiner/cve-2026-47777
Detailed technical analysis of CVE-2026-47777, a high-severity authorization bypass in Mastodon's Featured Collections federation pipeline, including…
 sassoftware/jackson
This repository provides a comprehensive security remediation of denial-of-service and allocation of resources without limits or throttling security…
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 darrocarocatest-sys/pv2-victim
authz research - CVE-2026-3306 fix coverage
 shoucheng3/whitesource__curekit_cve-2022-23082_1-1-3
Java security library providing contextual encoders and sanitizers to automatically remediate vulnerabilities like XSS, path traversal, and command…
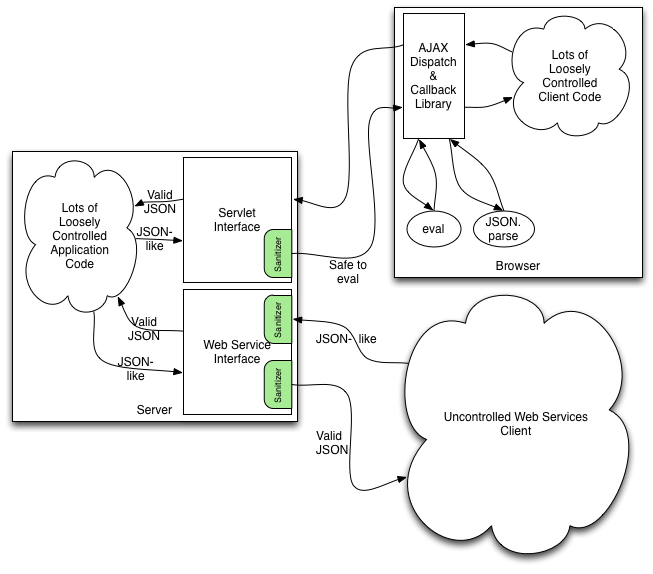 shoucheng3/owasp__json-sanitizer_cve-2020-13973_1-2-0
Java library that converts malformed JSON-like content into standards-compliant, safe JSON, preventing code injection and ensuring embeddability in…
 trinadh465/openssl-1_0_1g_cve-2016-0702
OpenSSL 1.0.1g source code snapshot, providing SSL/TLS and general-purpose cryptography library with ciphers, digests, and X.509 certificate handling.
 khayashi4337/lodash.template-fixed
Fork of lodash.template with CVE-2021-23337 fix (command injection via variable option)
 shoucheng3/xwiki__xwiki-rendering_cve-2023-37908_14-10-3
Generic wiki/HTML rendering system that converts textual input between syntaxes (wiki, HTML, XHTML). This repository contains a patched version…
 barsug/msgspec-python313-pre
CVE-2025-27607 fix